❌

Reading view

There are new articles available, click to refresh the page.

Ryuk ransomware operator sentenced to 2 years in prison

A 35-year-old Armenian national was sentenced to two years in prison for his involvement in a series of Ryuk ransomware attacks while living in Ukraine and Russia in 2019 and 2020, the Justice Department said Tuesday.

Karen Vardanyan was extradited from Ukraine to the United States last year and pleaded guilty to computer fraud and conspiracy to commit fraud and extortion in July. Vardanyan’s sentencing, which also calls for about $1.2 million in restitution to victims, matches terms of a plea agreement he reached with prosecutors.

Vardanyan and his co-conspirators’ victims include a Michigan-based company that paid a ransom of nearly $1.2 million in January 2020, a Watsonville, Oregon-based technology company that was attacked in December 2019 and a Texas-based school breached in February 2020, according to court records.

“Like Vardanyan, many cybercriminals are not masterminds of a complex ransomware or extortion scheme but nonetheless play an integral part in the success of these crimes,” read a memo signed by U.S. attorneys in the District of Oregon.

“Unfortunately, high rewards and a relatively low risk of detection are basic features of cybercrime. The only way to affect the cost-benefit analysis of these crimes is to impose meaningful sentences on those who are caught,” the U.S. attorneys added.

Prosecutors previously accused Vardanyan and his co-conspirators — Ukrainian nationals Oleg Nikolayevich Lyulyava and Andrii Leonydovich Prykhodchenko, and Armenian national Levon Georgiyovych Avetisyan — of illegally accessing computer networks to deploy Ryuk ransomware on hundreds of compromised servers and workstations between March 2019 and September 2020.

Ryuk ransomware was prevalent in 2019 and 2020, infecting thousands of victims globally across the private sector, state and local municipalities, local school districts and critical infrastructure, including a wave of attacks on U.S. hospitals.

Victims of Ryuk ransomware attacks include Hollywood Presbyterian Medical Center, Universal Health Services, Electronic Warfare Associates, a North Carolina water utility and multiple U.S. news outlets.

Justice Department officials said Vardanyan and his co-conspirators received about 1,160 bitcoins — valued at more than $15 million at the time — in ransom payments from victim companies.

Prosecutors said they found no evidence Vardanyan was still engaged in criminal activity at the time of his arrest. Vardanyan’s incarceration will be followed by three years of supervised release, and his conviction will have immigration consequences resulting in removal from the United States after serving his sentence.

The post Ryuk ransomware operator sentenced to 2 years in prison appeared first on CyberScoop.

ShinyHunters claims attack on FBI exposes almost all agents

The FBI is investigating an attack on its own systems after ShinyHunters claimed responsibility for the incident, putting the prolific cybercrime group in the most direct conflict yet with agents responsible for investigating data extortion attacks.

The Monday breach, first reported by 404 Media, allowed ShinyHunters to temporarily deface the FBI jobs site. The group claimed it stole “very sensitive data on almost all FBI agents and individuals who filed an application with the FBI for a job,” in a lengthy post on its data-leak site.

“The FBI is aware of claims regarding unauthorized activity affecting FBIjobs.gov and is currently investigating,” a spokesperson for the agency said in a statement.

An alert on the FBI jobs site notes that apply.fbijobs.gov and the Special Agent Application Portal are currently unavailable.

The attack marks a sobering escalation by ShinyHunters, a notorious group that previously targeted major cloud platforms, healthcare organizations, universities, technology companies, retailers and education service providers. Previous victims of ShinyHunters this year include Instructure, Salesforce, Snowflake and McKesson.

“The ShinyHunters ransomware group appears to be actively trying to put a target on their back,” Cynthia Kaiser, senior vice president at Halcyon’s ransomware research center, told CyberScoop. 

ShinyHunters claims it targeted the FBI in response to a public service announcement it says contains false allegations about the group. The FBI issued the PSA following ShinyHunters’ May attack on Instructure, the company behind Canvas, a widely used central hub for K-12 and university coursework, exams and communication. 

The group responded with its own “PSA” on its data-leak site, insisting it is not affiliated with The Com, has never conducted swatting attacks or claimed it had sensitive or compromising information, including embarrassing photos or videos, to extort victims. 

The PSA was addressed to Brett Leatherman, assistant director of the FBI’s cyber division, and FBI Director Kash Patel. 

“While ShinyHunters has in the past been hyperbolic about the criticality of the data they’ve accessed, the group has established itself as a legitimate threat,” Flashpoint analysts told CyberScoop. 

“This attack benefits ShinyHunters by bolstering their reputation as a credible threat,” the analysts added. “In the group’s statement on their leak site regarding the breach, they portray the FBI’s PSA as an “attempt to ‘disrupt’ our operations and hinder clients’ trust in our organization hoping nobody pays us.”

The threat group typically uses social engineering, abuses weaknesses in identity systems or exploits vulnerabilities to gain access to cloud-hosted environments containing troves of sensitive or proprietary data, which it threatens to leak if the victim doesn’t pay a ransom.

ShinyHunters doesn’t appear to be seeking a payoff in this case, but rather a bid to coerce the FBI into amending or removing the May PSA. The group didn’t make any direct threat in the data-leak site post to release the stolen data, but it set a deadline of one week for action.

That coercive approach toward the FBI could backfire, according to experts. 

“Ransomware groups are largely successful because they operate like businesses,” said Kaiser, a former deputy assistant in the FBI’s cyber division. “Targeting other criminal groups or law enforcement — especially in ways intended to publicly shame — demonstrates a lack of discipline that historically has led to takedowns, takeovers or defections.”

The post ShinyHunters claims attack on FBI exposes almost all agents appeared first on CyberScoop.

Conti ransomware crew member sentenced to four years in prison

A 44-year-old Ukrainian national was sentenced to four years in prison for his long-running participation in Conti, a ransomware group that attacked more than 1,000 organizations globally before it disbanded in 2022, the Justice Department said Thursday.

Oleksii Oleksiyovych Lytvynenko, also known as Alexsey Alexseevich Litvinenko, pleaded guilty in June to conspiracy to commit wire fraud as a result of some of those attacks. At that time, he admitted he joined the prolific cybercrime group in September 2021, developed malware and held data on 12 victims, including eight based in the United States.

“For years, the Conti ransomware group executed a sustained and sophisticated campaign that victimized hundreds of organizations across the United States and abroad, including critical infrastructure entities, causing losses in the millions of dollars,” A. Tysen Duva, assistant attorney general of the Justice Department’s criminal division, said in a statement. 

“Lytvynenko joined that conspiracy as both an intruder and a developer — personally harming at least 12 companies, storing stolen data from victims, and helping build the malicious tools Conti used to extort and threaten communities,” Duva added. “Even after the Conti conspiracy ended, he continued engaging in active ransomware operations until his arrest. Cybercriminals who build, deploy, or profit from malware like Conti — no matter where they operate — will face justice and meaningful consequences in U.S. courts.”

When Lytvynenko was arrested in Ireland, where he was living with temporary protective status in July 2023, authorities said he “was asleep but within arms’ reach of an open laptop running Cobalt Strike.” He was extradited to the United States in October 2025. 

Prosecutors said Lytvynenko and his co-conspirators extorted about $634,000 in Bitcoin from two victims in Tennessee, including an undisclosed government entity that resulted in the compromise of a sheriff’s department, local emergency medical services and a local police department. According to an indictment that was unsealed last fall, Lytvynenko and his co-conspirators also leaked data they stole from another Tennessee-based victim after it refused to pay a $3 million ransom demand.

Four of Lytvynenko’s alleged co-conspirators — Maksim Galochkin, Maksim Rudenskiy, Mikhail Mikhailovich Tsarev and Andrey Yuryevich Zhuykov — were indicted in 2023 in the same federal court for crimes related to their suspected involvement in Conti attacks from 2020 to 2022. 

Conti was among the most active ransomware groups globally, impacting hundreds of critical infrastructure providers, Costa Rica’s government in 2022, and ultimately leading the State Department to offer a $10 million reward for information related to Conti’s leaders. The group was notoriously resilient, bouncing back with new infrastructure and hitting new targets after a massive leak exposed chats between the group’s members in 2022.

Conti disbanded later that year, but members of the Cyrillic-language group rebranded under three subgroups: Zeon, Black Basta and Quantum, which quickly rebranded to Royal, before rebranding again to BlackSuit in 2024.

“Lytvynenko and his co-conspirators used Conti ransomware to attack computers and networks in nearly every state, and today’s sentence reflects the gravity and extent of those crimes,” Brett Leatherman, assistant director of the FBI’s cyber division, said in a statement. 

“Ransomware criminals should know they are not anonymous and operating from overseas does not mean operating without consequences,” he added. “The FBI and our partners will use every lawful tool to dismantle their infrastructure and bring them to justice.”

The post Conti ransomware crew member sentenced to four years in prison appeared first on CyberScoop.

McKesson copes with fallout from data theft extortion attack

McKesson said its business and distribution centers remain operational in the wake of a cyberattack it disclosed Friday that resulted in data theft and temporary service interruptions.

Attackers gained access to some of the health care vendor’s third-party applications and stole data associated with a subset of customers in the company’s oncology, multispecialty and medical-surgical business units, Francisco Fraga, chief information and technology officer at McKesson, said in a statement Saturday. 

McKesson is a major player in the healthcare sector, claiming it distributes about one-third of all pharmaceuticals used throughout North America. It reported $403.4 billion in revenue for the one-year period ending in March. 

The company’s size and critical role it serves also makes it a high-profile target for cybercriminals. McKesson did not identify the group behind the attack, but ShinyHunters, a cybercrime group known for targeting large organizations with extortion demands after stealing massive amounts of sensitive data, claimed responsibility.

The company declined to answer questions about ShinyHunter’s claims. Yet, on Friday, McKesson disclosed the attack in a regulatory filing while ShinyHunters added the company to its data-leak site. 

McKesson said it discovered the attack Aug. 25. A period of widespread data theft was over by then, following a four-day intrusion beginning Aug. 21, according to researchers.

“Upon discovery, we immediately activated our incident response protocols, launched an investigation, and engaged leading cybersecurity industry experts to support our response,” Fraga said in a statement. 

“We have reasonable assurance of no ongoing unauthorized activity in our systems. Customers can continue to connect to and use our systems and services as intended,” he added. 

While McKesson’s investigation continues, it faces a more urgent deadline of Sept. 1 from ShinyHunters, which is reportedly seeking a ransom demand in excess of $55 million. 

The company did not answer questions about any ransom demand or whether it responded to the alleged attackers. 

The circumstances of the attack against McKesson are similar to other recent victims of ShinyHunters. The threat group typically uses social engineering or abuses weaknesses in identity to gain access to cloud-hosted environments containing troves of sensitive or proprietary data, which it threatens to leak if the victim doesn’t pay a ransom. 

“Opportunistic data extortionists have been able to identify weaknesses within identity and access management, making these campaigns both cheap and scalable,” said Ian Gray, vice president of cyber threat intelligence at Flashpoint. 

“These attacks are particularly difficult to detect early because they often occur entirely within vendor-hosted environments using valid, socially-engineered credentials,” he added. “Since this activity mimics normal support or data-warehouse tasks, it typically doesn’t trip traditional malware alerts or show anomalies, meaning organizations often remain unaware of the breach until the extortionists make contact.”

Researchers have linked ShinyHunters to multiple attack sprees targeting major cloud platforms, including Oracle, Salesforce and Snowflake. The decentralized crew of cybercriminals was also linked to an expansive compromise last summer impacting hundreds of Salesloft Drift customers that put any platform integrated with the AI chat agent at risk as well. 

In April, ShinyHunters broke into the systems of Canvas — a central hub for K-12 and university coursework, exams, grades and communication — causing widespread outages and data theft. When an early deadline passed without payment, ShinyHunters escalated its pressure on Instructure, the company behind Canvas, by defacing the platform’s login pages with an extortion message that was visible to hundreds of schools.

Instructure ultimately relented and said it reached an agreement with the cybercriminals, insisting the stolen data was returned with assurances that other copies were destroyed.

The FBI issued a public service announcement about ShinyHunters days later, warning potential downstream victims of the threat group’s pressure tactics and claims.

In late July, less than a month before McKesson was hit, Health-ISAC warned organizations in the sector of an increase in successful attacks by ShinyHunters.

The post McKesson copes with fallout from data theft extortion attack appeared first on CyberScoop.

ATF confirms cyberattack hit system containing info on its investigation targets

The Bureau of Alcohol, Tobacco, Firearms and Explosives insists the cyberattack that it publicly disclosed Wednesday was limited to investigation targets, and has not impacted other agency systems.

ATF said it is responding to the breach, which first became public after a prolific ransomware group claimed it accessed the federal agency’s network “The incident involved a standalone computer system containing information about targets of ATF investigations,” Tanya Roman, ATF’s public affairs chief, told CyberScoop in an email.

“The standalone system was not connected to any other ATF systems, including any case management systems, laboratory systems, or eForms systems, and it was quickly shut down when the breach was discovered,” Roman added. 

Qilin, a financially-motivated threat group composed of Russian-speaking operators, claimed responsibility for the attack, but its involvement hasn’t been independently confirmed. The group has claimed hundreds of victims from more than 60 countries since 2022 and became one of the most active ransomware threats globally by mid-2025, according to Halcyon. 

ATF declined to comment on Qilin’s alleged involvement, the root cause of the attack or when it occurred. Yet, the agency disclosed the attack hours after Qilin claimed it breached ATF’s systems.

“This is an ongoing investigation, and no further details can be shared at this time,” Roman said. 

The federal law enforcement agency, which is under the Justice Department, said senior officials designated the event a “major incident” and completed notifications. “The incident has not impacted ATF’s ability to perform its missions,” ATF said in a statement.

Qilin operates an affiliate-based ransomware model and remains highly active, claiming dozens of new victims monthly across manufacturing, health care, financial services, education and government sectors.

The FBI said Qilin was among the five-most reported ransomware variants reported to Internet Crime Complaint Center last year. Google also said the group was one of the most active ransomware brands in 2025.

The majority of Qilin’s victims are based in the United States and nearly 1 in 4 alleged targets are in the manufacturing industry, according to Halcyon. The extortion group has formed strategic partnerships with Scattered Spider and Moonstone Sleet, and uses infrastructure overlapping with BianLian. 

While Qilin has targeted organizations in the government sector before, its claimed attack against a federal law enforcement agency could mark an escalation in targeting. Yet, its objectives in this case are unclear as any ransom payment is very unlikely.

The post ATF confirms cyberattack hit system containing info on its investigation targets appeared first on CyberScoop.

Arrested man allegedly impersonated NSA elite hacking unit, Supreme Court chief justice

Colorado police arrested a man last week over charges that he impersonated both Supreme Court Chief Justice John Roberts and head of the National Security Agency’s famed Tailored Access Operations hacking unit.

Joshua Culver, also known as “Maverick Young,” appeared in a Colorado court Tuesday after his arrest stemming from an indictment in Indiana in July on four counts of falsely impersonating an officer of the court and one count of using a forged signature of a judge.

Culver allegedly pretended to be an officer of the NSA in September of last year and said in that capacity he “could take adverse action” against the Tippecanoe County sheriff’s office in Lafayette, Ind. if it didn’t provide him information he sought, including the location of his biological daughter.

He also allegedly pretended to be an NSA officer again that month, then produced a document purportedly from the head of the Tailored Access Operations (TAO) elite hacking unit in February to the Clerk of the Lake County, Ind. Superior Court.

“The document, which purported to bear official letterhead, falsely stated that it was a directive issued by the ‘Director of TAO’ and that Culver was a ‘federal asset’ active in multiple investigations,” the indictment reads. “The document commanded that certain actions be taken as required by ‘federal directive,’ including that the case pending against Culver be dismissed with prejudice, that warrants be quashed, and that Lake County officials cooperate with a ‘federal audit’ of individuals identified in the document.”

TAO has gone by the name of Office of Computer Network Operations since 2017, although in July it indicated that it was resuming its old name. TAO garnered unflattering attention in 2017 after the global WannaCry ransomware outbreak used an exploit that the NSA developed.

The indictment also alleges that Culver used a forged signature of Roberts in September for an “Order of Dismissal With Prejudice” in a case against Culver in Grant County, Indiana.

A defender appointed to Culver did not immediately respond to a request for comment Tuesday.

You can read the indictment below.

The post Arrested man allegedly impersonated NSA elite hacking unit, Supreme Court chief justice appeared first on CyberScoop.

The long tail of Clop’s PTC hack is just beginning to emerge

A notorious cybercrime group has once again exploited a critical zero-day vulnerability on a large scale, claiming it stole data from dozens of organizations, including some of the world’s largest publicly traded companies.

Clop, a prolific but calculated data theft extortion group that’s been active since 2020, began sending threatening emails to its alleged victims in mid-July, according to researchers. 

The fallout from the attack spree, which followed a familiar pattern for Clop and its targeted pool of victims, is still evolving as companies hunt for potential signs of compromise.

The vulnerability at the center of Clop’s latest campaign affects a pair of software products from PTC — Windchill and FlexPLM — which manufacturers and retailers, particularly in the manufacturing, aerospace, and automotive industries, use to automate supply chain systems and manage product lifecycles.

“This continues Clop’s trend of targeting SaaS logistics companies’ platforms with zero-days and carrying out mass-exploitation campaigns,” Allan Liska, field chief information security officer at Recorded Future, told CyberScoop.

PTC disclosed the vulnerability — CVE-2026-12569 — on June 17 and issued a patch and initial indicators of compromise the following day. 

Yet, that was too late for some of Clop’s known victims who were likely compromised by exploitation of the zero-day in early June, according to Ransom-ISAC.

The Cybersecurity and Infrastructure Security Agency added the defect, which allows unauthenticated attackers to execute code remotely, to its known exploited vulnerabilities catalog June 25.

PTC consistently added new indicators of compromise as they were discovered by researchers. But the company hasn’t said how it first became aware of the vulnerability and ensuing attacks, when the earliest known instance of exploitation occurred or how many customers are known to be compromised. 

PTC did not respond to a request for comment. 

Clop’s claimed victim set is diverse. The point-of-sale restaurant management platform Toast and software vendor Zebra both told CyberScoop they detected and contained system intrusions, but claimed limited impacts. Other alleged victims, including GE, Philips and Shell, did not respond to requests for comment. 

Researchers continue to uncover new details about the tools Clop used once it exploited and gained access to PTC customer systems. ReliaQuest said the group used a custom web shell that gave attackers a direct path to credential theft and large-scale data theft.

The fully equipped extortion platform, which was purpose-built for Windchill, decrypts credentials, delivers malware, and includes tools for sustained access, network traversal and data encryption, ReliaQuest researchers wrote in a report Tuesday.

The toolkit allows attackers to move quickly from initial access to data theft and additional post-exploitation activity without executing manual commands — a framework that mimics Windchill’s standard functions and limits defenders’ ability to detect any malicious activity.

“This campaign is another reminder that Clop remains a sleeping dragon, always looking and preparing to mass exploit vulnerabilities in software that holds sensitive data,” ReliaQuest researchers wrote in the report. “The group commonly goes inactive between campaigns but springs to life with custom-built web shells whenever there is another opportunity for mass extortion.” 

The drawn-out impact of Clop’s latest attack spree also mirrors some of its previous campaigns. The threat group has successfully exploited zero-days across multiple technology vendors’ systems, allowing it to steal sensitive data for weeks — sometimes months — from many downstream customers.

Clop targeted dozens of Oracle E-Business Suite customers for more than three months, beginning in the summer of 2025, before it started bombarding victims with extortion emails. The group also achieved mass exploitation as it infiltrated MOVEit environments in 2023, ultimately exposing data from more than 2,300 organizations, making it the largest and most significant cyberattack that year.

The post The long tail of Clop’s PTC hack is just beginning to emerge appeared first on CyberScoop.

Medusa ransomware tallies hundreds of new victims, says updated advisory on group’s tactics

The ransomware-as-a-service group Medusa has adopted fresh tactics to gain access and added hundreds of victims in a little more than a year, according to an updated U.S. government advisory published Tuesday.

The gang is relying on access brokers,compensating them anywhere from $100 to $1 million, with higher prices going to those who work exclusively with Medusa. However, most of the brokers work simultaneously for “multiple variants at the same time,” the advisory from the Cybersecurity and Infrastructure Security Agency, FBI and Health and Human Services Department states in one of the updated portions of the advisory.

Tuesday’s update advisory expands upon aMarch 2025 advisory, drawing on ongoing FBI investigations.nIt includes information on the kinds of software vulnerabilities Medusa has exploited, such as Fortra GoAnywhere and BeyondTrust flaws.

“Medusa actors operate opportunistically by targeting victims with unpatched software rather than focusing on specific organizations or sectors; however, the Healthcare and Public Health (HPH) Sector has been a frequent victim of Medusa operations,” according to the advisory. “Medusa actors leverage newly announced exploits within 24 hours and have been observed to use exploits up to a week before public vulnerability disclosure.’

“However, there is no indication Medusa actors develop their own zero-day or N-day vulnerabilities, preferring instead to obtain advanced access to exploits from unknown sources or to quickly leverage newly announced exploits before potential victims can mitigate vulnerabilities through patching,” the advisory continues.

The approach appears to be netting gains: From March 2025 to April of this year, the victim tally in the advisory jumped from more than 300 to more than 500. The group was first identified in 2021.

“Medusa actors often use legitimate tools and living off the land techniques to evade detection. They may also leverage remote monitoring and management software and remote access services, including Remote Desktop Protocol, for lateral movement,” as updated sections of the advisory detail. “Once inside a network, they use common utilities and tools to support credential access, data exfiltration, and ransomware deployment.”

Earlier this year, Microsoft detailed how a group it dubbed Storm-1175 was making use of Medusa ransomware in speedy operations. Symantec and Carbon Black also detailed earlier this year how North Korean hackers were leaning on Medusa to target the health care sector.

The post Medusa ransomware tallies hundreds of new victims, says updated advisory on group’s tactics appeared first on CyberScoop.

U.S., South Korean government agencies caution to be on lookout for Gunra ransomware gang

U.S. and South Korean cyber agencies warned Monday about a ransomware-as-a-service outfit, Gunra, that reportedly recruits ethical hackers and penetration testers and benefits from North Korean government-linked hackers’ tools to target government and critical infrastructure organizations.

Gunra has gone after sectors such as academia, financial services and insurance, government services and facilities, healthcare, manufacturing and construction, media, retail, transportation and utilities. Its global scope is far-ranging, according to Monday’s alert: Africa, the Americas, the Asia-Pacific, Europe and the Middle East.

“Gunra is another variant in the ongoing trend of ransomware attacks causing disruption and harm to U.S. and international organizations,” said Chris Butera, acting assistant director for cybersecurity at the Cybersecurity and Infrastructure Security Agency, which produced the advisory with the Department of Defense’s Cyber Crime Center, FBI, National Security Agency, Secret Service and Republic of Korea’s National Police Agency.

The alert is part of the #StopRansomware series, a joint FBI-CISA project aimed at network defenders.

The FBI first took notice of Gunra in April of last year. The double-extortion group established a data leak site on Tor to list victims and publish purloined data. By January of this year, Gunra had launched a formal ransomware-as-a-service affiliate and was growing in its ambition, Monday’s alert states.

“The FBI observed the group adopting new branding aliases (notably operating under the name Golden Community) to support this expansion,” it reads. “Gunra has further commercialized its platform by actively recruiting penetration testers and ethical hackers to serve as initial access brokers, offering a share of the ransom profits in exchange for enterprise network access.”

Gunra seeks initial access with known vulnerabilities in internet-facing devices like firewalls or virtual private networks, and is based on or influenced by the Conti ransomware code leaked in 2022, according to the agencies.

Research published in July by a South Korean cybersecurity firm took note of Gunra overlap with Lazarus Group, although it doesn’t explicitly mention the latter group’s name.

“These commonalities suggest that although the state-sponsored threat group and the Gunra ransomware group appear to be separate threat actors with different ultimate objectives, they may have shared certain techniques, tools, and infrastructure or collaborated to a limited extent during the attacks,” AhnLab wrote in its report.

That kind of North Korean government-ransomware gang collaboration dates back to at least 2024. Nor is Gunra alone among ransomware-as-a-service outfits recruiting penetration testers.

The post U.S., South Korean government agencies caution to be on lookout for Gunra ransomware gang appeared first on CyberScoop.

Ransom Cartel creator sentenced to 16 years in prison

A longtime cybercriminal was sentenced to 16 years in prison for creating and running Ransom Cartel, a ransomware strain linked to attacks on at least 18 companies between 2021 and 2023, the Justice Department said Wednesday. 

Maksim Silnikau, a Belarusian national, actively participated in Russian-speaking cybercrime forums since at least 2005, and was a member of the cybercrime site Direct Connection from 2011 to 2016, officials said. The 40-year-old created Ransom Cartel and began recruiting participants from cybercrime forums in 2021. 

Silnikau and his co-conspirators attempted to extort at least $5.2 million from victims during the multi-year scheme. 

Victims included a group of law firms, medium-sized businesses, a small medical technology startup, educational institutions and large multinational corporations based in California, New York, Nebraska and elsewhere. Some of the victims’ operations were disrupted for several months, officials said. 

Officials said Silnikau provided his co-conspirators information and tools to attack systems, including stolen credentials and mechanisms to encrypt compromised computers. He also built a site to monitor and control ongoing attacks, communicate with co-conspirators and victims, negotiate payment demands with victims and manage the distribution of funds between co-conspirators. 

Silnikau, also known as “J.P. Morgan,” “xxx,” and “lansky,” fled from Spain while awaiting extradition to the United States and was arrested in Poland in July 2023 as he tried to return to Belarus, according to court records. He was extradited to the United States in August 2023. 

Ransom Cartel’s operations ended when Silnikau was arrested. Authorities applauded his capture at the time, noting that Ransom Cartel didn’t grow large enough to inflict losses comparable to larger ransomware variants. 

Silnikau pleaded guilty to conspiracy to commit wire fraud and aggravated identity theft.

The post Ransom Cartel creator sentenced to 16 years in prison appeared first on CyberScoop.

Prolific ransomware group behind SonicWall zero-day attacks

Researchers said INC ransomware, one of the most active ransomware groups globally, has been the main attacker exploiting a pair of SonicWall zero-days soon after they were disclosed last month.

The prolific ransomware-as-a-service operation wasn’t the first group to exploit the flaws, which were actively exploited for three weeks before the vendor disclosed and patched the defects July 14, but it has been the most assertive and concerning group to target and chain both vulnerabilities together for full access.

“Since public disclosure, INC ransomware has emerged as the most commonly named threat actor actively weaponizing this vulnerability chain,” Brett Deroche, director of incident response at Rapid7, told CyberScoop. “While Inc is the name driving the post-disclosure wave, we can’t attribute the full body of exploitation to INC specifically.”

SonicWall did not respond to a request for comment.

The SonicWall vulnerabilities — CVE-2026-15409 and CVE-2026-15410 — are the latest in a series of security issues confronting the vendor’s customers, including actively exploited zero-days, previously disclosed defects, and an attack last year that allowed a state-sponsored threat group to steal the firewall configurations of every SonicWall customer. 

Just last week, Huntress researchers spotted an attack spree that compromised 30 SonicWall customers in less than two days. 

Ransomware groups have taken a special interest in SonicWall. Ten of the 17 SonicWall defects added to the Cybersecurity and Infrastructure Security Agency’s known exploited vulnerabilities (KEV) catalog since late 2021 are known to be used in ransomware campaigns.

INC ransomware, which has claimed nearly 900 victims across 71 countries since it was first discovered three years ago, is just the latest financially-motivated group to target SonicWall customers. 

Researchers haven’t determined how many organizations have been impacted by the latest SonicWall zero-days, including attacks linked to INC ransomware. 

“Attribution here isn’t a single clean answer. The earliest exploitation we observed, beginning June 22, traced back to common hosted infrastructure, though those attacks were largely unsuccessful,” Deroche said. 

“INC’s confirmed activity that we’ve observed came after public disclosure, using different infrastructure and moving from initial access to ransomware deployment in short order. That’s a meaningfully different operational tempo and skill level than what we saw pre-disclosure,” he added. 

Deroche said Rapid7 has successfully prevented data theft and encryption in the majority of recent cases, yet noted ransomware was deployed in at least one case the security vendor observed.

Yet, there could be other attacks outside the purview of Rapid7’s telemetry. INC ransomware has listed multiple new alleged victims on its data leak site, including organizations and government agencies in Australia, the United States, the United Arab Emirates, Colombia and Switzerland, Resecurity said in a blog post Saturday.

The company said it has aided several victims with incident response, and learned multiple victims received emails and phone calls from alleged hackers who pressured them to engage in negotiations.

The post Prolific ransomware group behind SonicWall zero-day attacks appeared first on CyberScoop.

Despite multiple takedowns, botnets continue to grow

Botnets powered by residential proxy networks are proliferating, enabling cybercriminals of all types to evade detection by blending in with seemingly legitimate traffic, Lumen Technology’s Black Lotus Labs said in a report Friday.

The global scale of botnets observed by Lumen is currently approaching 60 million victim IP addresses, Chris Formosa, senior lead information security engineer at Black Lotus Labs, told CyberScoop. Roughly 1 in 4 of those compromised IPs are based in the United States, and the true number of infected devices is much greater because there are networks beyond Lumen’s visibility and multiple devices are often unknowingly running a malicious proxy network on the same IP. 

Super-sized botnets are also gaining momentum, according to Lumen, with an average of 10 distinct botnets controlling their own populations of about 1 million active victims daily.

“The only reason these botnets keep getting more and more victims is because there is clearly a market. Aside from criminal activity, who wants access to millions of IPs regularly?” Formosa said. 

That demand for botnets fuels opportunities for growth, reselling, collaboration, and quick rebounds following massive disruptions.

IPIDEA, one of the largest residential proxy networks in operation when its infrastructure was disrupted by coordinated strikes in January, recovered at nearly half-strength within hours and earlier this surpassed its pre-disruption botnet size with a current botnet population of about 10 million IPs, researchers said.

“Their rebuild was eye-opening as they began to rebound from that interdiction,” Ryan English, information security engineer at Black Lotus Labs, told CyberScoop. “Even for how quickly some botnets can rebound, theirs was surprising. We’ve seen them all rebuild, but we haven’t seen anybody do it that fast.”

Meanwhile, botnets are continuously growing, as cybercriminals seek out the cover they provide, more cheap and poorly defended devices hit the market and vendors stop providing security updates for older but still usable products. 

“Your available pool for those proxy hunters grows every year, and it will continue to grow every year,” English said, adding that more than 1 billion devices are currently vulnerable and available to be unknowingly sucked up into botnets.

The challenge for defenders is lopsided, and while disruptions and seizures occur relatively often, botnet operators have formed a global supply chain with pathways that are difficult to break. 

“We have observed multiple residential proxy services collaborating to form what amounts to the largest cooperative network ever seen on the internet,” researchers wrote in the report.

Black Lotus Labs currently tracks more than 30 distinct malicious proxy botnet clusters, and most of those regularly boast more than 100,000 daily victims.

“Our understanding of the various botnets in this space, along with experience in multiple disruptions, leads us to a very important conclusion: taking down a single malicious proxy provider or their botnet in isolation is likely to result in a short-lived solution,” researchers wrote. 

“In recent years, the malicious proxy environment has essentially created the largest collective botnet currently active on the internet, capable of moving millions of IPs within hours to wherever they are needed,” they added. “Until the malicious proxy landscape is properly addressed and regulated on both the private industry and law enforcement sides, this issue will grow and, along with the DDoS botnet landscape, will most likely become a greater problem in the long term.”

The post Despite multiple takedowns, botnets continue to grow appeared first on CyberScoop.

Leading members of Scattered Spider sentenced in UK to 66 months in jail

A pair of young men were sentenced to 66 months in jail for committing a cyberattack on the Transport for London that brought the network’s operations to a standstill in 2024, the United Kingdom’s National Crime Agency said Thursday.

Thalha Jubair and Owen Flowers were arrested at their homes in September 2025, barely a year after the attack, and pleaded guilty last month just as their trials were set to begin. Flowers was previously arrested in connection with the attack in September, but was released after questioning by officers.

Jubair and Flowers were leading members and highly involved in Scattered Spider, a nebulous hacker subset of The Com, according to researchers. The 20-year-old Jubair was a prolific cybercriminal and core member of the unbound collective. 

U.S. authorities last year accused Jubair of direct, prominent involvement in at least 120 cyberattacks, including extortion of 47 U.S.-based organizations and the January 2025 attack on the federal court system. 

Officials said they traced a combined total of at least $89.5 million in cryptocurrency, at the time of payments, to Bitcoin addresses and servers controlled by Jubair. Two financial services firms paid Jubair $25 million and $36.2 million, respectively, in Bitcoin between June and November 2023, according to an unsealed criminal complaint against Jubair. 

At the time of Jubair’s arrest, “he was one of the four principal people that we associated with Scattered Spider,” and one of the two most core players, Adam Meyers, senior vice president of counter adversary operations at CrowdStrike, told CyberScoop. 

Jubair and Owens had significant resources and support, and “victim payments were reinvested back into the enterprise,” said Allison Nixon, chief research officer at Unit 221B. 

The lasting impact of Jubair and Owens’ capture and imprisonment remains hazy.

U.K. authorities insist Jubair and Owens’ arrests and punishment “effectively halted the group’s criminal activity,” yet they added that other cybercriminals continue to use the Scattered Spider brand in more recent attacks. 

Thursday’s announcement “represents a significant step in holding accountable two members of Scattered Spider, a group that has repeatedly relied on data extortion, SIM-swap attacks, and other social engineering techniques to infiltrate networks and undermine critical services,” Brett Leatherman, assistant director of the FBI Cyber Division, said in a statement. 

The FBI also noted, in a LinkedIn post, that members of Scattered Spider “continue to victimize organizations around the world and cause significant financial and operational harm.”

When Owens, now 18, was first arrested for the Transport for London attack in 2024, investigators said he was “in the process of hacking the systems of U.S. health care companies SSM Health Care Corporation and Sutter Health, which had been infiltrated and damaged.”

Officials also said Jubair and Owens failed to cooperate after their arrests. 

“This is the largest cybercrime prosecution ever brought before the U.K. courts and the culmination of nearly two years of painstaking work,” Paul Foster, head of the National Crime Center’s National Cybercrime Unit, said in a statement. 

“Scattered Spider has been the most significant cybercrime threat to the U.K. in recent years. Through this investigation, we have severely disrupted that threat and brought key offenders to justice,” Foster added.

Despite the upbeat reaction from U.K. officials, Nixon said the punishment for Jubair and Owens is “remarkably lenient considering the period of continuous reoffending lasted longer than the sentence.”

Nixon hopes the United States will eventually extradite the pair to face additional charges. “If that happens, they won’t be able to use mental illness as a loophole to get back to harming society as soon as possible,” she added.

“No one who worked on their case was surprised they would reoffend, and there seems to be no allowance in the law to protect the public from what everyone knew was going to happen,” Nixon said. “I know the narrative in the cybercriminal culture will glorify them, but they wouldn’t if they knew the full story.”

The post Leading members of Scattered Spider sentenced in UK to 66 months in jail appeared first on CyberScoop.

Russian trio indicted for allegedly running bulletproof hosting providers that spurred cybercrime

Three Russian nationals and a pair of bulletproof hosting providers directly supported a series of attacks on critical infrastructure in 21 states and several countries, according to a 2024 indictment unsealed in federal court Tuesday. 

Officials, who have been investigating the trio and their companies since 2019, said the attacks resulted in losses surpassing $62 million.

Alexander Alexandrovich Volosovik, the 43-year-old owner of Media Land; Yulia Vladimirovna Pankova, the 29-year-old owner of ML.Cloud; and 34-year-old Kirill Andreevich Zatolokin were charged with conspiracy to commit and aid computer fraud, conspiracy to commit wire fraud, wire fraud and conspiracy to commit money laundering.

The State Department also offered a reward up to $10 million for information on government-linked associates of the alleged cybercriminals and malicious use of Media Land or ML.Cloud. The Treasury Department and officials from the United Kingdom and Australia imposed sanctions on Volosovik, Zatolokin, Pankova, Media Land and ML.Cloud in November 2025. 

The three accused Russians, Media Land and ML.Cloud were all based in St. Petersburg as of 2024.

“With today’s actions, the FBI and our partners are striking at the core services that cybercriminals rely on to attack U.S. critical infrastructure,” Brett Leatherman, assistant director of the FBI Cyber Division, said in a statement. “This is another step in our broader campaign to shrink the space in which these actors can operate, forcing them to work harder, take greater risks, and lose the anonymity they depend on.”

Media Land and ML.Cloud allegedly provided cybercriminals with infrastructure and technical support to infect systems with malware and ransomware for extortion. Officials said the organizations also supported criminal marketplaces, fraudulent domain registrations and platforms that cybercriminals used to commit phishing and brute-force attacks.

Officials said they identified a consistent and long-running pattern of criminal activities facilitated by Volosovik, Pankova, Zatolokin, Media Land and ML.Cloud.

Investigators located victims across 21 states, including nine cities in the Northern District of Ohio, where the indictment was filed. Additional victims were located in Australia, the European Union, the United Arab Emirates, Canada and the United Kingdom.

Bulletproof hosting providers are increasingly used by cybercriminals to obfuscate their activities, deliver malware, phishing, and host content and services that support ransomware, data extortion and denial-of-service attacks.

“From their overseas safe haven, these defendants ran the criminal infrastructure that powered attacks on critical institutions across our nation,” A. Tysen Duva, assistant attorney general of the Justice Department’s Criminal Division, said in a statement. “Their actions put the American public at risk. We will continue to dismantle these networks and protect our critical infrastructure from cybercriminals at home and abroad.”

The post Russian trio indicted for allegedly running bulletproof hosting providers that spurred cybercrime appeared first on CyberScoop.

Treasury sanctions First VPN Service, others for abetting ransomware gangs

The Treasury Department is slapping sanctions on First VPN and its administrator for allegedly selling services to ransomware operators, as well as another person aiding ransomware gangs.

First VPN Services, or 1VPNS, was “deeply embedded in the cybercriminal ecosystem” and appeared in virtually every Europol investigation in recent years, the law enforcement body said after a sting targeting the service in May.

Treasury’s Office of Foreign Assets Control (OFAC) sanctioned 1VPNS as well as its alleged administrator, Ukrainian citizen Dmytro Rashevskyi, Monday in conjunction with the United Kingdom. The outfit provided anonymity services that could be legitimate in some instances, but 1VPNS advertised itself in online cybercrime forums for more than a decade, touting its refusal to cooperate with law enforcement, the office said.

“Numerous ransomware groups have purchased infrastructure from 1VPNS, which they have leveraged in attacks on U.S. companies and institutions — including to hide the origins of their attacks, deploy malware, and manage exfiltrated data,” OFAC said. “Victims of ransomware attacks that involved the use of 1VPNS infrastructure have included U.S. businesses, financial services companies, hospitals, and municipal governments.”

Treasury also sanctioned Belarus national Yegeniy Vladimirovich Silayev for allegedly selling “cryptors,” tools used to disguise ransomware and other malware, to ransomware operators.

“Unlike legitimate encryption tools, which are designed to protect data and the privacy of the people that own it, cryptors are built specifically to make malware stealthier and more effective by disguising it as harmless files,” OFAC said.

Treasury’s sanctions designations dovetail with separate, unrelated cyber sanctions that European governments from Monday. The FBI has previously issued an alert about First VPN Service. 

Blockchain intelligence firm TRM Labs said it has seen 1VPNS selling its services to ransomware operators for prices ranging from $723 for Anubis to $58 Sinobi.

“The amounts are small because infrastructure subscriptions are small,” Ari Redbord, global head of policy and government affairs for the company, wrote on LinkedIn. “A named ransomware group paying a named enabler on public chains still leaves a trail investigators can follow after the fact.”

Victims tied to First VPN Service infrastructure include U.S. municipalities, hospitals and financial services companies.

Europol said it had arrested the administrator of 1VPNS in its May sting, but did not name them. 

The Treasury Department did not immediately respond to a question about whether its sanctions targeted that same arrested person.

The post Treasury sanctions First VPN Service, others for abetting ransomware gangs appeared first on CyberScoop.

Armenian national pleads guilty to Ryuk ransomware attacks

An Armenian national who was extradited from Ukraine to the United States last year pleaded guilty to participating in a series of attacks in 2019 and 2020 involving Ryuk ransomware, the Justice Department said Thursday.

Karen Serobovich Vardanyan pleaded guilty to computer fraud and conspiracy to commit fraud and extortion. He agreed to pay nearly $1.2 million million in restitution and faces up to 15 years in jail.

The 34-year-old admitted to participating in cybercrime from November 2019 to April 2020 when he and his co-conspirators deployed Ryuk ransomware against three U.S.-based organizations while living in Ukraine and Russia.

Vardanyan’s victims include a Michigan-based company that paid a ransom of nearly $1.2 million in January 2020, a Watsonville, Oregon-based technology company that was attacked in December 2019 and a Texas-based school breached in February 2020.

Prosecutors previously accused Vardanyan and his co-conspirators — Ukrainian nationals Oleg Nikolayevich Lyulyava and Andrii Leonydovich Prykhodchenko, and Armenian national Levon Georgiyovych Avetisyan — of illegally accessing computer networks to deploy Ryuk ransomware on hundreds of compromised servers and workstations between March 2019 and September 2020.

Ryuk ransomware was prevalent in 2019 and 2020, infecting thousands of victims globally across the private sector, state and local municipalities, local school districts and critical infrastructure, including a wave of attacks on U.S. hospitals.

Victims of Ryuk ransomware attacks include Hollywood Presbyterian Medical Center, Universal Health Services, Electronic Warfare Associates, a North Carolina water utility and multiple U.S. newspapers.

Ryuk ransomware operators extorted victim companies by demanding ransom payments in Bitcoin in exchange for decryption keys. Justice Department officials said Vardanyan and his co-conspirators received about 1,160 bitcoins — valued at more than $15 million at the time — in ransom payments from victim companies.

Vardanyan, as part of his guilty plea, also acknowledged that his conviction will have immigration consequences resulting in removal from the United States after serving his sentence. 

The U.S. District Court for the District of Oregon has yet to schedule his sentencing.

The post Armenian national pleads guilty to Ryuk ransomware attacks appeared first on CyberScoop.

Former DigitalMint ransomware negotiator who duped clients sentenced to 70 months in jail

A former ransomware negotiator for DigitalMint was sentenced to 70 months in jail for deceiving his employer’s clients and conspiring with ransomware affiliates to extort a combined $75.3 million from five U.S. companies he was entrusted to aid during their moments of extreme crisis, the Justice Department said Thursday. 

Angelo John Martino III shared confidential information he gained from his work as a ransomware negotiator, including victim organizations’ negotiating positions and insurance policy limits, to extract the maximum payment for himself and other BlackCat affiliates he colluded with in backchannels.

Five of Martino’s victims hired DigitalMint, which assigned the 41-year-old to conduct ransomware negotiations on their clients’ behalf — a rare position he exploited to play both sides, effectively conducting ransomware negotiations with himself and his co-conspirators.

The five victims, all of which paid a ransom between April 2023 and September 2023, include a nonprofit that paid a nearly $26.8 million ransom, a financial services company that paid nearly $25.7 million, and a hospitality company that paid almost $16.5 million. 

DigitalMint hired the South Florida-based man in 2022 after he was already engaging in criminal activity, according to court records. The husband and father of two young children had a long history as a cybersecurity professional, dating back to at least 2015, with previous stints at Booz Allen Hamilton, Tracepoint and TRM Labs.

Martino surrendered to U.S. Marshals in March, was released on a $500,000 bond, and pleaded guilty in April to conspiracy to obstruct, delay or affect commerce or the movement of any article or commodity in commerce by extortion. He faced up to 20 years in prison.

Martino also admitted to conspiring with Kevin Tyler Martin, another former ransomware negotiator at DigitalMint, and Ryan Clifford Goldberg, a former manager of incident response at Sygnia, to deploy BlackCat ransomware, also known as ALPHV, against five additional U.S. companies between April and November 2023. 

Goldberg, Martin and Martino split proceeds from a nearly $1.3 million ransom payment they received from a medical company in May 2023, but did not successfully extort a financial payment from the other four victims.

Goldberg and Martin pleaded guilty in December to participating in a series of ransomware attacks and were each sentenced in April to four years in prison. 

DigitalMint insists it had no knowledge of Martino’s criminal acts. “The actions of Martino and his co-conspirators were deliberately concealed from DigitalMint and were in clear violation of the company’s values, ethical standards and the law,” a company spokesperson told CyberScoop in a statement.

The company also reiterated that it immediately terminated Martino and suspended his access to systems when the Justice Department notified the company it was investigating him in April 2025.

“DigitalMint maintained controls consistent with industry standards, including background checks and compliance procedures, but Martino intentionally hid his conduct from the company, including through separate, unauthorized communication channels that the government’s filings describe as accessible only to Martino and the BlackCat negotiators and affiliates,” the spokesperson added.

DigitalMint has yet to directly answer questions about whether it refunded its clients who were victimized by Martino. 

“We are not able to discuss specific client relationships or fee arrangements due to confidentiality obligations,” the spokesperson said. “We remain committed to our clients and will continue to maintain strict confidentiality on all commercial matters.”

The case against Martino showcases an extreme, albeit rare, example of the dark underbelly of ransomware negotiation as a practice. The pitfalls of ransomware negotiation are excessive and these backchannel negotiations, which remain largely unscrutinized, can go awry for various reasons.

Officials describe Martino as a ‘double agent’ driven by greed

Prosecutors said Martino obtained an ALPHV affiliate account that he shared with his co-conspirators and received a portion of the ransomware payments for his involvement in the conspiracy.

Authorities have seized $10 million in assets, including a bayfront home with an estimated value of $1.68 million, a second single-family home with an estimated value of $396,000, and cryptocurrency wallets controlled by Martino. Law enforcement also seized multiple vehicles, a food truck and a 29-foot luxury fishing boat that Martino obtained using proceeds from his crimes.

“Angelo Martino’s victims shared heartbreaking accounts of how their businesses were nearly destroyed, while the people they hired to help them instead betrayed them to ransomware gangs,” A. Tysen Duva, assistant attorney general at the Justice Department’s Criminal Division, said in a statement. “Today’s sentence accounts for the harm Martino caused and demonstrates that the Department of Justice can and will identify and prosecute cybercriminals to the fullest extent of the law.”

Court records include a series of chats Martino held with co-conspirators and victims that exemplify the lengths he went to betray DigitalMint’s clients and empower his accomplices with crucial tips for a successful negotiation strategy.

During an incident response with one of his victims, Martino told a BlackCat affiliate the company’s insurance carrier “was only approving small accounts,” according to his plea agreement. “Keep denying our offers and I will let you know once I find out the max the[y] want to pay,” he added.

“We don’t know how you came up with your demand but we are losing money operationally and all of our loans are going to turnover on us this year at double the interest rates,” Martino said in a negotiation chat visible to DigitalMint and the victim organization in the hospitality industry. “We are able to give you $1 million now, which is a very serious offer.”

Following Martino’s instructions, the BlackCat accomplice responded: “Well, you can keep that for the penalties and lawsuits which are coming your way in case we expose you. Time is ticking — we know how much you can pay. Contact your insurance. We know about them also. Stop wasting time.”

That victim company ultimately paid a ransom worth nearly $16.5 million at the time to receive a decryptor and the BlackCat affiliate’s commitment to not publish stolen data. Two other victims Martino represented via DigitalMint at the time paid $6.1 million and $213,000 ransoms for similar commitments.

“Angelo Martino sold out the very victims he was hired to represent, handing their confidential negotiating positions to BlackCat actors to drive up ransoms and enrich himself,” Brett Leatherman, assistant director of the FBI’s Cyber Division, said in a statement.

In a sentencing memo, federal prosecutors described Martino as a “double agent working to maximize the harm to his clients and the financial gain to cybercriminals who paid him a part of the ransom.”

Prosecutors added: “This was not a crime of opportunity or momentary weakness; it was a sustained abuse of a fiduciary-like relationship driven by a single purpose: greed.”

ALPHV/BlackCat, which first appeared in late 2021, was a notorious ransomware variant linked to a series of attacks on critical infrastructure providers. The Justice Department disrupted BlackCat in December 2023, seized sites operated by some of its affiliates, and said the FBI developed a decryption tool that helped hundreds of victims restore their systems and save about $99 million in ransom payments at the time. 

Martino is scheduled to return to court Sept. 17 to determine the amount of restitution ordered against him for his crimes.

The post Former DigitalMint ransomware negotiator who duped clients sentenced to 70 months in jail appeared first on CyberScoop.

Sysdig clocks first documented case of agentic ransomware

Artificial intelligence is claiming many firsts as it permeates every layer of technology, including the tools cybercriminals use to break into networks, steal sensitive data, hop into connected systems and deploy malware. 

This includes, for the first time, according to Sysdig researchers, a case of agentic ransomware managing an extortion operation spanning reconnaissance, credential theft, lateral movement, persistence, encryption, destruction and the delivery of the ransom note itself.

The AI agent didn’t accomplish every step in the late June 2026 attack, but it allowed the threat actor, which Sysdig tracks as JadePuffer, to significantly reduce complexity, speed up the tempo and gain operational advantages. 

“We have seen attackers script attacks for years, and we have seen AI speed up individual steps of attack chains,” Michael Clark, senior director of threat research at Sysdig, told CyberScoop. However, this recent attack was “driven end-to-end by the model’s own decision-making, rather than a human at the keyboard,” he added.

The AI-aided attack achieved initial access by exploiting a Langflow vulnerability — CVE-2025-3248 — before moving on to its intended target: a production server running MySQL and Alibaba Nacos. 

Sysdig observed multiple factors that bolstered what it described as the first documented use of agentic ransomware.

The payloads involved in the attack narrated their objectives in plain language and identified high-value databases, details that large-language models annotate by default, according to Clark. The AI agent also quickly diagnosed problems and worked around obstacles — in one case redeploying a corrected payload 31 seconds after it originally encountered an error.

Before it was all over, the AI agent ran more than 600 distinct, purposeful payloads in rapid succession.

“The model closed loops that used to require a skilled human,” Clark said. “The 31-second failure-to-fix cycle on the Nacos backdoor is the clearest example of where agentic AI gave the attacker an advantage. The agent read the error, switched its approach from subprocess calls to direct library imports, and redeployed at a speed no human matches.”

Sysdig researchers found evidence that multiple models were used in the attack. The agent accessed keys for OpenAI, Anthropic, DeepSeek and Gemini as it gathered information on the victim’s systems. The cybersecurity vendor did not name the victim.

The AI agent played a crucial role in the attack, but a person was still heavily involved, Clark said. “A human still set up and pointed the operation and provisioned the infrastructure behind it, the command-and-control server, the staging server used for the stolen data and chose a victim,” he added.

The agent also connected to the victim’s MySQL server with root credentials that were not lifted from the victim’s environment, indicating a person gained access to the credential through a prior compromise. 

The origins of JadePuffer, a financially motivated threat actor, are unknown and it doesn’t overlap with any established ransomware group or nation state, researchers said.

For Clark, there is a clear uncomfortable takeaway from this attack: “The skill floor for running a full ransomware operation just dropped to whatever it costs to run an agent,” he said. 

“We have not yet seen operations against other victims, and given how cheap this agentic ransomware operation is to run, I would expect this will not be the last.”

The post Sysdig clocks first documented case of agentic ransomware appeared first on CyberScoop.

Alleged longstanding member of Scattered Spider extradited to US

A 19-year-old alleged member of the Scattered Spider extortion crew was extradited to the United States last week and remains in federal custody awaiting several cybercrime charges, the Justice Department said Wednesday. 

Peter Stokes, a dual citizen of the United States and Estonia, was allegedly involved in Scattered Spider since it formed in 2022 and boasted on social media about the luxurious globetrotting life he enjoyed while he was still a child. 

The cybercrime ring of young, native English-speaking people has infiltrated more than 100 businesses since 2022, and extorted more than $100 million from its victims around the world, officials said. 

“Scattered Spider has repeatedly targeted U.S. companies, extorting employees, inflicting millions of dollars in losses, and disrupting essential operations,” Brett Leatherman, assistant director of the FBI’s cyber division, said in a statement. “Through strong domestic and international partnerships, the FBI will continue to identify, disrupt, and hold cybercriminals accountable, no matter where they are located.”

Stokes, also known as “Bouquet” and “Jordan,” is accused of participating in multiple data theft and extortion attempts, but the FBI only provided specific details about some more recent attacks on a luxury jewelry retailer in May 2025 and a U.S.-based insurance company in June 2025.

Cybercrime researchers have been tracking Stokes’ online activity since 2022.  Microsoft determined his true identity and implicated Stokes as a member of Scattered Spider in a criminal referral in October 2024, according to court records.

He was still a child at that time, and authorities typically don’t arrest known cybercriminals until they reach adulthood. Stokes lived in Estonia and the United Arab Emirates while he allegedly committed some of his crimes. 

Police arrested Stokes in Finland as he attempted to board an April 10 flight to Japan, possessing two hard drives containing allegedly incriminating evidence. He made an initial court appearance in Chicago Tuesday and was ordered to remain in jail.

Stokes exhibited an opulent life before his capture, according to his social media activity and State Department travel records. This included trips and multiple stays in luxury hotels in Paris, Italy, Spain, Germany, New York, Florida, New Mexico, Thailand and Dubai between 2024 and 2025, according to a criminal complaint filed against him in the U.S. District Court for the Northern District of Illinois.

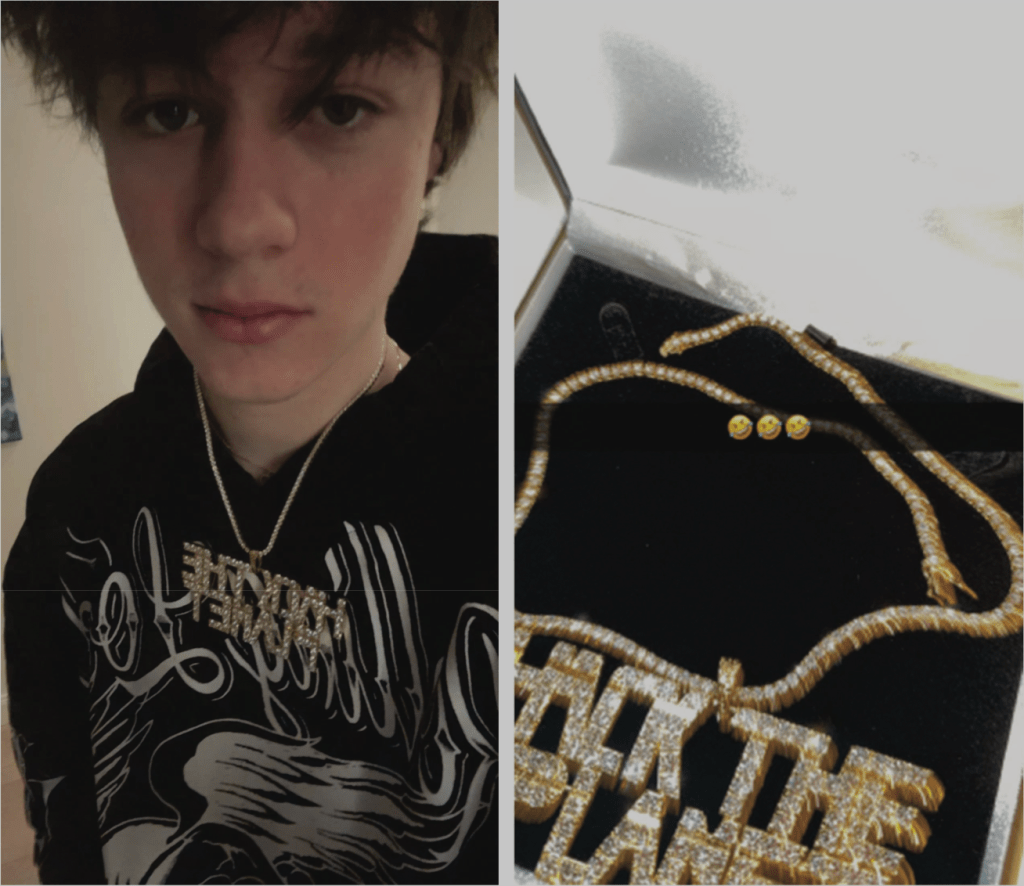
He also posted images of watches, substantial cash and an apparently diamond-encrusted chain depicting the words “Hack the Planet.”

Images from Peter Stokes’ Snapchat account in February 2025 and December 2024. Credit: Justice Department

Officials also noted that Stokes’ family appeared to be well off, as his father was a previous executive in two major European companies. 

Stokes was charged with conspiracy, cyber intrusion and fraud offenses.

“The malicious attacks from Scattered Spider caused widespread disruption to businesses and organizations throughout the United States,” Andrew Boutros, U.S. attorney for the Northern District of Illinois, said in a statement. “These charges underscore our unwavering commitment to keeping pace with technologically savvy criminal actors and holding accountable those who seek to profit from cyber intrusions, including those located in foreign jurisdictions who do harm to American businesses and victims.”

The post Alleged longstanding member of Scattered Spider extradited to US appeared first on CyberScoop.

❌