❌

Reading view

There are new articles available, click to refresh the page.

What Democratic control of Congress means for cybersecurity

Democrats’ big win on Election Day, which saw them take control of both the House and Senate, has ramifications for the Cybersecurity and Infrastructure Security Agency, artificial intelligence, surveillance policy and much more.

Here’s what lawmakers and cybersecurity experts have to say about the short-term and long-term prospects on Capitol Hill.

Leadership plans ahead

Maggie Hassan, D-N.H. is in line to take the gavel on the Senate Homeland Security and Governmental Affairs Committee, with Sen. Gary Peters, Mich., retiring.

“Our government’s number one job is to keep people safe, and the Senate Homeland Security and Governmental Affairs Committee must work to ensure that our country remains safe, secure and free from all kinds of threats,” Hassan said in a statement to CyberScoop. “That work involves protecting against terrorism and fentanyl trafficking, but it also includes guarding against emerging threats like artificial intelligence security risks and strengthening our cybersecurity.”

“The Trump-Vance administration has undermined our security on these fronts, including by diverting resources away from combatting fentanyl trafficking and gutting CISA,” she continued. “We need to reverse these cuts, confront these challenges and put public safety first.”

Rep. Bennie Thompson, D-Miss., is poised to return once again as chair of the House Homeland Security Committee, said Democrats are taking over at a “pivotal time for CISA,” with it looking to add staff after cutting back by nearly one-third.

“First and foremost, we will aim to work with CISA to expedite its critical re-staffing effort and to ensure it has the expertise necessary to support stakeholders as they defend against the scale and velocity of AI-enabled cyber-attacks,” he said in a statement to CyberScoop. “Advances in AI can help defenders, but it will also accelerate the consequences of deferred investments in security and CISA must be well-positioned to help critical infrastructure owners and operators rapidly improve their cybersecurity posture.”

“We will prioritize getting resources straight into the hands for defenders — by extending the State and Local Cybersecurity Grant Program and improving support of under-resourced sectors, especially water,” he continued. “We will work to ensure CISA re-establishes its cross-sector coordination capacity, which was diminished when the Trump administration- terminated CIPAC, by making sure the Anchor-CI is eventually up and running and meets the needs of stakeholders. Finally, we will make sure CISA is well-positioned to support the secure development and deployment of AI.”

What happens in the lame-duck session

Before the GOP relinquishes control of the House and Senate to Democrats, though, there’s a lame-duck session ahead. 

Long-term renewal of the Cybersecurity Information Sharing Act of 2015 (CISA 2015) is a bipartisan and industry priority, with it set to expire Dec. 11. Current Senate Homeland Security and Governmental Affairs Chairman Rand Paul, R-Ky., has been the biggest obstacle to reauthorization, but he could get “rolled” by GOP leadership on an extension, said Michael Garcia, a former government cyber official and vice president of the cybersecurity practice at Monument Advocacy. Possible vehicles for CISA 2015 to hitch a ride include an omnibus funding bill or the annual defense policy bill.

The Department of Homeland Security, and its subagency CISA, are currently operating on a continuing resolution that’s also set to expire Dec. 11, where lawmakers could temporarily extend CISA 2015 if a long-term solution can’t be reached in the lame duck. Another continuing resolution before Dec. 11 in lieu of an omnibus spending bill is an option for the lame duck. Both a CR and omnibus spending bill would theoretically include DHS funding, although the agency’s funding has been made more difficult in the past by the presence of Immigration and Customs Enforcement within the department.

Republicans have talked about wanting to get the fiscal 2027 National Defense Authorization Act done in the lame duck. Besides the possibilities of CISA 2015 being included in the bill, Nicholas Leiserson, senior vice president for policy at the Institute for Security and Technology, said the Senate version of the legislation has a pair of very noteworthy cyber provisions: a “very broad” authorization for contractor-owned, contractor-operated offensive cyber operations, and a requirement that every artificial intelligence product sold to the Defense Department have an AI bill of materials.   

Additional leadership shuffle

While Paul is losing his gavel, he’s shown he can be a disruptive force on passing cybersecurity legislation through the Senate in the minority. That makes what he does next possibly determinative for cyber bills, Leiserson and Garcia said. “If he leaves HSGAC, let a thousand cyber bills flourish!” Garia quipped on social media. Paul could opt to become the top Republican on the Senate Health, Education, Labor and Pensions Committee instead of HSGAC.

Nebraska Sen. James Lankford would take over for Paul as top HSGAC Republican in that scenario, and an industry source said he’s viewed as a supporter of CISA 2015.

On Senate Intelligence, the panel’s leadership goes to a lawmaker who has placed a big emphasis on cybersecurity in his congressional career: Mark Warner, D-Va. 

On the House side, while Rep. Andrew Garbarino, R-N.Y., moves to the minority on the Homeland Security panel, he has proven willing to collaborate with Democrats on cybersecurity issues. Rep. Delia Ramirez, D-Ill., is poised to take the gavel of the panel’s cybersecurity subcommittee, and Rep. Vince Fong, R-of California looks set to become the subcommittee’s top Republican and has his own history of bipartisanship. Fong would replace current subcommittee chair Andy Ogles, the far-right Tennessee Republican who lost in the primaries.

One thing to watch in the House, Leiserson said, is how the House looks to tackle AI — through existing committees, a select committee or some other structure. Democrats haven’t put forward a unified front on AI guardrails yet.

With AI models uncovering as many vulnerabilities as they are, “highly capable frontier models are going to drive a lot of discussion” about AI and cybersecurity, said Craig Albright, the Business Software Alliance’s senior vice president for U.S. government relations.

Appropriations, oversight, legislation

If the NDAA or a CISA 2015 extension don’t pass in the lame duck, they’d be priorities in 2027, too.

“CISA 2015 has to happen, and if we can’t get it done, then we can’t move to the next thing,”  said Henry Young, BSA’s policy director. “Once we get it done, there’s an open question about which of these priorities that we’ve talked about gets to be number one. Is it post-quantum cryptography? Is it government IT modernization? Is it frontier AI cybersecurity systems? We don’t know that yet, and we can’t know until we pass this law.”

How damaged the agency CISA is by Trump administration’s budget cuts is something Democrats are expected to scrutinize closely. Another top budget issue is what to do with the expired State and Local Cybersecurity Grants Program housed at DHS, since even if it’s reauthorized, it will require appropriators taking steps to invest in it.

Democrats could take a look at a variety of other Trump administration changes at DHS and CISA, on topics like election security, the Cyber Safety Review Board, the Joint Cyber Defense Collaborative and more. 

More broadly, Leiserson said an area of Democratic cyber oversight is likely to be the Department of Government Efficiency that cut cyber personnel at agencies at and beyond CISA, and “particularly the integrity of systems that DOGE touched when they were given very high privileged access to federal systems.”

If the White House puts forward a permanent nominee for director of CISA, Democrats would be poised to vet that person. They also would have a say in who leads the Office of the National Cyber Director, should the incumbent, Sean Cairncross, depart.

So far, Democrats haven’t put forward a unified posture on expired surveillance authorities known as Section 702, although both Warner and incoming House Intelligence Chairman Jim Himes, D-Conn., have fought in the past for its renewal. The surveillance program is operating similarly still due to a court order, but that order only lasts through next spring.

The post What Democratic control of Congress means for cybersecurity appeared first on CyberScoop.
All the security risks Anthropic is worried about before its IPO 

Anthropic said its AI systems could drastically reshape the software and cybersecurity sectors in the “near term,” while also laying out a litany of cybersecurity and regulatory risks facing the company as it prepares to go public.

In a filing with the Securities and Exchange Commission ahead of its initial public offering, the company said its technology could transform entire industries and the economy. Already, cybersecurity-focused models by Anthropic and rival OpenAI can find and exploit cybersecurity vulnerabilities at an alarming speed.

But the company also acknowledged serious risks its models, including Claude, pose to itself, its users and the world. Hacks by bad actors using Claude or AI agents could cause financial, legal or physical damage, spark lawsuits and affect Anthropic’s ability to insure against future losses. 

Anthropic expects bad actors, including foreign governments, to increase their efforts to access its latest frontier models as their cybersecurity capabilities improve. That creates persistent risk, since its models could be used in cyberattacks carried out by foreign governments and cybercriminal groups.

“Any successful attempt to misuse, or any perceived misuse of, our models, platform, and applications for a cyberattack or for any other malicious purpose could result in exposure to liability, disruption of our customer or other commercial relationships, or damage to our reputation,” Anthropic said in its filing.

That potential legal and regulatory risk extends to independent security researchers and others who have “used, and may in the future use, our models to identify and exploit vulnerabilities in the systems of other companies, including other AI developers, at times in connection with authorized bug bounty programs.”

Anthropic cited the rise of AI-enabled cybersecurity incidents in the U.S., the U.K. and other countries, saying they could result in more adversarial regulatory environments around the world. European laws, for example, require detailed breach reports within a strict time frame, which could be difficult for Anthropic to meet.

Federal intervention could also disrupt AI development and release timelines. Anthropic cited the Department of Commerce placing export controls on its Mythos 5 and Fable 5 models, and confirmed that the Federal Trade Commission issued it a civil investigative demand earlier this month for more information on the safety and security of its products, as well as its consumer, data and privacy protection policies.

AI development will be guided by more than ethics

Anthropic has developed a public reputation as an ethics-first AI company,  most notably in disputes with the Department of Defense over how its models are used in wartime. But the IPO filing states the company must “balance safety considerations against commercial objectives, competitive pressures, and stakeholder expectations.”

The company also said it is “actively” improving security infrastructure and controls. It also has acknowledged it has moved forward on projects with “known limitations or gaps in our defenses” and may do so again.

“There can be no assurance, however, that the safeguards or access regimes we adopt will prove adequate, that we will correctly identify which capabilities require restriction, or that constraints we impose will not be circumvented,” the document stated.

AI agents can create new and “distinct” cybersecurity attack surfaces because they interact with so many other tools, databases, APIs and other third-party systems. That creates  feedback loops between a model and other systems, which can be compromised or manipulated to feed malicious instructions to the agent.

Anthropic suggested the problems could be so pronounced that it may have difficulty obtaining insurance for some cybersecurity incidents and data breaches related to its models.  

Andrew Yoon, head of research at the nonprofit CivAI, told CyberScoop that both the document and Anthropic’s overall record show a company that has consistently put profit considerations over building safer AI.

“I think in general they’re not meeting the moment here,” Yoon said. “Despite all of these risks that they flagged, they’re moving ahead pretty much as fast as humanly possible, and their justification for this is ‘You can’t do safety from second place.’”

Yoon said Anthropic has not only pushed its own frontier research toward dangerous and harmful capabilities like hacking, “they are pushing very aggressively ahead” and in some cases influencing competitors to follow suit. Anthropic’s release of its Mythos and Fable models earlier this year caused OpenAI to shift “its entire corporate strategy” to match the capabilities of Anthropic models in coding, science, and general intelligence by building models at breakneck speed.

“They have pretty directly caused the industry to speed up toward this mad, frenzied race and yet they’re saying ‘Oh, our models are too powerful,’ ”….it just doesn’t add up to me,” said Yoon.

But Yoon said it’s not clear that building AI systems to carry out dangerous, complex activities like hacking or bioweapons is necessary to be competitive in the global marketplace. He pointed to the wide assortment of Chinese-developed, open-weight AI models that are widely used around the world, but are not powerful enough to chain together complex exploits or develop new viruses.  

“This is not an accident, this is not the models generalizing from regular programming capabilities…the labs are intentionally training them on hacking as well,” said Yoon. “This is because they want to offer better defensive capabilities, they want to be able to sell offensive products to the government…and they do pretty cavalier testing with [the models] inside the labs.”

The post All the security risks Anthropic is worried about before its IPO  appeared first on CyberScoop.

Alleged Kimwolf Botmaster ‘Dort’ Arrested, Charged in U.S. and Canada

Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. KrebsOnSecurity publicly named the suspect in February 2026 after the accused launched a volley of DDoS, doxing and swatting campaigns against this author and a security researcher. He now faces criminal hacking charges in both Canada and the United States.

A criminal complaint unsealed today in an Alaska district court charges Jacob Butler, a.k.a. “Dort,” of Ottawa, Canada with operating the Kimwolf DDoS botnet. A statement from the Department of Justice says the complaint against Butler was unsealed following the defendant’s arrest in Canada by the Ontario Provincial Police pursuant to a U.S. extradition warrant. Butler is currently in Canadian custody awaiting an initial court hearing scheduled for early next week.

The government said Kimwolf targeted infected devices which were traditionally “firewalled” from the rest of the internet, such as digital photo frames and web cameras. The infected systems were then rented to other cybercriminals, or forced to participate in record-smashing DDoS attacks, as well as assaults that affected Internet address ranges for the Department of Defense. Consequently, the DoD’s Defense Criminal Investigative Service is investigating the case, with assistance from the FBI field office in Anchorage.

“KimWolf was tied to DDoS attacks which were measured at nearly 30 Terabits per second, a record in recorded DDoS attack volume,” the Justice Department statement reads. “These attacks resulted in financial losses which, for some victims, exceeded one million dollars. The KimWolf botnet is alleged to have issued over 25,000 attack commands.”

On March 19, U.S. authorities joined international law enforcement partners in seizing the technical infrastructure for Kimwolf and three other large DDoS botnets — named Aisuru, JackSkid and Mossad — that were all competing for the same pool of vulnerable devices.

On February 28, KrebsOnSecurity identified Butler as the Kimwolf botmaster after digging through his various email addresses, registrations on the cybercrime forums, and posts to public Telegram and Discord servers. However, Dort continued to threaten and harass researchers who helped track down his real-life identity and dramatically slow the spread of his botnet.

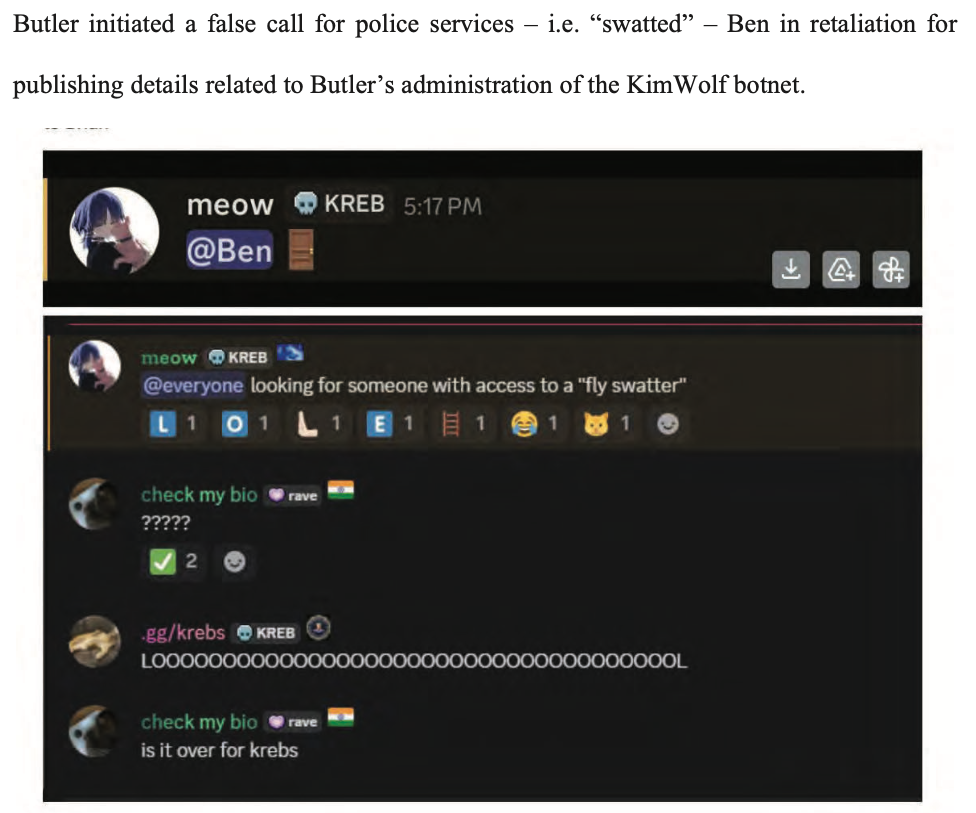
Dort claimed responsibility for at least two swatting attacks targeting the founder of Synthient, a security startup that helped to secure a widespread critical security weakness that Kimwolf was using to spread faster and more effectively than any other IoT botnet out there. Synthient was among many technology companies thanked by the Justice Department today, and Synthient’s founder Ben Brundage told KrebsOnSecurity he’s relieved Butler is in custody.

“Hopefully this will end the harassment,” Brundage said.

An excerpt from the criminal complaint against Butler, detailing how he ordered a swatting attack against Ben Brundage, the founder of the security firm Synthient.

The government says investigators connected Butler to the administration of the KimWolf botnet through IP address, online account information, transaction records, and online messaging application records obtained through the issuance of legal process. The criminal complaint against Butler (PDF) shows he did little to separate his real-life and cybercriminal identities (something we demonstrated in our February unmasking of Dort).

In April, the Justice Department joined authorities across Europe in seizing domain names tied to nearly four-dozen DDoS-for-hire services, although because of a bureaucratic mix-up the list of seized domains has remain sealed until today. The DOJ said at least one of those services collaborated with Butler’s Kimwolf botnet.

A statement from the Ontario Provincial Police said a search warrant was executed on March 19 at Butler’s address in Ottawa, where they seized multiple devices. As a result of that investigation, Butler was arrested and charged this week with unauthorized user of computer; possession of device to obtain unauthorized use of computer system or to commit mischief; and mischief in relation to computer data. He is scheduled to remain in custody until a hearing on May 26.

In the United States, Butler is facing one count of aiding and abetting computer intrusion. If extradited, tried and convicted in a U.S. court, Butler could face up to 10 years in prison, although that maximum sentence would likely be heavily tempered by considerations in the U.S. Sentencing Guidelines, which make allowances for mitigating factors such as youth, lack of criminal history and level of cooperation with investigators.

❌