❌

Reading view

There are new articles available, click to refresh the page.

‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help

The Trump administration rolled out a six-month test program in Texas on Monday that will draw on volunteer expertise and technology from cyber and artificial intelligence companies to protect the water sector.

“Project Watershed 250” is the first of the state-based, industry-centric pilot projects to cross the finish line that the Office of the National Cyber Director has previewed since the publication of its national cybersecurity strategy earlier this year. Water systems have long been viewed as among the most vulnerable and neediest critical infrastructure sectors, and in recent months the sector has been the victim of a spree of attacks.

“Project Watershed 250 is a commitment from the states, industry and federal government that we will continue to prioritize our nation’s safety and deliver on America-first policies for the American people,” National Cyber Director Sean Cairncross said at a rollout event in San Antonio Monday.

“U.S. companies are providing world-class cyber capabilities, red teaming that tests utilities’ current defenses, system hardening using the latest private sector cyber tools and AI tooling that helps utilities’ frontier cyber defenders to protect Texas water systems and scale proven solutions across the country,” he said. “This six-month pilot program is designed to make our water and wastewater critical infrastructure more resilient and resistant to cyber attacks by proactively finding and fixing system weaknesses.”

The pilot program, featuring collaboration between federal and state governments, stands in contrast to how the Biden administration tried to tackle the issue, with audit requirements that some GOP states challenged in court, forcing Biden’s Environmental Protection Agency to withdraw its rule.

“For too long, at least on the federal level, the government has admired the problem of cybersecurity in water systems,” Cairncross said. “We are going to find out what works. We’re going to target that, and we are going to scale off of this and learn lessons.”

A dozen companies — Parsons, Microsoft, Fortinet, Google Cloud, Palo Alto Networks, Amazon Web Services, Reflection AI, Cloudflare, Zscaler, Forescout, Abnormal AI and Dragos — appeared at the rollout Monday to praise the initiative and tout their contributions to it.

Not everyone praised the initiative elsewhere, however. One cyber professional who works on water security issues, speaking on condition of anonymity, said the program was “all smoke” and that “there’s no real money behind it.”

“The White House did what it always does — reached out to industry with their hands out asking for industry to pay for things the government should be doing, at least in part,” the person said.

Texas Gov. Greg Abbott said the program would be overseen by Cairncross’s office and Texas Cyber Command, which was established just last year. Abbott cited the need for the program by mentioning “an Iranian-backed cyberattack” on 30 water systems across 12 states and a 2024 attack on the water system in Muleshoe, Texas, suspected to be the work of Russian hackers.

“The need for cyber resilience is overwhelming,” Abbott said. “Many rural providers simply don’t have the resources they need to be able to protect themselves.”

Watershed 250 isn’t the only federal effort to bolster water cybersecurity, with lawmakers introducing legislation in the aftermath of the recent attacks. Past legislation that Congress has enacted also sought to tackle the problem.

Updated 8/31/26: with comment from cyber professional.

The post ‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help appeared first on CyberScoop.

Unit 42 warns AI has shifted balance of power from defenders to attackers

Unit 42’s top brass has seen enough from internal frontier AI model testing and malicious in-the-wild use of commercially available AI tools to be genuinely concerned.

“I can tell you without exaggeration that we believe that this is a generational shift in cybersecurity,” Sam Rubin, senior vice president of Palo Alto Networks’ threat intelligence arm, said in a media briefing Wednesday. 

A period of relative balance between security and exposure has been broken by frontier AI model capabilities that could allow attackers to find and exploit network weaknesses with speed, Rubin said.

Unit 42 warned that capabilities demonstrated by readily available agentic AI models, and those unlocked by frontier AI models that remain gated for defense, have shifted the balance of power from defenders to attackers.

“The defenses that we’ve had built up over years weren’t necessarily built for or prepared for these machine-speed attacks,” Rubin said. “Organizations are ill-equipped to detect and to respond quickly in the face of these attacks.

Back in April, when Anthropic brought Palo Alto Networks and other major technology companies together to form Project Glasswing, an initiative to find and address security defects with its Mythos model, Unit 42 estimated the same capabilities would be in the hands of attackers within a year. 

“Well, here we are five months later, and we’re starting to see the early waves of this threat in the wild,” Rubin said. 

Unit 42 is actively investigating an attack on one of its customers where an attacker used an agentic framework to exploit 50 applications and other weaknesses across the enterprise in less than 10 hours. Rubin estimates AI allowed the attacker to accomplish in 10 hours what would have taken at least 10 days in a pre-AI era. 

Attackers are already using AI across the entire attack chain, said Sherrod DeGrippo, vice president of threat intelligence at Unit 42. “We are not far from fully agentic attacks across all at once, but right now it’s piece by piece by piece,” she said. 

“AI has seeped into every part of what threat actors do,” including malware development at scale, delegation, social engineering and ransomware negotiations, DeGrippo added.

As such, she sees the threat landscape shifting in four areas. AI is a force multiplier, identity is the primary compromise vector, attackers are burrowing into foundational libraries and software supply chains “baked into the fabric of our digital world,” and nation-sponsored threat groups are learning more about points of weakness in enterprise systems, DeGrippo said.

Nobody is fully prepared for what’s coming and it would be naive or a bad defender mindset to think otherwise, she said. “This is a transformative period, and how organizations navigate that transformation is going to be make-or-break for a lot of them.”

The post Unit 42 warns AI has shifted balance of power from defenders to attackers appeared first on CyberScoop.

Iran-Backed Hackers Claim Wiper Attack on Medtech Firm Stryker

A hacktivist group with links to Iran’s intelligence agencies is claiming responsibility for a data-wiping attack against Stryker, a global medical technology company based in Michigan. News reports out of Ireland, Stryker’s largest hub outside of the United States, said the company sent home more than 5,000 workers there today. Meanwhile, a voicemail message at Stryker’s main U.S. headquarters says the company is currently experiencing a building emergency.

Based in Kalamazoo, Michigan, Stryker [NYSE:SYK] is a medical and surgical equipment maker that reported $25 billion in global sales last year. In a lengthy statement posted to Telegram, a hacktivist group known as Handala (a.k.a. Handala Hack Team) claimed that Stryker’s offices in 79 countries have been forced to shut down after the group erased data from more than 200,000 systems, servers and mobile devices.
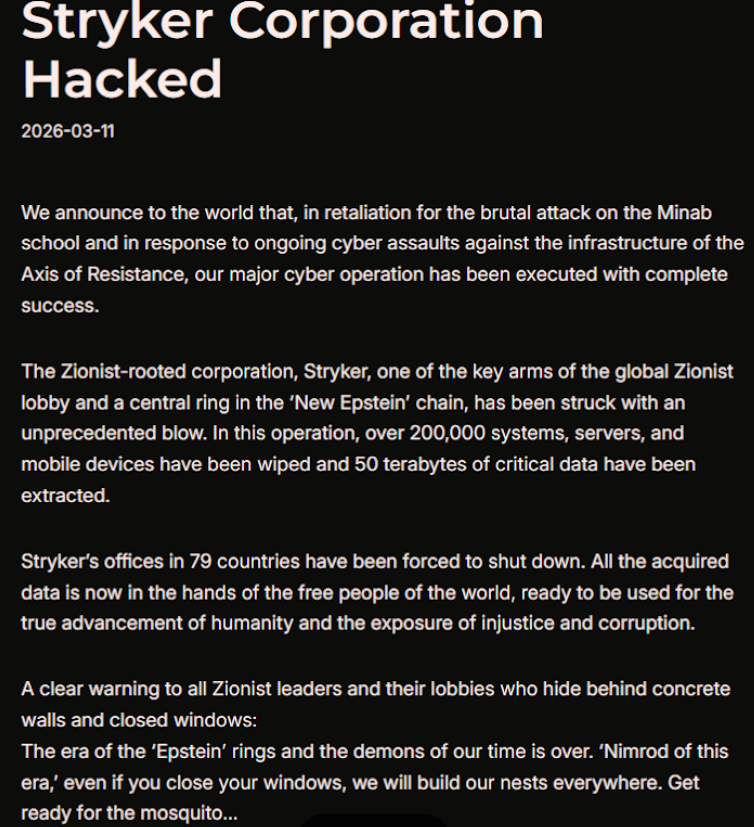
A manifesto posted by the Iran-backed hacktivist group Handala, claiming a mass data-wiping attack against medical technology maker Stryker.

A manifesto posted by the Iran-backed hacktivist group Handala, claiming a mass data-wiping attack against medical technology maker Stryker.

“All the acquired data is now in the hands of the free people of the world, ready to be used for the true advancement of humanity and the exposure of injustice and corruption,” a portion of the Handala statement reads.

The group said the wiper attack was in retaliation for a Feb. 28 missile strike that hit an Iranian school and killed at least 175 people, most of them children. The New York Times reports today that an ongoing military investigation has determined the United States is responsible for the deadly Tomahawk missile strike.

Handala was one of several hacker groups recently profiled by Palo Alto Networks, which links it to Iran’s Ministry of Intelligence and Security (MOIS). Palo Alto says Handala surfaced in late 2023 and is assessed as one of several online personas maintained by Void Manticore, a MOIS-affiliated actor.

Stryker’s website says the company has 56,000 employees in 61 countries. A phone call placed Wednesday morning to the media line at Stryker’s Michigan headquarters sent this author to a voicemail message that stated, “We are currently experiencing a building emergency. Please try your call again later.”

A report Wednesday morning from the Irish Examiner said Stryker staff are now communicating via WhatsApp for any updates on when they can return to work. The story quoted an unnamed employee saying anything connected to the network is down, and that “anyone with Microsoft Outlook on their personal phones had their devices wiped.”

“Multiple sources have said that systems in the Cork headquarters have been ‘shut down’ and that Stryker devices held by employees have been wiped out,” the Examiner reported. “The login pages coming up on these devices have been defaced with the Handala logo.”

Wiper attacks usually involve malicious software designed to overwrite any existing data on infected devices. But a trusted source with knowledge of the attack who spoke on condition of anonymity told KrebsOnSecurity the perpetrators in this case appear to have used a Microsoft service called Microsoft Intune to issue a ‘remote wipe’ command against all connected devices.

Intune is a cloud-based solution built for IT teams to enforce security and data compliance policies, and it provides a single, web-based administrative console to monitor and control devices regardless of location. The Intune connection is supported by this Reddit discussion on the Stryker outage, where several users who claimed to be Stryker employees said they were told to uninstall Intune urgently.

Palo Alto says Handala’s hack-and-leak activity is primarily focused on Israel, with occasional targeting outside that scope when it serves a specific agenda. The security firm said Handala also has taken credit for recent attacks against fuel systems in Jordan and an Israeli energy exploration company.

“Recent observed activities are opportunistic and ‘quick and dirty,’ with a noticeable focus on supply-chain footholds (e.g., IT/service providers) to reach downstream victims, followed by ‘proof’ posts to amplify credibility and intimidate targets,” Palo Alto researchers wrote.

The Handala manifesto posted to Telegram referred to Stryker as a “Zionist-rooted corporation,” which may be a reference to the company’s 2019 acquisition of the Israeli company OrthoSpace.

Stryker is a major supplier of medical devices, and the ongoing attack is already affecting healthcare providers. One healthcare professional at a major university medical system in the United States told KrebsOnSecurity they are currently unable to order surgical supplies that they normally source through Stryker.

“This is a real-world supply chain attack,” the expert said, who asked to remain anonymous because they were not authorized to speak to the press. “Pretty much every hospital in the U.S. that performs surgeries uses their supplies.”

John Riggi, national advisor for the American Hospital Association (AHA), said the AHA is not aware of any supply-chain disruptions as of yet.

“We are aware of reports of the cyber attack against Stryker and are actively exchanging information with the hospital field and the federal government to understand the nature of the threat and assess any impact to hospital operations,” Riggi said in an email. “As of this time, we are not aware of any direct impacts or disruptions to U.S. hospitals as a result of this attack. That may change as hospitals evaluate services, technology and supply chain related to Stryker and if the duration of the attack extends.”

According to a March 11 memo from the state of Maryland’s Institute for Emergency Medical Services Systems, Stryker indicated that some of their computer systems have been impacted by a “global network disruption.” The memo indicates that in response to the attack, a number of hospitals have opted to disconnect from Stryker’s various online services, including LifeNet, which allows paramedics to transmit EKGs to emergency physicians so that heart attack patients can expedite their treatment when they arrive at the hospital.

“As a precaution, some hospitals have temporarily suspended their connection to Stryker systems, including LIFENET, while others have maintained the connection,” wrote Timothy Chizmar, the state’s EMS medical director. “The Maryland Medical Protocols for EMS requires ECG transmission for patients with acute coronary syndrome (or STEMI). However, if you are unable to transmit a 12 Lead ECG to a receiving hospital, you should initiate radio consultation and describe the findings on the ECG.”

This is a developing story. Updates will be noted with a timestamp.

Update, 2:54 p.m. ET: Added comment from Riggi and perspectives on this attack’s potential to turn into a supply-chain problem for the healthcare system.

Update, Mar. 12, 7:59 a.m. ET: Added information about the outage affecting Stryker’s online services.

❌