❌

Reading view

There are new articles available, click to refresh the page.

The long tail of Clop’s PTC hack is just beginning to emerge

A notorious cybercrime group has once again exploited a critical zero-day vulnerability on a large scale, claiming it stole data from dozens of organizations, including some of the world’s largest publicly traded companies.

Clop, a prolific but calculated data theft extortion group that’s been active since 2020, began sending threatening emails to its alleged victims in mid-July, according to researchers. 

The fallout from the attack spree, which followed a familiar pattern for Clop and its targeted pool of victims, is still evolving as companies hunt for potential signs of compromise.

The vulnerability at the center of Clop’s latest campaign affects a pair of software products from PTC — Windchill and FlexPLM — which manufacturers and retailers, particularly in the manufacturing, aerospace, and automotive industries, use to automate supply chain systems and manage product lifecycles.

“This continues Clop’s trend of targeting SaaS logistics companies’ platforms with zero-days and carrying out mass-exploitation campaigns,” Allan Liska, field chief information security officer at Recorded Future, told CyberScoop.

PTC disclosed the vulnerability — CVE-2026-12569 — on June 17 and issued a patch and initial indicators of compromise the following day. 

Yet, that was too late for some of Clop’s known victims who were likely compromised by exploitation of the zero-day in early June, according to Ransom-ISAC.

The Cybersecurity and Infrastructure Security Agency added the defect, which allows unauthenticated attackers to execute code remotely, to its known exploited vulnerabilities catalog June 25.

PTC consistently added new indicators of compromise as they were discovered by researchers. But the company hasn’t said how it first became aware of the vulnerability and ensuing attacks, when the earliest known instance of exploitation occurred or how many customers are known to be compromised. 

PTC did not respond to a request for comment. 

Clop’s claimed victim set is diverse. The point-of-sale restaurant management platform Toast and software vendor Zebra both told CyberScoop they detected and contained system intrusions, but claimed limited impacts. Other alleged victims, including GE, Philips and Shell, did not respond to requests for comment. 

Researchers continue to uncover new details about the tools Clop used once it exploited and gained access to PTC customer systems. ReliaQuest said the group used a custom web shell that gave attackers a direct path to credential theft and large-scale data theft.

The fully equipped extortion platform, which was purpose-built for Windchill, decrypts credentials, delivers malware, and includes tools for sustained access, network traversal and data encryption, ReliaQuest researchers wrote in a report Tuesday.

The toolkit allows attackers to move quickly from initial access to data theft and additional post-exploitation activity without executing manual commands — a framework that mimics Windchill’s standard functions and limits defenders’ ability to detect any malicious activity.

“This campaign is another reminder that Clop remains a sleeping dragon, always looking and preparing to mass exploit vulnerabilities in software that holds sensitive data,” ReliaQuest researchers wrote in the report. “The group commonly goes inactive between campaigns but springs to life with custom-built web shells whenever there is another opportunity for mass extortion.” 

The drawn-out impact of Clop’s latest attack spree also mirrors some of its previous campaigns. The threat group has successfully exploited zero-days across multiple technology vendors’ systems, allowing it to steal sensitive data for weeks — sometimes months — from many downstream customers.

Clop targeted dozens of Oracle E-Business Suite customers for more than three months, beginning in the summer of 2025, before it started bombarding victims with extortion emails. The group also achieved mass exploitation as it infiltrated MOVEit environments in 2023, ultimately exposing data from more than 2,300 organizations, making it the largest and most significant cyberattack that year.

The post The long tail of Clop’s PTC hack is just beginning to emerge appeared first on CyberScoop.
Germany Doxes “UNKN,” Head of RU Ransomware Gangs REvil, GandCrab

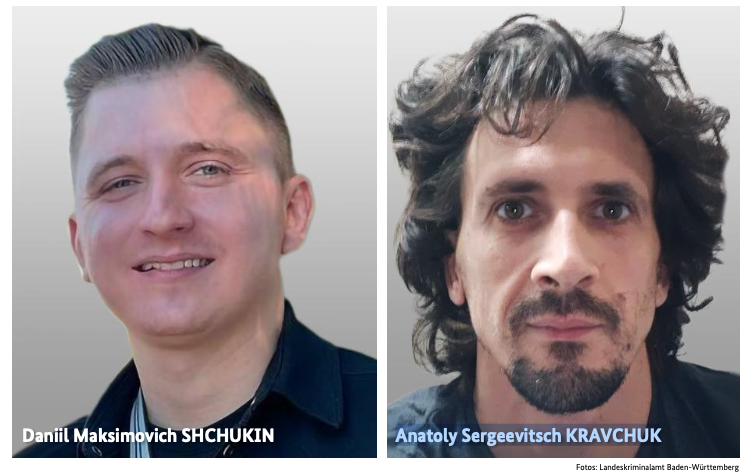
An elusive hacker who went by the handle “UNKN” and ran the early Russian ransomware groups GandCrab and REvil now has a name and a face. Authorities in Germany say 31-year-old Russian Daniil Maksimovich Shchukin headed both cybercrime gangs and helped carry out at least 130 acts of computer sabotage and extortion against victims across the country between 2019 and 2021.

Shchukin was named as UNKN (a.k.a. UNKNOWN) in an advisory published by the German Federal Criminal Police (the “Bundeskriminalamt” or BKA for short). The BKA said Shchukin and another Russian — 43-year-old Anatoly Sergeevitsch Kravchuk — extorted nearly $2 million euros across two dozen cyberattacks that caused more than 35 million euros in total economic damage.

Daniil Maksimovich SHCHUKIN, a.k.a. UNKN, and Anatoly Sergeevitsch Karvchuk, alleged leaders of the GandCrab and REvil ransomware groups.

Germany’s BKA said Shchukin acted as the head of one of the largest worldwide operating ransomware groups GandCrab and REvil, which pioneered the practice of double extortion — charging victims once for a key needed to unlock hacked systems, and a separate payment in exchange for a promise not to publish stolen data.

Shchukin’s name appeared in a Feb. 2023 filing (PDF) from the U.S. Justice Department seeking the seizure of various cryptocurrency accounts associated with proceeds from the REvil ransomware gang’s activities. The government said the digital wallet tied to Shchukin contained more than $317,000 in ill-gotten cryptocurrency.

The GandCrab ransomware affiliate program first surfaced in January 2018, and paid enterprising hackers huge shares of the profits just for hacking into user accounts at major corporations. The GandCrab team would then try to expand that access, often siphoning vast amounts of sensitive and internal documents in the process. The malware’s curators shipped five major revisions to the GandCrab code, each corresponding with sneaky new features and bug fixes aimed at thwarting the efforts of computer security firms to stymie the spread of the malware.

On May 31, 2019, the GandCrab team announced the group was shutting down after extorting more than $2 billion from victims. “We are a living proof that you can do evil and get off scot-free,” GandCrab’s farewell address famously quipped. “We have proved that one can make a lifetime of money in one year. We have proved that you can become number one by general admission, not in your own conceit.”

The REvil ransomware affiliate program materialized around the same as GandCrab’s demise, fronted by a user named UNKNOWN who announced on a Russian cybercrime forum that he’d deposited $1 million in the forum’s escrow to show he meant business. By this time, many cybersecurity experts had concluded REvil was little more than a reorganization of GandCrab.

UNKNOWN also gave an interview to Dmitry Smilyanets, a former malicious hacker hired by Recorded Future, wherein UNKNOWN described a rags-to-riches tale unencumbered by ethics and morals.

“As a child, I scrounged through the trash heaps and smoked cigarette butts,” UNKNOWN told Recorded Future. “I walked 10 km one way to the school. I wore the same clothes for six months. In my youth, in a communal apartment, I didn’t eat for two or even three days. Now I am a millionaire.”

As described in The Ransomware Hunting Team by Renee Dudley and Daniel Golden, UNKNOWN and REvil reinvested significant earnings into improving their success and mirroring practices of legitimate businesses. The authors wrote:

“Just as a real-world manufacturer might hire other companies to handle logistics or web design, ransomware developers increasingly outsourced tasks beyond their purview, focusing instead on improving the quality of their ransomware. The higher quality ransomware—which, in many cases, the Hunting Team could not break—resulted in more and higher pay-outs from victims. The monumental payments enabled gangs to reinvest in their enterprises. They hired more specialists, and their success accelerated.”

“Criminals raced to join the booming ransomware economy. Underworld ancillary service providers sprouted or pivoted from other criminal work to meet developers’ demand for customized support. Partnering with gangs like GandCrab, ‘cryptor’ providers ensured ransomware could not be detected by standard anti-malware scanners. ‘Initial access brokerages’ specialized in stealing credentials and finding vulnerabilities in target networks, selling that access to ransomware operators and affiliates. Bitcoin “tumblers” offered discounts to gangs that used them as a preferred vendor for laundering ransom payments. Some contractors were open to working with any gang, while others entered exclusive partnerships.”

REvil would evolve into a feared “big-game-hunting” machine capable of extracting hefty extortion payments from victims, largely going after organizations with more than $100 million in annual revenues and fat new cyber insurance policies that were known to pay out.

Over the July 4, 2021 weekend in the United States, REvil hacked into and extorted Kaseya, a company that handled IT operations for more than 1,500 businesses, nonprofits and government agencies. The FBI would later announce they’d infiltrated the ransomware group’s servers prior to the Kaseya hack but couldn’t tip their hand at the time. REvil never recovered from that core compromise, or from the FBI’s release of a free decryption key for REvil victims who couldn’t or didn’t pay.

Shchukin is from Krasnodar, Russia and is thought to reside there, the BKA said.

“Based on the investigations so far, it is assumed that the wanted person is abroad, presumably in Russia,” the BKA advised. “Travel behaviour cannot be ruled out.”

There is little that connects Shchukin to UNKNOWN’s various accounts on the Russian crime forums. But a review of the Russian crime forums indexed by the cyber intelligence firm Intel 471 shows there is plenty connecting Shchukin to a hacker identity called “Ger0in” who operated large botnets and sold “installs” — allowing other cybercriminals to rapidly deploy malware of their choice to thousands of PCs in one go. However, Ger0in was only active between 2010 and 2011, well before UNKNOWN’s appearance as the REvil front man.

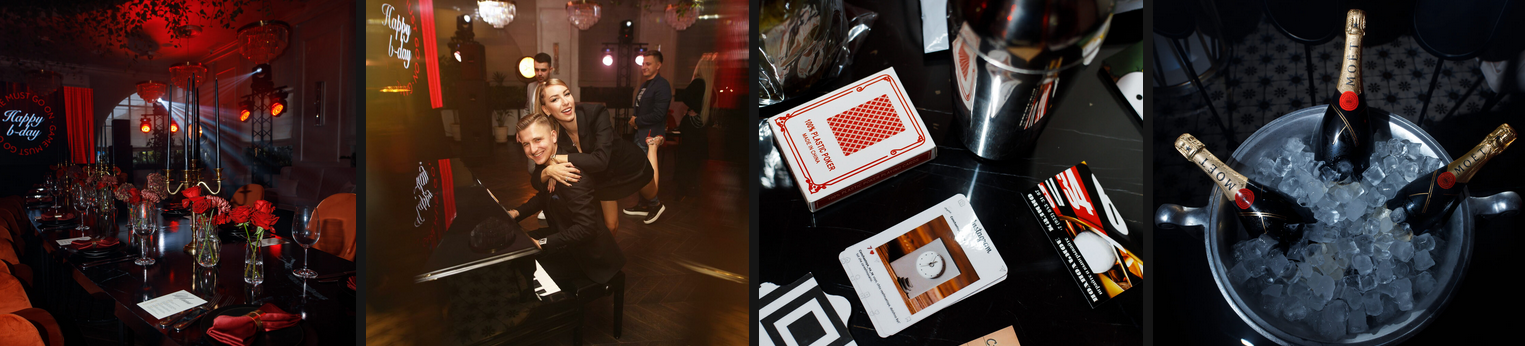
A review of the mugshots released by the BKA at the image comparison site Pimeyes found a match on this birthday celebration from 2023, which features a young man named Daniel wearing the same fancy watch as in the BKA photos.

Images from Daniil Shchukin’s birthday party celebration in Krasnodar in 2023.

Update, April 6, 12:06 p.m. ET: A reader forwarded this English-dubbed audio recording from a ccc.de (37C3) conference talk in Germany from 2023 that previously outed Shchukin as the REvil leader (Shchuckin is mentioned at around 24:25).

❌