❌

Reading view

There are new articles available, click to refresh the page.

CISA Announces Enhanced Reporting Form for Cyber Incidents

A press release from the Cybersecurity and Infrastructure Security Agency (CISA) today: Today, the Cybersecurity and Infrastructure Security Agency (CISA) unveiled the updated cyber incident reporting form, an enhanced web-enabled questionnaire available on CISA’s Incident Reporting Portal for reporting cyber incidents. By improving data quality, the more robust form strengthens the effectiveness and efficiency of...

Astraeus — Maybe we can hope that Windows 27 will be like this

FREEWARE SPOTLIGHT By Deanna McElveen Zipping around the sky in my car with the new Windows 27 running on my brain implant, I will enjoy my music, weather forecasts, system info, calendars, and my everyday tools and settings. They will be displayed in a single panel that appears when I need it and goes away […]

Coding Agents Copy Your Secrets to a Hidden File. Thousands Are on GitHub (2)

Shmulik Cohen and Matan Giladi write: Apiiro research found 2,539 real secrets in 1,994 public GitHub repositories: database passwords, cloud keys, API tokens, SSH root logins. Among them: a database vendor’s own admin-level cloud key, a production Azure Postgres password, a Square production token, and the owner password of a medical-records database. 63 organizations, mostly...

Norad targeted by cyberattack

From Norway’s aid agency, Norad, November 3: Norad has been targeted by a cyberattack in which the perpetrators may have gained access to the names and email addresses of 20,614 registered users of Norad’s Grant Portal. In addition, they extracted information related to grant applications submitted by at least three organizations. Norad is still working...

Canadian man extradited to the U.S. for his role in computer hacking scheme targeting universities

November 3, 2026: ROCHESTER, N.Y.-U.S. Attorney Michael DiGiacomo announced today that a federal grand jury has returned an indictment charging Ryan James Roach, 35 of Saskatchewan, Canada, and Mathiew James Stubbings, 41, of Ontario, Canada, with conspiracy to obtain information from a protected computer and to cause damage to a protected computer, obtaining information from a...

Syrian Man Sentenced for Wide-Ranging Hacking Conspiracy Conducted on Behalf of the Bashar Al Assad Regime

Ahmad Umar Agha (also known as Th3Pr0) had spent more than a decade as a fugitive for targeting of Western media entities, businesses, NGOs, and U.S. and allied government entities October 29 – Today a federal district court in the Eastern District of Virginia sentenced Ahmad Umar Agha to 42 months in prison for his...

Navigate360’s lack of transparency is catching up with them; More organizations tell people NOT to use their tiplines.

Multiple Ontario Crime Stoppers organizations have suspended use due to Navigate360’s data breach and unacceptable incident response; U.S. state education departments are collaborating to seek more answers from Navigate360; an update from DataBreaches.net. Toronto Crime Stoppers didn’t take long to respond after Valérie Ouellet and Michelle Allan dove into the Crime Stoppers data in the...

Attorney General Tong Announces $625,000 Settlement with Frontier Over Data Breach

Connecticut Attorney General William Tong has been active in litigating data breaches. The press release below relates to a 2024 breach of Frontier Communications by RansomHub: Attorney General William Tong today announced a $625,000 settlement with Frontier Communications Parent Inc., resolving an investigation into an April 2024 data breach that compromised the sensitive personal information,...

Source

Spyware found on devices belonging to prominent Serbian critics as elections loom

Spyware has been detected on devices used by some of Serbia’s most prominent figures connected to the country’s political upheaval, according to researchers who announced their findings Monday.

Vladan Ðokić, the rector of the University of Belgrade and prominent figure in the country’s student protest moment, and Rade Bajić, a lawyer with Serbia’s Public Prosecutor’s Office for Organized Crime, were targeted, according to research from the SHARE Foundation, a Serbian digital rights group, and The Citizen Lab at the University of Toronto.

The new cases follow what the SHARE Foundation described in September as the largest documented wave of spyware surveillance in the country to date. That wave included 14 people, among them a member of parliament and a local government official, targeted with Pegasus and a new version of the NoviSpy Android spyware.

Đokić, an architect and former dean of the university’s Faculty of Architecture, has led the University of Belgrade since 2021. He has publicly backed the student-led anti-corruption protests that followed the 2024 Novi Sad railway station canopy collapse, and government officials and pro-government news outlets have portrayed him as a driving force behind the movement.

His tenure has included direct confrontations with the government. In March, Serbian authorities raided his offices, and reportedly seized computers and servers. After the incident, Đokić accused authorities of trying to humiliate the institution, saying police entered without prior notice or clear legal grounds.

Andrijana Ristić, a researcher at the SHARE Foundation, whose organization conducted the initial forensic analysis, said the case is the second confirmed Pegasus infection in Serbia this year. She declined to say when the infection was discovered, citing the sensitive nature of the investigation.

The device was then given to The Citizen Lab to further confirm that Pegasus was used.

“We found with high confidence that it was infected with NSO Group’s Pegasus spyware in 2026,” a report released by the lab reads. “The infection leveraged a zero-click exploit. No action, such as a click or opening a file was necessary for infection.”

Ðokić was unavailable for comment. 

Bajić was on the legal team prosecuting a high-profile corruption case involving Serbian government officials signing off on a $500 million hotel and residential tower planned for a protected historic site in Belgrade. According to recent reporting from The Guardian, Serbian President Aleksandar Vučić allegedly pressed government officials to strip the building’s protection so that Affinity Partners, the private investment firm owned by Jared Kushner, could develop it into a Trump hotel. 

Bajić believes his work on the case led to him being a target of spyware. He pointed CyberScoop to news articles and Serbian television programs where Vučić referred to him as a “criminal” and part of a “gang that fabricated” the corruption case. 

“In my opinion, my involvement in this case was the sole reason for this unlawful spyware attack,” Bajić told CyberScoop.

Ristić told CyberScoop that Bajić received a threat notification from Apple, but neither SHARE nor Citizen Lab could pinpoint exactly what type of spyware his device was infected with. The investigation of Bajić’s device is ongoing.

Ristić described surveillance in Serbia as longstanding, tracing it to earlier tools such as FinFisher and alleged dealings with the hacking group Hacking Team — along with the original NoviSpy report by Amnesty International in 2024, which identified journalists, activists and civil society members as targets.

“I would definitely say that [spyware] is widespread,” she told CyberScoop. “I think right now it’s gaining much more media attention, especially internationally, because of the political moment.”

John Scott-Railton, senior researcher at The Citizen Lab, said “NSO has spent a decade claiming to turn over a new leaf each time an abuse surfaces. But there is no hiding the truth: Pegasus is a technology for repression. So it’s no accident that people standing up for freedom in the face of corruption keep getting hacked with NSO’s products.”

Serbia will hold parliamentary elections Oct. 25, with Vučić fighting to retain control of the government. The vote comes amid the student-led protest movement, fueled by anger over government corruption, that has grown into the largest challenge to Vučić’s rule in years.

The post Spyware found on devices belonging to prominent Serbian critics as elections loom appeared first on CyberScoop.

U.K. Sanctions Cryptomus for RU Money Laundering

The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions.

Heleket’s support agent on Telegram claims, despite all evidence to the contrary, that it is not affiliated with Cryptomus. Image: Richard Sanders.

On October 8, the U.K. issued sanctions (PDF) against Cryptomus — previously known as Certa Payments and Xeltox Enterprises — for processing payments that benefit the Russian government and its financial institutions. The sanctions freeze any Cryptomus assets at U.K. banks, and bar British companies from offering it any business, virtual or otherwise. Also targeted in these sanctions were the virtual payment platforms VexPay, TokenSpot, and the Tsunami Payments service.

As explained in our December 2024 investigation, “How Cryptocurrency Turns to Cash in Russian Banks,” Cryptomus has been a key payment processor for dozens of Russian cryptocurrency exchanges and websites hawking cybercrime services. The company has changed its name several times since emerging in 2022, most recently to “Heleket” last year after Canada levied a record CAD $176 million fine against the platform for anti-money laundering violations.

The blockchain data-crunching firm Chainalysis said the U.K. sanctions target the broader infrastructure supporting Russia’s wartime economy.

“Cryptomus and Heleket have emerged as major payment hubs for illicit activity,” Chainalysis wrote in an October 8 blog post. “Together, these services received more illicit funds across tracked categories than the mixers in our dataset and the number of illicit counterparties surged to more than 900 in a single month in late 2025.”

The Cryptomus support bot on Telegram, responding on Oct. 8 to an inquiry by saying the platform was suddenly unable to process transactions.

In April 2026, the blockchain analysis firm TRM Labs found Cryptomus had processed more than $7 billion in transactions since its inception in 2022, including transactions associated with child sexual abuse material vendors, terrorist financing networks, and human trafficking operations.

TRM noted that Cryptomus’s transaction volume cratered after the platform instituted new “know your customer” or KYC rules, and that the cryptocurrency platform responded to the Canadian fines by launching Heleket as a parallel service that continued to offer no-KYC payment processing.

Richard Sanders is a blockchain analyst and investigator who spent months mapping out Cryptomus’s payment infrastructure and transacting with its customers. Sanders said the U.K. sanctions on Cryptomus are important because Canada’s fine against the platform was ultimately unenforceable and uncollectible.

“A fine doesn’t stop a cryptocurrency payment processor from processing payments,” Sanders wrote on LinkedIn. “Sanctions kill the operation. The distinction matters.”

As our 2024 investigation noted, Cryptomus shared a Vancouver address with dozens of other foreign currency dealers and money transfer businesses — none of which appeared to be physically located there. Following the CAD $176 million fine for alleged money laundering violations, Cryptomus appealed the penalty, launched Heleket as a parallel service, and kept on processing large volumes of sketchy transactions, Sanders said.

Sanders said the sanctions also are notable because they are the first known instance of a “Five Eyes” country (referring to the Australia, Canada, New Zealand, the U.K. and the U.S.) sanctioning a cryptocurrency operation incorporated in another Five Eyes jurisdiction.

Where do entities like Cryptomus and Heleket derive their authority to offer international financial services? The answer appears to involve fake financial institutions overseen by a phony regulatory body positioned in a country that is not widely recognized as a sovereign nation.

Our 2024 investigation found the sole shareholder of Cryptomus’s parent company Certa Payments was a 25-year-old Ukrainian woman who also headed several other firms, including the WS Management and Advisory Corporation, which bills itself as the regulatory body that exclusively oversees licenses for cryptocurrency, foreign exchange and online gaming businesses incorporated in the disputed region in northwest Africa known as the Western Sahara.

That entity’s website — crasadr.com — says it assists applicants with bank setup and formation, online gaming licenses, and the creation and licensing of foreign exchange brokers. One of Certa Payments’ former sites — certa[.]website — also shared a server with 12 other domains, including rasd-state[.]ws, a website for the Central Reserve Authority of the Western Sahara.
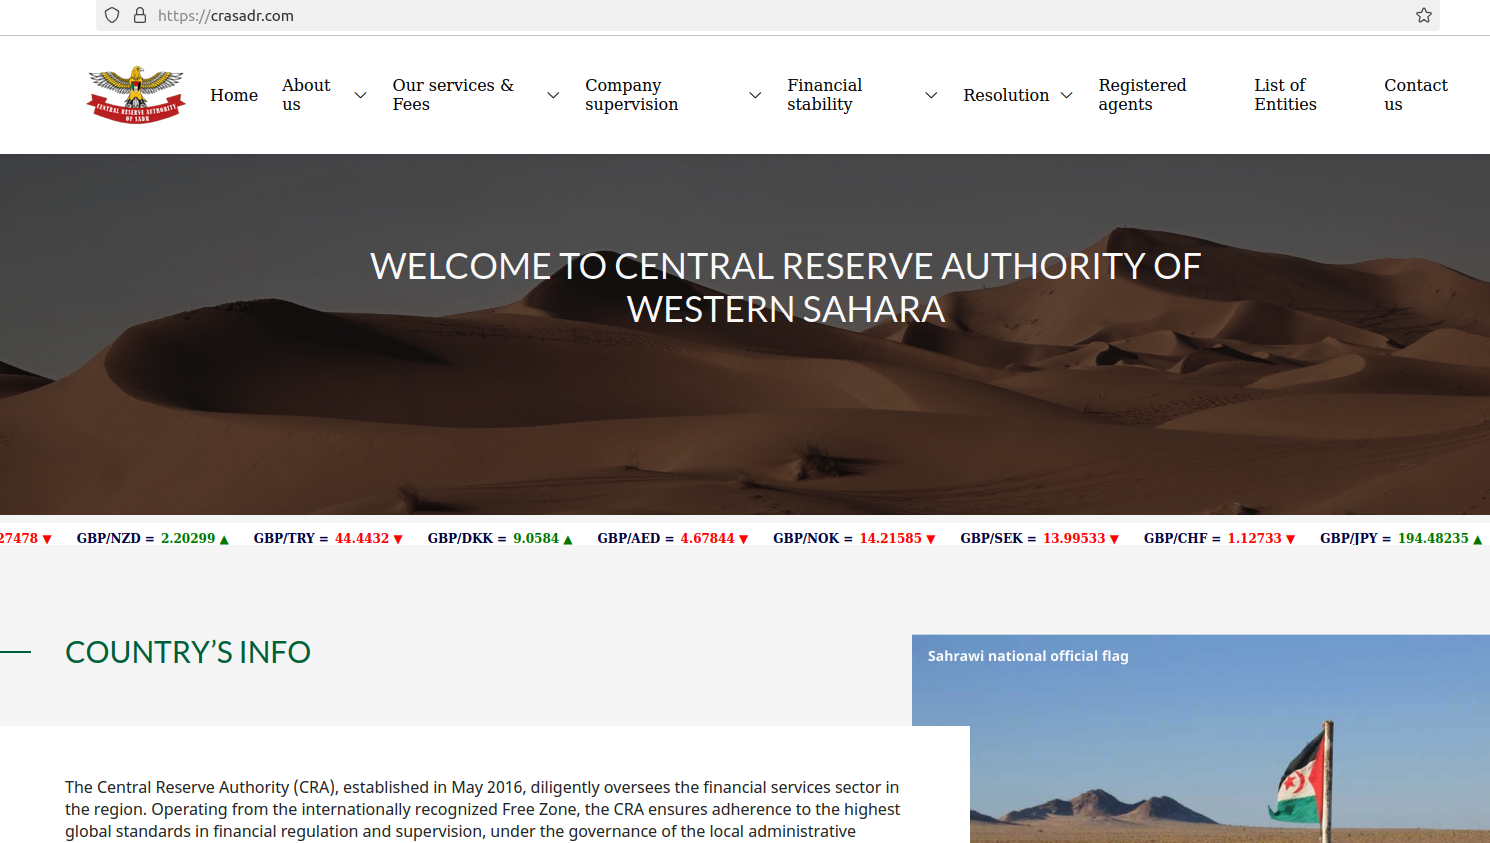
The website crasadr dot com, the official website of the Central Reserve Authority of Western Sahara, which lists the entities awarded licenses for cryptocurrencies, gaming and foreign exchange services.

Shipping firms and ports caught in mass cyber extortion claim

Bojan Lepic reports: A cyber extortion group has threatened to publish data it claims it stole from 38 shipping, port, and logistics companies unless they pay multimillion-dollar ransoms by October 19. Cybersecurity firm SOCRadar said the group, known as n0n, added the 38 organisations to its dark web leak site in a single batch on...

Source

Known Cybersecurity Expert and Owner of Florida Ransomware Remediation Company Charged with Defrauding Clients

Here’s another case where the folks who were supposed to be the good guys helping you may be harming you. Zohar Pinhasi, 50, also known as “Zack Silver” and “Zack Green,” a U.S. and Israeli national, was arraigned today in the Eastern District of New York on wire fraud charges relating to Pinhasi’s false representations...

Source

AI on your machine

The other day, a reader posed an interesting question about how one can tell whether they have inadvertently installed AI on their computer.  Most of the time, we know when we are installing or using AI. We download Claude. We launch perplexity.ai. In Office we look for the colorful icon and launch Copilot. In an […]

Self-described “cybersecurity engineer” arrested after computer case reopened

Natalie Dreier reports: A Florida man who calls himself a “cybersecurity engineer” on TikTok and Twitch was arrested after police reopened an investigation closed earlier this year. Mark Asea was held in the St. Lucie County Jail in Port St. Lucie, Florida, last week on a count of an offense against computer users, WPEC reported....

Source

❌