❌

Reading view

There are new articles available, click to refresh the page.

Authorities seize KillSec extortion group infrastructure, arrest 3 alleged members

Authorities arrested the alleged leader and two additional members of KillSec, a data extortion group primarily run by teenagers that successfully compromised about 500 organizations since 2024, Europol and the Justice Department said Thursday.

Investigators said the alleged leader of the group is 16 years old, but declined to name them. One of the group’s accused members, Fouad Eltibrizi, was arrested Wednesday in the United Kingdom and awaits extradition to the United States, the Justice Department said. 

The Dutch national, who is accused of acting as a negotiator for the group, was indicted last month in Puerto Rico and faces up to 10 years in prison for unauthorized computer access conspiracy. Europol said a suspected developer involved in the group committed multiple crimes before they turned 18 in August.

The arrests were part of “Operation KillSwitch,” a globally coordinated operation aided by 10 countries and private cybersecurity companies. Officials seized KillSec’s data-leak site and at least 110 terabytes of data, including information on the group’s criminal proceeds.

Law enforcement’s accumulated actions targeting KillSec’s infrastructure and people involved “imposed serious cost and degraded the adversary’s core capabilities,” the FBI’s Cyber Division said in a statement on X.

“We have undermined the group’s ability to rebuild, limited their operational reach and reduced the likelihood of future attacks,” the FBI added.

Europol said investigators gained control of domains and five central servers, including infrastructure the group used to manage its activities and store stolen data.

The cybercrime group, which was also known as Kill Security Ransomware Group, exploited various defects to intrude victims’ computers or cloud-based network infrastructure and steal sensitive data for extortion demands. Officials said the group obtained substantial ransom payments in some cases. 

Officials from the United States and Europe searched eight residences in Spain, Greece, the United Kingdom and Romania, and investigators are looking through evidence seized during those raids to identify other potential members of the group. 

Some of the group’s victims were identified by initials and the location and date of the attack in the indictment filed against Eltibrizi. This list includes I.D.O. in Puerto Rico in March 2025, U.S.B.L. in Washington state in March 2025 and A.A. in Louisiana in September 2025.

Three of those victims align with organizations that were listed on KillSec’s data-leak site for Instituto de Ojos, US BioTek Laboratories and Accelerated Academy. 

Prosecutors accuse Eltibrizi, who allegedly participated in the conspiracy from at least March through November 2025, of placing calls as a KillSec representative in at least one of those extortion demands. 

“The defendant and his co-conspirators carried out targeted intrusions against multiple companies and organizations, stealing highly sensitive information and attempting to extort their victims for substantial sums of money,” Héctor Ramírez‑Carbó, acting U.S. attorney for the District of Puerto Rico, said in a statement.

“Ransomware remains a serious and evolving threat to all sectors of our economy, from critical infrastructure to small businesses,” he added.

The post Authorities seize KillSec extortion group infrastructure, arrest 3 alleged members appeared first on CyberScoop.
Russian national extradited to US for alleged involvement in bank-account takeover scheme

Authorities extradited a 36-year-old Russian national from the Republic of Georgia under accusations of widespread bank-account takeover attacks, including a scheme to defraud two banks of more than $6.3 million, the Justice Department said Tuesday.

Sergei Anatolyevich Filimonov and unnamed co-conspirators ran an extensive operation starting in November 2023 to spoof domains of banks, obtain credentials of legitimate customers and use those details to steal money from accounts with large balances, according to court records. 

Filimonov and his co-conspirators allegedly collected more than 5,000 victim login credentials to various banks, including those assigned to employees with access to a company headquartered in Atlanta and another business with offices in Cumming, Ga.

Authorities said Filimonov and his co-conspirators registered and maintained spoofed domains of banks, purchased sponsored links to direct unsuspecting victims to those domains, and stole credentials from those banks’ customers when they attempted to log into the fraudulent sites.

The alleged bank-account takeover crew also created infrastructure to store victim login credentials and tricked victims into providing additional details to bypass security controls.

Prosecutors said Filimonov and his co-conspirators caused and attempted to cause the unauthorized transfer of nearly $5.58 million from one unnamed bank in June 2024 and $735,000 from another bank in November 2024. Both banks have local branches in the Northern District of Georgia and maintain headquarters in North Carolina, according to the indictment. 

Officials previously seized the domain, which the co-conspirators allegedly used to store credentials harvested from the spoofed banking sites in December 2025. The FBI at the time said it identified at least 19 victims in the U.S. linked to the domain and put total attempted losses at about $28 million, including confirmed losses of about $14.6 million. 

Filimonov is charged with conspiracy to commit bank and wire fraud, access device fraud conspiracy, multiple counts of bank and wire fraud, possession of unauthorized access devices and aggravated identity theft. He faces up to 175 years in prison. 

He pleaded not guilty Sept. 4 and remains detained in the Northern District of Georgia.

The post Russian national extradited to US for alleged involvement in bank-account takeover scheme appeared first on CyberScoop.

Ransom Cartel creator sentenced to 16 years in prison

A longtime cybercriminal was sentenced to 16 years in prison for creating and running Ransom Cartel, a ransomware strain linked to attacks on at least 18 companies between 2021 and 2023, the Justice Department said Wednesday. 

Maksim Silnikau, a Belarusian national, actively participated in Russian-speaking cybercrime forums since at least 2005, and was a member of the cybercrime site Direct Connection from 2011 to 2016, officials said. The 40-year-old created Ransom Cartel and began recruiting participants from cybercrime forums in 2021. 

Silnikau and his co-conspirators attempted to extort at least $5.2 million from victims during the multi-year scheme. 

Victims included a group of law firms, medium-sized businesses, a small medical technology startup, educational institutions and large multinational corporations based in California, New York, Nebraska and elsewhere. Some of the victims’ operations were disrupted for several months, officials said. 

Officials said Silnikau provided his co-conspirators information and tools to attack systems, including stolen credentials and mechanisms to encrypt compromised computers. He also built a site to monitor and control ongoing attacks, communicate with co-conspirators and victims, negotiate payment demands with victims and manage the distribution of funds between co-conspirators. 

Silnikau, also known as “J.P. Morgan,” “xxx,” and “lansky,” fled from Spain while awaiting extradition to the United States and was arrested in Poland in July 2023 as he tried to return to Belarus, according to court records. He was extradited to the United States in August 2023. 

Ransom Cartel’s operations ended when Silnikau was arrested. Authorities applauded his capture at the time, noting that Ransom Cartel didn’t grow large enough to inflict losses comparable to larger ransomware variants. 

Silnikau pleaded guilty to conspiracy to commit wire fraud and aggravated identity theft.

The post Ransom Cartel creator sentenced to 16 years in prison appeared first on CyberScoop.

Alleged longstanding member of Scattered Spider extradited to US

A 19-year-old alleged member of the Scattered Spider extortion crew was extradited to the United States last week and remains in federal custody awaiting several cybercrime charges, the Justice Department said Wednesday. 

Peter Stokes, a dual citizen of the United States and Estonia, was allegedly involved in Scattered Spider since it formed in 2022 and boasted on social media about the luxurious globetrotting life he enjoyed while he was still a child. 

The cybercrime ring of young, native English-speaking people has infiltrated more than 100 businesses since 2022, and extorted more than $100 million from its victims around the world, officials said. 

“Scattered Spider has repeatedly targeted U.S. companies, extorting employees, inflicting millions of dollars in losses, and disrupting essential operations,” Brett Leatherman, assistant director of the FBI’s cyber division, said in a statement. “Through strong domestic and international partnerships, the FBI will continue to identify, disrupt, and hold cybercriminals accountable, no matter where they are located.”

Stokes, also known as “Bouquet” and “Jordan,” is accused of participating in multiple data theft and extortion attempts, but the FBI only provided specific details about some more recent attacks on a luxury jewelry retailer in May 2025 and a U.S.-based insurance company in June 2025.

Cybercrime researchers have been tracking Stokes’ online activity since 2022.  Microsoft determined his true identity and implicated Stokes as a member of Scattered Spider in a criminal referral in October 2024, according to court records.

He was still a child at that time, and authorities typically don’t arrest known cybercriminals until they reach adulthood. Stokes lived in Estonia and the United Arab Emirates while he allegedly committed some of his crimes. 

Police arrested Stokes in Finland as he attempted to board an April 10 flight to Japan, possessing two hard drives containing allegedly incriminating evidence. He made an initial court appearance in Chicago Tuesday and was ordered to remain in jail.

Stokes exhibited an opulent life before his capture, according to his social media activity and State Department travel records. This included trips and multiple stays in luxury hotels in Paris, Italy, Spain, Germany, New York, Florida, New Mexico, Thailand and Dubai between 2024 and 2025, according to a criminal complaint filed against him in the U.S. District Court for the Northern District of Illinois.

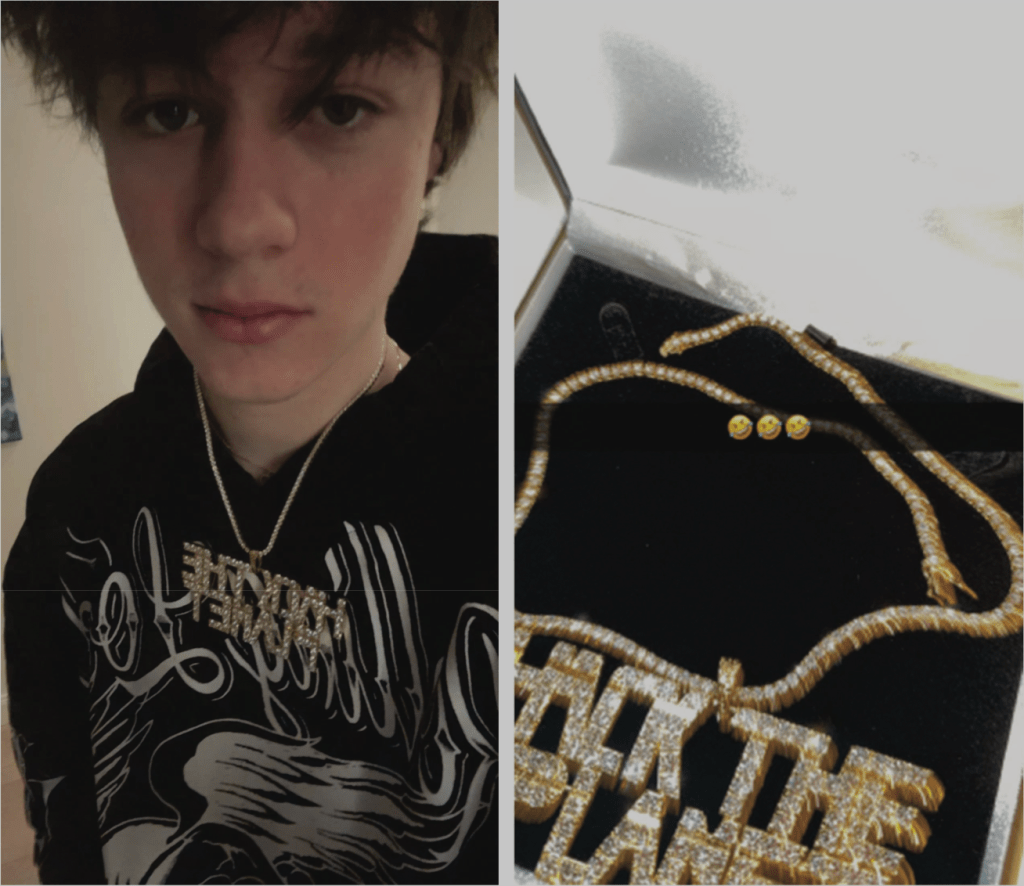
He also posted images of watches, substantial cash and an apparently diamond-encrusted chain depicting the words “Hack the Planet.”

Images from Peter Stokes’ Snapchat account in February 2025 and December 2024. Credit: Justice Department

Officials also noted that Stokes’ family appeared to be well off, as his father was a previous executive in two major European companies. 

Stokes was charged with conspiracy, cyber intrusion and fraud offenses.

“The malicious attacks from Scattered Spider caused widespread disruption to businesses and organizations throughout the United States,” Andrew Boutros, U.S. attorney for the Northern District of Illinois, said in a statement. “These charges underscore our unwavering commitment to keeping pace with technologically savvy criminal actors and holding accountable those who seek to profit from cyber intrusions, including those located in foreign jurisdictions who do harm to American businesses and victims.”

The post Alleged longstanding member of Scattered Spider extradited to US appeared first on CyberScoop.

❌