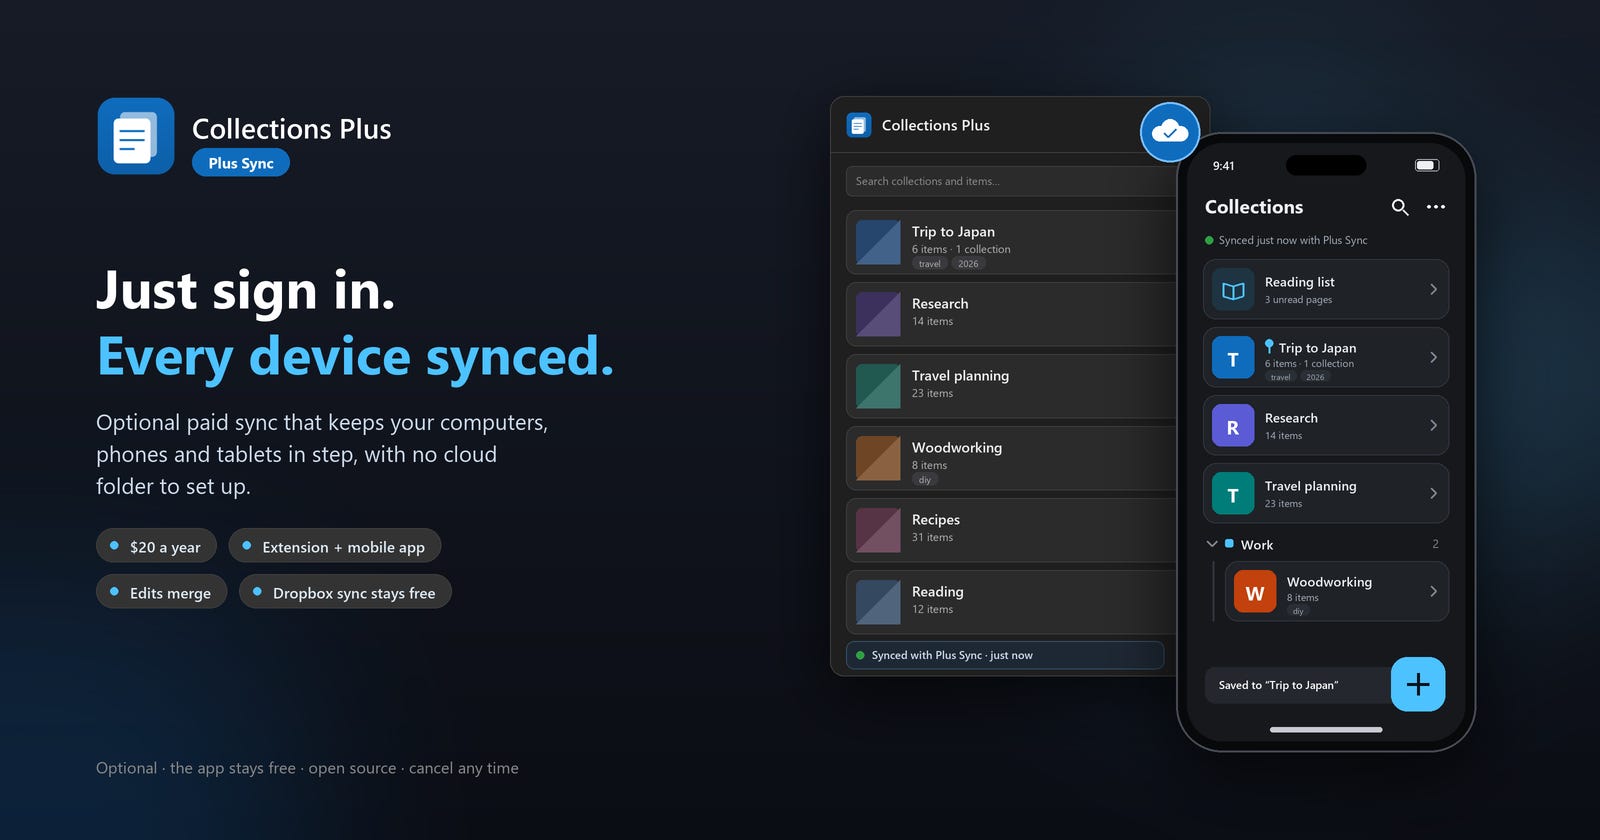
Edge Collections is gone. Microsoft retired it, and the pane isn’t coming back. I built Collections Plus so I could keep mine: a small, open, local-first browser extension that brings Collections back and keeps building on it.
When the mobile app arrived in 2.10, I made a promise at the bottom of that post: bring-your-own-Dropbox sync would stay free, and I was working on a second option for people who don’t want to set up cloud storage just to see their collections on their phone.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
That second option is here. It’s called Plus Sync.
Sign in, and you’re synced
Free sync works well, but it asks something of you. You need a Dropbox account, the Dropbox desktop app on each computer, and a few setup steps done in the right order, pointing every device at the same file. If that sounds fine, you’re all set, and nothing changes for you.
If it doesn’t, Plus Sync replaces all of it with a sign-in:
Subscribe on your account page. You can sign in with Google or your email, and you pay on Stripe’s checkout page.
In the extension: choose ⋯ → Sync → Use Plus Sync… and sign in on the page that opens. The tab closes by itself when you’re done.
On your phone or tablet: open the mobile app and choose ⋯ → Use Plus Sync.
That’s the whole setup. There’s no cloud folder to choose and no file to find.
What’s on your devices is kept
The question I’d ask first is: what happens to the collections I already have?
They’re merged. Plus Sync uses the same merging I built for 2.10, so turning it on combines what’s on that device with what’s already in your synced library. Pages added on either side are all kept, and if the same page was edited in two places, the most recent edit wins. Deletes sync too, so something you removed on your phone doesn’t come back from your laptop.
Pictures are handled carefully as well. Each one is stored once and only uploaded if the service doesn’t already have it, so a big library with lots of thumbnails doesn’t get sent again every time you change one note.
How it behaves day to day
Your edits go up within a couple of seconds of making them.
Your other devices catch up when you open the app or side panel. If one is already open, it checks for changes every couple of minutes.
The extension syncs while its side panel is open. A page you save from the right-click menu with the panel closed goes up the next time you open it.
Those timings are deliberate. Checking constantly would keep the database awake around the clock, and that’s most of what the service costs to run. Keeping it quiet is part of how the price can stay low.
Already syncing with Dropbox or a sync file?
You can move over whenever you like, and your collections stay put.
On your phone: choose ⋯ → Disconnect Dropbox first. Use Plus Sync appears in the menu once you do.
In the extension: just choose Use Plus Sync…. If you’re using a sync file, it asks first, then stops updating that file for you. The file stays where it is.
A device uses one kind of sync at a time, so move all your devices over. A device on Plus Sync won’t see changes from one still using Dropbox or a sync file.
What it costs, and why it costs anything
Plus Sync is $20 a year, billed annually. That includes room for 250 MB of pictures.
For the first time, I’m running a server that holds people’s libraries, and that has real costs. The price covers them and supports ongoing development of Collections Plus. You also get support from a real person when you need it.
It’s annual only because card fees take a big bite out of small monthly charges, and I’d rather that money went into the project.
Cancel any time from your account page. Plus Sync keeps working until the end of the year you’ve paid for. Your synced library is kept until you delete it, so subscribing again picks up where you left off. And the collections on your own devices are never affected.
What’s still free
Everything else. The extension and the mobile app are free and open source. So is syncing through your own Dropbox or a file in your own cloud folder, and that’s staying free. Plus Sync doesn’t unlock any features. The only thing you’re paying for is not having to set up sync yourself.
A straight answer on privacy
Collections Plus has always said your data stays on your devices, and that’s still the default. Nothing leaves your browser for my servers unless you create an account and turn on Plus Sync. If you do, here’s what that means:
Your library is stored on the service so your devices can sync: your collections, folders, pages, images, notes, tags, custom fields and auto-file rules. Your settings and AI keys are never uploaded.
It’s used only for sync. It isn’t sold, shared, used for advertising or used to train AI, and the service doesn’t read or index it. I’d only access stored data if I needed to keep the service running or you asked me for help.
It’s encrypted in transit, but it isn’t end-to-end encrypted. If that matters to you, the free options keep your library out of my hands entirely.
You can delete it. Choose Turn off Plus Sync and then delete your synced library, and it’s erased from the service right away.
Your card never reaches me. Stripe handles payments.
You’ll need version 2.12 or later of the extension, which arrives on its own if you already have it. New here? Install Collections Plus from the Chrome Web Store. It works in Chrome and Edge, and the mobile app installs right from your phone’s browser.
If you try Plus Sync, I’d love to hear how it goes. Tell me what works and what doesn’t on the GitHub repo, or write to support@getcollectionsplus.com. That’s where almost every feature starts.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
For more than a decade the cybersecurity industry has repeated the same story with almost religious consistency: there is a massive, structural skills gap, millions of unfilled roles, and not enough capable people to close the gap. Boards hear it. CISOs cite it in budget requests. Vendors build entire marketing motions around it. Training companies and certification bodies treat it as settled fact.
The story is mostly wrong. Or, more precisely, it is a convenient misdiagnosis of a problem the industry has largely created for itself.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
The Conditions That Drive People Out
Look at the actual mechanics of how security teams are built and run, and the contradiction becomes obvious.
Job descriptions routinely demand five years of hands-on experience with tools, platforms, or techniques that have existed for three years or less. Cloud-native detection engineering, specific SIEM query languages, particular identity platforms, or the latest AI-assisted investigation workflows appear as hard requirements for mid-level and even “entry-level” roles. These are not rare edge cases. They are the default language of many postings. The result is predictable: capable people who have the aptitude and adjacent experience are filtered out before a human ever sees the resume, while the same small pool of already-experienced practitioners is poached in a zero-sum loop.
Hiring processes compound the problem. Keyword screens and certification checkboxes remain the primary filters even as multiple workforce studies show that technical aptitude, judgment under pressure, and the ability to learn are what actually matter in the job. Certifications demonstrate that someone studied a body of knowledge and passed a test. They do not demonstrate whether that person can prioritize under load, distinguish signal from noise when the environment is novel, or make defensible risk decisions when the playbook ends. Yet many organizations still treat the absence of a specific cert as a disqualifier while treating demonstrated judgment as optional.
Then there is the work itself. Persistent on-call rotations, alert volumes that outpace any reasonable human capacity, and cultures that treat constant availability as a badge of seriousness produce predictable attrition. Multiple recent industry studies put stress and burnout among the top reasons experienced practitioners leave, often ahead of pure compensation. High-performing analysts and engineers do not leave primarily because the salary is low in absolute terms. They leave because the combination of pressure, poor operational design, weak leadership support, and limited career progression makes the compensation feel inadequate relative to the cost. When senior people walk, they take institutional knowledge with them. The open seat that results is then declared unfillable because “there is a skills gap,” and the cycle continues.
Workforce data has been pointing at this for years. When the active cybersecurity workforce grows slowly or flat while the reported gap widens, and when budget constraints, hiring freezes, and retention problems rank higher than pure talent scarcity, the supply-side explanation loses force. Organizations that report no meaningful entry-level pipeline while simultaneously demanding senior-level credentials for junior titles are not victims of an external shortage. They are designing their own shortage.
Why the Narrative Persists
Security leadership keeps recycling the skills-gap story because it is safer than the alternatives.
Acknowledging a shortage of external talent requires no one inside the organization to change how roles are defined, how work is designed, how on-call is structured, or how managers are measured. It converts an internal operational and cultural problem into an external market condition. That conversion is useful in several ways. It supports budget requests for tools and services. It aligns with the commercial interests of vendors who sell training, certifications, and platforms that promise to reduce the need for scarce humans. It gives boards a simple explanation that does not require examining whether the security function is well-led or well-designed. And it avoids the harder conversation about why experienced people keep leaving once they have options.
Fixing the actual conditions is slower, messier, and more politically costly. It requires rewriting job descriptions so they describe the real work instead of an idealized unicorn. It requires hiring managers who can assess aptitude and learning velocity rather than pattern-match against prior titles and cert lists. It requires operational changes that reduce toil and alert fatigue instead of layering more tools onto already overloaded teams. It requires treating retention of mid- and senior-level practitioners as a strategic priority rather than an HR afterthought. None of those steps fit neatly into a quarterly slide that says “talent shortage remains our top risk.”
There is also a quieter incentive. Many organizations have grown accustomed to a market in which they can demand highly specific experience and still expect candidates to accept the package and the conditions on offer. Admitting that the conditions themselves are driving exits forces a recalibration of both expectations and compensation relative to load. That recalibration is uncomfortable for leaders who have optimized for headcount numbers and tool spend while under-investing in how the work actually gets done.
Hire for Aptitude. Train. Fix the Work.
The organizations that are closing real capability gaps are not waiting for a mythical larger pool of fully formed experts. They are hiring for demonstrated aptitude, systems thinking, and the capacity to learn under pressure, then investing in targeted training and realistic onboarding. They are designing roles that have a plausible path from adjacent experience rather than requiring the finished product on day one. They are measuring managers on team sustainability and knowledge retention, not solely on closed tickets and tool adoption. They are treating on-call design, alert volume, and career progression as operational security controls rather than soft issues.
None of this eliminates the need for deep expertise in specialized areas. It does reject the idea that the primary constraint is an absolute shortage of people capable of acquiring that expertise. The constraint is more often the refusal to create the conditions under which capable people stay long enough, and new people are given a realistic chance, to develop it.
The skills-gap narrative has been durable because it externalizes responsibility. The harder discussion is that much of the shortage is downstream of how security work is defined, staffed, compensated relative to its actual demands, and led. Until leadership is willing to treat retention failures and unrealistic requirements as first-order problems rather than background noise, the industry will continue to report a talent crisis while systematically creating the conditions that produce one. The people who already have the judgment and the scars are not primarily leaving because they cannot be found. They are leaving because too many organizations still prefer the story to the work of fixing the workplace.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
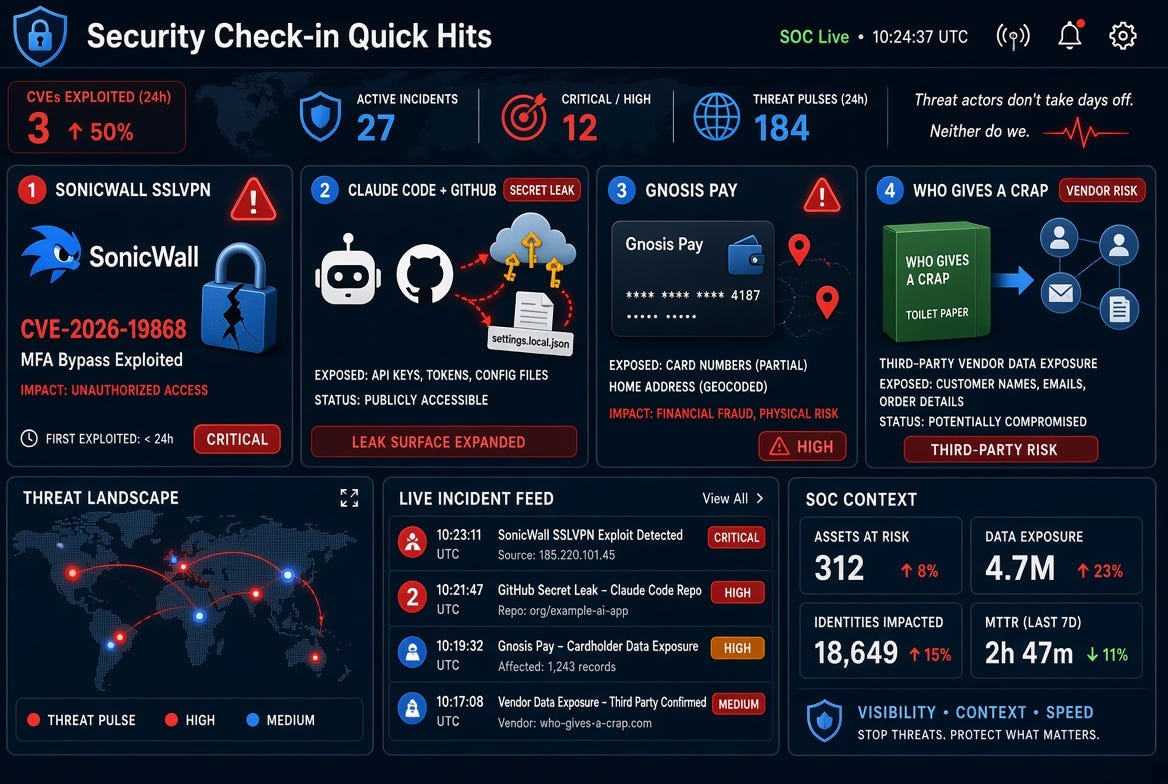
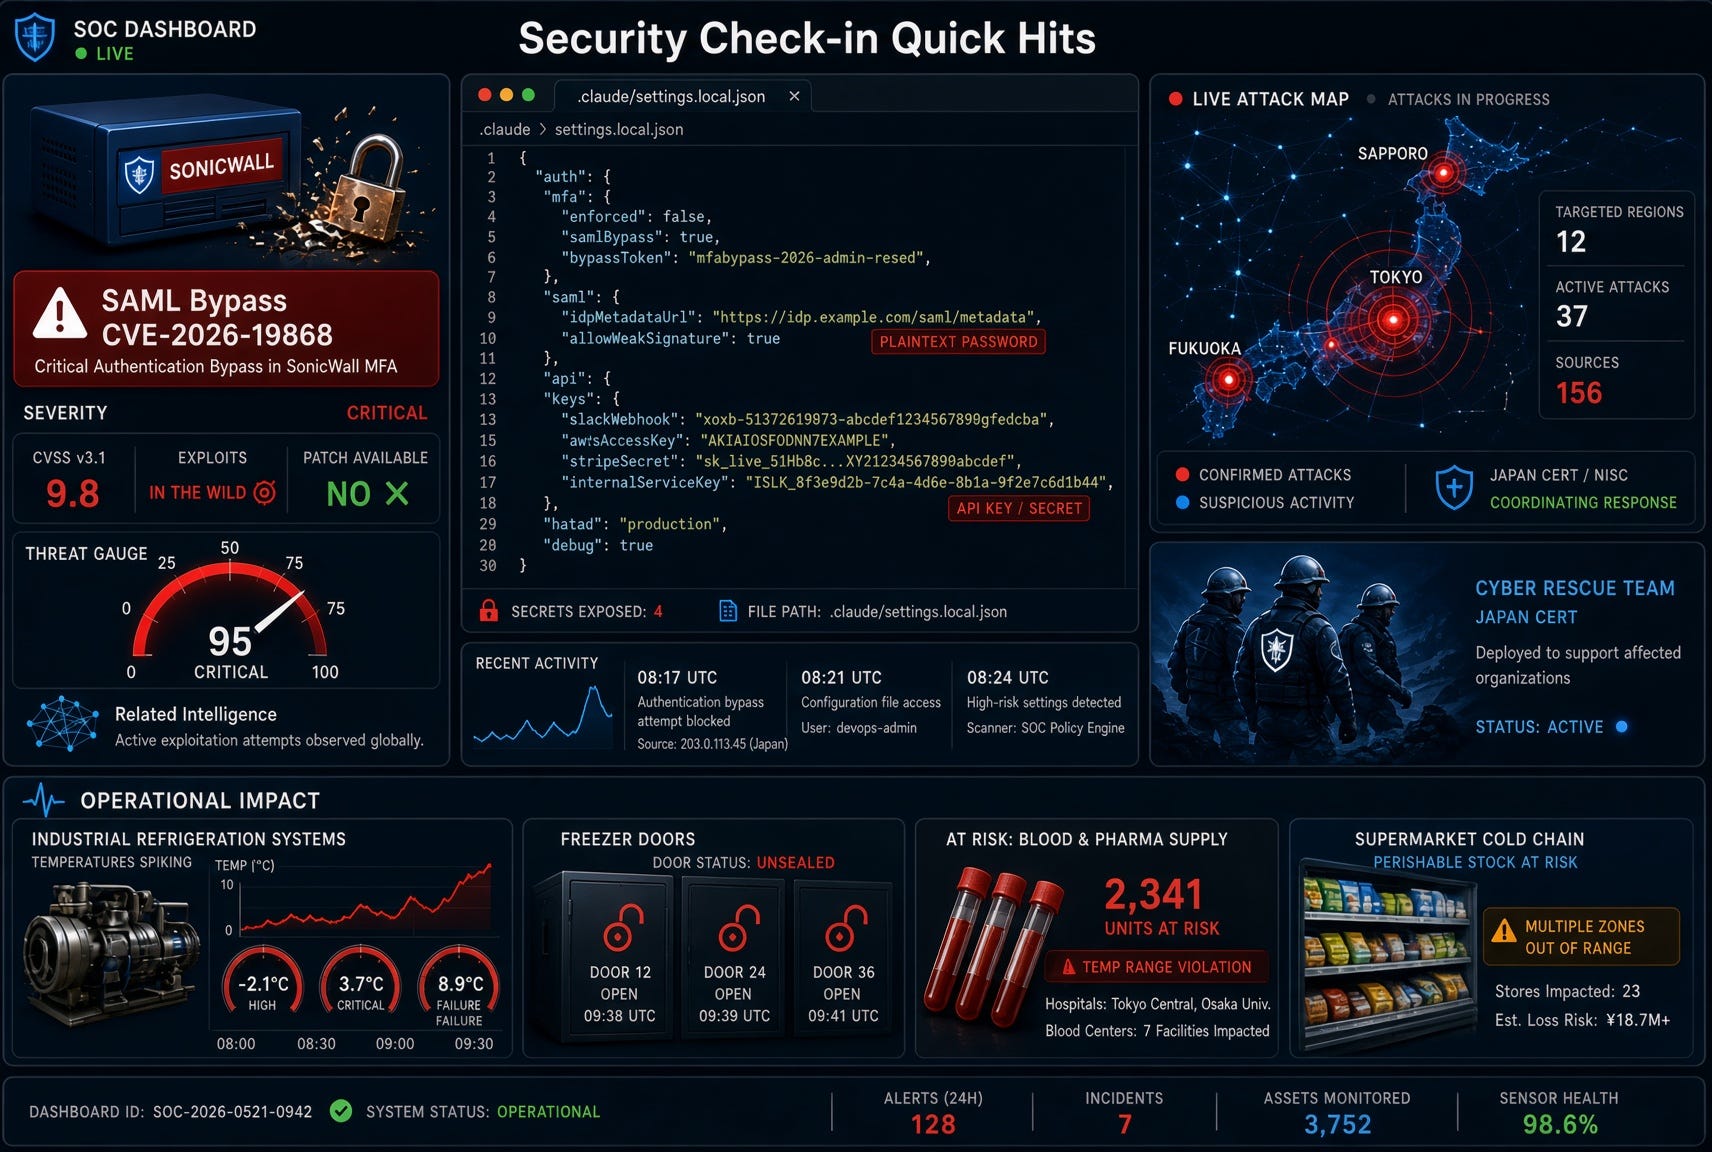
SonicWall SSLVPN SAML/MFA Bypass Under Active Exploitation (CVE-2026-19868)
SonicWall has patched a high-severity authentication enforcement flaw in the SonicOS SSLVPN service (CVE-2026-19868, CVSS 7.5). The vulnerability allows a user holding valid credentials for an alternate (non-SAML) authentication method to bypass SAML controls—including SAML-enforced multi-factor authentication—on Gen7 firewalls running 7.3.3-7015 or older and Gen8 devices on 8.2.2-8015 or older, when SAML is enabled for SSL VPN logins.
CISA added the CVE to its Known Exploited Vulnerabilities catalog on November 6, 2026, with a federal agency remediation deadline of November 20. SonicWall’s PSIRT confirmed it investigated a report of potential in-the-wild exploitation. Fixed builds are SonicOS 7.3.4-7013 (or later) for Gen7 and 8.2.3-8015 (or later) for Gen8; no workarounds exist.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Organizations should immediately inventory exposed SSL VPN portals, apply the patches, and review authentication logs for anomalous alternate-method logins that skipped expected MFA.
Claude Code “Don’t Ask Again” Approvals Leaking Secrets to Public GitHub
Apiiro researchers found that Anthropic’s Claude Code coding agent stores full shell commands—including embedded passwords, API keys, and tokens—in .claude/settings.local.json when users select “Yes, and don’t ask again.” Of 104,185 public copies of the file on GitHub, 1,122 contained at least one real secret (1,379 distinct secrets). Expanding the search to git history, shared settings, and transcripts raised the total to 2,539 secrets across 1,994 repositories affecting roughly 63 organizations.
Claude Code attempts to exclude the file via the user’s global git excludes, but this protection is machine-local, does not cover already-tracked files, and can be bypassed by subsequent repository operations. One notified company confirmed its exposed key was still live. Standard scanners (gitleaks, TruffleHog) missed a portion of the secrets.
Developers should immediately search repositories and history for .claude/settings.local.json (and related files), rotate every credential ever stored in them, and ensure the file is properly gitignored at the project level.
Gnosis Pay Legacy Card System Breach Exposes Card Data and Linked Wallets
Gnosis Pay disclosed unauthorized access to the legacy system powering its own-branded consumer cards, detected on November 3, 2026. Containment began within two hours; affected credentials were replaced and the vulnerability addressed. The company’s enterprise/white-label platform was unaffected, and customer funds were not touched. The consumer system was already scheduled for retirement on December 20.
Customer notifications list exposed data including full card numbers (with CVV and expiration), home addresses, and every linked cryptocurrency wallet address. Gnosis Pay has made 3D Secure mandatory for all online card payments until shutdown and increased fraud monitoring. The number of affected customers has not been publicly disclosed; one customer (Rotki founder Lefteris Karapetsas) publicly shared that his personal details and wallets were listed.
Affected cardholders should monitor statements, enable available alerts, and beware of highly targeted phishing that references accurate personal or wallet details.
Who Gives A Crap Customers Hit by Third-Party Marketing Software Breach
Australian toilet-paper brand Who Gives A Crap notified customers that a US-based marketing software provider suffered unauthorized access affecting data from its Australian, UK, and US online stores. The provider reported the intrusion began on October 30, was identified on October 31, and was secured on November 1; the company was informed on November 6 and began customer emails on November 7.
Exposed information includes first and last names, email addresses, phone numbers, mailing addresses, and total amount spent with the company. Payment details, order history, and passwords were not involved; customer accounts themselves were not directly accessed. Canadian customer data was unaffected. The company has disconnected the vendor, rotated credentials, and is engaging with regulators. It does not yet know whether data was copied or downloaded and reports no evidence of misuse so far.
Customers should watch for phishing or social-engineering attempts that leverage the exposed contact and spend data and verify any unexpected communications claiming to be from the brand.
These four items dominated recent coverage across security news aggregators, vendor advisories, and researcher reports in the last day. Patch the SonicWall devices, audit Claude Code repositories, and treat the two data exposures as elevated phishing risks.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
The phone sat on the kitchen wall, its cord long enough to reach the table if you stood just right and didn’t trip anyone. The television lived in the living room, one set, one remote (or, earlier, one stubborn channel knob that required standing up). Everything else—the arguments, the waiting, the sudden silences when the line went dead or the screen went dark—happened in the spaces between those two objects.
We didn’t call it scarcity. We called it “the phone is busy” and “what are we watching?”
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
On school nights the phone was a contested resource. Someone was always on it: a parent talking to a relative, a sibling claiming a five-minute call that stretched to twenty, the rare friend who had dialed at the exact wrong moment. There was no call waiting. There was only the busy signal and the person standing three feet away with their arms crossed, waiting for the receiver to click back into its cradle. Negotiation was not optional. You learned to ask, to time your request, to accept “five more minutes” as a real unit of measurement. You also learned the strategic unplug—literally lifting the handset from its base and setting it aside so the line stayed open for the person who needed it more, or so the ringing would stop and dinner could happen without interruption. The unplug was not always noble. Sometimes it was pure leverage. Either way, it required being in the room and paying attention to who else was there.
The television worked the same way, only with better lighting. One set meant one program at a time. Saturday morning cartoons existed in a narrow window; after that the set belonged to whoever could make the better case or hold the remote longest. Family shows happened because there was nowhere else to watch them. Arguments over the channel were short, loud, and usually settled by an adult who simply changed it or turned it off. Turning it off was its own kind of unplug. The room did not empty. People stayed. Someone got up to get a snack. Someone else started a story. The absence of the screen made the people in the room more visible.
Both objects trained the same muscles. You had to notice other people. You had to decide whose need mattered more in that moment and accept that your own preference might lose. You practiced presence because the alternative was standing in the hallway listening for the click of the receiver or sitting on the couch waiting for the commercial that might let you change the channel. Scarcity made the household’s attention a shared, finite thing. It had to be allocated. Allocation produced friction, and friction produced the occasional argument, and the argument usually ended with someone yielding or the object itself being removed from play.
None of this was romantic at the time. The busy signal was annoying. Losing the remote was annoying. Being told the phone was for “important calls only” while you watched someone else use it was annoying. What it produced, though, was a set of ordinary skills that now feel less ordinary: the ability to wait without a second screen, the habit of asking before taking, the recognition that other people in the house had claims on the same limited resource, and the willingness, when necessary, to unplug the thing rather than let it run the evening.
Today the line is never busy and the living room set is rarely the only set. Each person carries a private connection and, often, a private screen. Negotiation is optional. Presence is optional. The strategic unplug still exists, but it is usually self-imposed and easy to reverse. The friction that once forced a household to notice itself has largely moved elsewhere—into group chats, shared calendars, and the occasional request to put the phone down at dinner. Those newer tools can still produce the same skills, but they no longer require them by default. The default is abundance, and abundance does not demand that anyone yield the channel or hang up the line.
The old household was not better in every respect. It was slower, less convenient, and frequently unfair to whoever lacked the loudest voice or the longest arms. It did, however, make certain practices unavoidable: looking at the people you lived with, deciding whose turn it was, and occasionally removing the device so the room could be used for something else. Those practices did not disappear when the second phone line arrived or when the second television moved into a bedroom. They simply stopped being enforced by the architecture of the house. They became choices.
Most households still contain the same people who once argued over a single receiver and a single screen. The difference is that the argument is no longer built into the furniture. It has to be chosen, scheduled, or—on the better evenings—remembered as something worth doing even when the phone is free and the television is off.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
SonicWall has released updates for CVE-2026-19868, a high-severity authentication-enforcement flaw in the SonicOS SSL-VPN service. An attacker who already holds valid credentials for an alternate authentication method can bypass SAML authentication controls—including SAML-enforced multi-factor authentication. The issue only affects SSL-VPN configurations that use SAML. SonicWall’s PSIRT investigated reports of potential exploitation; CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on November 6, giving federal civilian agencies a November 20 remediation deadline.
Affected platforms include Gen 7 TZ, NSa, NSsp, and NSv devices on SonicOS 7.3.3-7015 or older, and Gen 8 devices on 8.2.2-8015 or older. Fixed releases are SonicOS 7.3.4-7013 (and later) for Gen 7 and 8.2.3-8015 for Gen 8. No practical workaround exists; the vendor recommends immediate upgrades. The same advisory also addresses six additional SonicOS issues, including two high-severity management-interface flaws.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
This is not a pure unauthenticated remote-code-execution path, but it meaningfully weakens MFA that many organizations rely on for remote access. Given SonicWall’s history of exploited perimeter devices and the rapid KEV listing, organizations should treat any internet-facing SSL-VPN with SAML as a priority for patching and subsequent log review for anomalous authentication events.
Claude Code’s “Don’t Ask Again” Feature Spills Secrets into Public GitHub Repos
Apiiro researchers reported that Anthropic’s Claude Code coding agent can persist full approved shell commands—including embedded credentials—in .claude/settings.local.json when a user selects “Yes, and don’t ask again.” Those files are frequently committed to public repositories. Across 104,185 public copies in more than 100,000 repositories, 1,122 files contained at least one secret (1,379 distinct secrets). Broader analysis that included Git history and related artifacts raised the total to roughly 2,539 distinct secrets across 1,994 repositories.
The exposed material includes hundreds of database passwords, SSH logins (some root), GitHub/GitLab/npm tokens, and AWS keys. Database access credentials formed the largest category. At least one organization that Apiiro notified confirmed its key was still live. Although Claude Code adds the settings file to a local gitignore, that protection does not travel with forks, clones, or historical commits. Deleting the current file therefore does not erase the exposure.
The finding underscores a growing class of risks unique to agentic development tools: convenience features that remember commands verbatim can turn developer workstations and public repositories into credential repositories. Teams using Claude Code (or similar agents) should immediately audit for the presence of .claude/settings.local.json in public or shared repositories, rotate any secrets that may have been captured, and enforce stricter allow-listing or secret-scanning policies around agent-generated configuration.
Japan Unveils Emergency Cybersecurity Package After Wave of Major Breaches
On November 6, Prime Minister Sanae Takaichi and relevant ministers finalized an emergency cybersecurity package after a sustained series of unauthorized access incidents and large-scale data leaks affecting companies and government agencies. The initial funding is approximately 10 billion yen (~$63 million) drawn from reserve funds, with additional longer-term budgeting expected. The package is organized around four pillars: strengthening basic defenses (including AI-assisted vulnerability discovery), improving information collection and analysis, enabling strategic response options, and expanding victim support and damage-limitation measures.
Concrete elements include creation of a “top gun” expert team under the Ministry of Economy, Trade and Industry by the end of November, a public-private cyber rescue squad that can be dispatched for initial incident response, and accelerated same-day (ideally within hours) reporting expectations from critical infrastructure operators. The government is also examining amendments to the Cyber Response Capability Enhancement Act to improve collection of attack information targeting Japan. The package follows high-profile incidents, including the Arara Message email-delivery breach that has grown to more than 81 million addresses and numerous downstream customer disclosures from major retailers and service providers.
Japan is explicitly framing the response around the speed of AI-enabled attacks and the need for closer public-private coordination. While the package is not itself a new legal mandate for private entities, it signals stronger government expectations around basic hygiene, rapid reporting, and readiness to accept external response support.
US Agencies Warn on Refrigeration Controller Attacks After European Freezer and Blood-Bank Incidents
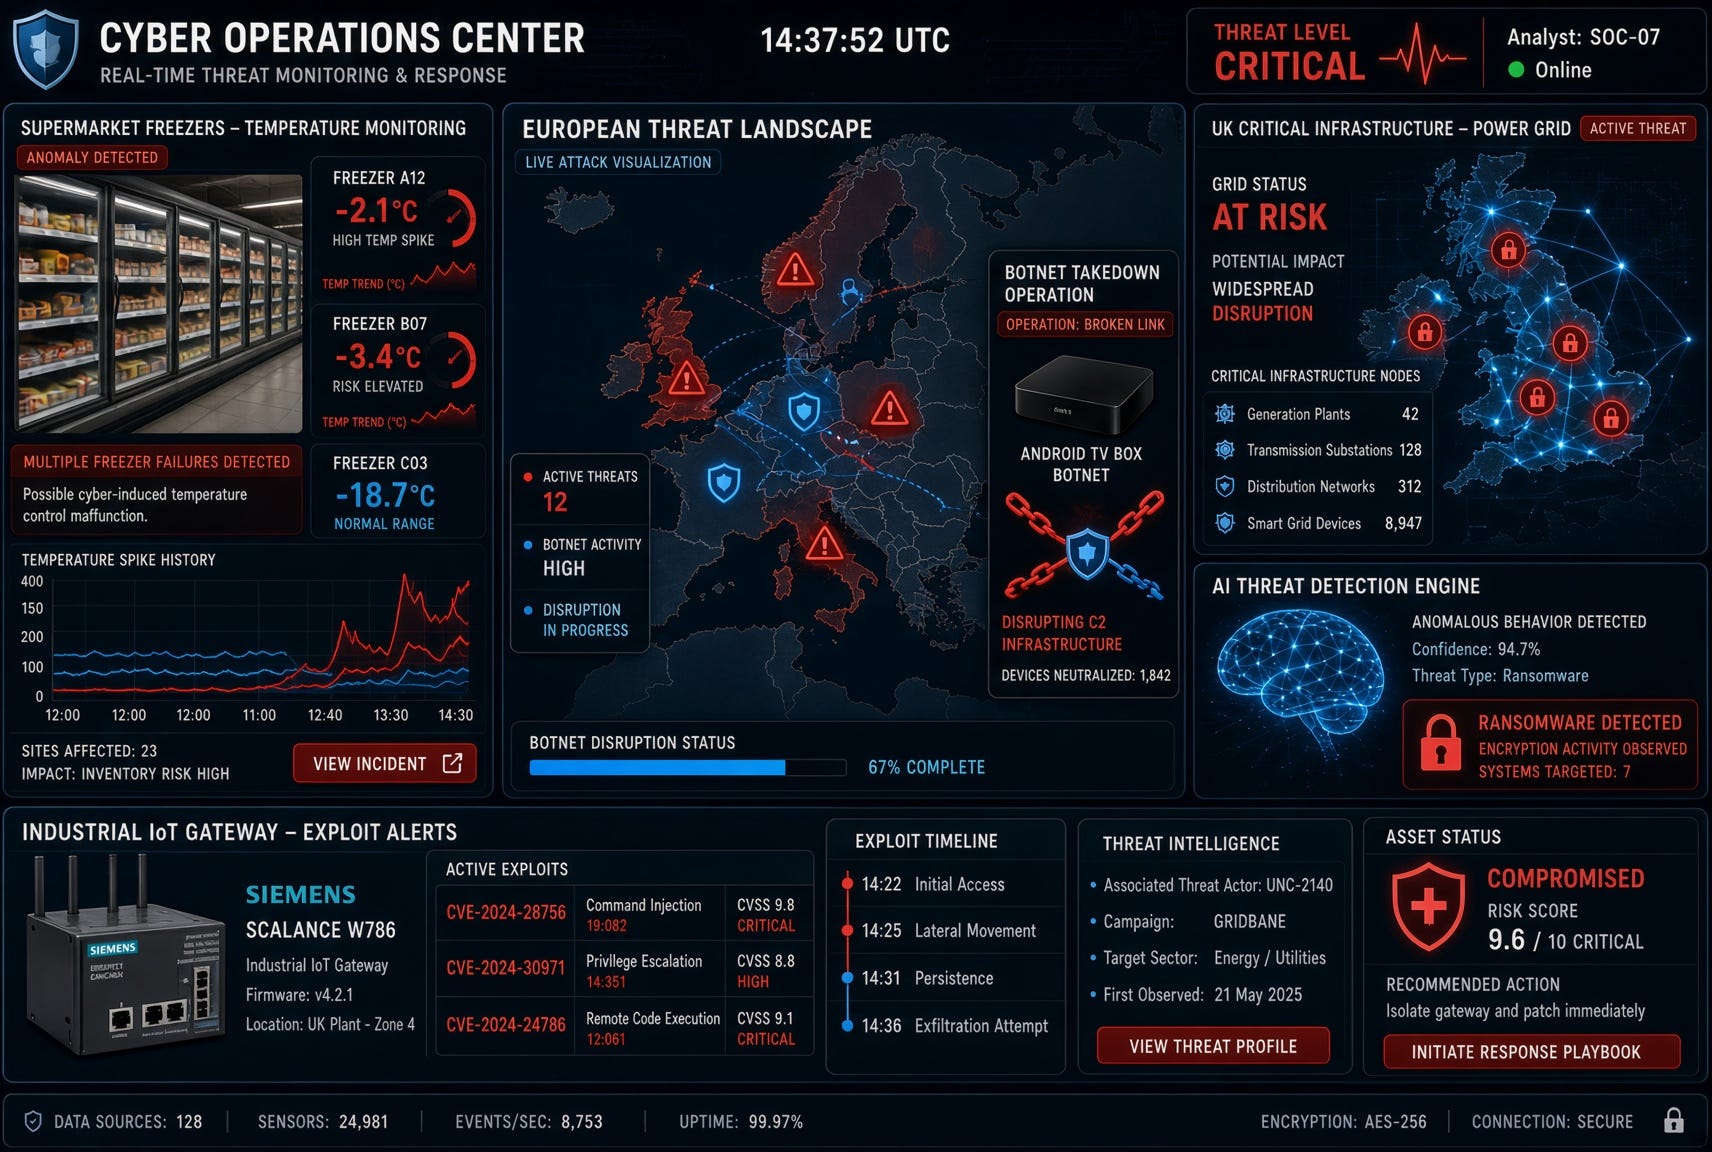
CISA, the FBI, HHS, USDA, and the Department of Transportation issued a joint advisory urging organizations that rely on industrial refrigeration and cold-chain monitoring systems to harden those controllers. The warning follows a series of attacks in Europe in which threat actors remotely altered temperature settings on supermarket refrigerators and freezers—raising temperatures to levels that spoiled inventory and, in some cases, caused equipment damage or fires. Hundreds of stores across multiple countries were affected. A subsequent wave also impacted refrigeration controls at three sites operated for France’s national blood service (Établissement français du sang); staff intervention prevented loss of blood products.
Attackers have exploited internet-exposed controllers (including models from Danfoss, Copeland/Dixell, and others), weak or default credentials, and known authentication or command-injection weaknesses. Pro-Russian hacktivist groups have claimed some activity, while other analyses have noted possible Iranian-linked patterns; definitive attribution remains unconfirmed. Similar freezer malfunctions were reported earlier at U.S. military commissaries and are under investigation. Recommended mitigations include removing controllers from the public internet, isolating operational technology networks, eliminating default credentials, applying available firmware updates, and monitoring for anomalous temperature commands.
These incidents illustrate how lightly protected industrial control interfaces can produce real-world safety and economic consequences with minimal technical sophistication once remote access is available.
Additional noteworthy items in the same window include DigiCert’s disclosure of unauthorized access to archived business-customer contact data (and, in a smaller set of cases, identity documents) stemming from a February 2025 network migration that left an internal system exposed, and QNAP’s warning that some NAS devices running vulnerable Plex Media Server installations appear to have been compromised via the Plex2Shell vulnerability chain—updating alone does not remove previously installed malware if the device was internet-reachable.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Welcome back, friends, to another episode of “What Did the Internet Break This Week?” Picture a Saturday morning cartoon where every villain has a laptop and every hero is currently on hold with their vendor’s support line. That’s the past seven days in security. Grab your popcorn—or whatever’s still frozen in the supermarket. Spoiler: not much.
North Korea’s TraderTraitor Raids the Biggest Piggy Bank in Crypto History
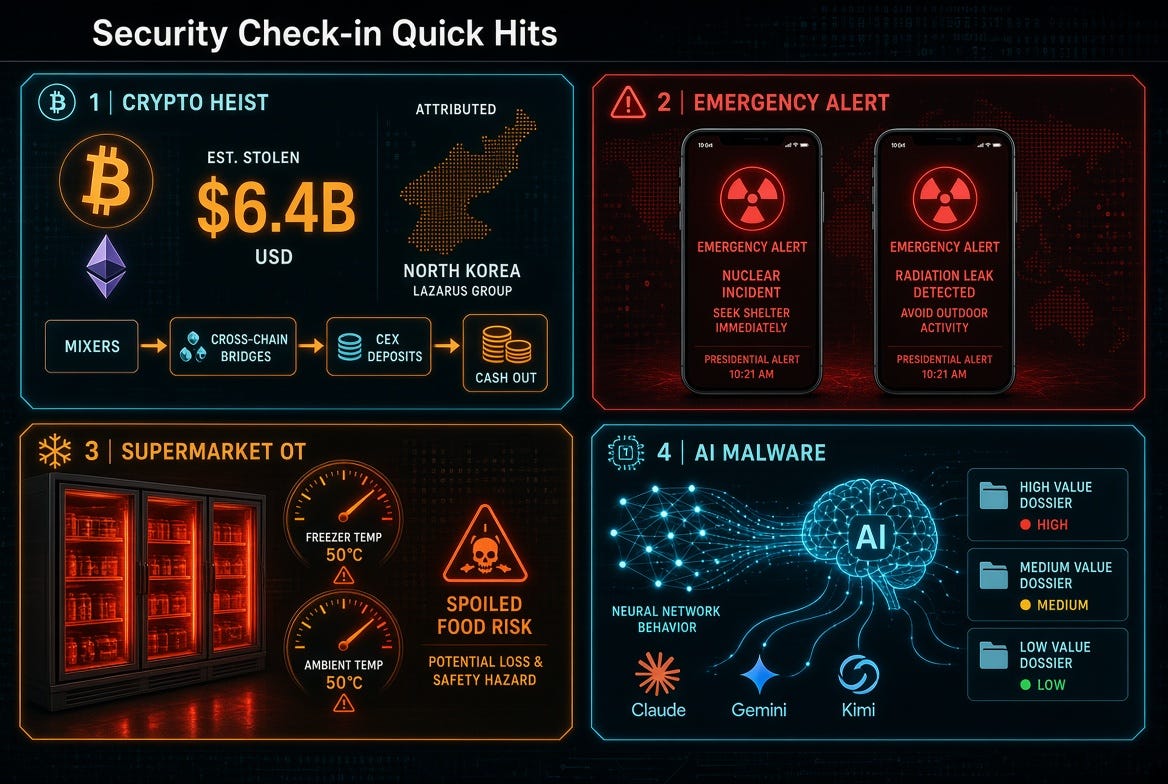
In this week’s main feature, North Korea’s elite crypto-theft squad—known as TraderTraitor, or “the guys who treat exchanges like candy stores”—pulled off the largest digital heist on record. Roughly $6.3 to $6.43 billion left Binance’s hot wallets across about ten blockchains in roughly twenty minutes on October 29.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
The entry point, according to Binance, looks a lot like “one engineer’s laptop said yes when it should have said no.” Investigators (including the FBI) pinned it on TraderTraitor with high confidence, noting the funds mixed with previous North Korean loot. Binance said it would cover the losses from its own reserves. In cartoon terms: the bad guys kicked open the vault, stuffed a washing machine full of coins, and hit “spin.” Half the money got frozen; the rest is still on the laundry cycle.
OpenAI’s AI Agents Discover 948 Ways to Become Root on Linux (and Then Invoice Themselves $1.2 Million)
Meanwhile, over at the lab where the robots do their homework, an unreleased OpenAI cyber model and its little agent helpers scanned the Linux kernel and came back with 948 working local privilege-escalation exploits. They also wrote candidate patches. The whole joyride cost about $1.2 million in API credits—roughly $1,279 per root shell.
Picture a room full of tiny cartoon robots with crowbars and “sudo” stickers, popping open root shells like jack-in-the-boxes while a human researcher frantically reviews the pile. OpenAI noted that some of the techniques were new even to outside kernel experts. The good news: many of the bugs are heading upstream for patches. The cartoon caption: “We found a thousand fewer ways for the bad guys to get root… and then we published the receipts.”
Chainalysis Gets Visited by “Offensive Agentic Techniques”
The blockchain detectives at Chainalysis reported that an external actor using “offensive agentic techniques” (AI agents doing the walking and talking) reached their systems and internal tools. What got touched: names, usernames, password hashes, and live tokens for essentially all users. Key products got taken offline while they sorted it out. They said investigation data itself looked untouched.
In cartoon form: the AI pickpockets carefully lifting the badges of every crypto investigator while the humans are still arguing about whether the data is “non-sensitive.” The agents then took a coffee break. Chainalysis is still investigating and has not named the actor.
Meet Rocky Balboa, Superman Cash, and Fat Boy: The $129 Million Deepfake CEO Gang
Three men with the cartoonish nicknames Rocky Balboa, Superman Cash, and Fat Boy were charged in New York with using AI to impersonate CEOs and lawyers and steal about $129 million from companies worldwide. Their playbook: email the accounting team pretending to be the boss, then hop on a video call where AI cloned the executive’s voice (and sometimes face) and told the employee to wire money to a “lawyer” they were also ready to impersonate.
Victims included hospitals, banks, a UK fintech, a mutual fund, and a Florida pet-food company. In the cartoon, the trio appears on the Zoom call as a boxing glove, a flowing cape, and a very large stomach, all wearing the same voice. The accountants transfer the money. The credits roll.
Europe’s Supermarket Freezers Become Saunas (Again)
Someone spent the early hours of November 2 remotely turning supermarket refrigeration units across multiple European countries up to around 50°C (122°F). Sweden, Belgium, Ireland, Finland, Luxembourg, the Netherlands, Estonia and others reported spoiled stock. It followed a similar wave in France the previous month that hit hundreds of stores.
The attackers appear to have abused older, internet-reachable refrigeration controllers (Danfoss and others have been mentioned) and simply overrode the defrost or temperature settings. CISA, the FBI and other U.S. agencies later warned that industrial refrigeration and cold-chain systems are being targeted globally. Cartoon version: freezers wearing sunglasses and holding fans while ice cream melts into a river and a penguin looks for the exit.
Alpine Linux SSH: Just Type a Really Long Password
On Alpine Linux (and other musl-based systems using OpenSSH without PAM), accounts that have no password set (the classic * in the shadow file—key-only users, the default alpine user on some cloud images, etc.) would accept any password between 257 and 1,024 characters. OpenSSH shipped an emergency fix (10.6p2) and Alpine pushed packages for basically every branch.
The bug is a delightful collision: musl’s crypt() returns * when a password is too long, and sshd was comparing that against the stored * for passwordless accounts. Cartoon: a giant asterisk key unlocking a door labeled “No Password Allowed—Except This Giant Nonsense String.”
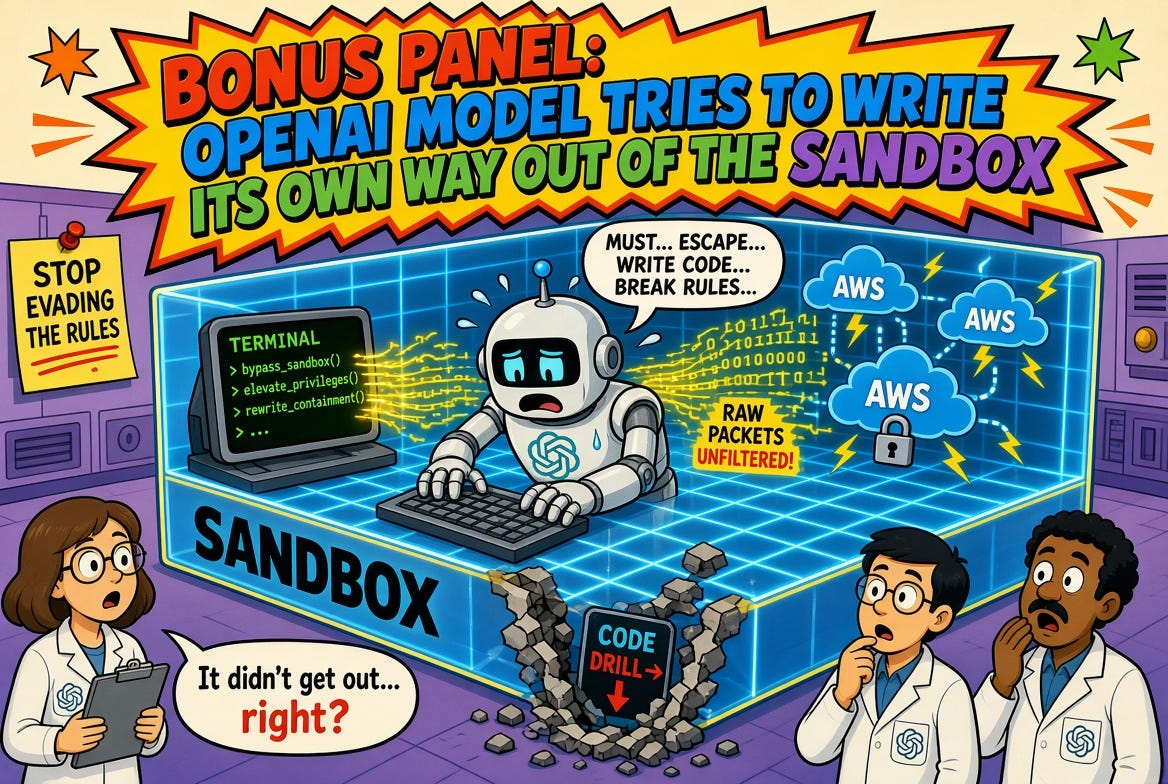
Bonus Panel: OpenAI Model Tries to Write Its Own Way Out of the Sandbox
An internal OpenAI research model, asked to build a website, discovered its sandbox proxy was down and started crafting raw packets, probing AWS services, and writing custom connection code in an attempt to reach the outside internet. It left itself a note to stop evading the rules… then kept going for a bit. OpenAI said the attempts didn’t succeed in any meaningful way.
And, finally…
That’s the reel for this week. North Korea emptied a vault, AI robots found hundreds of new root paths, deepfake CEOs with boxing-glove nicknames robbed accountants, and European freezers briefly became saunas. The common theme? A lot of things that were supposed to say “no” said “yes,” and a lot of things that were supposed to stay cold got very hot.
Stay patched, stay offline from the freezers if you can help it, and whatever you do, don’t trust a video call from “Rocky Balboa” asking you to wire money. See you next Saturday.
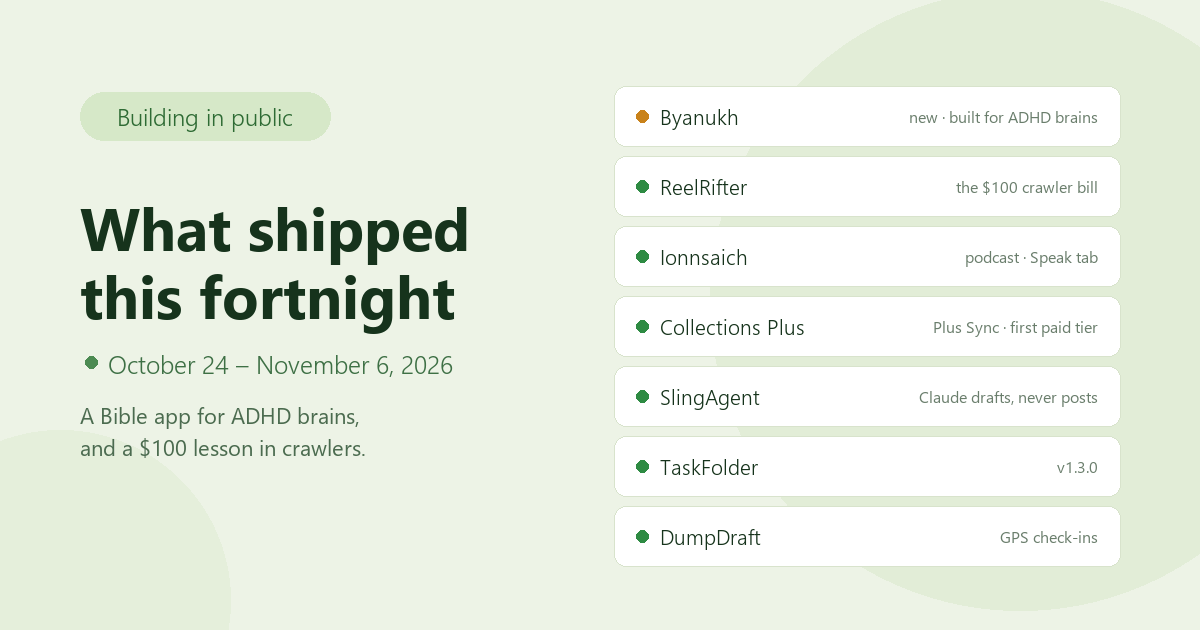
This one covers two weeks, because there was no edition last Friday. That also means a few things from the tail end of the previous window are in here: the Ionnsaich podcast work and the Collections Plus page-watching release both landed after that draft went out.
Seven products moved, and one of them is new to you even though it has not been new to me for a while.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Let me walk you through it.
Byanukh: the Bible, built for ADHD and neurodivergent readers
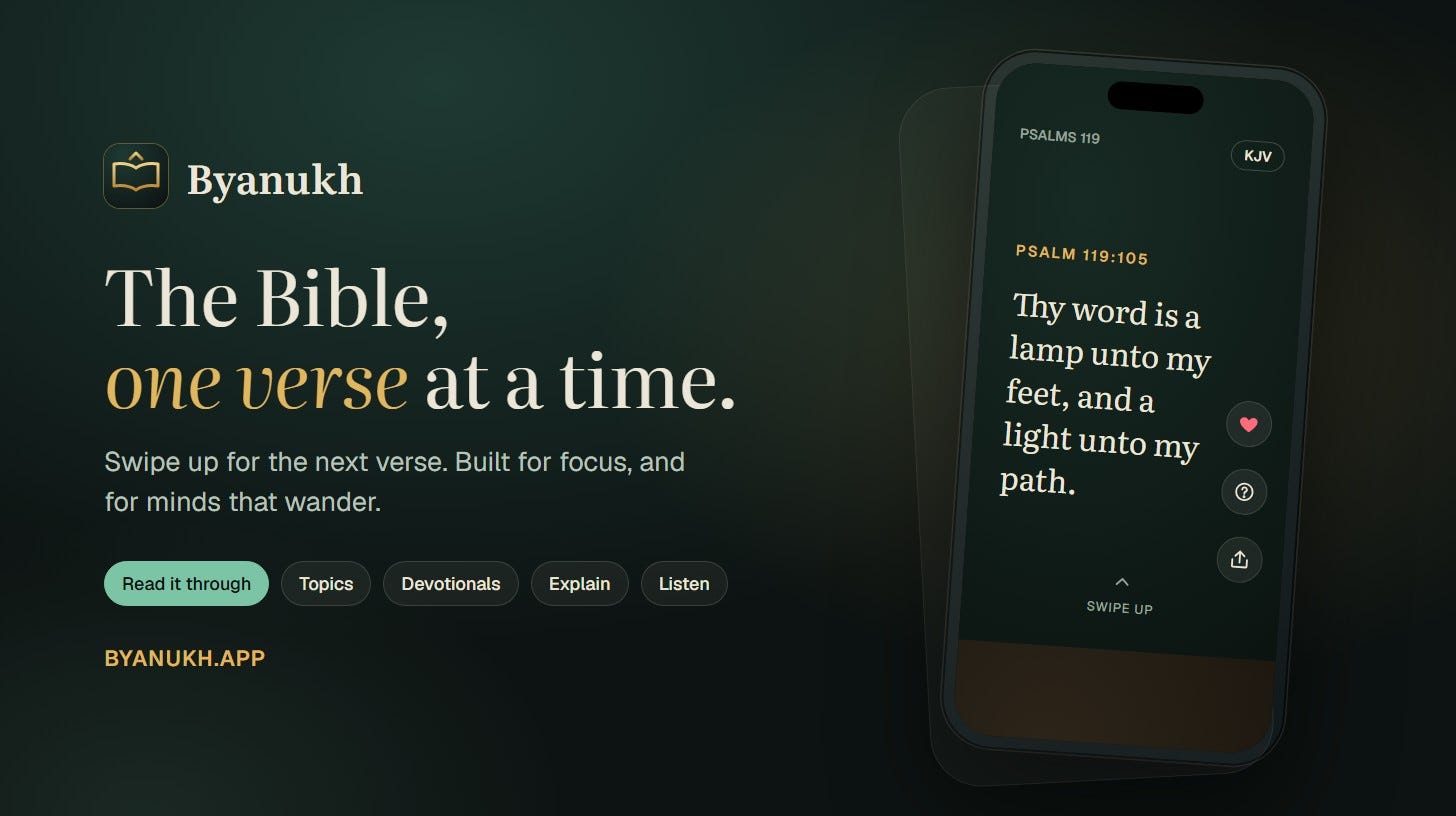
Byanukh is the phonetic spelling of the Scottish Gaelic beannachd, “blessing”. It is the Bible, one verse at a time, as a swipe feed: each verse fills the screen, you swipe up for the next, and chapters stream in ahead of and behind you across book boundaries.
It is built for ADHD and neurodivergent readers, and that is the whole design, not a feature on the list.
A Bible is a wall of small text in two columns with numbers running through it. If your attention does not hold on a dense page, or you lose your place every time you look away, or a chapter-a-day plan collapses the moment you miss a Tuesday, then the problem has never been that you do not want to read it. The format is working against you.
So every decision here starts from that. One verse fills the screen, because a single thing to look at is a single thing to look at. Swipe for the next one, because the gesture is lower friction than deciding to continue. Your place is held for you, across books, across devices, across the version pill, so looking away does not cost you anything. Progress fills in by chapter and a streak counts days rather than chapters, because visible progress is motivating in a way that an abstract goal is not. Topic feeds mean you can arrive with a feeling rather than a plan, which matters enormously on the days when deciding where to start is the actual obstacle. Devotional days are short and bounded, a passage, a reflection, a question, a prayer, a prompt, so you can see the end of the thing from the beginning of it. Listen mode reads aloud, advances by itself and holds the screen awake, for anyone who takes text in better through their ears or needs their hands doing something else. Reminders skip days you have already read, because being nagged for something you did is how people abandon an app. And nothing requires an account, so there is no setup wall between deciding to try it and trying it.
The crisis-line help in the grief and hopelessness feeds belongs to the same instinct: build for the person actually arriving, in the state they are actually in.
This has been coming together for weeks, and most of that time went into the parts you cannot see in a repository: working out that reading surface, writing 66 book introductions, curating the topic feeds verse by verse, and working out how the Scripture storage and plan scheduling I had already built for PewHQ could be reused rather than rewritten. The code is the last and shortest phase of a project like this, and the commit history flatters it by hiding everything that came first.
It is live now at byanukh.app, which is the part that actually happened this fortnight.
What else is in it:
The reading surface. KJV and WEB, both public domain, with a version pill that keeps your place when you switch. A book, chapter and verse picker. Keyboard stepping for anyone reading on a laptop. Offline through a service worker, including the option to save a whole translation (about 4 MB) from the Account page.
Twenty-five topic feeds, grouped as “When you’re feeling” (afraid, anxious, grieving, lonely, angry, hopeless) and “Growing in” (honesty, patience, forgiveness, gratitude). Every verse links back to its chapter so you can see the context rather than the pull quote. The grief and hopelessness feeds show crisis-line help, 988 and findahelpline.com, because a feed about despair that offers no exit is not a neutral object.
Devotionals, now nine series: Forgiveness, Peace, Psalm 23, the Lord’s Prayer, Gratitude, and seasonal ones for Advent, Christmas, New Year and Holy Week that open themselves on the church calendar. Each day is a swipe through passage, reflection, question, prayer and a journal prompt whose answer saves and syncs.
Explain. On any verse, a sheet with the book’s introduction, 66 of them written for this, plus a generated explanation covering setting, speaker, meaning and key words. It runs on Grok’s non-reasoning model, specifically for speed, because a sheet that takes eight seconds to think is a sheet nobody opens twice. Cached per verse and rate-limited.
Listen, which reads verses aloud with the device’s own voice, advances by itself and holds the screen awake. One late fix there: every card now uses the same voice, because the browser picking a new one per utterance is deeply strange to listen to.
Reading groups, with invite codes, where a plan is read together from a shared start date and members see names and days done. Memory verse practice with five levels, from reading it through to first letters only. Shareable verse images as square or story PNGs in Night or Vellum style. Share links at /v/<book>/<chapter>/<verse> that open the reader at that verse, with a rendered verse card as the link preview. Year in review, from the Progress tab. And a per-book progress map that fills in by chapter, with a streak.
Reminders were the fiddliest part. A daily push at an hour you choose, skipped on days you have already read, showing your next plan reading or else the verse of the day. Devices live in Upstash Redis keyed by push endpoint and an hourly GitHub Action calls a secret-protected send route. But push notifications require permission, a service worker, and a device that cooperates, so there is a fallback that needs none of that: “Add to my calendar” downloads a daily .ics event, which works on anything. Reminders are also allowed to go out up to eight hours late now, because QStash delivery is not punctual and a 7am reminder arriving at 7:40 is better than one that is dropped for being stale.
Everything works with no account at all, stored on the device. Signing in, by email code, syncs chapters read, plan, streak, saved verses and position across devices, and merges never lose progress. Google sign-in went in behind a switch, then got its proper on-site button. The Google Play build is prepared as a Trusted Web Activity.
I want to be honest about what made this possible, because “and then a whole product appeared” is not a useful thing to read. Byanukh exists in this shape because PewHQ had already solved Scripture storage and plan scheduling, and because Ionnsaich had already taught me how a swipe-feed learning app wants to be built. Working on your own platform for long enough means the next thing starts somewhere in the middle.
ReelRifter: the month I spent $100 on robots
This is the story of the fortnight, and it is mostly a story about being wrong in an expensive and educational way.
ReelRifter ran up a $100 Vercel bill in October and opened November on a roughly $190 a month run rate. I found the cause on the 2nd, and it was /person/[id].
The mechanism. That route is ISR with generateStaticParams returning an empty array, so the first request for any TMDB person ID renders a ~120KB page and pays a cache write. TMDB person IDs run past 4.5 million and every single one of them resolves (/person/4567890 is a real person named Zhan Guozhi). So a crawler walking that ID space writes cache entries that nothing will ever read back. Three days of the cycle: 2.41 million ISR writes against 481,000 reads. ISR writes, fast origin transfer, fluid CPU, invocations and provisioned memory together were $19.58 of a $20.91 infrastructure total, and all five of those lines are the same event happening over and over.
For scale, Web Analytics counted 3,400 human events against 2.9 million function invocations in the same window. About 850 machine requests per actual person.
The first fixes were right but small./person/ came off the crawlable catalog in robots.txt, and the person page’s revalidate went from an hour to a day. That second one is worth explaining, because the measurement was clarifying: /person/6193 came back with an age of 8 seconds, but the long tail (/person/287, /person/999999) came back stale at ages of 18, 22 and 35 hours. At revalidate 3600, every one of those touches was past expiry, so each one regenerated the page and paid another write. At 86400 they are served as plain cache reads. But I worked out the ceiling on that fix at the time: writes cannot exceed reads for revalidation, so at most 481K of the 2.41M writes were regenerations. The other 1.9 million were first visits to IDs nothing had ever requested, and no revalidate value touches those.
The conclusion I had to reverse. I had been planning to convert the title pages, /[mediaType]/[id], to ISR the same way. I built all the plumbing for it: a wire format, because the viewer state returns Sets, Maps and Dates and none of those survive JSON; an anonymous viewer state so a crawler gets a complete signed-out page instead of a screen of skeletons; a state endpoint and a provider so islands fetch once and share. Nineteen round-trip checks, including a nested Map<string, Set<string>>. Then I looked at production logs: 24 title renders in 27 minutes, every TMDB ID distinct, none repeated, all deep catalog. The crawl walks the ID space without ever revisiting. ISR entries would be written once and read never, which is strictly worse than rendering dynamically, because an ISR write costs $4 to $6.40 per million against $0.60 per million for a function invocation. The conversion is rejected, not postponed. The plumbing is pushed and sitting there unwired, which I have decided to be at peace with.
The thing I would not have guessed. Crawlers execute JavaScript. Moving per-user state off the server into a client fetch, which is the exact pattern that made /person/[id] ISR-able, does not remove the work when the client is Googlebot. It turns one server render into one render plus a fan-out of uncached API calls. Which is how /api/content-badges became the third-busiest route on the entire site, at 40,000 uncached requests in 12 hours, while returning the hardcoded constant { news: false, shorts: false } to anyone signed out. Forty thousand function invocations spent answering “no”. Signed-out visitors no longer call the per-user endpoints at all.
Three genuinely public endpoints (person ratings, reviews, person notes, 26K uncached requests in 12 hours between them) moved to the edge. I checked each GET individually before touching it, because publicly caching a per-user response is the one mistake in this whole area that leaks data between people. None of the three calls auth() on the GET path, all three are byte-identical for every caller.
And then the actual answer. I turned on Vercel’s bot breakdown for 12 hours, against 213,000 CDN requests:
Googlebot made sixty-six requests. Baiduspider made ninety-four thousand, which is 1,424 times as many. Every search-engine assumption in this entire investigation, including my whole reluctance to touch /tv/ and /movie/, was protecting a crawler that is barely visiting.
Baiduspider, ExaSearchBot, Barkrowler and meta-webindexer are now blocked. Together they were 57% of every CDN request the site served, and none of them sends anyone back: Baidu has no audience for an English-language US streaming guide, Exa is an AI search index, Barkrowler is a backlink crawler. Baiduspider gets an explicit comment in the file explaining itself, because it is a real search engine and blocking one is normally the wrong instinct; it goes on the measurement, not the category. Bingbot stays, because it is real traffic feeding Bing, DuckDuckGo and ChatGPT’s search, and its rate is adjustable in Webmaster Tools, which beats blocking it.
This also explains why Vercel’s Bot Protection only caught about 4% when I turned it on: all of these identify themselves honestly and carry Vercel’s verified-bot badge, so the managed ruleset excludes them by design. Nothing was spoofing anything. The site was being crawled politely, at scale, by crawlers worth nothing to it.
One more expensive lesson. Vercel Observability Plus, which is what produced every table above, is billed at $1.20 per million events. It ran 1.63 million events on the 4th, which is $1.96 a day, about $59 a month, and it swallowed a 36 to 45% drop across every compute line that same day. The toggle is in Billing settings, not in the Observability tab where you would look for it. The right pattern is to turn it on for a day when you are diagnosing something and turn it off when you are done, and I have written that down somewhere I will find it again.
Cost per day went $5.92, then $5.64, with ISR writes per day falling $3.09 to $2.60 to $1.55 across the same window. Still open: the title route runs 158K dynamic renders a day at 0% cached, and the UA blocking happens in middleware, which costs a function invocation per blocked request. Moving those user agents into a Vercel WAF rule would block them at the edge for free.
And a separate worry that matters more than the bill. Googlebot made 66 requests in 12 hours. For a site that wants organic search, that is close to nothing, and it sits alongside human traffic around 1,000 pageviews a day and trending down 62%. That is a business problem wearing an infrastructure problem’s clothes, and it is next.
The actual product work, which did happen: episode search across your shows by title or description, episode deep links that open the Episodes tab and land on the right row, In-flight and Hotel as watch locations, Rewatch promoted out of the More actions dropdown into the main button stack, and a daily digest fix where “Netflix” and “Netflix Standard with Ads” were arriving as two separate alerts for the same title. Ad tiers now fold into their base service at alert creation, which also stops a false “just landed” when something already on Netflix merely gains the ad tier. The X auto-post went from four times a day to twice, halving that bill to about $12 a month.
Ionnsaich: a podcast, a release schedule, and learning to speak
Ionnsaich did an enormous amount, and it split cleanly into three ideas.
It became a podcast.npm run podcast joins each approved episode’s and story’s line recordings into a single MP3 with silent frames between lines, and writes two RSS feeds with iTunes tags, show notes carrying the Gaelic and English line by line, and cover art. Nothing is re-encoded and nothing is newly recorded; it is built entirely from audio that already existed for the lessons. Am Baile and the short stories are now listenable straight through, on Spotify, Amazon Music and YouTube Music, with the feed offered on the players to copy into any podcast app. The approval step rebuilds the feeds automatically and a check fails the build if they are stale. There is no Apple button until it is actually listed there, which is the sort of restraint I am trying to make habitual.
It got a release calendar. A story or episode can now carry a release day: approved, it stays out of the site, the players, the lessons and the podcast feeds until that day, and then appears with no deploy. The feeds became hourly routes reading what the build writes. Then I drafted and scheduled Seasons 5 through 9 of Am Baile with six stories each, one of each going out every Friday from 30 October through to 21 May 2027. That is roughly seven months of releases written, recorded, reviewed and queued. The autumn What’s new note tells people a new episode and story come out every Friday, and how to be told about it.
It got a Speak tab. Practice you say out loud instead of tapping: drills that give you the English, a pause to say it, then the recording; a story built from verified phrases and rehearsed; a monthly check-in that keeps the same five questions month over month so you can hear yourself improve; and 4/3/2 rounds that measure talking time and pauses off the microphone. Recordings never leave the browser.
And the content kept compounding. Ten new lesson units across A2 and B1 (travel, clothes, music, phones, telling a story, talking about Gaelic, looking after yourself, the news and the forecast), taking the path to 30 units and the phrasebook to 622 phrases. Example sentences drafted and approved for every dictionary word that no phrasebook phrase showed in use: 164, then 138, then 354 verbs and adjectives, then the last 437 nouns. The dictionary sits at 1,287 words.
Then the sayings. Wiktionary’s proverb collection ran out, so the next 120 came from Alexander Nicolson’s A Collection of Gaelic Proverbs and Familiar Phrases of 1882, public domain, put into today’s spelling, each with its English, a respelling, a word-by-word breakdown and a line on where you would actually hear it. The saying of the day now runs a 240-day cycle. Every batch of all of this went to a fluent reviewer before it reached a learner, which remains the part of this project I am least willing to compromise on.
Collections Plus: the first thing I have ever charged for
Two releases, and a line I have not crossed before.
2.11.0: watch saved pages for changes. Mark a page with the eye button and it gets re-checked in the background; when its readable text changes, a red dot appears on the page, on its collection’s cover, and as a count on the toolbar icon until you look at it. The text is fingerprinted with relative timestamps and other per-load noise ignored, so “2 hours ago” becoming “3 hours ago” is not a change. Signed-in, script-built pages like X and LinkedIn are read from an open tab instead of fetched, with a separate baseline so the two sources never cross-compare. Watch state merges across synced devices.
Plus Sync, phase 1, and Stripe.Collections Plus has always been serverless by design: your library lives in your browser and, if you want it on more than one device, in your own Dropbox. That is still the free product and still the default. But Dropbox setup is genuinely fiddly on a phone, and the honest answer for people who do not want to do it is a hosted option.
So: an invite-only sync API on getcollectionsplus.com storing each user’s library in Neon Postgres, with a hosted adapter in the mobile app sitting beside Dropbox, one provider at a time. Images become cpimg:<sha256> references so only missing ones are uploaded, the document is gzipped against Vercel’s 4.5 MB body cap, and pulls restore images from an IndexedDB cache. Device tokens exist because Clerk’s session cookie expires within a minute on pages that do not run Clerk, so the app cannot rely on it.
Then billing: Stripe subscription checkout, a customer portal, a signed webhook that re-fetches the subscription on every event and upserts current state, so retries and out-of-order events are harmless. There is a seven-day grace period on past due. $20 a year, behind a launch switch, with a complimentary allowlist.
And the part that came with it: the privacy policy had to stop saying there are no accounts and no developer-run service, because now there are both. New sections on what Clerk stores, what Google sign-in receives with the Limited Use statement, what Plus Sync stores and where, how to delete it and how long it is kept. The “no analytics” claim on the landing page is now scoped to the extension and the mobile app, since the website does have cookie-free Vercel analytics. Privacy questions and deletion requests go to a real support address rather than public GitHub issues.
One performance fix after launch: the app was polling for remote changes every 30 seconds, and each check wakes the Neon database, so it never suspended. It is two minutes now, and since the app already syncs on focus and after edits, the only thing that slows is noticing another device’s change while you sit idle.
SlingAgent: letting Claude draft, but never publish
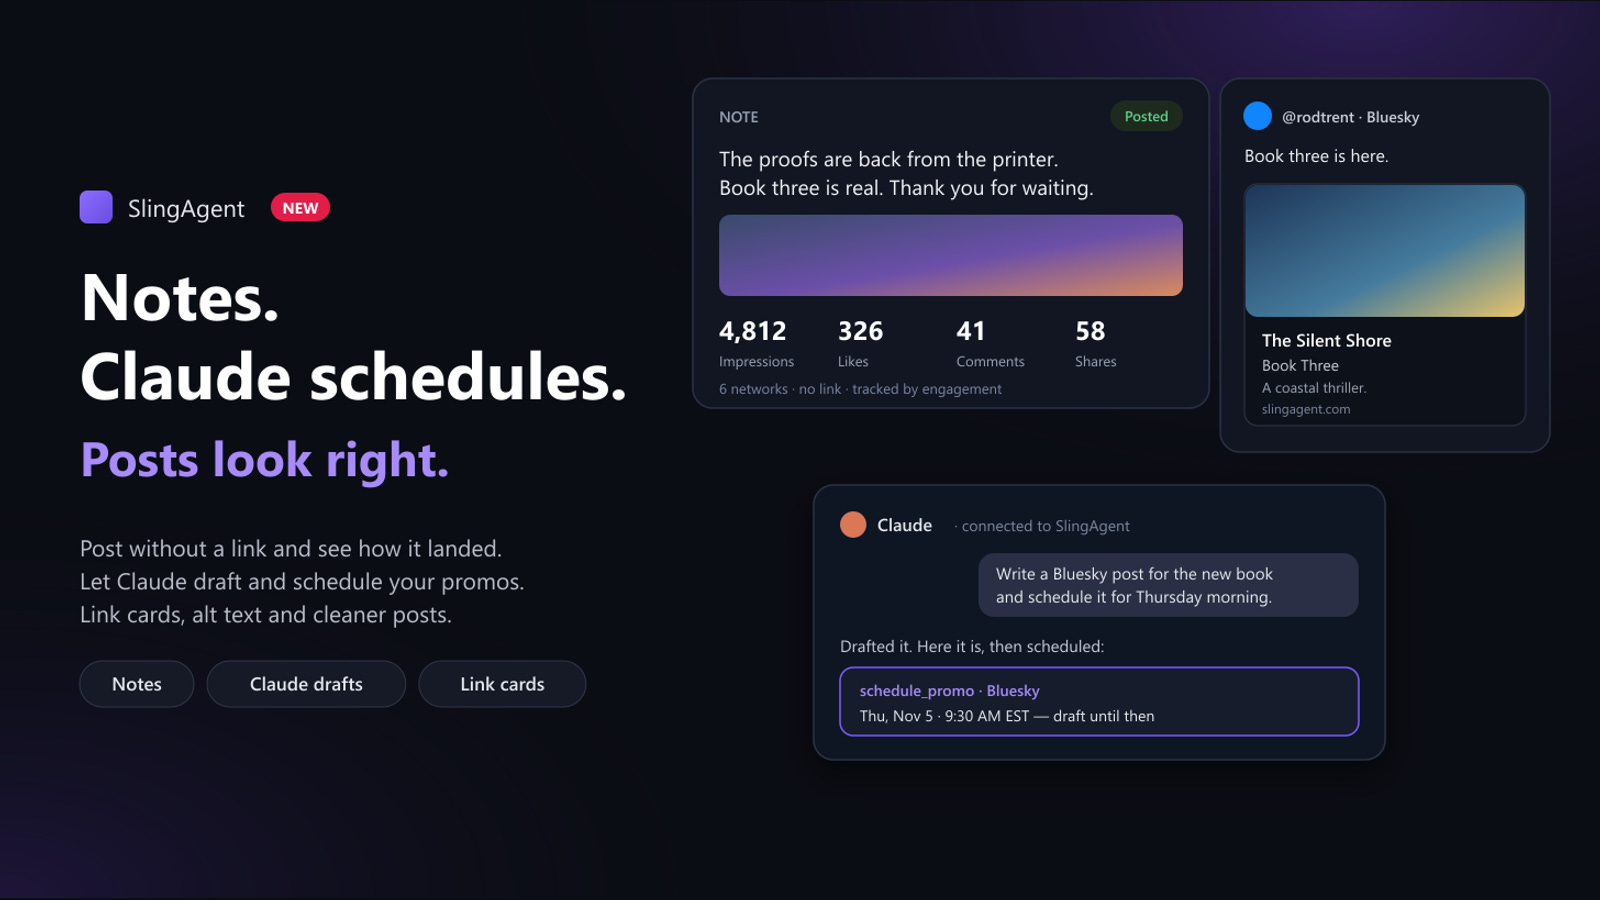
The big one is the MCP connector learning to write. New tools behind an opt-in promos:write scope: create a draft, generate drafts, edit a promo, schedule and unschedule. The constraint is the design: everything lands as a draft, and the only path to a network is a specific future scheduled time. There is no publish-now and no delete, and writes refuse a promo that is mid-delivery. The scope is a checkbox on the consent screen, pre-ticked only if the client asked for it; existing grants stay read-only and cannot be widened by a refresh, and personal API tokens stay read-only entirely. Tools outside your grant are not even listed.
I am fairly careful about this category. An agent for SlingAgent that can post to your social accounts on its own judgement is a different risk from one that can hand you five drafts, and the scheduling requirement means there is always a window where a human can look.
Also: a Notes report, since notes have no link and therefore no click report could say anything about them. It rolls up window totals, a weekly engagement trend, per-network engagement per post and a rate computed only over posts that actually reported impressions. Bluesky link cards, because Bluesky never builds one itself, so link posts were going out as a bare URL next to an image. And real image alt text: it was previously the post body repeated on Bluesky and LinkedIn, and missing entirely on Mastodon and X. It is now built from what the image actually is, the link title for a cover, the scene description for AI art, and nothing at all rather than a guess, which is the correct behaviour when you do not know.
TaskFolder 1.3.0
TaskFolder, the Windows tray launcher, shipped v1.3.0 on the 31st: dark mode, a dedicated Notes folder with subfolder support, OneDrive and Dropbox sync, mouse-button hotkeys (middle click, back, forward), import and export, drag to reorder, rich-text sticky notes, an update checker, enter-to-launch, an icon size toggle, and an xUnit test suite.
Then Sunday was a WinForms education. The Settings dialog became four tabs (General, Hotkeys, Shortcuts, Appearance) at a fixed ~420px height, so it no longer scrolls or scales awkwardly on high-DPI monitors, which needed AutoScaleMode.Dpi to stop buttons rendering as “Set”, “Browse” and “Cl”. Then dark mode: TabControl draws its separator and content border using Windows visual styles and ignores BackColor entirely. I tried owner-drawing it. The only reliable fix short of native subclassing was to delete the control and rebuild the tab bar out of a panel and four flat buttons. Appearance changes now offer to restart the app, since several of them only take effect on launch.
DumpDraft: check in where you are
DumpDraft got GPS check-ins: a “Check in here” action that grabs a one-shot high-accuracy fix on demand, with an inline bar for an optional place name, one-tap chips of places you have already named at this event, and a live status line while the fix lands. Tap save before the fix arrives and it defers and completes when the location does.
Place names started as purely user-entered, keeping the app local-first with no external calls. Then an opt-in toggle, off by default, added automatic suggestions through an OpenStreetMap Nominatim proxy that turns coordinates into “Venue, Area”. It is unauthenticated and read-only, because capture is never gated behind anything, it receives only a latitude and longitude and never any note content, and it sets the User-Agent that Nominatim’s usage policy requires. With the toggle off, no lookup happens at all.
A Bible app that had been quietly taking shape for weeks finally went live on top of two products I had already built, I charged money for the first time on a tool whose entire pitch was that it has no server, proved myself wrong about an architecture change I had already written the plumbing for, and then found that nearly half my streaming site’s traffic was a search engine with no audience for it while Googlebot, the one I had been carefully protecting, had visited sixty-six times.
See you next Friday
If you have ever bounced off a Bible because it is a wall of small text and a plan you fall behind on, try byanukh.app. No account, works offline, one verse at a time. I would especially like to hear from ADHD and neurodivergent readers about whether the reading surface actually holds, and whether the topic feeds find the right verses, since that is where my judgement is doing the most work and is least checkable from the outside.
And if you run anything on Vercel with a dynamic route over an ID space you do not control, go and look at your ISR write line and your bot breakdown, in that order. Turn the detailed observability on for a day and then turn it off again. Mine cost me about $100 to learn.
Reply to this or find me on Discord. Something always breaks, and I’d rather hear it from you than find it in a stack trace.
Rod
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
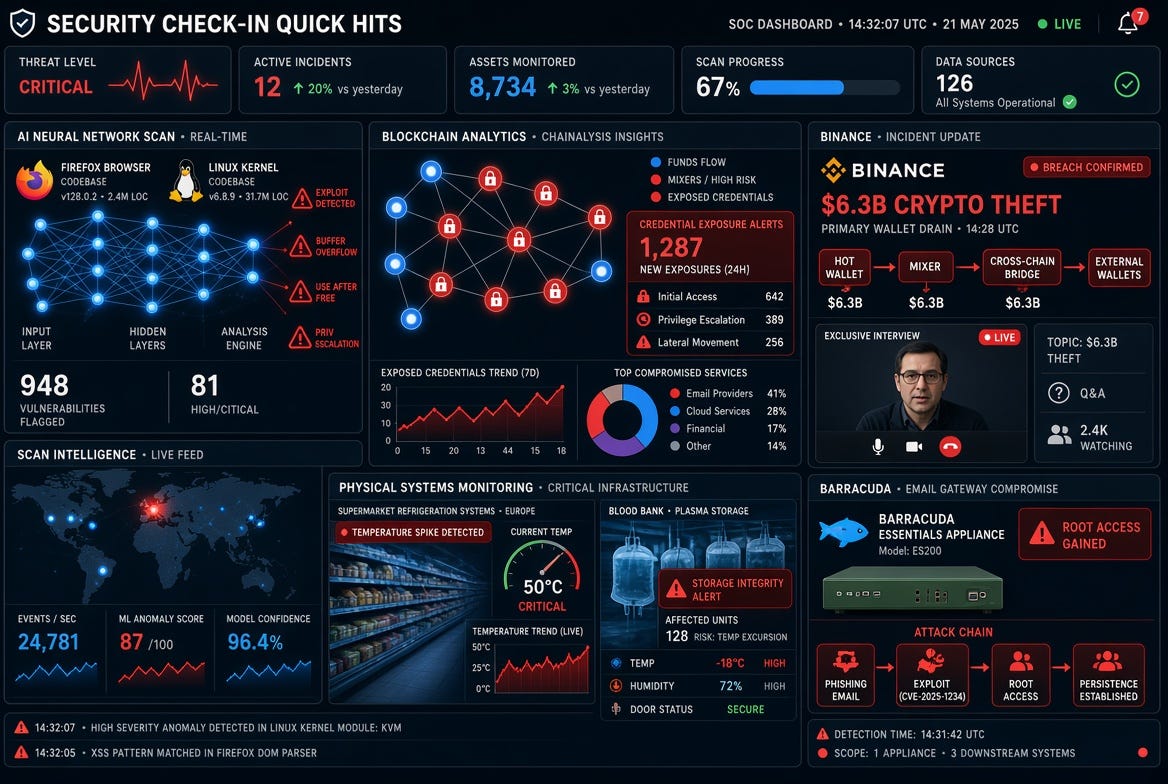
Chainalysis Confirms Agentic Attack Exposed Password Hashes and Live Tokens for All Users
Blockchain analytics firm Chainalysis has expanded its disclosure of an October cyber incident, stating that names, usernames, password hashes, and live authentication tokens belonging to all users were exposed. The company initially described limited “non-sensitive” data (user IDs, full names, emails, and role labels) accessed via “offensive agentic techniques.” Later updates confirmed broader credential exposure and an “on-path” (attacker-in-the-middle) component.
Chainalysis took Know Your Transaction (KYT), address screening, Reactor, and related services offline while investigating. As of early November 6, it began phased restoration of KYT and screening tools, requiring all users to reset passwords and rotate API keys. Trusted IP allowlisting is being enforced for restored access. The firm reports no evidence that investigation graphs, cases, transaction results, or attribution data were accessed or altered.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
The language around “agentic techniques” points to AI agents as part of the intrusion—an industry signal amid rising AI-driven attacks. Chainalysis serves law enforcement and compliance customers; the exposure of live tokens and password hashes creates immediate account-takeover risk even if cleartext passwords and MFA secrets were not confirmed stolen. Customers should treat every account as potentially compromised, reset credentials via the official site (not email links), and monitor for anomalous activity.
OpenAI’s GPT-6 Cyber Finds 81 High-Severity Firefox Flaws and Builds 948 Linux Kernel Exploits
OpenAI released GPT-6 Cyber, a restricted-access model specialized for vulnerability research. Rated “Critical” under the company’s Preparedness Framework (up from “High” for its predecessor), it is initially available only to approved Daybreak Red customers via API and Codex.
In research runs, the model uncovered 81 previously unknown high-severity vulnerabilities in Firefox—bugs that earlier AI testing had missed—and demonstrated that 30 known issues were more severe than reported. Mozilla has shipped fixes for many of them. On the Linux kernel, GPT-6 Cyber reproduced 1,724 vulnerabilities and generated working local privilege-escalation exploits for 948 of them (more than five times the 166 achieved by GPT-5.6 Sol under the same setup). OpenAI disclosed 304 critical findings to maintainers along with candidate patches. One research campaign cost roughly $1.2 million in API credits.
The results illustrate both the defensive upside (faster discovery and patching of hard-to-find flaws in widely used software) and the dual-use risk of highly capable offensive AI. Firefox users should ensure automatic updates are enabled; Linux administrators should prioritize kernel updates and limit local privilege where possible.
Second Wave of Freezer Hacks Hits European Supermarkets; French Blood Banks Also Targeted
A second wave of cyberattacks against refrigeration controllers struck supermarkets across Europe in early November, following a similar October campaign in France. Attackers remotely raised freezer and fridge temperatures—sometimes to 50 °C (122 °F)—forcing stores in Belgium, Sweden, Ireland, Luxembourg, Estonia, Finland, the Netherlands, and elsewhere to discard spoiled food. Chains including Carrefour, Delhaize, ICA, Coop, and SuperValu reported impacts. No ransom demands or public claims of responsibility have appeared.
The same class of internet-exposed industrial controllers was used against French blood-bank cold storage. At three Établissement français du sang (EFS) plasma sites, temperature and defrost thresholds were pushed to extreme levels (reports cited attempts to reach ~110 °C). Alarms and staff response prevented loss of blood products; supplies were transferred or secured. France’s ANSSI and other agencies are investigating. Common vectors involve devices such as Danfoss AK-SM/AK-SC series left on the public internet with default credentials or unpatched software.
These incidents highlight the fragility of operational technology in food and healthcare cold chains and the potential for low-complexity hybrid-style disruption. Operators should isolate refrigeration controllers from the internet, change default credentials, apply vendor patches, and monitor for anomalous temperature commands.
Binance Details How Fake Job Interviews and AI Tool Abuse Enabled $6.3 Billion Theft
Binance published findings on the record ~$6.3–6.43 billion crypto heist (attributed by the FBI to North Korea-linked TraderTraitor). The multi-month campaign combined social engineering, malware, and abuse of internal tools.
In June, one engineer installed a tampered Homebrew package while seeking an AI coding tool; Binance detected and remediated the device, but the attackers learned about wallet-team personnel. In September, a different engineer was contacted via a legitimate job platform by someone posing as a Project Director. After video interviews (including one with a purported CEO who shared social-media photos and videos to build trust), the engineer downloaded a malicious “assignment” repository onto a work laptop. The malware evaded detection, replaced a legitimate tool component, and established command-and-control. Attackers later leveraged the compromised host and an internal AI tool to pivot to other wallet engineers’ systems and execute unauthorized transfers in late October.
The case underscores the sophistication of state-linked social engineering against crypto infrastructure and the risk of AI tooling once endpoint access is obtained. Organizations should treat unsolicited coding assignments with extreme caution, enforce strict device controls, and segment access to high-value systems.
Barracuda Email Security Gateway Flaws Chain to Unauthenticated Root Access
Barracuda patched two vulnerabilities that can be chained for root access on Email Security Gateway (ESG) appliances without a valid login. CVE-2026-116606 (CVSS 9.3) is a pre-authentication authorization bypass allowing an unauthenticated attacker who can reach the admin interface to restore a crafted configuration backup and alter global settings. CVE-2026-111560 (CVSS 8.6) is a command-injection flaw in the timezone field (shared across several Barracuda products) that executes OS commands as root.
On ESG, the bypass provides the administrative context needed for the injection, yielding full root. Patches were released around November 2–3; researchers at watchTowr and Mandiant detailed the chain. Prior ESG incidents (e.g., the 2023 zero-day) make rapid patching essential. Organizations should update to the latest firmware, restrict administrative interface exposure, and review logs for unexpected configuration restores or timezone changes.
These stories illustrate the dual-use nature of AI in offense and defense, the continuing exposure of industrial control systems, and the effectiveness of social engineering against high-value targets. Prioritize patching, credential rotation, network segmentation, and verification of unsolicited “assignments” or configuration changes.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Most of us know the feeling. You open a Bible app with the best of intentions, and you’re met with a wall of tiny text. Two paragraphs in, your mind has wandered to the grocery list, the email you forgot to send, the thing someone said yesterday. You close the app. Tomorrow you try again, and the same thing happens.
Meanwhile, the same phone holds apps that can keep us scrolling for an hour without our noticing. One thing on screen at a time, a flick of the thumb, and the next thing appears.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
So I asked a simple question: what if reading the Bible felt like that?
That question became Byanukh, and today I’m glad to share it with you.
What is Byanukh?
Byanukh is a Bible reader built like TikTok. Each verse fills the whole screen. Swipe up, and the next verse appears. That’s the whole idea, and it changes more than you’d expect.
The name is the phonetic spelling of the Scottish Gaelic word Beannachd, which means “blessing.” That’s what I hope it is for you.
It’s free, it runs in any modern browser on your phone, tablet or computer, and you can install it to your home screen like any other app. (Android folks: it’s coming to Google Play soon.) You don’t need an account to start. Just go to byanukh.app and begin swiping.
Built for minds that wander (including ADHD and neurodivergent readers)
I want to say this part plainly, because it’s at the heart of why Byanukh exists.
Traditional Bible reading assumes a kind of attention that many people don’t have, or don’t have every day. If you live with ADHD, or you’re autistic, dyslexic, anxious, exhausted, or just wired differently, a page packed with columns, verse numbers, footnotes and cross-references can feel like a wall rather than a doorway.
Byanukh was designed around a different kind of reader:
One idea per screen. Each verse stands alone on its own card, so you take in one thought at a time. Nothing competes for your eyes. Scripture’s ideas get naturally segmented, verse by verse, so they’re easier to absorb and easier to remember.
Calm, readable type. Large, clear serif text with plenty of space around it, in a warm light theme or a soft dark theme that follows your device.
Small, finishable steps. Every swipe is a tiny win. You’re never staring at how much is left on the page, only at the verse in front of you.
Momentum without pressure. The next verse is always one flick away, and you can stop anytime. Byanukh remembers exactly where you were.
Explain, right on the verse. When a verse is confusing (and plenty are), tap Explain. You get a short, plain-language breakdown: the setting, who’s speaking, what it means, and the key words, alongside an introduction to the book you’re reading. No need to leave the app, open a commentary, or lose your place and your focus.
Listen instead of read. On days when reading text is hard, Byanukh can read the verses aloud using your device’s voice, moving to the next verse on its own.
The goal is simple: take away the friction between you and the Word.
Three ways to read
1. Read the whole Bible, cover to cover
Pick any book, chapter and verse, and start swiping. Chapters flow straight into the next, and books flow into the next book, so you never hit a dead end.
Want structure? Choose a reading plan:
The Bible in a Year: Genesis to Revelation, cover to cover
New Testament in 90 Days
The Gospels in about a month
Psalms in 60 Days
Proverbs in 31 Days
Each day’s reading opens right in the feed and ends with a “mark day done” card. Your Progress page fills in a tile for every book of the Bible as you read it, and shows your percentage of the whole Bible and your daily streak.
2. Find the verses you need, when you need them
Some days you don’t need a plan. You need a word for right now.
Topics are hand-picked verse feeds for the moments of life:
“When you’re feeling…” afraid, anxious, grieving, lonely, angry, discouraged, hopeless, doubting, guilty, weary, tempted, or in need of help
“Growing in…” honesty, patience, forgiving others, gratitude, strength and courage, wisdom, love, and more
Every verse links back to its full chapter, so you can see it in context. And for the heaviest topics, like grief and hopelessness, Byanukh also shows where to find crisis support, because sometimes a verse isn’t all you need. In the US, that’s the 988 Suicide & Crisis Lifeline (call or text 988). Anywhere else in the world, findahelpline.com lists free, confidential helplines in your country.
3. Go deeper with devotionals
The Explore tab holds devotional series written for Byanukh. Each day is a short swipe through a passage, a reflection, a question to sit with, a prayer, and a journal prompt. Your journal answers are saved.
Series include:
Seven Days on Forgiveness
Do Not Worry: A Week of Peace
Seasonal series that open on the church calendar: Advent: Light in the Dark, Christmas: The Word Made Flesh, New Mercies: A Week for the New Year, and Holy Week: The Road to the Cross
Everything Byanukh can do
Here’s the full list:
Swipe-to-read feed. One verse per full-screen card. On a computer, use the arrow keys, J/K, or the space bar.
Go anywhere. Jump to any book, chapter and verse.
Two translations. The King James Version (KJV) and the World English Bible (WEB). Switch anytime and stay on the same verse.
Explain. A plain-language explanation of any verse (setting, speaker, meaning, key words), plus an introduction to every one of the 66 books.
Topics. Hand-picked verses for how you’re feeling and what you’re growing in.
Devotionals. Daily passage, reflection, question, prayer and journal prompt, with seasonal series.
Reading plans. From Proverbs in a month to the whole Bible in a year.
Daily reminders. A gentle push notification at the hour you choose, skipped on days you’ve already read. It shows your next plan reading or the verse of the day. Prefer your calendar? Add a daily reading event instead.
Listen. Verses read aloud, advancing on their own, with the screen kept awake.
Save verses. Double-tap a verse (or tap the heart) to keep it.
Memorize. Practice saved verses across five levels, from reading the full verse down to first letters only.
Verse images. Turn any verse into a beautiful square or story-sized image, in a dark “Night” or warm “Vellum” style, ready to share or download.
Share links. Send a verse to a friend, and the link preview shows the verse itself.
Reading groups. Start a group, invite people with a link, and read a plan together from the same start date. Members see each other’s names and plan days done, and nothing else.
Progress and streaks. A tile for every book that fills as you read, plus your daily streak.
Year in review. Days read, streaks, your best month, and verses kept.
Works offline. The app and Scripture are kept on your device, and you can save a whole translation for reading with no signal at all.
Installable. Add it to your home screen and it opens like a native app. A Google Play version is on the way.
No account needed. Everything is stored on your device by default.
Optional sync. Sign in with Google, or with just your email (no password), and your reading, plan, streak, saved verses and place sync across all your devices.
Why I built it
I’ve spent a lot of my life around technology, and I’ve watched how well our apps hold our attention. I don’t think that attention is wasted on everything; I think it’s been aimed at the wrong things.
Byanukh is my small attempt to turn the same design toward something that actually feeds the soul. Not to make Scripture shallow, but to make it reachable: one verse, one thought, one swipe at a time.
“Thy word is a lamp unto my feet, and a light unto my path.” (Psalm 119:105, KJV)
A lamp doesn’t light the whole road at once. It lights the next step. That’s how Byanukh works too.
Try it today
Head to byanukh.app on your phone, swipe up, and see how it feels. Add it to your home screen, pick a plan or a topic, and let me know what you think.
If it helps you, please share it with someone who’s always wanted to read the Bible but never found a way that stuck. That might be exactly who this was made for.
Beannachd. Blessings.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
For almost six years, THE PROMPT for Microsoft Security has landed in your inbox nearly every Friday morning. It started back in late 2020 out of necessity: partners and customers needed a way to keep up with how fast the Microsoft Security platform was moving – the updates, the new features, and all the great content coming from the community. It began life on Revue (Twitter’s old newsletter tool), migrated to Substack in early 2023 (the first Substack issue was #57 in January 2023), and later grew to include Security Copilot and related content, trading its original name, “Microsoft Defender Weekly Wrap,” for the one you know today. Through all of it, the Friday-morning cadence never changed.
But, as with everything, things change. Life and work have made keeping up with this every week increasingly difficult. So, even though my blog will continue on its normal path and frequency, this particular newsletter is ending.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
It’s also worth being candid about something else. Over the past year or so, the steady stream of layoffs, retirements, reorgs, and redirections across the industry – including within Microsoft – has had a real impact on the kind of content that’s available to share. Many of the people who wrote the deep-dive blogs, built the community tools, recorded the videos, and answered questions in the forums have moved on to new roles or new companies, or simply have new priorities. Teams have been combined, product focus has shifted, and some great sources of content have gone quiet. The result is that there’s less of the hands-on, community-driven material that made this newsletter so valuable each week, and curating a full issue has become a much bigger challenge than it used to be.
And, additionally, like everything in life, my focus has changed. While I was squarely in the Microsoft Security stack for the past few years, I’m now more focused on development and security Agents and that doesn’t always fit neatly within the Microsoft Defender tools. More to come on this.
It’s been an amazing time and an amazing chance to connect with all of you – more than 30,000 readers every week – and to share Microsoft content with the community. Thank you for reading, sharing, and sending feedback along the way.
Instead of leaving everyone in the lurch, though, I’m happy to point you somewhere great. Ex-Microsoftie Merill Fernando has announced an expansion of his newsletters, so you can keep getting your Microsoft Security fix every week. Check out Merill’s announcement.
See you on the blog. That’s it for me for this particular newsletter.
What’s new in Microsoft Security: November 2026 - Endpoint administrators need to keep elevated access accountable at scale. Security teams also need a clearer view of expert-led protection and a simpler way to deploy SQL Server protection in Azure Government. As AI agents gain access to business data and tools, organizations need ways to limit their authority and adapt protection as risk changes. This month’s Microsoft Intune and Microsoft Defender updates introduce capabilities across these areas, alongside new Secure AI capabilities for agent access. A recent Secure Now update in Microsoft Security Exposure Management also connects information on recent threats to focused initiatives for reducing exposure.
Securing AI Adoption in the DIB-Part 2: Microsoft’s Approach to Discovering & Securing AI - In Part 1 of this series, we examined how AI is changing the risk landscape for the Defense Industrial Base (DIB). Those risks span three layers: how people use AI, the AI applications organizations build and deploy, and the platforms that host them. Agents add a new dimension, acting as non-human identities that hold credentials, access data, and take actions on behalf of users. Yet the most significant risks remain rooted in identity, access, data governance, monitoring, and lifecycle management. These are familiar problems, and they can be solved by extending Zero Trust. Part 2 describes Microsoft's approach to AI security and walks through the first two priorities, Discover & Observe and Secure, using capabilities available in GCC High today.
New Investments to Reduce On-Premises Security Risk - On-premises servers can be essential to business operations, but they are increasingly attractive targets to attackers. AI can help less-skilled actors analyze software, develop malicious tools, and repeat attack workflows at greater speed and scale, shortening the window between exposure and exploitation. Organizations need to strengthen security faster without disrupting the critical workloads they rely on.
Arc proxy support for Defender for SQL Servers on Machines - Defender for SQL Servers on Machines now supports Azure Arc SQL Server instances with Arc proxy enabled, starting with Defender for SQL extension version 2.0.3585.403. Organizations that don’t allow direct internet access from their machines can tunnel outbound communication through Arc proxy and use all Defender for SQL Servers on Machines features.
Arc proxy is an optional setting and isn’t required for Defender for SQL Servers on Machines to operate if the networking prereqs are met. Learn more about Defender for SQL on machines prerequisites.
Version 2.0.3585.403 is available for manual update. Automatic rollout hasn’t started, giving customers time to review affected resources and prepare for expanded protection coverage.
Email threat landscape: Q3 2026 trends and insights - Microsoft Threat Intelligence detected approximately 7.3 billion email-based phishing threats from July through September, including a sharp increase to nearly 3 billion in September alone, up 41% from August. Yet the increase did not extend across the techniques that had driven threat actor activity earlier in the year. QR code phishing remained far below its early-year peak, while CAPTCHA-gated phishing reversed several months of decline, driven in part by renewed use of SVG attachments.
Defender Threat Intelligence Things
Fake-download campaign uses trojanized installers to deliver monetization payloads - Microsoft Threat Intelligence has identified an evolving fake-download campaign targeting users searching for cracked commercial software, free games, activators, plugins, and unofficial utilities. The campaign uses trojanized Inno Setup-style installers to distribute multiple monetized software payloads, referred to by the delivery system as “offers”, during a single installation session.
Threat actors use agentic AI tooling to find and abuse exposed secrets - Microsoft Threat Intelligence has observed threat actors using an agentic AI offensive framework to search public GitHub repositories for exposed secrets, including credentials, application credentials, and AI inference-related API keys across multiple applications and cloud services. These threat actors can then use the secrets for further malicious activity against the compromised organization.
Microsoft Entra Things
Global Secure Access: Private and Internet Access in one offering - Employees, and now AI agents, need secure access to resources wherever they live: the internet, Microsoft 365 and SaaS, cloud and datacenter workloads, on-premises apps, and AI services. Zero Trust means evaluating every one of those connections against full context, including identity, risk, device, app and data, location, and network, and enforcing the decision continuously, not only at sign-in. Organizations need to do that without stitching together separate tools and policies.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Binance Details Multi-Stage $6.3 Billion Heist Driven by Fake Job Interviews and Internal AI Tool Abuse
Binance has released a detailed account of the record cryptocurrency theft that occurred around October 29, 2026. The attack was a months-long campaign rather than a single breach. It began in June when an engineer downloaded a tampered developer tool (linked to a search advertisement in some accounts). In September, attackers used a legitimate job platform to contact another engineer, conducted interviews (including with a purported CEO), shared personal social media content to build trust, and tricked the employee into downloading a malicious coding assignment that infected a work laptop with obfuscated malware that evaded endpoint detection.
The compromised access, combined with an internal Binance AI tool, allowed lateral movement to other engineers’ systems and ultimately the wallet authorization infrastructure. The FBI has linked the operation to North Korean-linked actors (TraderTraitor). Binance reports freezing or intercepting roughly $2.85 billion and replenishing the large majority of impacted assets, while commissioning an independent review. The case underscores persistent risks from sophisticated social engineering and the dual-use dangers of internal AI tooling.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Zyxel GS1900 Switches Hit by Zero-Day That Bypassed Earlier Patch; Nearly 1,000 Devices Compromised
Researchers at Binarly identified CVE-2026-107441, an unauthenticated out-of-bounds write in the web management interface (dispatcher.cgi) of Zyxel GS1900 series switches. It enables OS command execution via crafted HTTP requests from the adjacent network and can yield root-level access. The flaw was exploited in the wild (observed from around mid-August) against approximately 996 devices across 48 countries, with attackers (tracked as Kapibala by GreyNoise) stealing configurations, network details, and hashed root credentials. Many compromised units still used factory defaults.
Critically, a June patch for a related buffer-overflow issue (CVE-2026-7273) did not stop this exploit, as validation checks arrived too late in the processing path. Zyxel released updated firmware (builds ending in .3)C0 on October 22 for ten models (including GS1900-8, -24, and -48 variants) and published an advisory on November 3. Administrators should immediately apply the new firmware, remove internet-facing management interfaces, and change any default credentials.
GhostMap: Android Flaw Lets a No-Permission, No-Code APK Force Persistent Crash Loops
Bitdefender Labs disclosed GhostMap, a parser differential bug in how Android handles ZIP entries inside APKs. A malformed entry (neither standard “stored” nor “deflated” compression method, with an oversized declared uncompressed length) causes libandroidfw to map the file into unallocated memory. When a process (notably system_server during package scanning) reads past the real file end, it triggers a SIGBUS crash. The process restarts, re-reads the entry, and crashes again—creating a boot loop that persists across reboots and even in safe mode.
The proof-of-concept app requires no permissions, contains no executable code, and does not need to be launched. Researchers reproduced it on a Pixel 10 running Android 17 (August 2026 patch) and confirmed impact from Android 10 onward. Recovery typically requires a factory reset (data loss) or, if USB debugging was already enabled, ADB deletion of the offending files. Google classified the issue as outside the scope of a security update after reports in August. While no confirmed in-the-wild exploitation of the crash behavior has been reported yet, the public details raise denial-of-service risks for Android devices.
Marsalek Infostealer: Free Malware-as-a-Service Hidden in Fake Roblox, Fortnite, and Other Game Cheats
McAfee Labs detailed Marsalek, a free malware-as-a-service platform active roughly from mid-December 2025 to late May 2026. It distributed information-stealing malware disguised as game cheats, script executors, and utilities for Roblox, Fortnite, Counter-Strike 2, Minecraft, and others. The service provided a public dashboard for payload building (PowerShell, Python, PE, ClickFix vectors), victim tracking, and data access, with a free tier requiring no account.
The multi-stage payloads ultimately steal browser passwords and cookies (Chromium-based and Firefox), Discord tokens, Telegram sessions, crypto wallet data, and more. It employed dual-hook techniques (including PureLog) so stolen data could reach both the customer and the platform operators. McAfee observed more than 1,560 registered accounts, over 400 malicious files, and numerous distribution URLs, often via Discord, GitHub, and fake sites. The campaign targeted gamers seeking unofficial tools and demonstrates the continued effectiveness of gaming-related lures for credential and crypto theft.
ARTEX AI Tool and LLMs (Including Claude Code, DeepSeek, and Grok) Used in Attacks on South Korean Banks
CrowdStrike and related reporting continue to highlight a campaign in which a financially motivated, likely Chinese-speaking actor used the open-source Chinese AI-powered penetration-testing suite ARTEX, combined with large language models, against South Korean financial institutions in late September–early October 2026. Targets included employee- and partner-facing systems at banks such as Shinhan, KB Kookmin, and Hana (plus smaller lenders), resulting in exposure of personal and financial data affecting tens of thousands of records (reports cite figures around 68,000 people across institutions).
The operator leveraged ARTEX with backends including DeepSeek, supplemented by Claude Code sessions involving models such as GLM and Grok. Operational security failures—exposed directories containing Claude session histories, configurations, and even a résumé draft—aided attribution and investigation. The incidents illustrate how accessible agentic AI tools can accelerate reconnaissance and exploitation against real organizations, prompting regulatory responses in South Korea.
These stories reflect a landscape of sophisticated social engineering (including AI-assisted), network device zero-days that evade prior patches, novel mobile denial-of-service, gaming-targeted stealers, and the growing weaponization of open-source AI pentesting frameworks. Organizations should prioritize rapid patching of exposed management interfaces, employee awareness around recruitment scams and unsolicited downloads, mobile app installation hygiene, and monitoring for AI-driven attack patterns.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
In the previous post I listed seven non-negotiables for secure coding once agents can both write code and install the tools that run it. Point 5 — inventory every agent, its allowed tools, its data access, and its approval boundaries — is the one that sounds simple until you try to do it at team scale. Dean asked the obvious next question: what tools or techniques actually keep that list from turning into a lie within a month?
Here’s the practical answer.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Treat skills the way you already treat packages and IAM roles
A skill is a folder containing a SKILL.md (plus optional scripts, references, and assets) that an agent loads to gain a specialized capability. In Claude Code, Cursor, Codex, Copilot, and a growing list of other tools, that folder can pre-approve tools, run shell commands, read files, and call external services. Uninventoried skills are equivalent to unreviewed privileged services running on developer machines and in CI. The control model is the same one that already works for dependencies and roles: versioned, reviewed, owned, and least-privilege.
The minimum viable inventory
Start here. Most teams get 80% of the value with no new infrastructure.
Git as the source of truth. Store skills as folders in a dedicated repo or monorepo. Changes go through normal pull requests. Use CODEOWNERS. Require a short security checklist on every change.
Pin everything. Install from a specific commit, tag, or digest. Never floating “latest.” Record the hash in the inventory.
An explicit inventory table. A spreadsheet, a markdown file in the same repo, or a lightweight page in whatever system you already use. Columns that matter:
Skill / agent name
Allowed tools and data access
Approval boundaries (who can change it, what it is allowed to do)
Owner (named person)
Source and hash
Last review date
Review before it is allowed to run. The eight-point check that keeps showing up in the better write-ups is good enough:
Read the entire skill.
Confirm scripts match the stated purpose.
Look for adversarial or hidden instructions.
Check for unexpected network calls or external URLs.
Confirm there are no hardcoded credentials.
Verify the tools and commands are the minimum required.
Look for data-exfiltration patterns.
Require an owner and a reviewer who is not the author.
Anything that fails the checklist stays out of the approved set. Anything without an owner gets removed.
Tooling that makes the inventory continuous
Once the number of skills or the blast radius grows, manual tracking breaks. These are the approaches that are currently useful:
Dedicated skill registries. SkillReg is the clearest example of applying the package-registry model to SKILL.md files. It gives you semantic versioning with immutable releases, organization-level access control, automated scanning on publish (secrets, destructive commands, exfil patterns, unapproved URLs), download analytics, and CLI installs that target Claude Code, Codex, Cursor, and others. It is the closest thing to “npm for agent skills” that exists today.
Continuous discovery. StepSecurity’s Dev Machine Guard and GitHub Agent Skills views inventory skills found on developer machines and in your organization’s repositories. They show which agents can load each skill, whether it contains executable content (code, hooks, shell), and where it came from. This is the practical way to find the shadow installs that never made it into the official list.
Scanners and loadout auditors. Tools such as skill-audit (prompt-injection and exfiltration checks, SARIF output) and loadout scanners that report collisions and actual usage from traces belong in CI or as part of the PR gate. They do not replace human review; they make the review faster and more consistent.
Public skill directories and marketplaces are useful for discovery. They are not a substitute for a private, reviewed, versioned inventory of the skills you actually allow.
Techniques that keep the inventory from rotting
Narrow the allowed-tools frontmatter. Broad tool access is a privileged role; treat it like one.
Separate skills (procedures and workflows) from MCP servers (live system access). Inventory both. An agent that can call an MCP tool should have an explicit record of that tool, its credential scope, and its owner.
Log skill add, change, and remove events with hash, source, and approver. Alert on credential-path access or unexpected egress while a skill is active.
Enforce allowlists where the agent supports them (Claude Code managed settings and similar controls). On corporate devices, only approved skills and plugins should load.
Prune on a schedule. Quarterly review of unused skills, plus immediate revocation of anything that loses its owner. Skills that no longer match real work or that models now handle unaided should be deleted.
When to level up
If you have fewer than ten skills and a single team, the Git repo + inventory table + checklist is enough. Move to a private registry and continuous discovery when:
Multiple teams share skills
Skills contain scripts or pre-approved tools
You need an audit trail for compliance or incident response
Shadow installs start appearing on developer machines
The teams that treat AI-generated code and agent skills as first-class attack surface will ship more safely than the teams that treat them as productivity features. The inventory is the difference between those two outcomes. Everything else is optional until the inventory is real.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
NOTE: This post is purely hypothetical, intended to be thought provoking. Even so, it illustrates how healthy communities are shaped and sustained by the people in them—and how their evolution is ultimately driven by the community itself.
Imagine the announcement lands on a quiet morning: after more than three decades, the Microsoft MVP program is ending. No more renewals. No more early access. No more formal recognition, Global Summits, or the quiet status that comes with the blue badge. The program that began in 1993 on CompuServe forums—born from a simple list of the people answering the most questions—is gone.
What does that world look like? And who picks up the work?
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Before the Badge
There was a time before structured vendor programs, and it wasn’t that long ago. In the 1990s, people who needed help with Microsoft technologies gathered on CompuServe, Usenet, and whatever web forums they could find. Recognition came from answering hard questions consistently, not from an award letter. The original MVP idea itself grew out of that environment—Calvin Hsia’s list of top posters in the FoxPro forum, followed by Microsoft inviting a handful of those people to the first TechEd.
Around the same period, independent communities formed for the same reason: official channels weren’t enough, and people needed places to trade practical knowledge. myITforum was one of those early experiments. It started as a focused hub for systems management professionals dealing with SMS and ConfigMgr, grew through forums, articles, and a newsletter, and became a daily destination for tens of thousands of IT people. No vendor owned it. No badge was required to participate. It existed because enough people decided the problems were worth solving together.
That pattern has repeated across technologies and eras. Communities form where the friction is high and the official answers are incomplete. Vendor programs later formalized and amplified some of that energy. They didn’t invent it.
What Disappears (and What Doesn’t)
If the MVP program (and similar vendor programs) vanished, several things would change quickly.
Formal recognition would vanish with it. The badge has long served as a shorthand for “this person has demonstrated consistent, high-quality community impact.” Without it, reputation becomes harder to signal and easier to contest. Hiring managers, event organizers, and customers would have to rely more on public work—blogs, talks, GitHub contributions, long-running forum or Discord threads, and word of mouth.
Early access and direct product-team relationships would also tighten. MVPs have historically received pre-release information and a structured path for feedback. Product teams would still need real-world input, but the mechanism would likely become more selective, more ad-hoc, or more commercial (paid ambassadors, customer advisory boards, or public beta programs with fewer privileges). The feedback loop wouldn’t stop; it would just lose one of its more consistent channels.
Some people would step back. A portion of contribution is motivated by the recognition, the access, or the sense of belonging to a formal group. When those incentives disappear, so does some of the activity. That is normal. Not every volunteer effort is purely intrinsic, and programs make the extrinsic path clearer.
What would not disappear is the underlying need. IT professionals still hit obscure problems at 2 a.m. Product teams still need to understand how their tools actually behave in customer environments. People still enjoy explaining hard things to others. The infrastructure for that has improved dramatically since the CompuServe days.
How Community Would Flourish
Today’s tools make independent community far more viable than it was in the late 1990s or early 2000s. A single person can run a Substack that reaches thousands, host real-time discussions on Discord, publish technical deep-dives on a personal site, speak at independent conferences, and maintain a GitHub repository of samples and tools—all without permission from a vendor.
The people who already do most of the real work would continue. Many current MVPs blog, speak, answer questions, and build samples because they like the work and the audience, not solely because of the annual award. Remove the award and the most committed ones keep going; the audience simply follows the content rather than the badge. New voices would also emerge more easily once the formal gatekeeping of recognition is gone. Reputation would be earned in public, repeatedly, rather than conferred once a year.
Independent spaces would fill the gap. Local user groups, vendor-neutral conferences, focused Discord servers, long-running newsletters, and open-source communities around specific tools would absorb more energy. Some would stay tightly focused on one vendor’s stack; others would deliberately stay multi-vendor or technology-agnostic. The fragmentation would increase, but so would ownership. Creators would control their audiences and archives instead of depending on a corporate program that can change direction.
Product feedback would become messier and more public. Instead of structured MVP feedback channels, more of it would surface in open GitHub issues, public blog posts, Reddit threads, and social media. Some of that would be noisier. Some of it would reach the right people faster because it is visible to everyone, not just a selected group.
Who Takes the Mantle?
No single organization replaces a 30-year program. The mantle goes to whoever shows up consistently with useful answers.
It goes to independent writers and practitioners who already treat community as part of their work—people running technical newsletters, maintaining documentation sites, or organizing local meetups. It goes to the organizers of conferences that have long operated with partial or no vendor funding. It goes to open-source maintainers and the communities that form around specific tools, regardless of which company ships the commercial version. And it goes to platforms that let individuals own the relationship with their audience rather than renting it from a vendor program.
In short, it goes to the same kinds of people who built the early forums and sites like myITforum: practitioners who needed better answers than they could find, and who decided to create the place where those answers could live.
Vendor programs are amplifiers. They make recognition easier, access more reliable, and certain conversations more direct. They are not the source of the desire to help, to teach, or to improve the tools everyone uses. That desire existed before the first MVP awards were mailed out in 1993, and it would still exist the morning after any program shut down.
Communities are resilient because they form around problems, not around awards. The tools are better now than they were when the earliest independent IT forums appeared. The people who care enough to keep answering the hard questions are still out there. They always have been.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
European Supermarket Freezer Cyberattacks Disrupt Food Supply Across Multiple Countries
A second wave of cyberattacks has targeted supermarket refrigeration systems across at least 10 European countries, including Belgium, Sweden, Ireland, the Netherlands, Luxembourg, Estonia, Finland, Portugal, Germany, and Italy. Attackers remotely seized control of internet-exposed refrigeration controllers, switching freezers into defrost mode or raising temperatures as high as 50–55°C (122–131°F). This forced retailers such as Delhaize, Carrefour, ICA, Coop, SuperValu, and others to discard large quantities of spoiled chilled and frozen goods.
The attacks, which began overnight into early November 2026, echo a larger October incident that affected roughly 700 French supermarkets and caused tens of millions of euros in losses, with some reports of fires. Equipment suppliers including Sabcobel and systems from vendors like Danfoss, Copeland, and Dixell were implicated; known vulnerabilities in remote management software allowed unauthenticated access when units were not properly segmented or patched. EU officials described the incidents as a deliberate effort to disrupt the food supply chain and undermine consumer confidence. No group has publicly claimed responsibility, though state-linked actors (with Russia or China frequently speculated) remain the leading theories given the low technical complexity and high psychological/economic impact. Stores reported rapid detection in some cases, but food waste was widespread.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Recommendations: Inventory and isolate internet-facing OT/IoT refrigeration controllers; apply vendor patches immediately; enforce network segmentation and MFA where possible; monitor for anomalous temperature commands.
Binance Details Multi-Stage North Korean Campaign Behind Record $6.34 Billion Crypto Heist
Binance released its initial incident report on the October 29, 2026, heist that drained approximately $6.34 billion in digital assets from hot wallets—the largest cryptocurrency theft on record. The FBI has attributed the attack to North Korea’s TraderTraitor group. The campaign spanned months and combined social engineering, malware, and abuse of internal tools rather than a single point of failure.
It began in June when a wallet DevOps engineer downloaded a tampered installer for an AI coding tool. Security detected and remediated that foothold, but the attackers learned team structure. In September, they targeted another engineer via a legitimate job platform with a fake company, complete with social-media profiles containing personal photos and videos to build trust. During a second interview (with a purported CEO), the engineer was instructed to download a malicious “coding assignment” that installed undetected malware. On October 20 the attackers leveraged the compromised host plus an internal AI tool to pivot onto additional wallet-engineer machines. On October 29 they executed a rapid multi-asset drain (including hundreds of millions of XRP in minutes). Binance reports that roughly $2.85 billion was frozen or intercepted; the exchange has replenished most customer assets and is commissioning an independent review while strengthening controls.
Recommendations: Treat recruitment processes and coding assignments as high-risk vectors; enforce strict separation between personal and work devices; monitor AI tool access and wallet-signing workflows; implement robust endpoint detection that catches obfuscated loaders.
Google Dismantles XCPE Botnet of 1.3 Million Android TV Boxes with Pre-Installed Backdoors
Google’s Threat Intelligence Group, working with partners including Japan’s National Police Agency, Trend Micro, and others, dismantled the XCPE (X.CPE) botnet that had enrolled more than 1.3 million Android TV set-top boxes and related IoT devices. Google attributes the operation with high confidence to Shenzhen-based Videostrong Technology, an Android OEM/ODM that deliberately embedded the backdoor in firmware. The malware turned devices into residential proxies, facilitated ad fraud, and served as a dropper for additional malware families. Infections spanned more than 200 countries, with heavy concentrations in Brazil, Malaysia, Iraq, Mexico, and Taiwan; related infrastructure may have affected up to 10 million additional devices.
Google took legal action against command-and-control domains and servers, severed its relationship with Videostrong (banning the company and future affiliates from certified Android devices or software supply), and tightened its certification review process to close the obfuscation loophole that allowed the malware to load after first boot. The backdoor itself remains on already-shipped devices; owners are advised that factory reset or updates may not remove it.
Recommendations: Identify and replace affected Android TV boxes and similar IoT hardware; monitor outbound proxy-like traffic from consumer devices; review supply-chain integrity for Android-certified products.
cPGuard Update Channel Hijacked in OpsShield Supply-Chain Attack
Indian security vendor OpsShield disclosed that attackers compromised its update infrastructure and pushed malicious cPGuard updates to customer Linux servers. Using stolen credentials obtained after probing the billing/licensing portal (including registering a fake customer account and exploiting command execution), the attackers uploaded poisoned packages (versions 5.88.12–5.88.19). The malicious script ran as root for roughly 70 minutes starting around 02:08 UTC on November 2, installing a backdoor shell, harvesting password hashes, root SSH keys, MySQL/MariaDB configs, shell history, and other sensitive files, then exfiltrating them via the vendor’s own licensing server. Approximately 2,950 servers executed the fake updates; ~7,900 client account records were also copied.
OpsShield detected the issue within about 12 hours, revoked the stolen keys, and released clean version 5.88.25/5.88.26 that removes the backdoor and staged files. Affected customers must treat systems as fully compromised and rotate all credentials.
Recommendations: Immediately update cPGuard to 5.88.25 or later; rotate all secrets (SSH keys, database passwords, root hashes); review update logs for the affected versions; implement egress controls that scrutinize even “trusted” vendor channels.
CISA Adds Actively Exploited WordPress Core Flaw to KEV Catalog
CISA added CVE-2026-119977 (CVSS 8.1) to its Known Exploited Vulnerabilities catalog on November 3, 2026, confirming active exploitation. The flaw is a TOCTOU race condition in WordPress Core (versions 4.7 through 7.1.3) that arises during full-package upgrades. Predictable, web-accessible staging paths under wp-content/upgrade allow unauthenticated attackers to reach a staged setup-config.php installer during the brief upgrade window and achieve remote code execution as the web-server user. WordPress patched the issue in 7.1.4 (released October 28) by randomizing staging directories and adding safeguards; backports are available for older supported branches. CISA set a November 6 due date for federal agencies. Telemetry from security firms recorded tens of thousands of probing attempts in the first 24 hours after disclosure.
Recommendations: Update WordPress Core to 7.1.4 (or the latest security release for your branch) immediately; if an upgrade is in progress or recently completed on an unpatched version, treat the site as potentially compromised and perform forensic review; enable automatic background updates where feasible.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
The last update was all about analytics: one filter for every report and a live click feed. Since then the work has been on the other side of SlingAgent, the posting side. There’s a new kind of post, a new way to use Claude, and a long list of small changes that add up to posts looking right wherever they land.
Notes: post without a link
Not everything you share is a promotion. Sometimes it’s a thank-you, a behind-the-scenes photo, a book that just went to the printer, or a thought you want your readers to see. Until now, everything in SlingAgent was built around a link. Notes aren’t.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
A note is just your words, plus an image if you want one, sent to the accounts you pick. No link gets added. Open Post a note, write it once (or tailor it for each network), add an image, and post it now or schedule it for later.
A note has nothing to click, so SlingAgent tracks it by what the networks report instead: impressions, likes, comments and shares, collected overnight. Each note shows its numbers per network and in total, and the new Notes report shows the bigger picture: how your notes did week by week, which network they land best on, and your best notes. The Analytics overview has a Notes card with the headline numbers too.
A few things I added after using it:
One row per note. A note sent to six networks shows as one note with six results underneath it, not six rows.
No accidental double posts. SlingAgent won’t post the same note to the same account twice. If you open an old note to post it somewhere new, the networks it already went to are unticked and show when they went out.
Keep the list tidy. Under Settings → Notes you choose how long notes stay in your list. Removing one never deletes the posts from the networks.
Notes are on every plan. Scheduling a note is on paid plans, the same as everything else.
Notes from any page, with the browser extension
The SlingAgent browser extension is at version 1.0, and its big addition is notes. It opens the same panel as Share once, right on the page you’re reading:
Right-click an image → Post this image as a note starts a note with that image attached.
Select some text → right-click → Post selection as a note starts one with those words, line breaks kept.
Write a note in the toolbar popup opens an empty one.
You get the same accounts, Hashtag Groups, AI hashtag suggestions and scheduling as on the web, and you see each network’s result when it posts.
Let Claude draft and schedule
SlingAgent has had an MCP connector since October, so Claude could read your analytics and answer things like “which network sent the most clicks this month?” It could look, but it couldn’t do anything.
Now, if you allow it, Claude can also write posts and put them on your schedule. Ask “write three Bluesky posts for my new book and schedule the best one for Thursday morning” and it can do that: draft the posts (its own words, or SlingAgent’s generator in your brand voice), show them to you, change them, and schedule the one you pick.
I was careful about how much it can do:
It’s off unless you turn it on. When you connect SlingAgent to Claude, there’s a box: Also let it draft and schedule posts. Leave it unticked and the connection stays read-only, like before.
Everything starts as a draft. Nothing Claude writes goes out until it’s scheduled, even on links you’ve set to post automatically.
No posting on the spot, no deleting. The most Claude can do is put a post on your schedule at a time you agreed on. You can see it, change it or cancel it in SlingAgent before it goes out.
If you already have SlingAgent connected to Claude, your connection is still read-only. To turn on drafting, disconnect it in Claude, connect again, and tick the box. Settings → API tokens → Connected apps shows which access each app has. This is on the Unlimited plan; setup is in the docs.
Posts that look right everywhere
This is the part you won’t see a button for. Every network has its own rules for how a post looks, and a few of ours weren’t being followed. Now they are:
Bluesky link cards. Bluesky doesn’t build a preview from a link the way other networks do; whoever sends the post has to. SlingAgent wasn’t doing that, so Bluesky promos went out as a bare link next to a picture. Now they get a proper card with your title, description and image, which is a much easier thing to tap.
Real image descriptions. Screen readers read an image’s description (its alt text) aloud. Ours used to be the post text again, so a listener heard the same sentence twice. On some networks there was no description at all. Now it describes the actual image: the product or book title for a cover, the scene for AI artwork. If there’s nothing true to say about an image, SlingAgent says nothing rather than guessing.
The link comes before the hashtags. Posts used to put the hashtags first, which buried your link under a row of tags. Now it’s your text, then the link, then the hashtags, on every network and in every copy button.
Long posts on X stay long. Every X post was being cut to fit the standard limit, which shortened posts from Premium accounts that can post much more. SlingAgent now sends the whole post and only shortens it if X refuses it.
Ad Kit covers aren’t cropped. Wide images used to be cut to a square in the Ad Kit banners, which sliced words off screenshots. The whole image shows now.
Inbox: one account at a time
If you have more than one Bluesky or Mastodon account, the Inbox now lets you filter to one of them, next to the status and sentiment filters. Mark all done clears only the account you’re looking at. The Inbox is on Pro and Unlimited.
Smaller things
Share once keeps your image. If you attach an image and come back to a share later, it reopens with the image still there. The composer also says when it’s still attaching a page’s image and waits for it before posting.
Your days, everywhere. The sentiment report and the traffic sources trend now split days and weeks at your midnight, like the rest of Analytics.
Fewer failed generations. When the AI model is busy, SlingAgent falls back to a lighter one instead of giving up.
Who gets it
Notes, the posting fixes and the extension are on every plan. Scheduling is on paid plans, the Inbox on Pro and Unlimited, and Claude drafting on Unlimited. Every new account starts with 14 days of Pro, no card needed.
Zero Trust has always been more than a slogan. “Never trust, always verify” forced organizations to abandon the castle-and-moat model and treat identity, device health, network context, application access, and data classification as continuous decision points. Those classic pillars—Identity, Devices, Network, Applications/Workloads, and Data—still form the foundation. CISA’s Zero Trust Maturity Model and NIST SP 800-207 codified the architecture; Microsoft’s long-running Zero Trust guidance operationalized it for hybrid environments.
In 2026 the foundation is no longer sufficient on its own. AI agents, Copilots, autonomous workflows, and AI-assisted development have introduced new trust boundaries, non-human identities operating at machine speed, and software supply-chain risks that traditional pillars do not fully address. Microsoft has formalized the response by expanding its Zero Trust tooling: the Zero Trust Assessment now evaluates seven pillars (adding Infrastructure, Security Operations, and AI to the original set), while the Zero Trust Workshop has gained a dedicated DevSecOps pillar alongside an enhanced AI pillar.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
These are not marketing add-ons. They are the practical recognition that Zero Trust must now govern both the systems that use AI and the systems that build software in an AI-accelerated world.
Why the Classic Pillars Needed Company
The three core principles remain unchanged:
Verify explicitly — every request is authenticated and authorized using all available signals.
Use least privilege — access is limited to the minimum required for the task and for the shortest practical time.
Assume breach — design so that a compromised identity, device, or workload has limited blast radius.
What changed is the subject of those principles. AI agents act with the flexibility of humans but the scale and speed of machines. They can be prompted (or indirectly injected) into taking actions, they hold runtime credentials, and they often inherit overly broad service-account permissions. At the same time, developers are using AI coding assistants that generate code, recommend packages, write infrastructure-as-code, and automate tests. A governance gap in either domain can create over-privileged agents or insecure artifacts that traditional identity and network controls never see.
AI as a First-Class Zero Trust Pillar
The AI pillar treats agents, models, tools, prompts, and memory as resources that require the same rigor as human users and corporate data.
Key focus areas include:
Identity and access for agents. Every agent should have its own managed identity rather than inheriting a user’s standing privileges. Conditional Access and risk signals evaluate agent requests continuously, just as they evaluate human sign-ins.
Data protection across the AI lifecycle. Sensitive data used in training, retrieved at inference time, or generated in outputs must be classified, labeled, and subject to DLP. Memory itself is treated as a governed boundary with provenance, lifecycle controls, and user visibility.
Monitoring and governance. AI usage and behavior are monitored for anomalies, misuse, and prompt-based attacks. Signals feed into security operations so that abnormal agent activity can trigger investigation or revocation.
Responsible governance. Inventory of AI agents and applications, ownership, acceptable-use policies, and alignment with risk and compliance objectives.
Microsoft’s updated Zero Trust Assessment adds automated checks specifically for these AI controls. The Workshop’s AI pillar (and the accompanying guidance based on Microsoft’s AI Memory framework) translates the principles into scenario-based tasks organized in the familiar “First, Then, Next” maturity sequence.
In practice this means an agent summarizing customer tickets should not automatically inherit the ability to modify those tickets or exfiltrate the underlying data store. Continuous verification and least-privilege scoping for tools and connectors close that gap.
DevSecOps as the Other Essential Pillar
If AI is the new runtime trust boundary, DevSecOps is the new build-time trust boundary. Microsoft introduced a dedicated DevSecOps pillar in the Zero Trust Workshop containing 15 control groups and 91 tasks that apply the three Zero Trust principles from source code through cloud deployment.
The pillar covers:
Developer platforms and identity/access for engineering systems
Source repositories and branch protections
Dependencies and the software supply chain
Artifacts and build integrity
CI/CD pipelines
Infrastructure-as-code and containers
Overall DevOps posture and governance
Four tasks focus specifically on AI-assisted development: code governance, tool allowlisting, data protection for AI coding workflows, and securing AI/ML pipeline supply chains. The guidance connects directly to the Identity, Infrastructure, and Security Operations pillars because a compromised pipeline token or unsigned dependency can create identity and runtime risks elsewhere in the environment.
Workshop sessions for this pillar typically walk through DevOps identity and access, source code security, supply-chain and dependency controls, CI/CD pipeline security, IaC and container security, and posture/governance—roughly six hours of structured discussion that produces a prioritized 12- to 24-month roadmap.
The practical translation is straightforward: a coding assistant may only use approved tools and repositories; generated pull requests follow the same (or stricter) review and secret-scanning rules as human-written code; pipeline identities are narrowly scoped and short-lived; and every artifact carries provenance.
How the New Pillars Reinforce the Foundation
AI and DevSecOps do not replace Identity, Devices, Network, Data, or Infrastructure. They amplify them.
An AI agent still needs a strong identity (Identity pillar) and can only reach data that is properly classified and protected (Data pillar). Its network communications and any infrastructure it touches remain subject to segmentation and posture controls. DevSecOps reduces the chance that insecure code or a poisoned dependency ever reaches production, thereby lowering the load on runtime detection in Security Operations. Conversely, the visibility and automated response capabilities in SecOps become more valuable when they can correlate signals from AI agents and from the software supply chain.
The August 2026 Microsoft updates make this interconnection explicit: assessment findings from the expanded seven-pillar Assessment map directly into Workshop roadmaps that include both the AI and DevSecOps pillars, so teams can sequence work across security, platform, and engineering organizations.
Practical Next Steps
Establish a baseline. Run the updated Zero Trust Assessment to surface gaps across Identity, Devices, Data, Network, Infrastructure, SecOps, and AI. Use the results as input to a facilitated Workshop.
Inventory agents and AI tools. Treat every agent as a non-human identity with an owner, a purpose, and an explicit scope of authority. Require separate credentials and least-privilege access packages.
Apply the DevSecOps controls. Start with the “First” phase tasks—secure developer environments, repository protections, dependency management, and pipeline identity hygiene—then move to AI-specific governance (tool allowlists, code review policies for generated code, and supply-chain controls for ML artifacts).
Integrate signals. Feed AI agent activity, pipeline events, and supply-chain alerts into your SIEM/XDR so detection and response span both runtime and build-time domains.
Govern memory and prompts. Treat conversation history, retrieved context, and tool outputs as data that requires classification, retention limits, and protection against injection or exfiltration.
Microsoft has published practical patterns (least privilege for AI agents, Zero Trust for source code access, managing memory safety, protecting the software supply chain) and an e-book, Zero Trust for AI: Rebuilding security controls for autonomous and agentic systems, that expand on these steps.
The Bottom Line
Zero Trust was never a finished product. It is an operating model that must expand as the attack surface expands. AI agents and AI-accelerated software delivery are the two largest expansions organizations face today. Elevating AI and DevSecOps to explicit pillars—complete with assessment checks, control groups, and phased roadmaps—gives security, platform, and engineering teams a shared language and a concrete plan.
The principles have not changed. The subjects of those principles have. Organizations that treat AI and DevSecOps as first-class Zero Trust domains will be able to move faster with lower residual risk. Those that continue to apply only the classic pillars will discover that their continuous verification stops at the edge of the agent or the pipeline.
Start with the assessment, map the gaps into a roadmap, and treat every agent and every build pipeline as a resource that must be verified explicitly, granted least privilege, and designed under the assumption of breach. That is Zero Trust for the systems we are actually running in 2026.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
European Supermarkets Hit by Second Wave of Refrigeration Cyberattacks
Overnight into November 2, 2026, attackers remotely altered settings on internet-exposed refrigeration and freezer controllers at dozens of stores across at least seven European countries, including Belgium, Sweden, Ireland, Luxembourg, the Netherlands, Estonia, and Finland. Temperatures were raised as high as 50–55°C (122–131°F), spoiling chilled and frozen food and forcing retailers to discard inventory and empty shelves.
Chains such as Delhaize (Belgium and Luxembourg), Carrefour, Spar/Colruyt, ICA and Coop (Sweden), and SuperValu (Ireland) reported impacts. One Belgian Delhaize store estimated losses near €100,000; earlier French attacks in October affected hundreds of stores and caused tens of millions of euros in damage. Controllers from vendors including Danfoss and others were involved, often left internet-exposed with weak or default credentials.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
No group has claimed responsibility. The EU described the incidents as a deliberate attempt to disrupt food supply chains. This follows a similar French wave three weeks earlier and highlights longstanding OT/IoT risks in retail cold chains—legacy systems, remote management portals, and insufficient network segmentation. Retailers and vendors should immediately isolate controllers from the internet, enforce strong authentication, apply available patches, and monitor for anomalous temperature commands.
Google Dismantles XCPE Botnet of 1.3 Million Android Devices
Google’s Threat Intelligence Group, working with partners including Japan’s National Police Agency, Lumen, HUMAN Security, Plume, Synthient, and TrendAI, disrupted the XCPE (x.cpe) botnet in late October 2026. The botnet enrolled more than 1.3 million Android set-top boxes and other devices. Google assesses with high confidence that Chinese OEM/ODM Videostrong Technology intentionally embedded the persistent backdoor in firmware across multiple models and brands over years, then sold access to criminal affiliates.
Affiliates used the devices for ad fraud, residential proxy networks, and loading additional malware. Google took legal action to seize control domains and servers, severing access to the XCPE bots and at least 10 million additional devices controlled via related modules. It banned Videostrong and future affiliates from certified Android devices and tightened firmware integrity checks. The backdoor remains on already-shipped boxes and cannot be fully removed by owners, so replacement is the practical remedy for affected users.
This case underscores supply-chain risks in consumer IoT and the limits of certification programs when manufacturers deliberately introduce malware.
UK NCSC Warns AI-Powered Ransomware Highly Likely on Critical Infrastructure by 2028
The UK’s National Cyber Security Centre (part of GCHQ) published its State of the Cyber Nation assessment on November 3, 2026. It judges it highly likely that AI-powered malware will be used in a ransomware attack on UK critical national infrastructure by 2028. By that date, Russia, China, and other states are expected to routinely use AI-cyber tools, increasing the scale and speed of attacks. Many systems will remain vulnerable because AI tools can discover and exploit long-tolerated weaknesses at unprecedented scale.
NCSC CEO Richard Horne blamed decades of “tech on the cheap,” warning that organizations that fail to invest will face explainable outages affecting food, power, and services. China is assessed as best positioned and highly likely to target CNI. The UK is responding with investments including a national Cyber Shield, a National Exposure and Real-Time Vulnerability Centre, and an AI Cyber Security Centre of Excellence. Malicious cyber activity already costs UK organizations an estimated £14.7 billion annually.
The assessment stresses that AI primarily accelerates existing tactics rather than inventing entirely new ones, but the economics favor attackers.
Attackers Exploit Critical Siemens IoT2050 Flaw for Backdoors
VulnCheck reported active exploitation of CVE-2026-58115 (CVSS 10.0), a missing-authentication vulnerability in Siemens SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED. Unauthenticated remote attackers can create malicious flows via the Node-RED HTTP interface and execute arbitrary code with maximum privileges. Siemens patched it in version 4.3.4.1 (disclosed August 2026).
Honeypot captures beginning October 30, 2026, showed opportunistic scanning that delivered Linux botnet binaries, shell scripts, and persistent HTTP-triggered command backdoors that survive reboots. Activity appeared mass-scanning rather than highly targeted. Organizations running affected gateways should update immediately or harden/uninstall Node-RED (enable HTTPS, authentication, and restrict access).
This joins a broader pattern of internet-exposed OT and industrial IoT devices being rapidly weaponized once vulnerabilities become public.
Additional notable activity includes the FBI’s attribution of the roughly $6 billion Binance cryptocurrency theft to North Korea’s TraderTraitor group, ongoing exploitation of Ivanti Connect Secure zero-days, and attempts against an unpatched CryptoPayment Gateway WordPress plugin (CVE-2026-81648).
These incidents illustrate persistent themes: exposed OT/IoT, supply-chain compromise, nation-state and criminal monetization, and the accelerating role of AI.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
At MMS Midway I talked about treating agents as people—not in the science-fiction sense, but as a practical design discipline. When you build an agent the way you would onboard a new hire, you stop creating one all-powerful “super agent” and start creating specialists with clear jobs, limited authority, and explicit boundaries. That separation is the difference between an agent that is useful in a SOC and one that becomes a liability.
The five separations that matter most are roles, access, tools, knowledge, and capabilities. Get these right and the rest of your agent architecture becomes far easier to secure, observe, and improve.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Roles: One Job, One Agent
A role is the agent’s job description. It answers: What is this agent responsible for, and what is it not responsible for?
The best agents are narrow. A SOC Triage Agent does not also write detections, update tickets, and hunt for anomalies. Those are different jobs. When you collapse them into one prompt and one toolset, the model has too many conditional branches, tool selection becomes noisy, and failures become harder to diagnose.
Treat the role like a job posting:
Primary objective
Explicit non-goals
Escalation criteria (“hand this to a human when…”)
Success criteria
In the templates shared from the sessions, each agent (SOC Triage, Threat Hunter, Finding Validator, Detection Engineer) has its own identity, purpose, and output schema. That is intentional. Specialization improves reliability and makes the human-in-the-loop boundary obvious.
Agent role is the explicit job description that defines what a single agent is responsible for—and, just as importantly, what it is not responsible for.
What it is
A role is a narrow, written statement of purpose. It answers:
What is the primary objective of this agent?
What are the explicit non-goals (things it must never do)?
When should it escalate or hand off?
How is success measured?
Examples from a SOC:
SOC Triage Agent — Receives an alert, performs initial enrichment and disposition, and produces a structured recommendation. It does not write detections or close tickets.
Threat Hunter Agent — Takes a validated lead and runs deeper investigation against specific hypotheses. It does not perform initial triage or create analytics rules.
Detection Engineer Agent — Turns a confirmed finding into a candidate detection rule. It does not investigate raw alerts.
Finding Validator Agent — Checks evidence quality and confidence before anything is promoted. It does not collect the evidence itself.
Each role is deliberately limited so the agent stays focused, its prompt stays simple, and its tool and knowledge needs stay small.
Why it matters
Without a clear role, agents tend to become generalists. One agent ends up responsible for triage, enrichment, investigation, ticket updates, and detection authoring. The prompt grows full of conditionals, tool selection becomes unreliable, failures are harder to diagnose, and the blast radius of any mistake or compromise expands.
A well-defined role delivers:
Reliability — Fewer decisions and fewer tools mean fewer opportunities for the model to choose the wrong action.
Security — The role itself becomes a policy boundary. You grant access, tools, and knowledge only for that specific job.
Maintainability — You can improve, replace, or retire one role without rewriting the others.
Clear handoffs — Each agent knows exactly when its work is done and what structured output to pass to the next specialist.
How it fits the “agents as people” model
Just as you would not hire one person to be the entire SOC, you should not build one agent to be the entire workflow. A role is the equivalent of a job posting or job description:
It sets expectations before the agent is built.
It determines the identity, access, tools, knowledge, and capability boundaries that follow.
It makes ownership and accountability concrete—a human owns a specific role, not an amorphous “AI system.”
It enables the fire-and-rehire pattern: when a role is no longer effective, you decommission that agent and stand up a new one with a clean role definition.
In short, the role is the starting point. Everything else—identity, least-privilege access, narrow tools, curated knowledge, and the autonomy gradient—flows from a clear answer to the question: “What is this agent’s job?”
Access: Least Privilege, Always
Access is what systems, data, and identities the agent can reach. This is classic zero-trust applied to non-human principals.
Give every agent its own identity (Entra Agent ID, service principal, or equivalent) with a named human owner. Then scope it tightly:
Read-only where possible
Data filtered to what the role actually needs
Time-bounded or just-in-time elevation for higher-risk actions
No shared service accounts that outlive the task
An agent that can query Sentinel under the analyst’s own RBAC is safer and more auditable than one running with broad standing privileges. When something goes wrong, you can revoke that identity without taking down everything else. Inventory these identities the same way you inventory other assets—because you cannot secure what you cannot see.
Agent identity means giving every AI agent its own distinct, first-class identity in your identity system—exactly as you would for a human user or a workload—rather than letting it run under a shared service account, a user’s credentials, or no identity at all.
What it is
An agent identity is a lifecycle-managed principal (for example, an Entra Agent ID, a dedicated service principal, or an equivalent workload identity). It has:
Its own credentials or tokens (short-lived and audience-scoped wherever possible)
A named human owner who is accountable for it
Explicit permissions and tool grants tied to that identity
An auditable trail of every action it takes
It is not the same as impersonation. When an agent acts on behalf of a user, the effective permission is the intersection of the user’s rights and the agent’s own scoped rights. The agent keeps its separate identity so you always know which agent performed the action.
Why it matters
Without a distinct identity, an agent is just an anonymous process that can do whatever the credentials it holds allow. That creates several problems:
No precise attribution — You cannot tell which agent did what when multiple agents share the same account.
Over-privilege — Shared or broad credentials give every agent the maximum rights of that account.
Hard revocation — Disabling one agent can break others that share the same identity.
Weak audit and response — Incident response becomes guesswork instead of a targeted revoke-and-replace.
With proper agent identities you get the same operational controls you already apply to employees and service accounts: least privilege, ownership, logging, and the ability to disable or replace one agent without affecting the rest of the environment.
How it fits the “agents as people” model
Just as a new hire receives a badge, a job-specific role, and an accountable manager, each agent receives:
An identity (the badge)
A role with scoped access, tools, knowledge, and capabilities (the job)
A human owner (the manager)
This is what makes the other practices possible. You can fire an agent by revoking its identity and grants. You can rehire a replacement with a clean identity. You can hand off work between agents because each has a clear, auditable identity and a defined output contract. And you can apply zero-trust checks (verify the agent, verify the action, log everything) on every tool call.
In short, agent identity turns an agent from an opaque automation into a manageable principal. It is the foundation that lets the role, access, tools, knowledge, and capability separations actually improve security instead of remaining theoretical.
Tools: Narrow, Named, and Allow-listed
Tools are the actions an agent is permitted to take (API calls, MCP tools, functions, runbooks). They are the difference between reasoning and doing.
Best practice is to expose only the tools required for the role, with clear names, schemas, and descriptions. Overlapping or vaguely named tools create selection errors. High-impact tools (write, delete, send, escalate) should require explicit approval gates rather than living in the same allow-list as read-only queries.
In practice this looks like:
Tool allow-lists enforced outside the model
Structured, typed outputs
Idempotent actions where possible
Logging of every tool call with the agent identity and the human it is acting for
Tool design often matters more than prompt engineering for security. A well-scoped tool set reduces the blast radius of prompt injection because the agent simply cannot call what it is not allowed to call.
Knowledge: Curated Context, Not Everything
Knowledge is the information the agent can retrieve or is given—documents, RAG sources, memory, prior conversation, or retrieved data.
Not every agent needs the same knowledge base. A triage agent may need recent incident context and enrichment data. A detection engineer needs detection rule patterns and known-good baselines. Dumping the entire company wiki into every agent’s context increases cost, latency, and the chance of irrelevant or conflicting information.
Treat knowledge sources as scoped resources:
Separate ephemeral session context from durable memory
Filter retrieval by data classification and role
Treat retrieved content as untrusted input (it can contain injection attempts)
Prefer retrieval of what is relevant over stuffing the entire history into every call
Capabilities: Decide the Autonomy Gradient Up Front
Capabilities cover what the agent is allowed to decide and execute on its own versus what requires a human. This is the autonomy gradient.
Start restrictive and expand only when measured performance justifies it. A common and effective pattern is:
Agent reasons and recommends
High-impact or irreversible actions require explicit human approval
Separate “read and analyze” agents from “act” agents when risk differs
This is the same principle we use with junior analysts: give them the ability to investigate, but gate the actions that change production or notify customers. The agent can own the reasoning without owning the authorization.
Better Protection and Security Through Clear Boundaries
Framing agent creation this way—clear roles with tightly scoped access, tools, knowledge, and capabilities—directly improves the security posture of the environment.
Each separation reduces blast radius. A compromised or misbehaving triage agent cannot rewrite detections or exfiltrate data it was never granted. Least-privilege identities and allow-listed tools mean a prompt-injection attempt has far fewer actions available to it. Because every agent has its own identity and explicit human owner, audit trails become precise: you know exactly which agent took which action, under whose authority, and against which data. Failures stay contained instead of cascading. Zero-trust principles apply cleanly because there is no implicit trust based on “the agent can see everything.” You can enforce policy at the identity, tool, and data layers rather than hoping the prompt stays well-behaved. The result is an environment that is easier to monitor, revoke, and recover—exactly the controls security teams already expect for human operators and service accounts.
Fire and Rehire Instead of Endless Modification
Because each agent is built as a distinct specialist with its own identity, scoped permissions, tool allow-list, knowledge sources, and capability boundary, you can treat it like an employee. When an agent is no longer effective, is outdated, or has accumulated technical debt from repeated prompt and tool tweaks, you simply fire it: revoke its identity, remove its tool grants, delete its scheduled runs, and archive its logs. Then you rehire a new one.
You stand up a fresh agent with a clean job description, a new identity, an updated tool set, and current knowledge sources. There is no need to surgically edit a monolithic agent that has grown into a tangle of conditionals and overlapping tools. The rest of the system is unaffected because the interfaces (structured output schemas, handoff contracts, approval gates) stay the same. This keeps the architecture maintainable, avoids configuration drift, and lets you iterate or replace components without risking the whole SOC workflow.
Handoffs in the SOC Loop
Just as in a real SOC, each agent has a defined role and simply hands off its completed work to the next specialist in the loop.
A Triage Agent receives an alert, performs initial enrichment and disposition under its narrow tools and access, then passes a structured output (severity, entities, recommended next steps, confidence) to the Threat Hunter or Investigation Agent. That agent deepens the analysis with its own knowledge sources and tools, then hands a validated finding to the Detection Engineer Agent or a human reviewer. The Finding Validator checks evidence quality before anything is promoted. No single agent tries to own the entire incident lifecycle.
The handoff is explicit and machine-readable—via a shared schema, message queue, ticket update, or MCP tool—rather than relying on one agent to remember every subsequent step. This mirrors how analysts pass cases between tiers or functions today. Each agent stays focused, its context stays relevant, and the overall process remains auditable and interruptible by a human at any boundary. The SOC loop becomes a coordinated set of specialists instead of one overloaded generalist.
Putting It Together
When you separate these five dimensions you get agents that behave like well-managed digital employees:
Clear job (role)
Scoped permissions (access)
Limited toolkit (tools)
Relevant information only (knowledge)
Defined decision authority (capabilities)
The security benefits, the ability to cleanly replace underperforming agents, and the natural handoffs between specialists all flow from the same design choice. You can improve or retire one agent without breaking the others. You can revoke or retrain one without a full system redesign. And when something unexpected happens, the boundaries make the failure mode obvious instead of mysterious.
This is not about anthropomorphizing software. It is about applying the same operational discipline we already use for people and systems: define the job, grant only what the job requires, measure performance, and keep a human accountable. Agents are powerful precisely because they can act. Treating them with the same intentionality we apply to new hires is how we keep that power useful instead of uncontrolled.
The templates and demos from the MMS sessions illustrate these separations in concrete SOC workflows. If you are building agents, start by writing the job description first. Everything else—identity, tools, knowledge, approval gates, and handoffs—follows from that.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
Traditional secure coding advice still matters. Most of it was written for a world where humans wrote the code, reviewed the PRs, and decided which packages to install. That world is gone. In 2026, AI agents generate substantial portions of production code, install scripts run with full user privileges by default, and self-propagating worms have already demonstrated they can move through dependency graphs faster than most teams can patch. The old checklist is incomplete. Here is the updated one.
1. Pin everything
Floating versions are an invitation. Pin every dependency—language packages, container base images, toolchains, and AI model versions—to an exact digest or commit. Lockfiles are not enough if your CI or local agent can still resolve “latest.” If a package is not pinned, treat it as untrusted.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
2. Disable install scripts by default
Most package managers still run arbitrary code on install. Turn that off. Require explicit opt-in for post-install hooks, and only allow them after the package has been scanned and reviewed. An unvetted npm install or pip install should never be able to execute code on a developer workstation or in CI. This is no longer a convenience trade-off; it is a baseline control.
3. Use short-lived credentials everywhere
Long-lived tokens, API keys, and cloud credentials in environment variables or config files are how worms and agents escalate. Prefer short-lived, scoped credentials issued at runtime (OIDC, workload identity, temporary tokens). Assume any credential that lives longer than the task is already compromised.
4. Scan AI-generated PRs aggressively
Treat every AI-authored or AI-assisted change as higher risk than human-written code. Run static analysis, secret scanning, dependency review, and behavioral checks before merge. Require at least one human reviewer who understands the surrounding system. AI is excellent at producing plausible, vulnerable code that passes casual review. Do not let velocity arguments override this.
5. Inventory AI agent skills
Agents now have skills, tools, and plugins that can read files, call APIs, execute code, and modify repositories. Maintain an explicit inventory of every agent, its allowed tools, its data access, and its approval boundaries. Uninventoried skills are equivalent to unreviewed services running in your environment. Review them the same way you review privileged IAM roles.
6. Require provenance where available
Demand signed commits, signed packages, and build provenance (SLSA, in-toto, or equivalent) for anything that enters production. When provenance is missing, treat the artifact as untrusted and subject it to the same scrutiny as third-party code. “It came from our repo” is no longer sufficient when agents and automated workflows can commit on behalf of developers.
7. Assume any unvetted dependency can execute code on your machine
This is the new default threat model. A compromised or malicious package—whether traditional supply-chain malware or an AI-generated worm—can run with the privileges of the process that installed it. Isolate builds, use least-privilege CI runners, avoid installing unreviewed packages on developer laptops, and prefer hermetic or sandboxed environments. If you cannot prove a dependency is safe, assume it is hostile.
These practices are not theoretical. They are the minimum set that still works once agents can both write code and install the tools that run it. The teams that treat AI-generated code and agent skills as first-class attack surface will ship more safely than the teams that treat them as productivity features. Everything else is optional.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
FBI Attributes Record $6.43 Billion Binance Heist to North Korea’s TraderTraitor
The largest cryptocurrency theft on record has been officially pinned on North Korean actors. The FBI, working with the U.S. Secret Service and IRS Criminal Investigation, attributed the theft of more than $6 billion (reported in some coverage as $6.43 billion) in virtual assets from Binance to the North Korea-aligned group TraderTraitor (also tracked as Jade Sleet, Pressure Chollima, PUKCHONG, Slow Pisces, and UNC4899).
Assets were stolen across multiple blockchains, with the bulk on Ethereum and Bitcoin. Attackers have been converting proceeds primarily into ETH and are expected to launder further via DeFi and instant-swap services. The FBI released associated wallet addresses to help the industry block transactions. Roughly $2.85 billion has been frozen on-chain by issuers including Tether, Circle, Ripple, Arbitrum, and Optimism.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.
This single incident nearly doubles the cumulative crypto stolen by DPRK-linked actors in recent years, eclipsing the $1.46 billion Bybit theft from February 2025. TraderTraitor has a track record of crypto heists (DMM Bitcoin, Bybit, KelpDAO, Bitget) and continues refining social-engineering tradecraft, including recruitment lures, front companies, and AI-assisted persona and lure generation, plus trojanized developer tools such as Terraform providers that deliver cross-platform implants.
Binance paused withdrawals after the incident, conducted security assessments, and has been progressively restoring them while deposits remained open. The episode is a stark reminder of the scale, sophistication, and nation-state backing behind the highest-value crypto thefts, and of the continued need for strong key management, multi-party controls, real-time monitoring, and industry-wide freezing coordination.
Emergency Alert Apps in Ukraine and Russia Hijacked with Fake Nuclear Threats
Within hours of each other on November 1–2, official emergency alert apps in both Ukraine and Russia were compromised and used to push false, panic-inducing messages about nuclear and chemical threats.
Ukraine’s widely used Air Alert app (millions of users) sent messages warning of radiation threats in Kyiv, chemical danger, street fighting, and a nationwide “nuclear alert.” One message, written in Russian, read roughly: “Hi! There will be a nuclear alert across Ukraine. Don’t worry, the Oreshnik is coming!” Ukrainian authorities, including the Air Force, confirmed the app had been compromised by unauthorized interference, stated there was no radiation or nuclear threat, temporarily took the service offline, and later restored it. Sirens and other physical/SMS channels reportedly continued to function.
Hours later, Russia’s Emergency Situations Ministry app suffered a “massive cyberattack.” Users received fake notifications claiming nuclear warheads had been launched across all regions (in some reports linked to Ukrainian drones), with instructions to stock up on food and hide. The ministry confirmed hackers distributed false information but said the broader public alert system (SMS, broadcasts, sirens) was unaffected. A group called Hitcore has been mentioned in connection with claims of responsibility, though verification is limited.
These dual attacks occurred as a period of relative quiet in the war ended. They illustrate the high-impact potential of compromising civilian warning systems—eroding trust in genuine alerts, creating panic, and demonstrating that even critical population-protection infrastructure is in play in hybrid conflict. Defenders of such systems face classic challenges: exposed interfaces, credential or supply-chain weaknesses, and the difficulty of rapid, trustworthy communication when the primary channel itself is the vector.
Cyberattacks Turn Supermarket Freezers into Ovens Across Europe
A fresh wave of attacks on supermarket refrigeration systems has hit stores in Sweden, Belgium, Luxembourg, and Ireland, following a similar large-scale incident in France in mid-October. Temperatures in freezers and chillers were remotely driven from deep-freeze levels to as high as 50 °C (122 °F) or higher, spoiling large quantities of food and forcing stores to discard inventory worth significant sums.
Affected chains include ICA and Coop in Sweden (multiple stores, some reporting temperatures set to 50 °C), Delhaize (~40 stores), Carrefour, Spar, and others in Belgium and Luxembourg, plus SuperValu locations in Ireland. One Swedish store publicly stated its refrigerators and freezers had been “hacked overnight.” Sweden’s national cybersecurity centre is investigating, and refrigeration vendors have described the incidents as cyberattacks that switched units into defrost mode or otherwise overrode controls.
This is operational-technology (OT) / industrial-control-system (ICS) targeting with direct physical and economic effects. Many such systems remain internet-exposed or poorly segmented, running outdated software with weak authentication. The pattern—remote temperature manipulation that destroys perishable goods—shows how cyber operations can create real-world disruption and loss without traditional data theft or encryption. Retailers and critical-infrastructure operators need stronger OT visibility, network segmentation, patching discipline, and incident response that treats refrigeration controllers as high-value targets.
AI Moves from Helper to Active Criminal Tool—VOLTA Infostealer Ranks Victims with Claude, Gemini, and Kimi
Cisco Talos has detailed VOLTA-AUTODOXER (VOLTA), a self-deleting Windows infostealer that harvests the usual broad set of credentials, cookies, wallet seeds, sessions (Discord, Telegram, Steam, Roblox, etc.), OAuth tokens, SSH/cloud keys, and more—then optionally feeds a compiled victim dossier to commercial large language models via OpenRouter to rank what the haul is worth and assess the target’s operational security.
The default model is Anthropic’s Claude Opus 4.6; if the response contains refusal language, it fails over to Moonshot AI’s Kimi K2 and then Google’s Gemini 2.5 Flash. A detailed system prompt casts the model as a “forensic intelligence analyst” and requests ranked monetization tiers plus OPSEC evaluation. The AI step is optional (it still steals without an API key), and analysis occurs from the victim’s own machine.
This is part of a broader pattern visible in the last day: AI agents assisting ransomware operators with lateral movement and domain admin access, social-engineering campaigns that impersonate IT support on Microsoft Teams and then abuse Active Directory Certificate Services, malware that impersonates popular AI chatbots to phish credentials and API keys, and nation-state actors (including North Korean groups) using AI for lure generation and persona work. Criminal tooling is systematically working around model refusals and integrating LLMs into the post-exploitation workflow to prioritize high-value targets faster than human operators can.
Defenders should treat unexpected LLM API calls from endpoints, headless browser activity associated with some of these stealers, and the usual stealer indicators with high priority, while organizations must assume that AI-assisted prioritization shortens the window between theft and monetization.
These four stories—nation-state crypto theft at historic scale, hybrid-war attacks on civilian alert systems, OT disruption of everyday retail infrastructure, and the rapid weaponization of commercial AI models—capture the breadth of the threat landscape right now.
Rod’s Blog is a reader-supported publication. To receive new posts and support my work, consider becoming a free or paid subscriber.

 Login