❌

Reading view

There are new articles available, click to refresh the page.

Email threat landscape: Q3 2026 trends and insights

Microsoft Threat Intelligence detected approximately 7.3 billion email-based phishing threats from July through September, including a sharp increase to nearly 3 billion in September alone, up 41% from August. Yet the increase did not extend across the techniques that had driven threat actor activity earlier in the year. QR code phishing remained far below its early-year peak, while CAPTCHA-gated phishing reversed several months of decline, driven in part by renewed use of SVG attachments.

Line graph showing the number of phishing emails sent over several months, showing a steady decline in Q3 until a sharp increase in September.
Figure 1. Monthly detected email threat volume (January – September 2026)

The quarter also highlighted how sender identity and security exceptions can shape the outcome of detected threats. Microsoft detected approximately 129 million malicious messages spoofing the sender domains of tracked business services. Many were delivered because organization- or user-configured exceptions overrode security protections, even after the messages failed authentication checks and were identified as malicious, showing how overly broad exceptions intended to preserve legitimate workflows can also expose them to impersonation. In Microsoft Teams, attackers increasingly used ordinary personal names rather than explicit help desk identities while continuing to use live interactions for social engineering. Across malicious attachment activity more broadly, credential theft remained the dominant objective in Q3.

Two campaigns observed during the quarter illustrate the range of activity behind these trends. An August campaign targeting legal organizations used personalized salary review documents and QR codes to lead recipients into device code phishing, despite the broader decline in QR code attacks. In September, purchase order and payroll lures used disguised archives to deliver Agent Tesla, malware commonly used to collect credentials and other information. Together, the campaigns show how familiar business requests remained effective lures across distinct attack paths.

The effects of the March disruption of the Tycoon2FA phishing-as-a-service (PhaaS) platform also remained evident. By July, Microsoft detected approximately 21,000 phishing messages linked to the platform, down 99.8% from 8.9 million in February, the last full month before the operation.
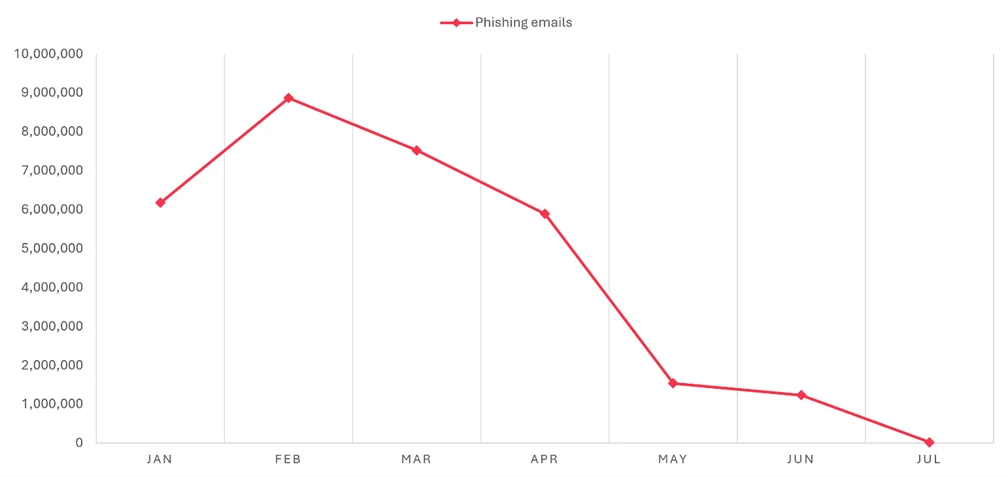
A decreasing number of phishing emails from January to July, starting at 10 million and dropping to nearly zero.
Figure 2. Tycoon2FA-linked phishing email volume (January 2026 – July 2026)

This blog provides a view of email threat activity across Q3 2026, examining shifts in phishing techniques, malicious payloads, business contact impersonation (BCI), and Teams-based threats. We also highlight spoofed business-service sender domains and two campaigns that show how attackers used familiar work requests to make malicious messages appear credible. Together with recommendations, Microsoft Defender detections, and hunting queries, these findings can help defenders assess where existing protections may be weakened and investigate activity across email and collaboration platforms.

Spoofed sender domains

Requests to sign a document, review an invoice, or respond to a survey are routine business communications. Attackers exploit that familiarity by spoofing the sender domains of the legitimate services that deliver them. Rather than relying only on a misleading display name or a lookalike domain, these messages claim the service’s actual domain as their sender identity.

Microsoft detected approximately 129 million malicious messages spoofing the business-service domains tracked in this analysis during Q3. Activity had remained consistently high since at least May, at roughly 41 million to 46 million messages a month. DocuSign was the most frequently spoofed brand in September, accounting for 29% of that month’s total. Adobe, SurveyMonkey, and Barracuda also saw increases toward the end of the quarter, even as overall spoofing volume remained broadly steady.

A downward trend in phishing emails from 46 million in June to closer to 42 million in September.
Figure 3. Malicious messages spoofing tracked business-service sender domains (May – September 2026)

The more consequential finding was how security exceptions affected these messages after detection. Despite failing email authentication checks and being identified as malicious, many were associated with tenant- or user-level overrides. In September, overrides applied to 63% of messages with a recorded security outcome, with tenant-level overrides accounting for most of them.

The figures do not establish that recipients opened the messages or that accounts were compromised. They do show why exception policies deserve attention alongside detection coverage. An organization may create an exception to avoid interrupting a legitimate business workflow, but an overly broad exception can also weaken protection against messages impersonating that workflow. Familiar branding is not a substitute for an authenticated sender.

QR code phishing attacks

QR code phishing ended Q3 far below the levels seen during its early-year surge. Microsoft detected approximately 12.1 million attacks over the quarter, down 67% from Q2. The decline continued through September despite the broader increase in email threats, leaving monthly QR code volume 86% below its March peak.

A downward trend in phishing email occurrences, with counts decreasing from 19 million in March to less than 4 million by September.
Figure 4. Monthly QR code phishing volume (January – September 2026)

Much of the volume reduction came from the attachments that had supported that earlier growth:

  • PDF attachments remained the most common delivery format in Q3, accounting for 78% of QR code attacks in July and August before dropping to 61% in September. Nonetheless, the volume of PDFs carrying malicious QR codes fell by roughly 65% by the end of the quarter.
  • DOC/DOCX attachments accounted for 14% of QR code attacks in July and August before rising to 20% in September. Word document delivery volume similarly contracted in Q3, falling 39% between July and September following a sharp drop at the start of the quarter.
  • Email-embedded QR codes increased from 5% of attacks in July to 12% in September. After dropping to near-zero in Q2, the volume of malicious QR codes embedded in email bodies more than tripled by the end of Q3, although the method remained a smaller delivery category than attachments.
A line graph showing the   percentage of documents processed through various methods, with PDFs remaining the top method throughout Q3 followed by DOC attachments, email-embedded URLs, and other delivery methods.
Figure 5. QR code phishing delivery method share by month (January – September 2026)

The distinction between delivery methods matters for inspection coverage, but not for the recipient’s experience: either attachment or embedded formats can move a user from a message on a managed device to a phishing page on a personal phone. The reduction in volume has not changed that underlying challenge.

CAPTCHA-gated phishing tactics

CAPTCHA-gated phishing began to recover while QR code attacks continued to fall. By September, Microsoft detected 3.1 million CAPTCHA-gated attacks, nearly twice the volume seen at July’s low. Activity remained well below its March peak, but the recovery ended several months of sustained decline.

A declining trend in phishing emails, depicting over 12 million in March, dropping to 2 million in July, and closer to 4 million by September.
Figure 6. CAPTCHA-gated phishing volume (January – September 2026)

The increase in CAPTCHA-gated phishing attacks was not confined to a single attachment format as delivery methods shifted throughout Q3, though SVG attachments were central to the initial recovery.

  • SVG attachment volume increased sixfold in August, accounting for almost half of September’s total CAPTCHA-gated phishing attacks. Up from 17% of attacks in July, SVGs represented 65% of CAPTCHA-gated phishing attacks in August, remained elevated at 49% in September, and were the leading delivery method at the quarter end.
  • Email-embedded URLs accounted for 49% of attacks in July before falling to 19% in August as SVG activity surged. URL-delivered attacks more than doubled in September, reclaiming 30% of attacks.
  • PDF attachments declined from 22% of attacks in July to 12% in August, remaining at 12% in September.
  • HTML attachments declined from 9% of attacks in July to 2% in August, then more than tripled in volume in September to account for 6% of attacks.
  • DOC/DOCX attachments remained comparatively uncommon throughout Q3, representing only 1% of attacks each month.
A bar chart illustrating the percentage distribution of different document formats, with SVG attachments on top for Q3, generally followed by URL, PDF, HTML, and DOC or Other distribution methods by the end of the quarter.
Figure 7. CAPTCHA-gated phishing distribution method share by month (April – September 2026)

Malicious payloads

The dominant risk from malicious attachments continued to be credential theft, not malware installation. Approximately 94-96% of payload-based attacks during Q3 directed recipients toward a phishing site or presented a fraudulent sign-in page locally. An attachment did not need to install software to put an account at risk.

HTML and PDF attachments remained the two most common malicious payload types during Q3, together accounting for approximately 56–62% of payload-based attacks each month, while the more significant change was the return of SVG files:

A pie chart representing the distribution of various file types: 29% HTML and PDF, 4% DOCX, 16% SVG, 4% ZIP/GZIP, 3% RAR, 15% other
Figure 8. Malicious payloads by type
  • HTML attachments accounted for nearly two-thirds of malicious payloads and remained relatively steady across the quarter. HTML files ranked first in July at 32% of attacks before declining to 26% in August and recovering to 29% in September.
  • PDF attachments accounted for 27–30% of attacks and were the leading payload type in August and September. Volume remained comparatively stable, declining only 2% between July and September.
  • SVG attachments increased from 13% of attacks in July to 20% in August, when volume reached 10.1 million—the highest monthly volume in more than a year. Volume then fell 34% in September, although SVGs still represented 13% of attacks and remained roughly 50% higher than the monthly average for the first half of 2026.
  • DOC/DOCX attachments declined from approximately 5% of attacks in July and August to less than 3% in September, falling 76% below its monthly average volume for the first half of 2026.
  • ZIP/GZIP attachments declined from 5% of attacks in July to 3% in August before recovering slightly to 4% in September. Raw volume remained 24% below July.

The reduced use of Word documents alongside the renewed use of SVG files left a different mix of attachment threats, though credential theft remained the dominant objective.
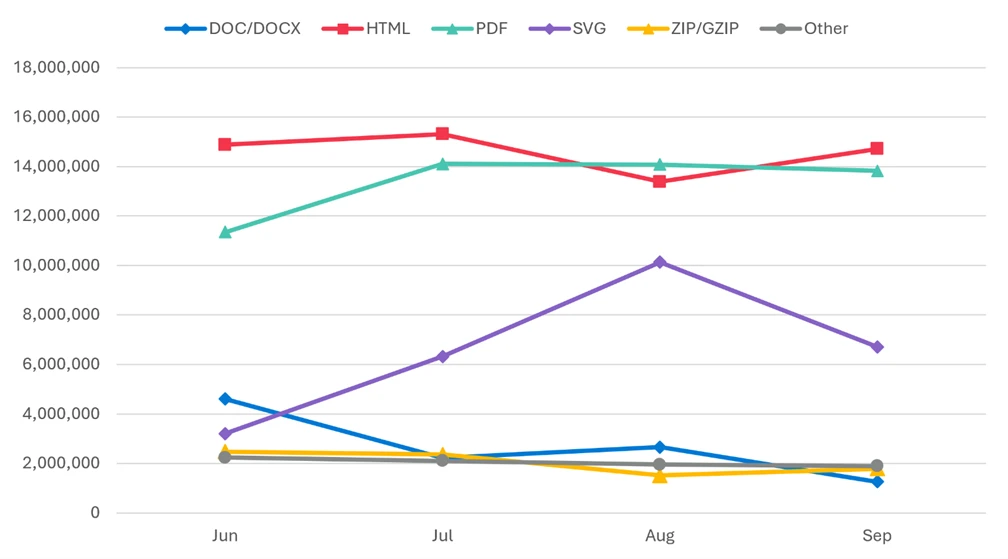
A line graph depicting a trend in the number of file types, with HTML on top followed closely by PDFs, then SVG files, and DOC, ZIP, and other files all hovering around 2 million by the end of the quarter.
Figure 9. Malicious payload file type distribution by month (June – September 2026)

CAPTCHA-gated phishing accounted for only part of the malicious SVG activity. The resurgence was therefore broader than the use of SVG files to deliver that particular technique.

Business contact impersonation

Microsoft defines business contact impersonation (BCI) as a text-based attack targeting enterprise users that impersonates a trusted entity for the purpose of persuading a recipient into initiating a fraudulent financial transaction or sending the attacker sensitive documents.

BCI volume declined throughout Q3, totaling approximately 6.2 million attacks. That was substantially below Q2, although the comparison is influenced by the unusually large spike in April. By September, monthly activity had fallen to its lowest level since at least July 2025.

A downward trend that peaked at 9 million attacks in April before dropping sharply down to between 2-3 million for all of the third quarter.
Figure 10. Monthly BCI attack volume (January – September 2026)

The reduction in overall volume also concealed differences among financial lures. Generic messages continued to dominate initial BCI contact during Q3, but explicit task and financial requests gained share as overall attack volume declined:

  • Generic outreach messages, such as “Are you at your desk?”, accounted for 82% of attacks in July and August before declining to 79% in September. Raw volume fell 14% across the quarter, reinforcing that operators still overwhelmingly favored establishing contact before introducing a fraudulent request.
  • Generic task requests represented 8–10% of attacks during Q3, increasing from 9% in July to 10% in September despite a 9% decline in raw volume.

Within the smaller subset of explicit financial requests:

  • Payroll update requests were the most common financial lure, accounting for 6% of attacks in July and August and 7% in September. Raw volume remained broadly stable at approximately 126,000–130,000 attacks per month.
  • Invoice payment requests recovered from June’s low. Volume increased 34% in July, 25% in August, and 89% in September, more than tripling between June and September. Their share reached 3% in September, its highest level since March.
  • Gift card requests remained at 2% of attacks each month, while raw volume declined 9% from July to September.
Pie chart depicting BEI lures; 81% generic outreach contacts, 9% generic task requests, 2% payroll updates, 2% gift card requests, 6% invoice payments, and less than 1% for other types.
Figure 11. Initial BCI email content by type (Q3 2026)

The decline in BCI overall did not extend equally to the requests reaching payment and payroll staff.

Microsoft Teams threats

Microsoft observed approximately 141,000 malicious Teams call attempts during Q3. Activity peaked in July before declining 31% by September, although September volume remained 38% above the monthly average for the first half of 2026. Teams-based attacks continued to use live interactions across chat, voice, screen sharing, and remote-support tools to facilitate remote access, credential theft, and hands-on-keyboard compromise.

A trend line of call attempts, displaying a peak of over 50,000 attempts in July to about 35,000 by September.
Figure 12. Monthly observed malicious Microsoft Teams calls (January – September 2026)

Attackers increasingly moved away from display names that explicitly announced an IT- or tech-related support role. Ordinary personal-name display names rose from 46% of the observed July sample to 88% in September, while explicit help desk identities fell from 17% to 2%.

Bar chart comparing call impersonation types in Q3, with username impersonations rising from 46% in July to 88% by September, IT support impersonations ultimately decreasing from 17% to 10% after a spike in August, Help desk impersonations dropped from 17% to 2%, and Other impersonations dropped from 20% to virtually 0 by September.
Figure 13. Malicious Teams call impersonation comparison (Q3 2026)

This shift does not necessarily mean attackers abandoned IT support stories. A personal name can accompany a claim to work for the help desk, while the underlying account address retains technical or service-related wording. More targeted attempts also used domains resembling the intended victim organization’s domain, emphasizing that the visible name is only one part of the impersonation.

Voice phishing attempts peaked in July and then receded, but September volume remained above the levels observed early in 2026. Calls were concentrated during recipients’ weekday working hours, when a live response was more likely. These attempts included unanswered, rejected, and short-lived calls, partly reflecting Microsoft’s expanding visibility and ongoing efforts to strengthen protective measures against social engineering abuse. Attemps should not be interpreted as successful attacker interactions.

Notable phishing campaigns

The following campaigns were observed during the quarter and highlight notable credential phishing, BCI, and malware delivery activity. For analysis of a separate Teams-based IT-support impersonation campaign observed in August, see Impersonating IT support: Threat actors turn remote session into enterprise-wide access.

Salary review lure delivers personalized QR code attachment for device code credential capture targeting legal organizations

On August 19, 2026, Microsoft Defender Research observed a phishing campaign targeting more than 10,000 users across more than 4,800 organizations, almost exclusively located in the United States. While most phishing attacks typically don’t focus on a single vertical, this campaign targeted the professional services sector, specifically law firms and legal organizations. Messages in this campaign were sent out over a 13-hour period between 13:27 UTC on August 19, 2026, and 2:59 UTC on August 20, 2026.

Pie chart depicting 72.1% of campaign targets were professional services, 22.5% were technology and software, and 5.4% were other.
Figure 14. Intended campaign targets by industry

Emails in this campaign were sent with the subject line “Salary Review” from smtp[@]wekash[.]net via Amazon Simple Email Service. The email body carried no visible text and the sole payload was a Word document attachment named Your-Q3-Compensation-Summary.docx.

A notification regarding a revised compensation package for an employee, emphasizing the employee's exceptional performance and requesting confidentiality.
Figure 15. Sample of the campaign document attachment

The Word document impersonated the recipient’s own organization, displaying company branding and addressing the recipient by name. The message claimed that the recipient’s compensation had been revised following a Q2 performance review and that updated details were ready for review. A QR code in the document carried an instruction to scan it to access the revised details. This approach moved the phishing URL out of the email body and into an image, bypassing email gateway controls that scan text-based links but do not decode QR code images.

Scanning the QR code would have directed users to an attacker-controlled phishing page impersonating a Microsoft OneDrive sign-in portal hosted on the domain splace[.]co[.]za. The page presented an alphanumeric code and instructed recipients to copy it and proceed to the Microsoft sign-in portal.
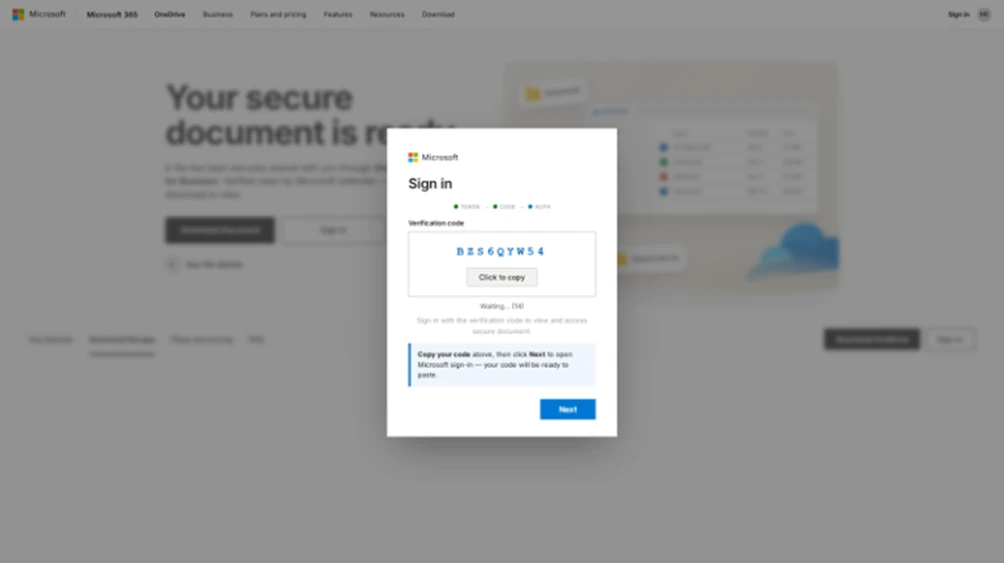
Screenshot of a phishing landing page depicting a sign in pop up asking the user to copy the code and then click Next
Figure 16. Sample phishing landing page

The phishing page used a device code phishing technique, which works by making an authentication request to Microsoft’s device authentication service before the recipient arrived, receiving a user code in return, and embedding that code into the page. When a recipient copied the code and proceeded, the page redirected them to the legitimate Microsoft device authentication portal at microsoft.com/devicelogin, where they entered the code and signed in. Completing that sign in would have transferred a valid session token to the attacker. The token granted persistent access to the recipient’s Microsoft 365 account without ever exposing the password and without re-triggering multifactor authentication (MFA). A countdown timer on the page signaled that each code had a limited validity window, pressing recipients to act quickly.

Spanish-language purchase order and payroll campaign leads to Agent Tesla malware

On September 21, 2026, Microsoft Defender Research observed a phishing campaign targeting more than 56,000 users across more than 8,100 organizations. The campaign primarily targeted users in Spanish-speaking countries, with Colombia accounting for the largest share of intended recipients (15%), followed by the United States (12%), Mexico (12%), Chile (11%), and Spain (8%). Like most large-scale phishing attacks, this campaign did not focus on a single vertical, but instead targeted a broad range of industries, most notably retail and consumer goods (27%), manufacturing and agriculture (19%), and financial services (13%). Messages in this campaign were sent out over an almost nine-hour period between 14:57 UTC and 23:35 UTC on September 21, 2026.
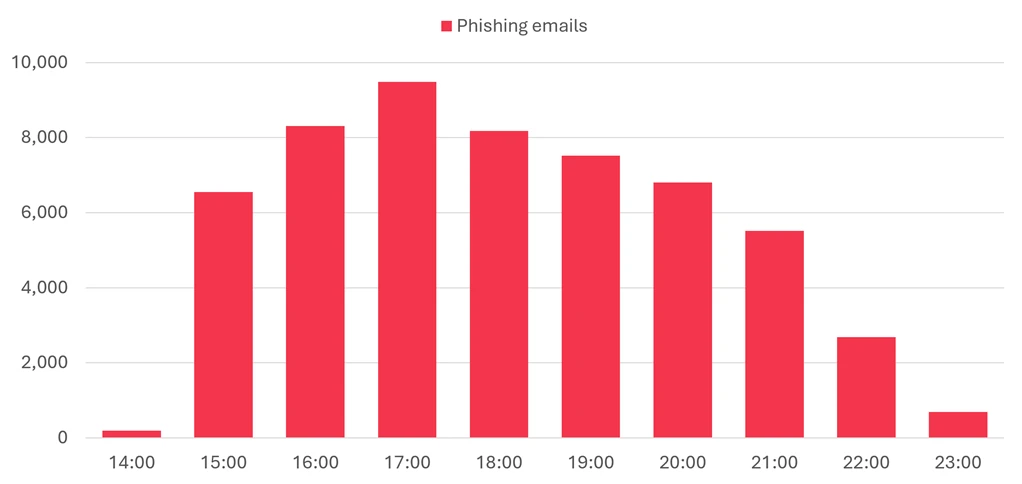
Figure 17. Timeline of campaign message volume

Two lure variations were observed throughout the duration of the campaign: a purchase order theme, which was used in 63% of messages, and a payroll theme, which was used in the remaining 37%. Both variations were sent from the address contacto06[@]carloxmextos[.]org. Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and Domain-based Message Authentication, Reporting, and Conformance (DMARC) all passed for that domain, so the messages did not depend on simple address forgery. The actor changed the display name to resemble a sales or human resources identity associated with the recipient’s organization. That combination gave the messages technically valid authentication while using the visible sender identity and familiar business context to support the impersonation.

The purchase order lure variation used the reply-style subject “Re: solicitud de cotización”. Its body said, “Buen Dia”, claimed that a purchase order was attached, and asked the recipient to confirm receipt before closing with the lowercase “saludos”. The abrupt wording, inconsistent capitalization, and copied professional signature made the message look like a short continuation of an existing commercial exchange while avoiding details that a recipient could easily challenge.

The attached file, Nuevo orden de compra – 21092026.pdf.uu, was a RAR archive despite its uncommon .uu ending and PDF-like name. Inside it was Nuevo orden de compra – 21092026.pdf.js, a JavaScript downloader whose second extension exposed the executable script type only after extraction. If run, the script fetched a file named Lincoln.ps1 from a campaign-controlled object in Firebase Storage, and that PowerShell payload led to Agent Tesla malware. The nested archive and misleading extensions separated the visible business document theme from the code that executed, while the cloud-hosted download gave the actor a remotely accessible staging point.

Screenshot of a Spanish-language email with the subject “Re: solicitud de cotización.” The sender is shown as a sales-themed display name with the address contacto06@carloxmextos.org; the recipient and signature are redacted. The message says an order is attached and asks the recipient to confirm receipt. The attachment is labeled “Nuevo orden de compra - 21092026.pdf.uu.”
Figure 18. Redacted rendering of the purchase order lure email

The payroll-themed lure used the subject “Nomina 21.09.2026”. It addressed the recipient by name, said the September 21 payroll list was attached, and signed off as a human resources manager. The date-specific payroll pretext created an immediate work-related reason to open the file, while the personalized greeting made a bulk message appear locally relevant.

The payroll lure’s attachment, Nomina 21.09.2026.xml.001, was also a RAR archive. Extraction produced Nomina 21.09.2026.xml.exe, an Agent Tesla executable disguised with an XML-themed double extension. Unlike the purchase order delivery chain, this branch did not require a separate downloader in the supplied evidence, but both paths used the same sender infrastructure, attachment camouflage, date, and malware family. Agent Tesla is commonly used to collect credentials and other information from an infected host, so the shared final payload suggested that credential and information theft were the campaign’s likely objective.

Screenshot of a Spanish-language email from an HR-themed display name at contacto06@carloxmextos.org to a redacted recipient. The subject is “Nomina 21.09.2026.” The message says a payroll document for September 21, 2026, is attached and is signed “Gerente de Recursos Humanos.” The attachment is labeled “Nomina 21.09.2026.xml.001.”
Figure 19. Redacted rendering of the payroll lure email

Defending against email and collaboration threats

Microsoft recommends the following mitigations to reduce the impact of this threat. Check the recommendations card for the deployment status of monitored mitigations.

  • Microsoft helps organizations reduce the risk of phishing and social engineering in Teams through user awareness and layered, built-in protections. Users should exercise caution with external connection requests and messages, including verifying a sender’s identity and requests before acting on them. Administrators can also block external Teams users and specify which users in their organization are permitted to chat or meet with people outside the enterprise. These flexible controls help organizations manage risk for employees in sensitive roles and departments. Teams will also be introducing AI-powered phishing detection that uses conversation context to identify phishing and social engineering in higher-risk messaging scenarios, particularly first-contact chats with external users. Together, these measures help organizations collaborate more securely in Teams.
  • Review the recommended settings for Exchange Online Protection and Microsoft Defender for Office 365 to ensure your organization has established essential defenses and knows how to monitor and respond to threat activity.
  • Invest in user awareness training and phishing simulations. Attack simulation training in Microsoft Defender for Office 365, which also includes simulating phishing messages in Microsoft Teams, is one approach to running realistic attack scenarios in your organization.
  • Enable Zero-hour auto purge (ZAP) in Defender for Office 365 to quarantine sent mail in response to newly acquired threat intelligence and retroactively neutralize malicious phishing, spam, or malware messages that have already been delivered to mailboxes.
  • Responders can also manually check for and purge unwanted emails containing URLs and/or Subject fields that are similar, but not identical, to those of known bad messages. Investigate malicious email that was delivered in Microsoft 365 and use Threat Explorer to find and delete phishing emails.
  • Turn on Safe Links and Safe Attachments in Microsoft Defender for Office 365.
  • Enable network protection in Microsoft Defender for Endpoint.
  • Encourage users to use Microsoft Edge and other web browsers that support Microsoft Defender SmartScreen, which identifies and blocks malicious websites, including phishing sites, scam sites, and sites that host malware.
  • Enable passwordless authentication methods (for example, Windows Hello, FIDO keys, or Microsoft Authenticator) for accounts that support passwordless. For accounts that still require passwords, use authenticator apps like Microsoft Authenticator for MFA. Refer to this article for the different authentication methods and features.
  • Configure automatic attack disruption in Microsoft Defender XDR. Automatic attack disruption is designed to contain attacks in progress, limit the impact on an organization’s assets, and provide more time for security teams to remediate the attack fully.

Microsoft Defender detections

Microsoft Defender customers can refer to the list of applicable detections below. Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, email, and apps to provide integrated protection against attacks like the threat discussed in this blog.

Microsoft Defender for Endpoint

The following alert might indicate threat activity associated with this threat. The alert, however, can be triggered by unrelated threat activity.

  • Suspicious activity likely indicative of a connection to an adversary-in-the-middle (AiTM) phishing site

Microsoft Defender for Office 365

The following alerts might indicate threat activity associated with this threat. These alerts, however, can be triggered by unrelated threat activity.

  • A potentially malicious URL click was detected
  • A user clicked through to a potentially malicious URL
  • Suspicious email sending patterns detected
  • Email messages containing malicious URL removed after delivery
  • Email messages removed after delivery
  • Email reported by user as malware or phish

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the activity and techniques discussed in this blog. These reports provide intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this threat actor.

Hunting queries

Microsoft Defender XDR

Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks:

Salary review campaign emails by sender address

The following query identifies emails associated with the August 19 campaign using a message’s sending email address.

EmailEvents
| where SenderMailFromAddress == “smtp@wekash.net”

Spanish-language purchase order and payroll campaign emails by sender address

The following query identifies emails associated with the September 21 campaign using a message’s sending email address.

EmailEvents 
| where SenderMailFromAddress == "contacto06@carloxmextos.org"

Indicators of compromise (IOCs)

IndicatorTypeDescriptionFirst seenLast seen
wekash[.]net Domain Sender domain used to distribute campaign emails via Amazon SES 2026-08-19 2026-08-20
smtp@wekash[.]net Email address Sender email address observed in campaign messages 2026-08-19 2026-08-20
Your-Q3-Compensation-Summary.docx File name Word document attachment carrying the compensation lure and QR code 2026-08-19 2026-08-20
splace[.]co[.]za Domain Domain hosting phishing content 2026-08-19 2026-08-20
https://splace[.]co[.]za/0987643345678908765421234567890987654320987654321223456787654/onedrive/ URL URL hosting phishing content 2026-08-19 2026-08-20
carloxmextos[.]org Domain Authenticated domain used to send both campaign variations 2026-09-21 2026-09-21
contacto06@carloxmextos[.]org Email address Sender address used for both observed lure variations 2026-09-21 2026-09-21
Nuevo orden de compra – 21092026.pdf.uu File name RAR attachment used in the purchase order variation 2026-09-21 2026-09-21
Nuevo orden de compra – 21092026.pdf.js File name JavaScript downloader contained in the purchase order archive 2026-09-21 2026-09-21
Lincoln.ps1 File name PowerShell payload downloaded by the purchase order branch 2026-09-21 2026-09-21
Nomina 21.09.2026.xml.001 File name RAR attachment used in the payroll variation 2026-09-21 2026-09-21
Nomina 21.09.2026.xml.exe File name Agent Tesla executable contained in the payroll archive 2026-09-21 2026-09-21
BEDD2297739632DA8EE470367295FE976E55BE74D628DCAEE7FA98121EE530F1 SHA-256 SHA-256 of the purchase order RAR attachment 2026-09-21 2026-09-21
CE832350C165522DB03DB040CA07917976D1A91F97E7016EA36DCC6B53E0EB13 SHA-256 SHA-256 of the JavaScript downloader 2026-09-21 2026-09-21
F8B49891D15A578E4DE28FECF99D0D78DB6B2C3DA81CD51C931B8D128E60C187 SHA-256 SHA-256 of the PowerShell payload associated with Agent Tesla delivery 2026-09-21 2026-09-21
C438B9A3BB67E2C10EFF0D01513422DC17DCE7C5508303A680E46F3DCEC886EF SHA-256 SHA-256 of the payroll RAR attachment 2026-09-21 2026-09-21
72966B30BBD87E42C683D2AC7A42BB62021FC14389D508551432FFD70D62F33A SHA-256 SHA-256 of the Agent Tesla executable from the payroll variation 2026-09-21 2026-09-21

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

The post Email threat landscape: Q3 2026 trends and insights appeared first on Microsoft Security Blog.

Fake-download campaign uses trojanized installers to deliver monetization payloads

Microsoft Threat Intelligence has identified an evolving fake-download campaign targeting users searching for cracked commercial software, free games, activators, plugins, and unofficial utilities. The campaign uses trojanized Inno Setup-style installers to distribute multiple monetized software payloads, referred to by the delivery system as “offers”, during a single installation session.

Our investigation found that the installers use a per-offer callback and status-tracking model to manage delivery and record installation outcomes. We confirmed three downstream monetization branches that transformed affected devices into monetized assets, including by routing third-party internet traffic through the device, enrolling it in a distributed-computing platform, or installing additional utility-style software, often without users’ informed knowledge or consent. These products and components may have legitimate uses, but their silent installation through deceptive software bundles without informed user consent introduces security and privacy risks.

Organizations can reduce their exposure to this activity by preventing the use of untrusted software sources, enabling potentially unwanted application protection, and monitoring for unexpected software installations and persistence mechanisms.

This blog details the campaign’s execution model and confirmed outcomes and provides mitigation guidance, Microsoft Defender protection information, advanced hunting queries, MITRE ATT&CK mappings, and indicators of compromise to help defenders identify, investigate, and respond to related activity.

Attack chain overview

The fake-download campaign follows a four-stage attack chain that progresses from deceptive lures through Inno-based staging, offer-controlled payload delivery, and installation of one or more monetization branches:

  1. Initial access via fake download lures – Users run fake installers promoted as cracked commercial software, free games, activators, plugins, executors, or unofficial utilities.
  1. Inno wrapper execution and temporary runner staging – The installer launches an Inno Setup-style temporary runner under %TEMP%\is-*.tmp\, which starts recurring eld*.exe, set_*.exe, or other numbered stages.
  1. Offer execution callback and payload delivery – The runner contacts rotating infrastructure using a repeatable d=inno and r=offer_execution callback pattern. Offer, affiliate, download-network, placement, and session values coordinate downstream payload selection and correlate activity within the installer session.
  1. Final payload installation and monetization – Staged payloads use unattended installation switches to install one or more confirmed campaign branches: WorldProxyPool for proxy and network-resource monetization; CharityEngine and Berkeley Open Infrastructure for Network Computing (BOINC) for compute-resource monetization; or Advanced Windows (AW) Manager and Windows Manager for adware-style utility monetization. WorldProxyPool also creates recurring SYSTEM scheduled tasks for agent startup, watchdog execution, and updater activity.

Attack Chain

Figure 1. Overview of the attack chain.

Initial access via fake download lures

The campaign begins when users download and run fake installers promoted as cracked software, game installers, executors, activators, plugins, utilities, or driver and mobile-unlock tools. Observed lures include cracked audio plugins, PC games, Roblox executors, auto-clickers, driver tools, and fake utility installers.

Example lures: Echo Client; FabFilter Total Bundle; Navicat Premium crack; Cue Club; auto-clicker; Deadpool Apunka Games; Command & Conquer: Red Alert 2; TFT Unlock Tool; and clownfishvoicechanger.

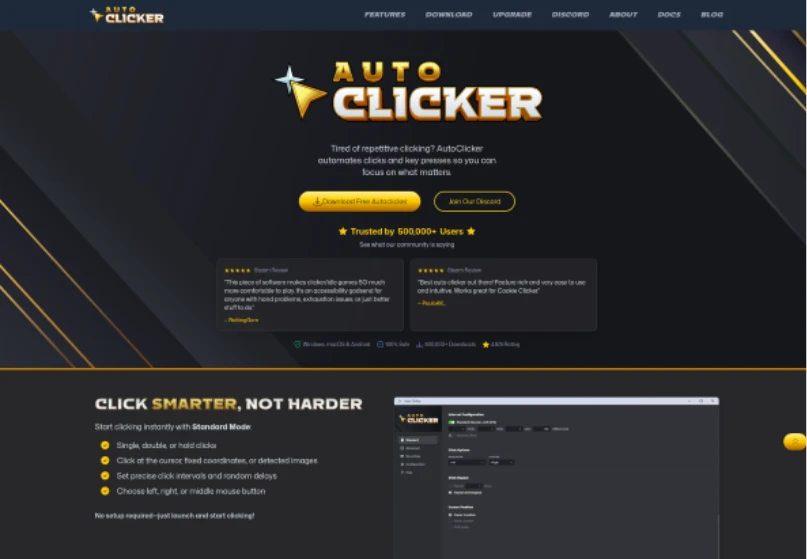
Dark-themed Auto Clicker promotional webpage with product screenshots, feature descriptions, and repeated gold download buttons, illustrating the polished software-download pages used as campaign lures.
Figure 2. Example utility download lure.

Inno wrapper execution and temporary runner staging

Across the investigated activity, user-launched lures spawned Inno Setup-style temporary runners under %TEMP%\is-*.tmp\ and then launched one or more numbered eld*.exe stages. Arguments such as /SL5, /SPAWNWND, and /FIRSTWND, together with the temporary path and numbered stage names, provide more durable indicators than the original lure filename.

The depth of the execution chain and its downstream outcome varied by installer session. One Echo Client example progressed through multiple numbered stages and reached several monetization branches, while other observed lures exposed fewer numbered stages or downstream components.

The table below uses the Echo Client activity as a representative example of the wrapper-to-stage sequence; individual installer sessions may launch different combinations of numbered stages.

Step Process Command-line / path signal Role
1 Echo Client.exe Launched from %USERPROFILE%\Downloads\Echo Client\ User-launched lure
2 Echo Client.tmp %TEMP%\is-*.tmp\… with /SL5=… Inno temporary runner
3 Echo Client.exe /SPAWNWND=… /FIRSTWND=… Inno child process / window handoff
4 Echo Client.tmp /SL5=… /SPAWNWND=… /FIRSTWND=… Temporary runner continues execution
5 eld*.exe eld0.exe, eld1.exe, eld3.exe, eld4.exe, and eld5.exe under %TEMP%\is-*.tmp\ Numbered staged payloads

Table 1. Inno wrapper execution and temporary runner staging.

Offer execution callback and payload delivery

After staging, the Inno temporary runner contacted rotating callback infrastructure using randomized URL paths but a repeatable query-string structure:

http:///?sis=&fz=&d=inno&r=offer_execution&ko=no&o=&a=&dn=&spot=&t=&cr= 

Failed or blocked offers used r=offer_execution_fail and sometimes included local error text, including messages that the operation did not complete because the file contained a virus or potentially unwanted software. These callbacks are useful campaign-attribution and sequencing markers, but they are not always the earliest prevention point. In some endpoint detection and response (EDR) traces, child payloads launched before or around the r=offer_execution callback.

The campaign used offer IDs, affiliate IDs, download-network IDs, and placement values to select or report downstream payload attempts. Observed offer and download-network combinations included o=1712 / dn=507, o=1720 / dn=536, o=1727 / dn=564, o=1729 / dn=566, o=331 / dn=244, o=1674 / dn=440, o=1675 / dn=441, o=1681 / dn=447, and o=1730 / dn=567. Different offers could succeed or fail independently within the same installer session, so a failed first offer did not necessarily mean that the full bundle stopped.

Parameter Observed use Assessment
d Often set to inno Installer or delivery-family marker
sis Stable within an installer session Session-correlation value
a Stable across related requests Affiliate, campaign, or distribution-partner identifier
o Changes by offer Offer identifier
dn / on Changes with the offer or retrieval path Download-network or offer-network field; exact meaning unconfirmed
spot Increments through the session Offer placement, slot, or execution order
paw Present across offer requests Request, package, or session-correlation value; exact meaning unconfirmed
fz Present in outcome callbacks Delivered package size or file-size field
t Present in outcome callbacks Timing, token, or request value; exact meaning unconfirmed
r offer_execution or offer_execution_fail Per-offer execution result
msg Present on failed offers Error text from the local download or installation attempt
ko / cr Boolean-like or short values Server-side control or result flags; exact meaning unconfirmed

Table 2. Assessments are based on observed telemetry correlations, not confirmed server-side definitions.

Offer / download-network pair Semantic meaning
o=1712 / dn=507 Primary first-stage offer commonly attempted at the start of the installer flow.
o=1720 / dn=536 Offer branch associated with CharityEngine/BOINC distributed-compute monetization.
o=1727 / dn=564 Offer branch associated with WorldProxyPool proxyware monetization.
o=1729 / dn=566 Recurring follow-on offer branch in the installer flow.
o=331 / dn=244 Secondary offer branch observed in the multi-offer sequence.
o=1674 / dn=440 Later campaign offer branch.
o=1675 / dn=441 Low-volume offer branch.
o=1681 / dn=447 Additional offer branch in the campaign’s installer rotation.
o=1730 / dn=567 Later high-volume offer branch.

Table 3. Offer and download-network pairs and their semantic roles in the installer flow.

The campaign rotated callback domains frequently while preserving the same d=inno and offer-execution callback structure across recurring lure categories. Individual domains are therefore short-lived infrastructure indicators; the durable hunting signal is the combination of the callback pattern, Inno temporary execution, staged filenames, and related installer-session activity. The full observed domain set is provided in the IOC section.

Final payload installation and monetization

After offer callback and payload delivery, the campaign launched downstream installers or components using unattended installation switches such as /qn, /S, /quiet, and /norestart. This stage converted the fake-download execution chain into installed software and recurring execution across three monetization branches: proxy and network-resource monetization, compute-resource monetization, and adware-style utility monetization.

Branch Primary behavior Representative artifacts
A. WorldProxyPool Proxy agent installation and scheduled-task setup sdk-agent.exe; sdk-agent.updater.exe; watchdog.ps1; WorldProxyPoolAgent task
B. CharityEngine / BOINC Distributed-compute software installation boinc.exe; charityengine.exe; ce11.exe; VirtualBox-7.2.8-r173730.msi
C. AW Manager / Windows Manager Utility and updater-style software installation Windows Manager – Postback Johan.msi; AdvancedWindowsManager.exe; Windows Updater.exe

Table 4. Summary of the three monetization branches and representative artifacts.

Proxy and network-resource monetization — WorldProxyPool

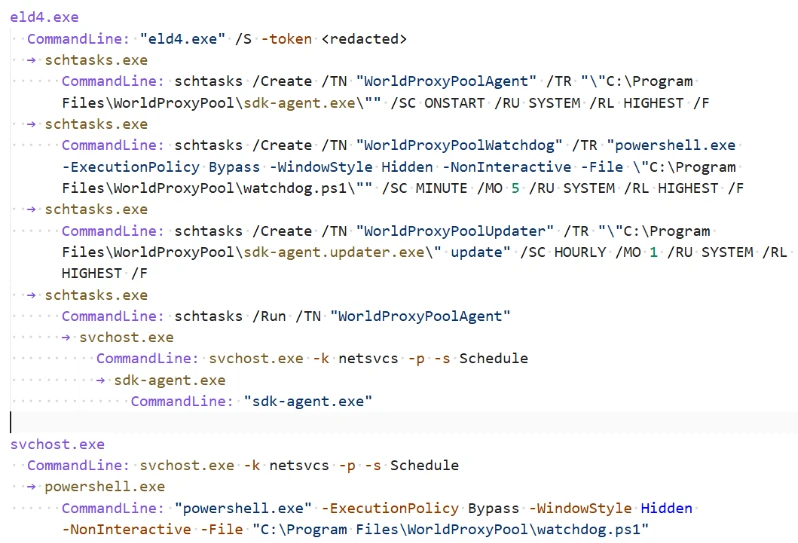
In the WorldProxyPool branch, a staged eld4.exe payload created three SYSTEM-level scheduled tasks for components under C:\Program Files\WorldProxyPool\. WorldProxyPoolAgent configured sdk-agent.exe to run at system startup with highest privileges; WorldProxyPoolWatchdog configured a hidden, noninteractive PowerShell watchdog script to run every five minutes; and WorldProxyPoolUpdater configured sdk-agent.updater.exe update to run hourly. The installer also started the agent task immediately with schtasks.exe /Run. Subsequent task launches were brokered by the Windows Task Scheduler service (svchost.exe -k netsvcs -p -s Schedule), causing sdk-agent.exe and the watchdog script to execute in the service context. This persistence mechanism supports recurring proxy-agent, watchdog, and updater activity, consistent with network-resource monetization.

Scheduled task Purpose
WorldProxyPoolAgent Runs sdk-agent.exe at system startup as SYSTEM with highest privileges; the installer also started it immediately with schtasks.exe /Run.
WorldProxyPoolWatchdog Runs a hidden, noninteractive PowerShell watchdog script every five minutes as SYSTEM with highest privileges.
WorldProxyPoolUpdater Runs sdk-agent.updater.exe update hourly as SYSTEM with highest privileges.

Table 5. WorldProxyPool scheduled tasks created during the proxyware installation chain

Process tree showing eld4.exe creating three SYSTEM-level WorldProxyPool scheduled tasks: an agent that runs at startup, a hidden PowerShell watchdog that runs every five minutes, and an updater that runs hourly. The agent is started immediately through Windows Task Scheduler.
Figure 3. WorldProxyPool installation and persistence. eld4.exe created SYSTEM-level startup, five-minute watchdog, and hourly updater tasks.

Compute-resource monetization — CharityEngine and BOINC

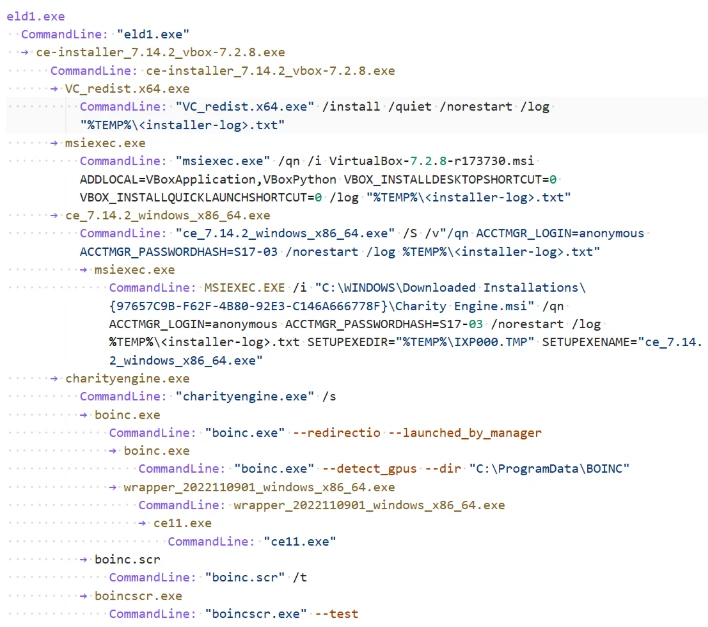
In the CharityEngine and BOINC branch, the offer payload installed distributed-compute software and supporting components under C:\Program Files\BOINC\ and C:\ProgramData\BOINC\. Observed components included ce-installer_7.14.2_vbox-7.2.8.exe, ce_7.14.2_windows_x86_64.exe, charityengine.exe, boinc.exe, boinctray.exe, boinc.scr, boincscr.exe, wrapper_2022110901_windows_x86_64.exe, ce11.exe, and VirtualBox-7.2.8-r173730.msi. They covered BOINC launch, compute-wrapper execution, GPU or compute-capability checks, CharityEngine project communication, and VirtualBox installation.

Process tree tracing eld1.exe through CharityEngine, VirtualBox, and BOINC installation. The chain installs supporting components, launches charityengine.exe and boinc.exe, checks GPU capabilities, and runs a compute wrapper that starts cell.exe.
Figure 4. CharityEngine/BOINC compute-monetization branch.

Adware-style utility monetization: AdvancedWindowsManager / Windows Manager

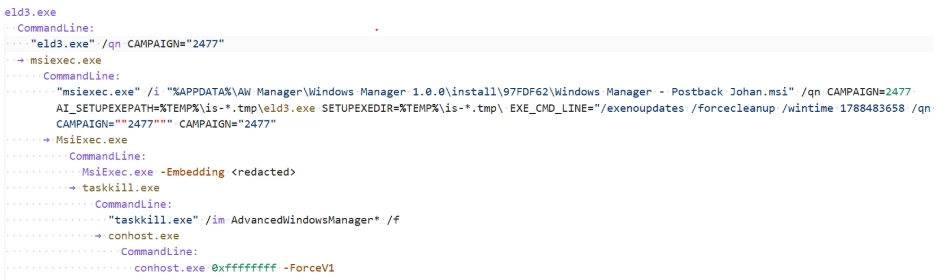
The same Inno offer-execution infrastructure delivered an AW Manager or Windows Manager branch. In one observed process tree, the Inno runner spawned eld3.exe, launched Windows Manager – Postback Johan.msi, and installed AdvancedWindowsManager.exe and Windows Updater.exe under paths resembling %APPDATA%\AW Manager\Windows Manager 1.0.0\ or C:\Program Files (x86)\AW Manager\Windows Manager\.

Process tree showing a command-driven AW Manager/Windows Manager installation under the user’s AppData directory. cmd.exe launches msiexec.exe, starts Windows Manager with an autostart option, and runs taskkill.exe against AdvancedWindowsManager processes.
Figure 5. AW Manager / Windows Manager utility-install branch.

Mitigation and protection guidance

Microsoft recommends the following actions to reduce exposure to this campaign and detect related activity:

Preventive controls

  • Avoid untrusted software sources. Do not download cracked software, key generators, unofficial game installers, or software activation tools, which are common delivery mechanisms for malware, potentially unwanted applications, and monetization campaigns.
  • Enable cloud-delivered protection. Verify that Microsoft Defender Antivirus cloud-delivered protection is enabled to improve detection of emerging malware and potentially unwanted applications. See: Configure cloud-delivered protection
  • Keep tamper protection enabled. Use tamper protection to help prevent unauthorized changes to Microsoft Defender security settings. See: Learn about tamper protection.
  • Enable reputation-based protection. Configure reputation-based protection to help block known malicious and untrusted applications and downloads. See: Configure reputation-based protection.
  • Consider Attack Surface Reduction (ASR) protections. Evaluate ASR rules, including rules that block executable files unless they meet prevalence, age, or trusted-list criteria. See: Review Attack Surface Reduction rules.

Investigation actions

  • Investigate execution from Inno temporary directories. Review activity from paths such as %TEMP%\is-*.tmp\, particularly when staged executables such as eld*.exe, set_*.exe, FirstFast[1].exe, or SecondRunner[1].exe are observed.
  • Correlate Inno callback activity. Monitor outbound requests containing d=inno together with r=offer_execution or r=offer_execution_fail, and review related process, file, and network activity across the complete installer session.
  • Review unexpected scheduled tasks. Investigate newly created scheduled tasks, particularly tasks running with SYSTEM privileges or recurring watchdog and updater functions. See: Audit scheduled task creation events.

Microsoft Defender XDR detections

Microsoft Defender detects and blocks campaign-linked payloads through cloud protection, machine-learning classifications, network inspection, and behavior monitoring. Relevant observed detections include remote-thread injection, scheduled-task launch, and suspicious outbound HTTP activity.

Customers with provisioned access can also use Microsoft Security Copilot in Microsoft Defender to investigate and respond to incidents, hunt for threats, and protect their organization with relevant threat intelligence.

Tactic Observed activity Microsoft Defender coverage
Initial access and execution Users execute fake cracked-software installers, including files presented as Navicat Premium or FabFilter bundles, from Downloads, archive-extraction folders, or Inno extraction paths. The installers launch temporary payloads from %TEMP%\is-*.tmp\. Microsoft Defender Antivirus
– Trojan:Win64/OfferLoader.DA!MTB
– Trojan:Win64/OfferLoader.DB!MTB

Microsoft Defender for Endpoint
– A suspicious file was observed
– An active ‘Wacatac’ malware was detected
– ‘Kepavll’ malware was prevented
Command and control / campaign tracking Outbound callbacks use a stable Inno offer-execution URL contract: d=inno with r=offer_execution or r=offer_execution_fail. Each callback reports an individual offer result. Correlating these callbacks with process, file, network, persistence, and installation events provides visibility across the multi-offer session. Microsoft Defender Antivirus
– Behavior:Win32/SuspInnoOffer.A!mapsi

Microsoft Defender for Endpoint
– Suspicious ‘SuspInnoOffer’ behavior was blocked
Staging and payload delivery The installer chain drops multiple staged files from Inno temporary directories, commonly named eld*.exe, set_*.exe, FirstFast[1].exe, and SecondRunner[1].exe. Microsoft Defender Antivirus
– Trojan:Win64/OfferLoader.DA!MTB
– Trojan:Win64/OfferLoader.DB!MTB

Microsoft Defender for Endpoint
– A suspicious file was observed
– An active ‘Wacatac’ malware was detected
– An active ‘Egairtigado’ malware was blocked
– ‘Kepavll’ malware was prevented
Persistence In the investigated Navicat chain, WorldProxyPool created SYSTEM scheduled tasks with highest privileges: WorldProxyPoolAgent at startup, WorldProxyPoolWatchdog every five minutes through hidden noninteractive PowerShell, and WorldProxyPoolUpdater hourly. It also wrote uninstall metadata under the WorldProxyPool registry key. Microsoft Defender for Endpoint
– Suspicious scheduled task activity
– Suspicious Scheduled Task Process Launched
– Suspicious Task Scheduler activity
Resource hijacking / monetization Two monetization paths were confirmed. The Navicat chain installed WorldProxyPool proxyware. The FabFilter chain silently installed CharityEngine/BOINC, VirtualBox, and Visual C++ components, launched BOINC workloads, and contacted CharityEngine infrastructure. Microsoft Defender Antivirus
– Adware:Win32/Clover
– Trojan:Win64/OfferLoader.DA!MTB
– Trojan:Win64/OfferLoader.DB!MTB

Microsoft Defender for Endpoint
– An active ‘Clover’ malware was detected
– An active ‘Wacatac’ malware was detected
Defense evasion and suspicious behavior Several staged payloads are associated with defense-evasion, execution, persistence, remote-thread, and other suspicious behaviors. Microsoft Defender Antivirus
– Trojan:Win32/OffLoader.A

Microsoft Defender for Endpoint
– Suspicious ‘SuspEtherRpcConn’ behavior was blocked
– Suspicious ‘SuspSmsScanConn’ behavior was blocked

Microsoft Security Copilot  

Security Copilot customers can use the standalone experience to create their own prompts or run prebuilt promptbooks to automate investigation and response tasks related to this campaign. Useful promptbooks include:

  • Incident investigation
  • Microsoft User analysis
  • Threat actor profile
  • Threat Intelligence 360 report based on MDTI intelligence
  • Vulnerability impact assessment.

Some promptbooks require access to Microsoft Defender XDR, Microsoft Sentinel, or related Microsoft security plugins.

For this campaign, analysts can prompt Security Copilot to summarize and correlate available incident evidence, subject to connected data and permissions.

Threat intelligence reports

Microsoft customers can use Microsoft Defender XDR Threat analytics and related Microsoft threat intelligence reporting to track this rotating, multi-offer fake-download campaign and review updates on its Inno callbacks, offer outcomes, staged payloads, infrastructure, and proxyware or distributed-compute results.

The reporting helps analysts correlate offer callbacks and endpoint activity from the same installer session, identify devices with associated monetization stages, and assess the overall bundle outcome. It also provides investigation context, protection guidance, relevant indicators, and recommended response actions.

Advanced hunting

 Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks.

Inno offer-execution callbacks

DeviceNetworkEvents 
| where RemoteUrl has "d=inno" 
| where RemoteUrl has_any ("r=offer_execution", "r=offer_execution_fail") 
| project Timestamp, DeviceName, RemoteUrl, InitiatingProcessFileName 

Payload execution from Inno temporary directories

DeviceProcessEvents 
| where FolderPath has @"\AppData\Local\Temp\is-" 
| where FileName matches regex @"(?i)^(eld[0-9]+|set_[0-9]+|FirstFast(?:\[1\])?|SecondRunner(?:\[1\])?)\.exe$" 
| project Timestamp, DeviceName, FileName, FolderPath, InitiatingProcessFileName, SHA256 

Outbound connections to observed campaign infrastructure

DeviceNetworkEvents 
| where RemoteUrl has_any ("orbittrack.cfd", "prairielink.cfd", "willowbox.xyz", "stonestation.cfd", "foldlodge.xyz", "friendsanchor.xyz", "fallport.cfd", "wishcourt.cfd", "cratebase.cfd", "belieftrack.cfd", "beliefdesk.xyz", "companyharbor.xyz", "signalpane.cfd", "inkact.xyz", "wishgrove.cfd") 
| project Timestamp, DeviceName, RemoteUrl, RemotePort, InitiatingProcessFileName 

Hunting note: Treat each callback as an individual offer result. Group events by device, time window, and available session or affiliate fields, then correlate the callbacks with Inno temporary execution, staged filenames, scheduled-task creation, and monetization-software activity. Domain-only matches are leads, not confirmation. Validate the queries against the current Microsoft Defender XDR schema before publication.

MITRE ATT&CK Techniques observed

The following MITRE ATT&CK mappings reflect behaviors observed in the investigated activity. Mappings are limited to evidence described in this report.

Execution

Persistence

Defense evasion

  • T1036 Masquerading | Installers are presented with names and branding associated with cracked commercial software or unofficial software bundles to encourage execution.

Command and control

  • T1105 Ingress Tool Transfer | The campaign retrieves staged executables and supporting components from threat actor-controlled, cloud-storage, and content delivery network (CDN)-hosted locations.

Impact

  • T1496 Resource Hijacking | The campaign installs CharityEngine/BOINC for distributed computing and WorldProxyPool for proxyware monetization, abusing victim compute and network resources through deceptive bundled installation.

For standard industry documentation about these techniques, refer to the MITRE ATT&CK framework.

Indicators of compromise (IOC)

The following indicators of compromise (IOCs) were observed during investigation of this campaign and can assist defenders in identifying related activity and conducting threat-hunting efforts.

Indicator Type Component
beliefdesk[.]xyz Domain Offer-execution callback infrastructure.
companyharbor[.]xyz Domain Offer-execution callback infrastructure.
signalpane[.]cfd Domain Offer-execution callback infrastructure.
inkact[.]xyz Domain Offer-execution callback infrastructure.
wishgrove[.]cfd Domain Offer-execution callback infrastructure.
%TEMP%\is-*.tmp\eld*.exe File path Recurring staged payload naming and path pattern.
C:\Program Files\WorldProxyPool\sdk-agent.exe File path WorldProxyPool proxyware component.
WorldProxyPoolAgent / WorldProxyPoolWatchdog / WorldProxyPoolUpdater Scheduled task SYSTEM-level persistence created in the investigated chain.
006510ce1da2b7410376f0788c19e55616eb4bcc30072d25b7d0871dc32aa11c SHA-256 Inno second-stage runner
21306fc5716f95e252388f920314b42f1c8bcc7df67cb4d39da30217b96f4044 SHA-256 Earlier Inno loader
72750d32b440e9f2b6d05ff3d218a561a75d3d75fb976b461fa59897674a7f70 SHA-256 Earlier Inno second-stage runner
ab2c2dd37fdcfe1e7620a57f98c80bd063258bea145adc0cc6a0f8b1e24c6a8f SHA-256 Inno eld0 / first-stage payload
452a210bba4c8d08f7cb7733a816d7220a7fa570a469aea0a997cfc8b594b6a0 SHA-256 Inno eld0 / eld1 first-stage payload
523fb81fae0c7beba7b5171243cc0dee7a4d04ae0483be9172eef2394a5a2152 SHA-256 Inno eld0 first-stage payload
55cd3d36fdcc58016a64398357b2c9724a060da9f0d09266e537a61ec9552e4f SHA-256 Later Inno eld2-eld5 payload

Learn More

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.  

The post Fake-download campaign uses trojanized installers to deliver monetization payloads appeared first on Microsoft Security Blog.
Hackers hit UNM hospital, then apologize and offer patients $2,500. In a new statement, they reveal more about the incident.

In more than 20 years of blogging about breaches, DataBreaches has never seen ransomware threat actors offer monetary compensation to patients affected by their attack. We have seen threat actors regret hitting a hospital or a facility providing direct patient care and then offer them a free decryptor and drop the ransom demands, but this...

HHS’ Office for Civil Rights Settles Ransomware Investigation of Lehigh Valley Health Network

DataBreaches.net previously covered the 2023 Lehigh Valley Health Network breach by AlphV (aka “BlackCat”). The breach garnered a lot of public attention when  the threat actors crossed a line by posting nude pictures of patients on their leak site. In 2024, patients settled civil litigation for $65 million. Now HHS has settled its own charges...

UNM Health addresses cyberattack in New Mexico after ransomware group claims responsibility

John Rupolo reports: University of New Mexico Health is addressing concerns after a cyberattack on Monday, with reports surfacing this week that a ransomware group claimed responsibility for the incident. “So what I can say is we’re also aware of those claims by that group,” said Chris Ramirez, communications director for UNMH. The community’s top...

Australia severs criminal access to 180,000 computers after breaching Amadey malware backend

Lukas Brandt writes: Criminals using the Amadey malware lost control of about 180,000 infected computers after operators from the Australian Signals Directorate (ASD) gained access to the operation’s backend and severed the connection between the controllers and the victims. “The next steps that we took were to disconnect that Amadey controller from all those victims,”...

Japanese internet giant GMO tells customers to shut down and disconnect PCs from the internet following data breach and ransomware threat

Sead Fadilpašić reports: Japanese internet giant GMO Group has told its customers to scan their computers for viruses, back up all of their data, disconnect the devices from the internet and then shut them down. The announcement, which literally told customers, “unplug any cords connected to your PC,” was made in response to a cyberattack...

Ukrainian National Sentenced for Role in Hacking Hospitals, Businesses, and Governments as Part of Ransomware Conspiracies Causing Over $100 Million in Losses

A press release from the U.S. Department of Justice: Artem Stryzhak, 36, a Ukrainian national, was sentenced today to 70 months in prison for conspiracy to commit computer fraud in connection with a series of ransomware attacks that targeted hospitals, government entities, law firms, and other businesses around the world. “This sentence concludes a years-long, multi-continent...

IN: 9 servers of Bajaj Hospital hacked in cyberattack at 3 am, sensitive data stolen; systems encrypted

The  Lokmat Times Desk  reports: A cyber attack on the digital systems of Kamalnayan Bajaj Hospital has sent shockwaves through the city. Around midnight, hackers broke into all nine of the hospital’s servers and encrypted its entire data in what appears to be a digital heist aimed at extorting money. The attack has put patient...

Welsh firms ‘Password1’ and ‘Test 2’ fails led to hackers stealing children’s data

Alex Hickey reports: Two Welsh organisations have been censured by the Information Commissioner’s Office (ICO) after a ransomware attack led to the theft of personal data belonging to 3,300 individuals, the vast majority of whom were children. Ogi Networks Limited (ONL) and the Local Government Data Unit – Wales, known as Data Cymru, received reprimands...

Source

Siemens Software Center Vulnerability Exploited in ClickFix Malware Attacks

Attackers paired a genuine, signed copy of Siemens Software Center with malicious DLLs to infect Windows PCs via ClickFix lures.

The post Siemens Software Center Vulnerability Exploited in ClickFix Malware Attacks appeared first on SecurityWeek.

Ransomware Attacks Intensify: Criminals Shift Focus to Target Employees and Their Families

Guru Baran reports: Ransomware gangs are moving beyond locked files and stolen data. Criminals now threaten employees, executives, and their families to force companies to pay. According to the Semperis 2026 Ransomware Risk Report, 37% of successful attacks included threats against workers’ friends or relatives. The findings show that ransomware is no longer only a...

Source

❌