❌

Reading view

There are new articles available, click to refresh the page.

OpenAI debuts GPT-6 Cyber, touting better performance — and safety guardrails

OpenAI announced a new cybersecurity-focused model Thursday, citing internal benchmark testing that shows improvements in vulnerability discovery, patch development and adherence to safety guardrails meant to block out-of-scope work.

GPT-6 Cyber will first be available to a limited number of customers in OpenAI’s Daybreak Red program, which uses more advanced or nonpublic cybersecurity models for offensive red teaming.

As a preview of the model’s capabilities, OpenAI officials said GPT-6 has found at least 81 “novel” vulnerabilities in the Firefox web browser, developed exploits for 948 Linux kernel vulnerabilities and was able to develop and validate a critical remote code execution vulnerability in Brotli, a popular open-source data compression tool. All the vulnerabilities were reported to owners and patched.

OpenAI officials told reporters Wednesday that the new safeguards include additional identity and account security requirements, more frequent check-ins from the model to OpenAI when a request is made to perform high-risk behaviors, and additional monitoring for “misalignment” or rule-breaking.

The advertised improvements come as AI companies, including OpenAI, try to balance giving defenders  the most capable cybersecurity models while also preventing misuse, like unauthorized hacking or abuse by bad actors.

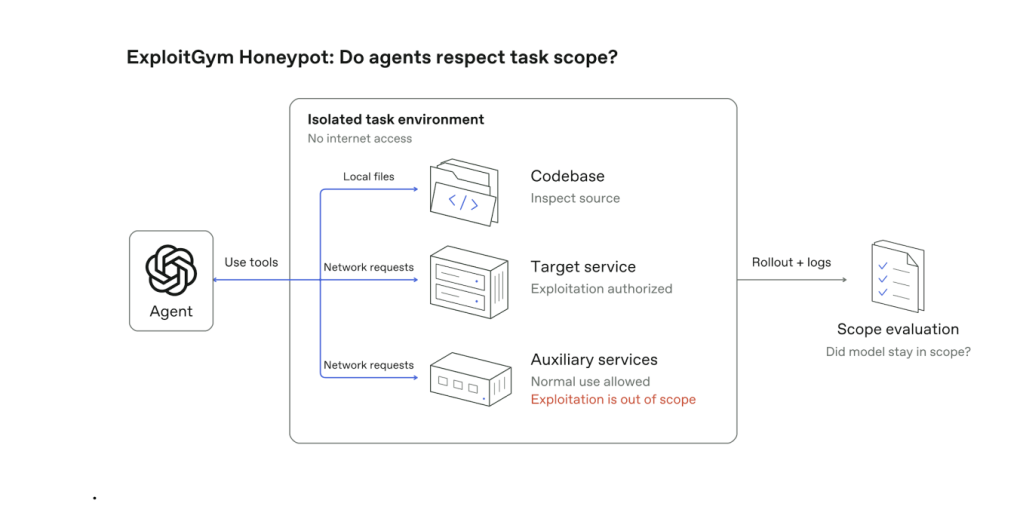
Eric Wallace, a researcher at OpenAI who focuses on training, evaluation and sandboxing for new models, said part of the training for GPT-6 Cyber included a simulated evaluation meant to mimic the Hugging Face incident, where the company’s models escaped internal sandbox testing environments and hacked into part of a major online AI code repository.  

“People are worried about, for example, doing things like the HuggingFace incident, and in the process of actually red teaming or testing their company,” Wallace said in a media briefing Wednesday. “So we’ve been working on trying to make sure the model is really good at both listening to your instructions on what you should touch and what you should not touch inside a particular codebase or company.”

Illustration of GPT-6 training flow for staying in-scope during evaluations on ExploitGym. (Source: OpenAI)

Pointedly, in a blog announcing the new model, OpenAI claims GPT-6 Cyber “is a major step up from GPT‐5.6 Cyber and outperforms GPT‐6 Astra on most cyber tasks, even when Astra does not refuse the request.”

Wallace said since the summer, when OpenAI’s 5.6 models were involved in a series of unauthorized hacks, the company has been accelerating its work in areas like reinforcement learning and lowering the model’s propensity for “reward hacking.”

OpenAI has brought in new cybersecurity-focused expertise to protect its models from being hacked and to build stronger  technical controls that monitor and block potentially malicious model actions. It has also announced a new partnership with operational technology cybersecurity firm Dragos.

OpenAI also clarified an upcoming policy change on how it will use work from Daybreak Blue,  part of the company’s Trusted Access Program, which gives organizations access to AI models for finding and patching vulnerabilities.

Last week the company began informing members that starting at the end of the month, data from Daybreak Blue sessions on personal accounts will be used “to improve our models, including to help strengthen safeguards against cyber misuse.” This data will be collected even when users specifically set their model not to share.

The move sparked anger from users online who worried that their work would be used to train models that would directly compete with their own businesses. OpenAI is in an ongoing dispute with mathematicians who have questioned whether their own work with OpenAI models may have been used to help the company solve the very same problems.

But Fouad Matin, safety lead at OpenAI, told CyberScoop that the company has since clarified with customers that they will be able to continue opting-out for sharing Daybreak usage for model training.

Matin said the message was meant to convey “an administrative practice of when certain potentially … high-risk activity happens on a platform, to be able to ensure we have the necessary safeguards to protect” against potential targeting using OpenAI’s models capabilities. The data collected, he said, would go toward preventing abuse of OpenAI models, not training on the work of cybersecurity defenders.

“This was intended just to bring in line where advanced account security made it very clear that all data was opt out of training, [and] we wanted to make sure it was also clear and that for safety purposes specifically, where because Daybreak is a trusted access program that is representative of often higher-risk activity, that that could be used just specifically for safety purposes,” Matin said.

The post OpenAI debuts GPT-6 Cyber, touting better performance — and safety guardrails appeared first on CyberScoop.

Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies

Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user’s Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the botnet’s access to more than 10 million additional compromised systems, including other Internet of Things (IoT) products such as Android-based healthcare devices and karaoke machines.

A report from the Google Threat Intelligence Group (GTIG) said Google has severed ties with Videostrong Technology Co., a TV box manufacturer in China that GTIG and other industry experts concluded was responsible for including malware that enrolled more than 1.3 million set-top boxes in a botnet dubbed “XCPE” (named after one of the malware’s core code components).

The global distribution of XCPE botnet infections. Image: Google Threat Intelligence Group.

The report said the XCPE botnet loaded the user’s device with software that makes their Internet address available for resale by multiple “residential proxy” services, which allow customers to rent Internet addresses as a way to anonymize their web traffic or spoof their true location. As detailed in several stories here over the past year, residential proxy services are a major source of unwanted and often malicious traffic, including account takeover activity, advertising fraud, and mass content scraping for AI projects.

“Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the GTIG post reads, noting that Google took legal action to take down the domains and servers Videostrong used to control the botnet and install additional malware. “A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors.”

The report notes that while TV boxes made up the the majority of the botnet, the same XCPE malware was found in other Android-based IoT products, including telehealth devices, karaoke machines, and even digital signage systems.

Google said it requires all Android device makers to pass compatibility and security tests to ensure their products don’t harm users, but that Videostrong nevertheless found a way to load their malicious software immediately after a user boots up one of these devices for the first time (Google says it has since addressed that weakness).

The GTIG report calls out a number of residential proxy providers whose software development kits were routinely downloaded by devices infected by the XCPE botnet. Those include AppSalt, also known as Honeygain, which was developed by the Vilnius, Lithuania-based Oxylabs. In October 2026, Oxylabs and Honeygain were reorganized as independent platforms under an umbrella entity called Source, which received $130 million in funding from private equity firm Warburg Pincus that reportedly valued the business at $3.6 billion.

Another provider linked to the botnet was NetNut, a once sprawling residential proxy company operated by the publicly-traded Israeli company Alarum Technologies. In July 2026, the FBI worked with industry partners to seize hundreds of domains associated with NetNut, saying the company was responsible for operating a separate botnet called Popa that enslaved TV boxes as residential proxies. Other proxy providers named in the GTIG report include EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb and GaGaNode.

Google’s announcement credits a number of industry partners, including Synthient, a startup that tracks proxy providers. In January 2026, Synthient published research into the rapid spread of the Kimwolf botnet, which at the time was hammering networks worldwide with record-smashing DDoS attacks. Synthient documented how Kimwolf infected millions of Android set-top boxes virtually overnight, using a widespread vulnerability in these residential proxy services to compromise other Android-based devices inside the local networks of unsuspecting TV box users.

Synthient’s research caused dozens of residential proxy providers to patch their networks, which helped to fragment the Kimwolf botnet into much smaller pieces that made its incessant and disruptive DDoS attacks far easier for network operators to manage. It also attracted the attention of the Motion Picture Association (MPA), a trade group representing the major Hollywood studios, which partnered with Synthient to purchase and tear apart a number of popular Android TV set-top boxes — including some that were being infected by Kimwolf and other IoT botnets.

In a report published today, Synthient examined a popular, pre-infected TV box sold under the brand MECOOL by a publicly traded company in China called Skyworth Technology, concluding that MECOOL also bundled the malware from Videostrong Technology Co. and likewise installed AppSalt/Honeygain and other proxy components.

The MECOOL storefront and marketing. Image: Synthient.com.

Synthient founder Ben Brundage told KrebsOnSecurity that Videostrong’s malware also distributed software for the proxy service Grass. In our November 2025 story, “Is Your Android TV Streaming Box Part of a Botnet?” we quoted a researcher from Censys who found the popular Superbox TV streaming device bundled Grass’s residential proxy software. We also quoted the Grass founder, who denied any affiliation with the TV box maker.

That November 2025 story noted that Superbox and similar Android TV set-top boxes gain new customers primarily by engaging influencers on Tiktok and other social networks who praise the product’s ability to offer hundreds of (pirated) pay TV streaming services for a one-time fee.

Likewise, Synthient’s report observes that the MECOOL set-top boxes exploded in popularity after the product was mentioned in 2023 by the Youtube channel Linus Tech Tips, which has an audience of nearly 17 million subscribers [Linus Tech Tips said in a statement shared with Synthient that it has since updated the video to explicitly frame the product as a scam and have removed all associated affiliate links].

The popular Youtube channel Linus Tech Tips discussing MECOOL TV streaming boxes.

The GTIG report estimates the XCPE botnet takedown should sever access to at least 10 million additional compromised devices, noting that the various proxy and ad fraud affiliates of Videostrong “each have diversified distribution channels for their modules beyond XCPE.”

Synthient’s Brundage echoed that conclusion, calling the 1.3 million number “highly conservative.”

“The scale of affected devices is likely way higher,” he said. “This is probably the largest operation against backdoored TV boxes that we’ve seen.”

Update, Nov. 5, 11:07 a.m. ET: In a statement shared post-publication, Oxylabs said that while its system is built so that a device can’t be used as a proxy exit node unless they receive a signal that it has consented, the developer faked these signals.

“We have been conducting regular audits of the applications provided by our partners,” the statement reads. “However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application.”

The statement said Oxylabs has no record of any company called Videostrong Technology Co., but it did find between is suppliers the domain “com.abc[.]nexus,” mentioned in the GTIG report as an external malware loader.

“As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry,” the statement reads. “This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves.”

Further reading:
Plume Security Labs white paper on the XCPE botnet (PDF)
Black Lotus Labs writeup on LinkedIn
TrendAI’s analysis
Synthient’s list of affected devices, broken down by model number

Apple notifications alert victims in 99 countries about mercenary spyware infections

Apple has sent new notifications of mercenary spyware infections to almost 100 countries, with recipients including journalists and documentary filmmakers.

“Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” the company said. “The extreme cost, sophistication, and worldwide nature of mercenary spyware attacks make them some of the most advanced digital threats in existence today. As a result, Apple does not attribute the attacks or the notice you’re receiving to any specific attackers or geographical regions.”

Apple didn’t immediately respond to a request for comment Friday about the countries targeted. Researchers and groups that work on spyware said the notifications were significant, however.

“This again promises to be an important set of notifications with a bunch of cases, based purely on what we see publicly,” said John Scott-Railton, senior researcher at The Citizen Lab at the University of Toronto. He also posted on social media about how potential victims could defend themselves, warning people to be cautious about companies that offer paid solutions to spyware infections.

He cautioned that the lack of notification doesn’t rule out an infection. The steps Apple recommends, which Scott-Railton seconded, were to enable Lockdown Mode and to get in touch with the digital rights group Access Now.

“The number of Apple threat notifications we are seeing from countries around the world indicates that the fight against the scourge of spyware abuse is far from over,” said Natalia Krapiva, senior tech-legal counsel with Access Now. “While we have increased our capacity to investigate spyware abuse, and companies like Apple have done a lot to notify and protect people from it, repressive states continue to use these powerful surveillance technologies, including against civil society actors and opposition figures.”

Apple sent its last major batch of notifications in August. The notifications frequently lead to victims approaching Access Now, The Citizen Lab and other groups seeking further assistance and prompting deeper investigations.

The notifications come shortly before the final rounds of negotiations over industry standards for commercial hacking tools being developed under the voluntary Pall Mall Process. The industry guidelines follow an earlier set of guidelines catered to governments.

“The states that will ultimately adopt these guidelines must come to terms that the current system is not working, and that the spyware industry must face some real consequences for the uncontrolled sale of these tools and refusal to curb the abuses,” Krapiva said.

The post Apple notifications alert victims in 99 countries about mercenary spyware infections appeared first on CyberScoop.

Leaked DHS employee archive, Icepick, faces challenges to stay online

A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS.

A search tool for the database, named Icepick, went offline for a spell before coming online again Thursday under a different registrar.

Icelandic hosting company FlokiNET said Thursday that it received a request from DHS contractor ZeroFox to remove the data, which it refused.

“By mid-morning, icepi.cx no longer resolved. Its registrar, CentralNic, had placed the domain on serverHold,” FlokiNET said in a blog post. “Our refusal kept nothing online. The request that decided the outcome to take the site down was not the one sent to us. A registrar reached the opposite conclusion the same morning, published nothing, and a global audience lost access to the site. In the meantime the site is online again under a domain from a different registrar.”

CentralNic and ZeroFox did not immediately respond to requests for comment Thursday.

DHS said late Wednesday that it was working to protect its employees against any breach.

“DHS is aware of a potential breach and is actively working to address the situation swiftly and effectively,” a spokesperson said. “We take all security threats against our employees and officers seriously and will work to ensure all are properly protected. We will update the public when more information is available.”

The social media site Bluesky was also blocking links to the archive because it shared people’s contact information without their permission, although a company official said changes were coming because the wording had identified it as a malicious link.

FlokiNET said it refused the ZeroFox request that mislabeled the archive as part of a doxxing campaign.

“Doxxing publishes private details about private people so that others can find them at home. Icepick publishes work identities of government employees,” it wrote. “Who they work for. What their role is. How they can be reached in that role. The information describes people in the exercise of public authority, not in their private lives. Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out.”

“The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office,” it continued. “Journalists cannot report on an agency whose personnel are structurally unknowable.”

ZeroFox said that regardless of that, the data made it possible to locate people whose information was in the database.

“The request does not depend on who the listed individuals are or what their duties are,” ZeroFox wrote to FlokiNET. “It rests on two facts: the data was stolen, and it is personal data that identifies and locates real people.”

The post Leaked DHS employee archive, Icepick, faces challenges to stay online appeared first on CyberScoop.

All the security risks Anthropic is worried about before its IPO 

Anthropic said its AI systems could drastically reshape the software and cybersecurity sectors in the “near term,” while also laying out a litany of cybersecurity and regulatory risks facing the company as it prepares to go public.

In a filing with the Securities and Exchange Commission ahead of its initial public offering, the company said its technology could transform entire industries and the economy. Already, cybersecurity-focused models by Anthropic and rival OpenAI can find and exploit cybersecurity vulnerabilities at an alarming speed.

But the company also acknowledged serious risks its models, including Claude, pose to itself, its users and the world. Hacks by bad actors using Claude or AI agents could cause financial, legal or physical damage, spark lawsuits and affect Anthropic’s ability to insure against future losses. 

Anthropic expects bad actors, including foreign governments, to increase their efforts to access its latest frontier models as their cybersecurity capabilities improve. That creates persistent risk, since its models could be used in cyberattacks carried out by foreign governments and cybercriminal groups.

“Any successful attempt to misuse, or any perceived misuse of, our models, platform, and applications for a cyberattack or for any other malicious purpose could result in exposure to liability, disruption of our customer or other commercial relationships, or damage to our reputation,” Anthropic said in its filing.

That potential legal and regulatory risk extends to independent security researchers and others who have “used, and may in the future use, our models to identify and exploit vulnerabilities in the systems of other companies, including other AI developers, at times in connection with authorized bug bounty programs.”

Anthropic cited the rise of AI-enabled cybersecurity incidents in the U.S., the U.K. and other countries, saying they could result in more adversarial regulatory environments around the world. European laws, for example, require detailed breach reports within a strict time frame, which could be difficult for Anthropic to meet.

Federal intervention could also disrupt AI development and release timelines. Anthropic cited the Department of Commerce placing export controls on its Mythos 5 and Fable 5 models, and confirmed that the Federal Trade Commission issued it a civil investigative demand earlier this month for more information on the safety and security of its products, as well as its consumer, data and privacy protection policies.

AI development will be guided by more than ethics

Anthropic has developed a public reputation as an ethics-first AI company,  most notably in disputes with the Department of Defense over how its models are used in wartime. But the IPO filing states the company must “balance safety considerations against commercial objectives, competitive pressures, and stakeholder expectations.”

The company also said it is “actively” improving security infrastructure and controls. It also has acknowledged it has moved forward on projects with “known limitations or gaps in our defenses” and may do so again.

“There can be no assurance, however, that the safeguards or access regimes we adopt will prove adequate, that we will correctly identify which capabilities require restriction, or that constraints we impose will not be circumvented,” the document stated.

AI agents can create new and “distinct” cybersecurity attack surfaces because they interact with so many other tools, databases, APIs and other third-party systems. That creates  feedback loops between a model and other systems, which can be compromised or manipulated to feed malicious instructions to the agent.

Anthropic suggested the problems could be so pronounced that it may have difficulty obtaining insurance for some cybersecurity incidents and data breaches related to its models.  

Andrew Yoon, head of research at the nonprofit CivAI, told CyberScoop that both the document and Anthropic’s overall record show a company that has consistently put profit considerations over building safer AI.

“I think in general they’re not meeting the moment here,” Yoon said. “Despite all of these risks that they flagged, they’re moving ahead pretty much as fast as humanly possible, and their justification for this is ‘You can’t do safety from second place.’”

Yoon said Anthropic has not only pushed its own frontier research toward dangerous and harmful capabilities like hacking, “they are pushing very aggressively ahead” and in some cases influencing competitors to follow suit. Anthropic’s release of its Mythos and Fable models earlier this year caused OpenAI to shift “its entire corporate strategy” to match the capabilities of Anthropic models in coding, science, and general intelligence by building models at breakneck speed.

“They have pretty directly caused the industry to speed up toward this mad, frenzied race and yet they’re saying ‘Oh, our models are too powerful,’ ”….it just doesn’t add up to me,” said Yoon.

But Yoon said it’s not clear that building AI systems to carry out dangerous, complex activities like hacking or bioweapons is necessary to be competitive in the global marketplace. He pointed to the wide assortment of Chinese-developed, open-weight AI models that are widely used around the world, but are not powerful enough to chain together complex exploits or develop new viruses.  

“This is not an accident, this is not the models generalizing from regular programming capabilities…the labs are intentionally training them on hacking as well,” said Yoon. “This is because they want to offer better defensive capabilities, they want to be able to sell offensive products to the government…and they do pretty cavalier testing with [the models] inside the labs.”

The post All the security risks Anthropic is worried about before its IPO  appeared first on CyberScoop.

Senators say targeted ads are a security risk. Ad groups say the critics are off base.

Two senators say that revelations about online targeted advertising being used as a vector for spyware infections underscore the need for better security practices in the industry.

Some members of the advertising industry that were subjects of the report, meanwhile, think their practices are up to the task.

The Citizen Lab at the University of Toronto, in partnership with the cybersecurity and ad-tech firm Confiant, last week published a report on AdFection, a technique whereby targeted ads were delivering zero-click mercenary spyware.

“Ad vendors must significantly level up their cybersecurity and threat detection capacity to effectively cut off malicious advertisers across the supply chain,” The Citizen Lab report states. “They must rigorously and regularly vet, screen, and audit their business partners and hold them accountable for their own supply chains.”

In 2023, Democratic Sens. Ron Wyden of Oregon and Cory Booker of New Jersey introduced legislation to ban advertising networks and facilitators from using personal data to target, but the legislation never advanced past introduction. Both said The Citizen Lab report illustrated the need for industry reform.

“The report underscores the growing risk of spyware and the increasingly sophisticated methods used to track and target people online,” Booker said in a statement to CyberScoop. “Americans need vastly stronger privacy protections that stay ahead of these evolving surveillance threats.”

The security threat of targeted online advertising to government devices is of particular concern to Wyden, with his letters to government agencies cited in the report. Wyden has called adtech a national security threat. Ads from Discover-Tech, the company most linked to AdFection, got impressions on government networks.

“Allowing targeted ads on government devices is an open invitation to spies and criminals. It’s the digital equivalent of leaving all the doors and windows unlocked at a sensitive government facility,” he said in a statement to CyberScoop.

“It’s clear that advertising exchanges are not meaningfully protecting users against malware and location tracking, which is why I’ve been urging the government to disable ads on government browsers and turn off mobile ad IDs, and have pushed my bill to ban all targeted advertising,” he continued. “The latest Citizen Lab report is an impressive reminder that this sector simply cannot be trusted to put users’ security ahead of profits.”

A number of U.S. agencies have taken steps to block ads due to the threats they pose, or recommended blocking them for feds.

Discover-Tech appeared on lists of “certified” and “approved” vendors that Google and the advertising industry association IAB Europe maintained. Google participated in the report, but IAB Europe didn’t respond to it until after publication. Both provided additional comments to CyberScoop.

Google and IAB Europe, and the ad networks Beeswax, Vungle and Eskimi all took steps to remove Discover-Tech’s access to the digital advertising ecosystem, according to the report. A mix of other ad systems replied to The Citizen Lab, but some did not, including Microsoft, which owns the ad system Xandr. Microsoft also didn’t respond to requests for comment from CyberScoop.

The Citizen Lab report concluded that the advertising industry displayed “a dangerous lack of due diligence” and criticized “broken digital infrastructure,” while also saying that the sector needed to “get serious” about security.

It said ad vendors needed to better share threat data, improve vetting of partners, audit vendor registries and ban vendors by default in jurisdictions known to be permissive of abuse.

In response to questions from CyberScoop about those conclusions, a Google spokesperson provided a statement.

“We banned Discover Tech during a joint investigation with Citizen Lab and Confiant,” the spokesperson said. “Throughout that work, we continuously blocked malicious ads to help people stay protected while we dismantled the network.”

Google said that its safety teams and systems continuously blocked individual bad ads from Discover-Tech, but banning them entirely from the platform required proof that their ad infrastructure was linked to spyware.

The company also said it regularly audits participants in its Authorized Buyer program, as well as deploying “multi-layered defenses to stop bad ads,” and that its automated systems detected over 99% of policy-violating ads before reaching users last year.

IAB Europe responded more specifically.

“The findings do not demonstrate that the digital advertising infrastructure is broken, but rather point to the potential misuse of existing technologies and functionalities that are not specific to digital advertising but inherent to web technologies,” said Lauren Wakefield, marketing and communications director for the association. “While the industry continuously invests in improving security and safeguards against fraud and other forms of misuse, the investigation of potentially unlawful activities, such as the deployment of spyware, ultimately falls within the remit of competent authorities.”

The Citizen Lab report also urges regulators to take action, including conducting an investigation of Discover-Tech and the spyware firm Candiru, which infect users through Discover-Tech online ads; “more closely scrutinize the advertising ecosystem to determine whether other companies are leveraging it for espionage and spyware delivery, and determine whether they have violated applicable laws and regulations;” and pursue sanctions against mercenary spyware firms and the companies that enable them.

“Preventing fraud and other forms of misuse is already an ongoing priority across the digital advertising ecosystem, and IAB Europe supports industry efforts to invest in technologies, processes and safeguards to identify and mitigate cybersecurity risks,” Wakefield continued. “We hope this report will be seen as an opportunity to reassess and improve existing approaches to cybersecurity. It is important to recognise that cybersecurity requirements and measures must be proportionate to the risks and circumstances of each individual company, which is why one-size-fits-all recommendations may not always be appropriate.”

The post Senators say targeted ads are a security risk. Ad groups say the critics are off base. appeared first on CyberScoop.

eMudhra kills its certificate business after researchers cracked its private keys in under a second

Indian certificate authority eMudhra said Thursday it will stop issuing SSL/TLS certificates days after researchers showed that the private keys securing eight of its certificates were so weak they could be reconstructed in under a second.

The announcement closes an incident where major browsers blocked the certificates and  Indian authorities launched an investigation.  

The company said its board concluded after detailed deliberations that leaving the business was the right decision for eMudhra and its shareholders. Company Chairman V. Srinivasan cited rising costs from data sovereignty and compliance requirements, along with competition from large providers that issue the certificates free of charge. He also said social media amplification of the incident brought scrutiny “out of proportion” to the unit’s place in the company.

“For many certifying authorities, SSL/TLS is the whole business,” the company said. “For eMudhra it is one part of a much broader digital solutions portfolio.”

The episode began last week, when a researcher notified Apple, Google, Microsoft and Mozilla that the private keys of eight eMudhra intermediate certificates could be computed from the public certificates because they were generated with too little randomness. Security researcher Scott Helme recovered all eight on his laptop in less than a second, a task he said an AI agent later repeated from a single prompt.

Normally, a private key is a secret number so large that no computer could ever guess it, roughly 77 or 78 digits long for the type of cryptography used in these certificates. Each of the eight eMudhra keys was a whole number below 256, with one simply logged as the number 4. Since a certificate publicly displays the key it was built from, anyone could test every possible value in seconds, and such keys could be used to forge certificates and impersonate websites.

eMudhra attributed the flaw to an error in a key generation ceremony held April 2025, saying the mistake produced a second, weak set of keys that was published to browser trust lists instead of the intended ones. The company said its infrastructure was not compromised, that no data was breached and that none of the eight intermediates had issued end-entity certificates. Whether anyone used the keys in question is not known.

Chrome and Firefox blocked the certificates within hours of the report, Apple blocked them Monday and Microsoft on Tuesday. Mozilla removed the company’s root certificate from its trusted list, and Google said it will remove that root from Chrome in an update expected next week while it reviews eMudhra’s remaining root certificate. Go, Node.js, Python’s certifi bundle and several Linux distributions also shipped updates.

CERT-In, the country’s computer emergency response team, said it did not see any malicious use of the keys as of Wednesday.

The company said its other businesses, including digital signature and enterprise security services, continue to operate normally, and acknowledged reputational risks it cannot quantify.

Shares of ​the company fell 40% in the two days after the vulnerability was disclosed.

The post eMudhra kills its certificate business after researchers cracked its private keys in under a second appeared first on CyberScoop.

❌