โŒ

Normal view

There are new articles available, click to refresh the page.
Today โ€” 25 September 2026Main stream

Phone-hacking company that won U.S. security agency contracts hid Russian ownership, DOJ alleges

24 September 2026 at 13:07

Law enforcement has arrested two leaders of a Russian-owned phone hacking company used by Kremlin agencies who allegedly masked its foreign ownership from the U.S. Defense Department, Department of Homeland Security and others to win millions of dollars worth of contracts, the Justice Department announced Wednesday.

Lee Reiber of Boise, Idaho, the CEO of Oxygen Forensics (Oxygen US), was arrested in his home state and Oleg Davydov, one of five Russian nationals whom DOJ said actually controlled the company, was arrested in London, from where the department plans to seek his extradition. They face charges of conspiracy to commit wire fraud.

Publicly, Oxygen went to great lengths to present Reiber as the true leader of a company based in Alexandria, Va., asserting that the company was not controlled by Russian-based executives, according to a criminal complaint., While the company told government agencies it was U.S.-owned, Russian officials with the company repeatedly overruled him, the complaint alleges.ย 

Oxygenโ€™s business aims were complicated in 2022 after the United States expanded sanctions against Russia following its invasion of Ukraine. Thatโ€™s when the company installed Reiber as CEO and removed the owners from public corporate filings. An unnamed co-conspirator in the complaint nonetheless said that โ€œfateful decisions will be made byโ€ five shareholders, including Davydov.ย 

Since March 2022, Oxygen has sold its forensics software to the U.S. Secret Service, Homeland Security Investigations, the DHS inspector general and DOD. After the 2022 sanctions, Oxygen won more than $2 million in contracts and purchases from the Secret Service and its National Computer Forensics Institute. Reiber asserted U.S. ownership as recently as February of this year to the NCFI, according to the complaint.

Reiber knew the company had to conceal its true ownership, the complaint states. Oxygen and its competitors have quarreled in the media and in courts. Oxygen in 2023 faced accusations that Oxygen US and Oxygen Russia were both using software code reverse-engineered from Elcomsoftโ€™s products. Oxygen Russiaโ€™s customers included the Russian Federal Security Service (FSB).ย 

โ€œThe accusation mattered to Reiber because answering it truthfully would have required disclosing that Oxygen US and Oxygen Russia sold the same software, developed by the same team, and were owned by the same people,โ€ the complaint reads, citing email correspondence.

Knowing Oxygenโ€™s actual ownership configuration wouldโ€™ve changed the equation for the government agencies, according to the complaint.

โ€œProcurement officials at the U.S. government customers have represented that they would not have awarded or renewed contracts for the forensic software had they known that OxygenUS was a Russian-owned company,โ€ the complaint reads.

Natalia Krapiva, senior tech-legal counsel at Access Now, celebrated what she nonetheless called an overdue move from DOJ.

โ€œFor years, civil society warned that Oxygen Forensics was owned and built from Russia. Now the Justice Department confirmed it,โ€ Krapiva told CyberScoop. โ€œWe applaud the U.S. government for taking this crucial step, but the fact that it took so long is both a national security and a human rights scandal.โ€

โ€œThe same technology that extracted data for U.S. investigations has been used inside Russia to jail journalists, activists, and peaceful dissenters. And it doesnโ€™t stop at the U.S. border,โ€ she continued. โ€œWe call on the U.S. and over 100 governments using this technology to immediately sever all ties to the company, implement sanctions, and conduct full investigation(s) of how Russian tech designed for the FSB spent all these years inside their sensitive law enforcement operations.โ€

Court-listed attorneys for Reiber listed in court documents didnโ€™t respond to requests for comment. No attorney for Davydov could be located.

The DOJ in its announcement specified that โ€œThe complaint does not allege that the software contained malicious code or that it was used to gain unauthorized access to any customerโ€™s computer systems or data.โ€

The post Phone-hacking company that won U.S. security agency contracts hid Russian ownership, DOJ alleges appeared first on CyberScoop.

Five Police Officers Criminally Charged for Misusing Flock Cameras in Indianapolis

24 September 2026 at 15:04
"Nationwide, at least 100 police department employees have been charged with or accused of misusing license-plate readers for unauthorized purposes," reports the Washington Post. They cite their past investigations "based on thousands of pages of police and court records," which found that "In many of these cases, officers used Flock's roadside cameras to track the location of romantic partners and exes." In fact, five Indianapolis police officers were just criminally charged Wednesday with fraud and misconduct. "One has also been charged with stalking," the police department said in a statement, noting that one office had already resigned, "while the four other officers have been suspended and recommended for termination. County prosecutor Ryan Mears admitted "A lot of this was initiated by The Washington Post." And the Post published a new investigation Wednesday: Using publicly available information, The Post found that...one of the officers charged Wednesday, appeared to have relied on Flock cameras to track vehicles used by his wife and two close personal acquaintances, searching the plates 3,759 times over a 10-month period โ€” an average of about 12 lookups per day. At the time, Police Chief Tanya Terry said she suspended one officer while the department conducted an investigation into possible misuse and a systemwide audit of the city's 301-camera Flock system. That audit led to the discovery of more widespread abuse, [County prosecutor Ryan] Mears said Wednesday. Mears said the department's findings highlight the vast power Flock cameras give police officers and raise questions about whether the government should be doing more to prevent the misuse of that power. "Many of the proposed guardrails and the things that have been proposed would not have prevented the behaviors and actions we see here today," Mears said. "Does there need to be independent oversight? Does there need to be judicial oversight of the Flock camera system?" One of the Indianapolis officers, Schultz, an 18-year veteran of the police department, was accused of using Flock to track his ex-wife and women he met while on duty or out in public. He was charged with multiple counts of official misconduct as well as two counts of stalking. Schultz told one woman he was an FBI agent, according to prosecutors, and began texting her and showing up at places she frequented, including at her gym and at a school function with her daughter. Prosecutors said he arrived at her gym within an hour of her at least nine times between June 12 and Aug. 1 of this year... Another woman met Schultz after her car was stolen from a mall parking lot, and he began texting her flirty messages later that night. The two dated briefly, and Schultz later looked up where the woman went on dates with another man. Schultz searched the plates of a third woman 178 times and also frequently showed up where she was, including her gym, a Smoothie King and a Walmart earlier this month... A third officer, Binford, told investigators he had used the log-in credentials of another officer who had logged in to Binford's laptop during a field training exercise. Binford searched the plate of his ex-wife more than 1,000 times between April 2024 and April 2025. Indianapolis police had no regular practice of auditing officers' Flock searches until recently, [Police Chief] Terry said in an interview last month. The department's investigation into the tool's misuse has been "a learning process for us," she said at the time.

Read more of this story at Slashdot.

Yesterday โ€” 24 September 2026Main stream

UK regulator to investigate Pornhub parent company for alleged age verification failings

23 September 2026 at 16:07
In May, Pornhub began using a new age assurance process to verify some usersโ€™ ages, according to an Ofcom press release. The new method relies on signals from Apple that suggest under 18s in the UK โ€œmay have completed Appleโ€™s age checks,โ€ the press release said.

Before yesterdayMain stream

Canadian regulator opens probe of IDScan for allegedly violating data privacy laws

22 September 2026 at 15:52
The investigation, announced Monday, will probe IDScanโ€™s security practices and whether victim notifications were adequate under Canadaโ€™s federal private-sector privacy law, the regulator said in a press release.

EU data regulator fines Google more than $460 million for location data violations

21 September 2026 at 15:15
Irelandโ€™s Data Protection Commission will fine Google more than โ‚ฌ403 million ($462 million) over the tech giantโ€™s processing of location data, concluding an inquiry into the company that began in early 2020.

LinkedIn wins court order blocking mass scraping of user data

21 September 2026 at 08:55
The agreement between LinkedIn, ProAPIs and joint business operator Netswift also requires the firms to stop selling and transferring the data, no longer access LinkedIn through fake accounts and delete the data that was scraped, according to a senior LinkedIn executive.

Google Hit With $463 Million Fine for EU Location Data Rule Breach

21 September 2026 at 13:19

Google has been fined 403 million euros ($463 million) for breaching the European Unionโ€™s strict privacy rules because it mishandled usersโ€™ location data.

The post Google Hit With $463 Million Fine for EU Location Data Rule Breach appeared first on SecurityWeek.

Australia Considers Smart Glasses Ban in Government Workplaces, While 70 People Sue Meta Over Unknowing Data Collection

21 September 2026 at 06:04
"Australia is considering barring the use of camera-equipped smart glasses in government workplaces..." reports Reuters, "in what it said could be the first ban of its kind." But meanwhile "more than 70 people who bought, used or were recorded with Meta's smart glasses have sued the social media giant," reports the Los Angeles Times, "claiming their intimate and sensitive images were exposed to workers abroad who are paid to review and label photos and videos." The contractors in Kenya work for companies that help train Meta's artificial intelligence, according to a proposed class-action lawsuit amended in late August. The smart glasses users, some in California, allege the gadget captured footage of themselves and family members undressing, going to the bathroom, having sex and entering passwords. In some cases, the people said they weren't aware the camera-equipped glasses were recording. One California user, referred to as PL18 in the lawsuit, alleges his glasses were unknowingly recording after he placed the smart glasses on the bathroom counter. "He noticed that at times photos of his family members using the bathroom and bathing began appearing in his gallery โ€” footage no one in his household intended to take," the lawsuit said.... The 230-page lawsuit, filed in a federal court in Northern California, accuses Meta of fraud and false advertising, along with violating other consumer protection laws in various states. Tina Wolfson, one of the lawyers representing the plaintiffs, said the case also centers on Meta's surveillance of people's lives without their consent and the exploitation of their image and likeness. "People who bought these glasses and thought that they were cool gadgets weren't aware that every time they activated AI, video was sent to train Meta's AI," said Wolfson, a principal at law firm Ahdoot & Wolfson in Burbank. Meta disagrees with the allegations and intends to fight them. "If you use Meta AI, we may review that data to help improve our products and people's experiences โ€” this works the same way as many other companies. We take steps to filter this data to help remove identifying information and to protect people's privacy," a Meta spokesperson said in a statement... The lawsuit alleges people wearing the smart glasses were unwittingly transmitting data to Meta whenever they used Meta AI by saying "Hey Meta," or sometimes accidentally when adjusting the glasses. "Every activation of the AI features, intentional or accidental, captures video and audio that is transmitted to Meta's servers, routed overseas, and reviewed by low-paid human workers who watch, label, and embed these moments into Meta's AI models," the lawsuit said... The lawsuit also seeks to block Meta from deploying biometric tools through its glasses. The company has been exploring a controversial feature called "NameTag" that would allow people to identify others... A separate lawsuit, filed in September in a federal court in Illinois, alleges Meta has been using images of people's faces uploaded to their public Facebook and Instagram accounts to train AI that powers NameTag and other AI tools.

Read more of this story at Slashdot.

Customer-Losing Flock Now Offers Buyouts to Avoid Laying Off Employees

19 September 2026 at 22:34
Mashable writes: Flock Safety offered employees voluntary buyouts on Friday, WIRED reported... Without the buyouts, those familiar with the situation suspect the company would have to lay off some of its 1,500 employees. WIRED writes that people familiar with the program "say they believe that a significant number of the startup's roughly 1,500 employees may try to depart." Flock is making the severance offers as it continues to lose customers... The company has had many of its contracts either not extended or dropped this year, which could leave it short of revenue goals, according to two of the people. A wave of vandalism targeting its cameras has unexpectedly increased expenses. Without buyouts, Flock almost certainly would have to lay off some staff, one of the people believes... People familiar with Flock's severance plan tell WIRED that some employees may take the offer amid speculation that the company, which has raised about $1.2 billion in venture capital, might resort to selling off parts or all of its business to stay afloat... One advocacy group identified 93 city and county governments that cut ties with Flock in August alone. Overall in 2026, roughly three times as many local governments have dropped Flock compared to the previous five years. Flock has recently been building products that extend the company beyond its core license plate reader offering. WIRED reported last month that the company has developed AI-powered investigative software to identify drivers, find potential associates based on patterns of movement, and search across police records and other data. A separate WIRED analysis of Flock's software found tools designed to continuously search camera feeds for people matching written descriptions. WIRED's analysis of Flock's code also found potential integrations with drones and other surveillance systems. Flock's financial scrambles might explain an incident in Syracuse, New York. The nonprofit news site Central Current discovered the city's contract said its license plate data wouldn't be shared outside the police department, reports Mashable: But the department had granted access to other agencies, which police said was an accident. Over roughly a year, searches by officers around the country reached Syracuse's data nearly 4.4 million times. And that wasn't the only surprise in the paperwork. Central Current also found that Flock could keep using Syracuse data after the contract ended. When the city approved cameras from Axon to replace Flock's, Flock said Syracuse couldn't simply end its agreement early. It warned that the city might have to pay for both systems; so even as officials moved to replace the cameras, they faced questions about what Flock could do with the data and what the city might still owe. Meanwhile, the Texas Department of Transportation "has stopped issuing permits allowing Flock cameras and other automated license plate readers to be installed along state roads..." reports the Texas Tribune. "There were an estimated 13,000 Flock cameras across Texas in August, but hundreds of the devices have been shut down after [governor] Abbott's funding freeze." And in August Florida's Republican Governor "ordered his state's transportation department to remove the cameras from state roads, saying he didn't want 'a surveillance state.'"

Read more of this story at Slashdot.

Hackers Stole Flock's Camera Software, Revealing How the Company Tracks Cars and People

17 September 2026 at 12:04
"Hackers ripped down a Flock camera above a roadway, made a near-complete copy of the data stored inside it, and shared the files with 404 Media and WIRED," according to an article published on both sites. Though Flock has described its system as protected by on-device encryption, "The hackers were able to copy the camera's storage and recover an encryption key stored on the device, which unlocked videos of thousands of vehicle detections." The hackers shared the material with 404 Media and the transparency nonprofit Distributed Denial of Secrets, which shared the data with WIRED. 404 Media and WIRED then analyzed those files as part of a joint investigation... [T]he joint analysis of the recovered data shows that software running on the device explicitly detects people as well as vehicles, license plates, and bicycles. The camera can produce dozens of images of a single passing vehicle and, according to several weeks of recovered logs, generated more than a million images. Its computer-vision software also sometimes isolated bumper stickers and other graphics, including, in one case, an American flag patch on a motorcyclist's saddlebag... According to our analysis, the camera's logs recorded about 21 days of activity across several periods. During those windows, the device photographed roughly 50,200 vehicles and generated about 1.6 million images. On a typical day, it logged around 3,300 vehicles, with a high of 4,454... The software running on the camera explicitly detects people, something which is typically overlooked in discussions around Flock cameras. When it spots a person, it records where they appear in the image and how confident it is in the detection. It was a collective calling itself stegan0gram that breached the cameras, according to the interview they did with Wired and 404 Media. "Why just destroy them when we can reverse engineer them and find the secrets of those spying on us?"

Read more of this story at Slashdot.

Data Broker Radaris Loses Domains in Privacy Fight

16 September 2026 at 14:14

The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state law enforcement officials. In the face of repeated stonewalling and prevarication by attorneys for Radaris, the judge in the case ordered that radaris.com and more than a dozen other data broker domains be transferred to the plaintiffs.

The radaris.com website, prior to the domain transfer to Atlas.

In February 2024, Radaris was sued by Atlas Data Privacy Corp, a company that has been pursuing data brokers alleged to be violating a New Jersey statute called Danielโ€™s Law. The statute allows state law enforcement officials, government personnel, judges and their families to have their information completely removed from commercial data brokers and people-search services, and provides for fines of $1,000 per violation against companies that ignore removal requests.

Less than a month after Atlas sued Radaris, KrebsOnSecurity published a deep dive into the Radaris co-founders โ€” Igor and Dmitry Lubarsky (also spelled Lybarsky) โ€” Russian-born brothers living in Massachusetts who operate a dizzying array of people-search companies as well as a number of Russian language dating services and affiliate programs.

Attorneys for the Lubarsky brothers threatened to sue for defamation if the story wasnโ€™t removed and an apology issued. Their attorney asserted that our reporting was wildly inaccurate, and that the true owners of the company were Ukrainians living in Ukraine.

The Lubarsky brothers Dmitry or โ€œDanโ€ (left) and Gary/Igor.

KrebsOnSecurity doubled down and showed how the Lubarsky brothers built and operated Radaris and other data broker companies using a fictitious CEOโ€™s name. Our follow-up story noted that Radarisโ€™s attorney โ€” a lawyer with the Boston Law Group named Val Gurvits โ€” admitted his clients had invented the CEO pseudonym โ€œGary Norden,โ€ and that Radaris also had issued multiple press releases over the years that quoted the fake CEO while seeking money from potential investors.

Attorneys for Radaris waited until the last minute to appear in court and contest what was all but certain to be a default judgment in favor of the plaintiffs, and then told the court that Atlas had failed to serve the real owners and operators of Radaris and several of its sister data broker companies.

Atlas re-filed the lawsuit in June 2025, this time dramatically expanding the number of Radaris family data brokers accused of violating Danielโ€™s Law. Matt Adkisson, president and CEO of Atlas, said Radaris turned to a tried-and-true playbook: Delaying in court until the last possible minute, and playing shell games with Radarisโ€™s true country of origin and the individuals listed as owners and operators of these sites.

โ€œWe refer to this period as their island-hopping phase. Privacy policies changed constantly, and new entities kept appearing from places like the Marshall Islands, the British Virgin Islands, and Seychelles,โ€ Adkisson told KrebsOnSecurity. โ€œBehind the scenes, it felt like a shell game. Defense lawyers told the court that certain entities merely operated the domains and were the proper parties to sue. But by the time a judgment neared, those entities would be discarded and new entities would appear. Meanwhile, the lawyers claimed the other entities that actually owned the domains should not be held responsible.โ€

Adkisson said when the defendants updated their terms of service to state that Radaris was suddenly managed by a company in the Marshall Islands, Atlas hired an investigator in that country and soon learned the brand new entity that Radaris claimed was managing the company didnโ€™t even exist yet.

Mr. Gurvits stepped forward as Radarisโ€™s attorney in a class action lawsuit the company temporarily lost in 2017 because it never contested the claim in court. When the plaintiffs told the judge they couldnโ€™t collect on the $7.5 million default judgment, the court ordered the domain registry Verisign to transfer the radaris.com domain name to the plaintiffs.

Mr. Gurvits appealed that verdict, arguing the lawsuit hadnโ€™t named the actual owners of the Radaris domain name โ€” a Cyprus company called Bitseller Expert Limitedย โ€” and thus taking the domain away would be a violation of their due process rights.

The judge in the 2017 case ruled in Radarisโ€™ favor โ€” halting the domain transfer โ€” and told the plaintiffs they could refile their complaint. Soon after, the operator of Radaris changed from Bitseller to Andtop Company, an entityย formedย (PDF) in theย Marshall Islands in Oct. 2020. The plaintiffs never re-filed their lawsuit.

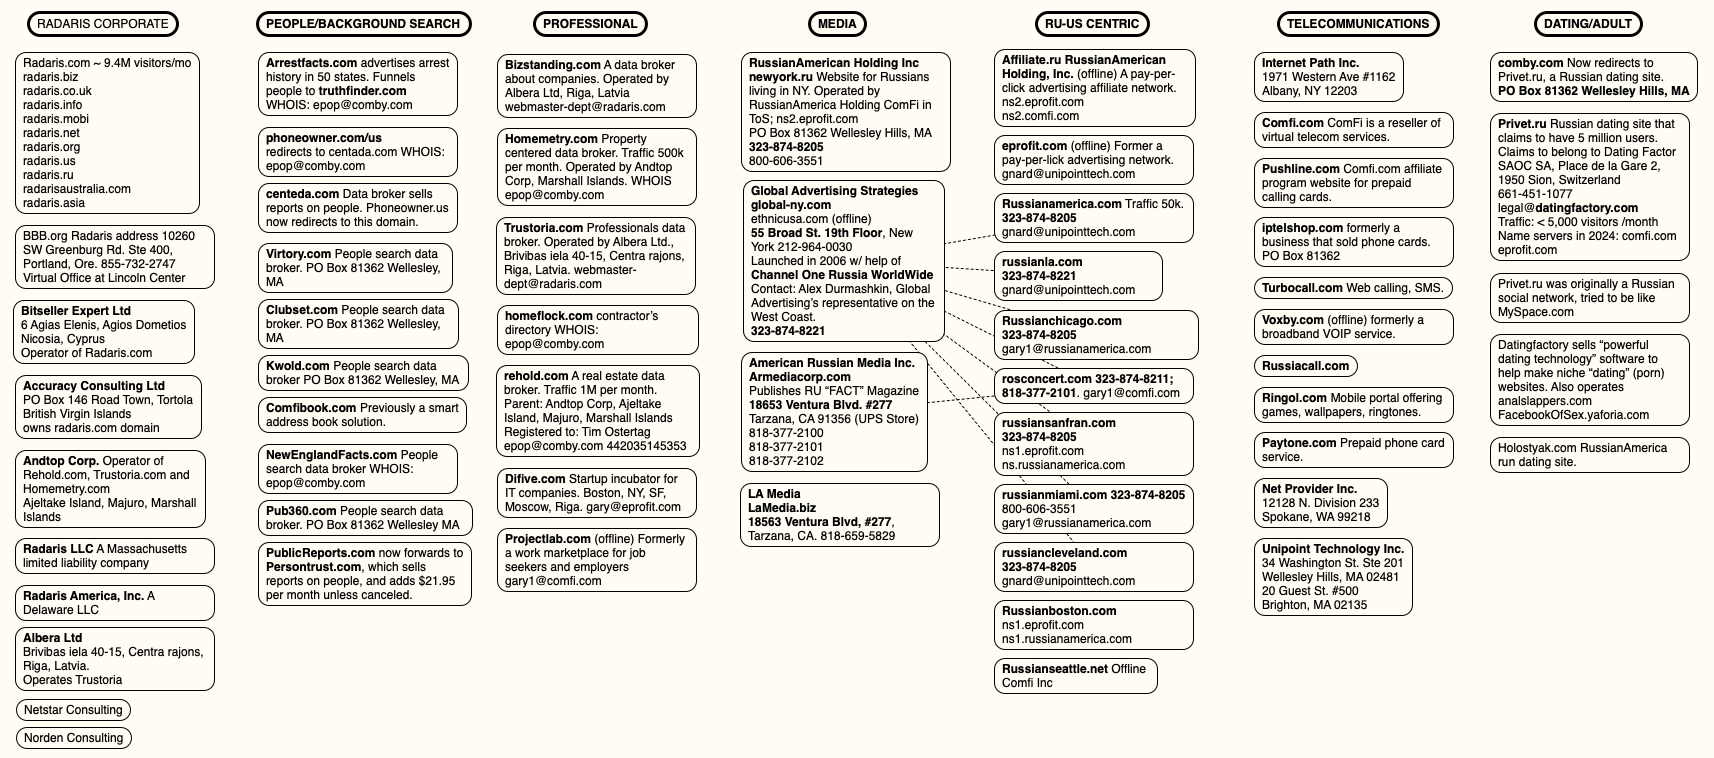
A mind map of various entities tied to Radaris and the companyโ€™s co-founders. Click to enlarge.

โ€œThat seemed to be their modus operandi,โ€ said Raj Parikh, a partner at PEM Law in New Jersey who handles most of the Danielโ€™s Law litigation for Atlas. โ€œIn the past, they won by attrition. Plaintiffsโ€™ attorneys tired of the procedural games and just gave up. That strategy worked for a decade, and it probably would have worked in this case too, since any financial recovery from foreign actors will be difficult. But we were acutely aware of the threat this website posed to law enforcement officers and other public officials in New Jersey, and decided early on to commit whatever time and resources were necessary to remove that threat.โ€

On August 26, the judge in the New Jersey case found the defendants were given multiple chances to appear and defend the claims against them but had failed to do so. Mr. Gurvits declined to comment on the case, saying it had been assigned to another attorney, a Mr. Victor Worms. In response to questions, Mr. Worms asserted the New Jersey court transferred Radaris.com to Atlas as part of a default judgment against Radaris.com, which is not a legal entity.

โ€œWe have made a motion to vacate that default judgment on the grounds that it is void since a non-entity has no legal capacity to sue or be sued,โ€ Worms replied. โ€œWe also intend to pursue all appropriate appeals because we believe the transfer of Radaris.com amounts to a forfeiture in violation of various constitutional principles.โ€

While radaris.com still comes up prominently in results when searching online for U.S. residents by name, the domain no longer sells detailed personal dossiers on millions of Americans. Its homepage now displays a notice from Atlas, as well as links to our previous reporting on Radaris.

EMAIL CONFIRMATIONS

Atlas told KrebsOnSecurity that it has obtained more than 10,000 emails and documents in the course of litigation, and that those messages confirm our previous reporting on the owners and operators of Radaris and its myriad companies.

Atlas said the emails clearly establish that the nominal legal vehicles โ€” Radaris America, Inc.; Bitseller Expert Limited; Digital Orbit Corp; Core Solutions Group Inc; Lucky Solutions Inc; Virtura Corp; Veripages Inc.; Nuform Solutions Inc.; Growth Data Advisors Inc.; Property Experts, Inc โ€” are all administered by the same three or four people from the same mailboxes, share one bank or payment card set, and are all managed from one virtual office address.

โ€œThe corpus establishes, with documentary evidence generated independently by banks, payment processors, hosting providers, registrars, software-as-a-service vendors and the operatorsโ€™ own systems, that radaris.com and at least twenty-five other people-search websites are one operation run by a small Boston-area group whose administrative, financial and technical functions sit on the difive.com mail domain and its successors (centerex.com, scienteco.com, eprofit.com, realmo.com, pub360.com),โ€ reads a summary shared by Atlas.

Atlas said the emails show Radaris.com earns approximately $42,000 a month, while Veripages.com earns around $45,000 monthly via its partnership with the Lifetime Value Company, a marketing and advertising firm whose brands include PeopleLooker, PeopleSmart, NumberGuru, and Bumper, a car history site.

According to Atlas, the emails also showed the Radaris family of websites earns as much as $25,000 each month from their partnership with Onerep, a company that claims to help people remove their information from people-search sites. In March 2024, KrebsOnSecurity revealed how the Belarusian founder of Onerep had launched and operated dozens of people-search sites over the years and was continuing to operate one of them (Nuwber), effectively spreading the disease and selling the cure.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

All told, the New Jersey court has so far transferred 14 domain names from the Radaris family of companies to Atlas. Radaris.com now redirects to a notice of the court-ordered domain transfer.

THE ROAD AHEAD

The Radaris family of companies is still potentially facing fines of $1,000 per alleged violation of Danielโ€™s Law. For the time being, however, Danielโ€™s Law is facing a constitutional challenge from virtually all of the 150 other consumer data broker firms being sued by Atlas.

The data broker industry responded by having at least 70 of the Atlas lawsuits moved to federal court, challenging the New Jersey statute as overly broad and a violation of the First Amendment. The U.S. Court of Appeals for the Third Circuit has not yet issued a decision on the constitutional challenge, but either way the case is widely expected to be appealed all the way to the U.S. Supreme Court.

Meanwhile, at least 14 other states have now passed laws modeled after the New Jersey statute, with more states considering similar measures. However, West Virginiaโ€™s Danielโ€™s Law was ruled facially unconstitutional under the First Amendment by a federal district court in August 2025.

Justin Sherman is a privacy expert and author of the forthcoming book โ€œThe Middlemen,โ€ which examines how the data broker industry powers modern surveillance. Sherman said federal lawmakers have long faced intense lobbying by the technology industry against more restrictive U.S. data privacy laws, but that many powerful industries are now working against passing comprehensive data privacy legislation.

โ€œThese days at the federal level, add in the intense amount of lobbying against these laws from social media companies, big tech, cryptocurrency firms, and now AI proponents in the mix who claim that limiting their data scraping is somehow going to collapse the whole U.S. economy under Chinese rule,โ€ he said.

Sherman said people-search companies will continue to thrive unless and until Congress enacts meaningful consumer privacy and data protection laws that are relevant to life in the 21st century. Thatโ€™s because virtually all state privacy laws exempt records that might be considered โ€œpublicโ€ or โ€œgovernmentโ€ documents, including voting registries, property filings, marriage certificates, motor vehicle records, criminal records, court documents, death records, professional licenses, bankruptcy filings, and more.

At least 25 states have passed or implemented laws requiring age verification for residents seeking to access adult content online, but there is no federal law that limits how the companies that are scanning everyoneโ€™s drivers license can use, share or keep the data provided. Had such restrictions been enshrined in law, we may have avoided the recent breach at IDScan.net, which exposed the drivers license information on more than 153 million Americans when the records were briefly turned into a point-and-click identity theft service on the dark web.

โ€œThe average person can look at Danielโ€™s Law and have a perfectly normal reaction, which is that everyone should be covered, not just police and judges,โ€ Sherman said. โ€œBut we donโ€™t need more wake-up calls. Weโ€™ve had eight million wake-up calls already on the need for better privacy laws. The lack of comprehensive federal privacy law is not for a lack of knowledge, and anyone claiming otherwise is either not reading the news or kidding themselves.โ€

220 Million Traveler Records Exposed In Vietnam-Linked APIS Leak

By: BeauHD
13 September 2026 at 22:34
A misconfigured Advance Passenger Information System (APIS) database linked to Vietnam exposed more than 220 million passenger and crew travel records spanning 2017 to 2026, including names, passport numbers, nationalities, flight details, seat assignments, and baggage references. Researchers said the database was reachable through a chain of security mistakes and default credentials. It was later secured after the disclosure, but it's unclear whether the data had already been copied or abused. BleepingComputer reports: Kinryu Labs discovered the Elasticsearch cluster on June 3 while surveying exposed databases as part of research into ransomware activity. The cluster, named 'pax-info', contained 29 indices and roughly 107 GB of data. Its two principal indices held 210,318,069 passenger records and 10,465,631 crew records, for a combined 220,783,700 entries. According to Kinryu Labs, the cluster was hosted in Viettel-assigned IP space in Hanoi. BleepingComputer could not confirm which Vietnamese organization operated the system. The exposed information included passengers' and crew members' names, dates of birth, sex, nationalities, passport or travel-document numbers, document expiration dates, and issuing countries. Associated travel data included flight numbers and dates, airlines, departure, destination and transit airports, seat assignments, baggage references, and scheduled, estimated, and actual flight times, information typically carried by APIS and related airline systems. Sample records reviewed by BleepingComputer included travelers of Korean, Chinese, Canadian, and New Zealand nationality, among others. While the researchers could not provide a complete breakdown by nationality, the data covered numerous international airlines across Asia-Pacific, Europe, and the Middle East. As a result, the exposed records could relate to people from virtually anywhere who visited or transited through Vietnam over the nine-year period. Kinryu Labs expects to publish additional details on its blog later this week.

Read more of this story at Slashdot.

Flock Worker Calls Police On Reporter - For Filming Them in Public

13 September 2026 at 09:00
"This is what happened when we tried to record Flock installing a new camera on public roads," says Emmy award-winning reporter Brendan Keefe in a new video for InvestigateTV. In an accompanying article, InvestigateTV says their reporter "parked on the public street at a distance, donned a yellow safety vest and a hat emblazoned with the logo of InvestigateTV's Atlanta affiliate where he also works, displayed a press placard on his dashboard and then pulled out a camera to record the installation.... The installer saw him and immediately packed up his equipment and drove away, so Keefe also returned to his car and followed several cars behind, hoping to document the next stop." And then Flock's technician called 911. When asked "What's the address of your emergency" Flock's technician answered "I'm getting followed โ€” harassed, pretty much. Taking videos and pictures!" Flock's worker said they'd been harassed multiple times that day, then stated incorrectly that "I know for a fact" that that was what the reporter wanted to do too. InvestigateTV reports that as a result of the Flock technician's call, "Three police cars ended up in the national investigative reporter's rearview mirror that Wednesday afternoon." Keefe told one of the three police officers who pulled him over, "There is an irony here that they're setting up these cameras that track all of our movements, that follow everywhere we go. But when I try to get video in public of him in public setting up a camera, he's afraid I'm following him?" InvestigateTV also reports that "About 17 minutes after the stop began, the responding officers returned to their vehicles and Keefe was allowed to drive away." But the call that brought three police cars to their reporter "was not the first time this summer someone working for Flock Safety summoned police over a camera. " About 17 minutes after the stop began, the responding officers returned to their vehicles and Keefe was allowed to drive away... [But the stop] was not the first time this summer someone working for Flock Safety summoned police over a camera. On June 5, police in Smyrna, Georgia, responded to a 911 call from a Flock employee after a group of YouTube creators began filming outside the company's distribution center located in the Atlanta suburb... The caller claimed the group filming had "been driving around the perimeter, basically harassing everyone" working at the facility. "Three young white males, probably mid-twenties, I'm not sure if they're armed. And they're carrying filming equipment as well," the caller said. Three times during the call he raised the possibility the people filming might be armed, though, when asked, he told the dispatcher he had not seen any weapons... [One of the protesters later told the caller "I think it's interesting, when you guys have this happen, you call the police and make us get stopped. But then you do it and it's okay?"] No one was charged in the YouTuber group, though the individuals were ordered to leave the premises under an official trespass warning. Keefe's video report ends with one final irony. "Every day on my way to work, I'm captured again by those same new shiny Flock cameras. We tried watching the watchers. Turns outs, it's a lot easier for them to watch us." Flock responded to the report by claiming "We do not object to members of the public or press photographing Flock cameras or personnel in public." But they added that employees working "in the field" must "prioritize their safety" and "may contact law enforcement when they believe they are being threatened, harassed, followed, or otherwise face a safety concern."

Read more of this story at Slashdot.

LG Responds to TV Spying Allegations

By: BeauHD
12 September 2026 at 13:00
LG is pushing back against reports that its smart TVs are "spying" on users, saying wake-word detection happens locally and that features such as Automatic Content Recognition, voice recognition, and interest-based ads are optional. But critics note that researchers found TVs keeping logs of ambient conversations, and LG's response "did not address broader concerns about how much data it collects, who it shares it with, the potential for bad actors to exploit its features, or the misleading way in which its privacy options are presented," reports The Verge. Here's an excerpt from LG's statement: Some recent media coverage may have contributed to misconceptions about how LG smart TVs work. As an industry leader, LG believes we have a responsibility to provide customers with clear and accurate information about how our smart TVs operate and the privacy controls available to them. We would like to clarify how our smart TVs operate and explain our approach to user privacy. LG smart TVs do not continuously record or transmit users' conversations. Speech-to-text processing begins only if a user activates a voice interaction through a supported wake-word feature or by pressing the voice (or AI) button on the remote control. Audio used for wake-word detection is processed locally on the TV and, if no wake word is detected, audio is not converted to text, stored, or transmitted. Voice-recognition results and related technical logs may be generated as part of processing a voice command. These records are associated with specific voice interactions and do not indicate continuous recording of conversations occurring outside an active voice recognition session. Speech-recognition results may be used to support voice-related features but are not uploaded later when the TV is offline or when connectivity is restored. Features such as Automatic Content Recognition (ACR), voice recognition, and interest-based advertising are optional. These features are not enabled by default. Users can choose to enable these features and can manage or withdraw consent through TV settings. ACR uses audio fingerprinting technology using the TV's internal audio processor (not a speaker) to identify content and does not collect screenshots, screen recordings, video recordings, voice recordings, or other audio recordings from the TV. Where ACR is available and enabled, ACR-related information may be used for audience segmentation and viewing or audience trend analysis. Interest-based advertising and cross-device advertising require separate user consent through the applicable advertising-related agreements. Protecting user privacy is a fundamental principle in the design and operation of LG products and services. The statement goes on to "provide additional details on how LG smart TV features work, how information may be processed, what choices users have, and how LG continues to strengthen privacy, transparency, and security."

Read more of this story at Slashdot.

Florida says motor vehicle data breach tied to credentials stolen from officerโ€™s personal device

11 September 2026 at 16:00
The Florida Department of Motor Vehicles confirmed a data breach claimed by the cybercrime group ShinyHunters, saying it originated with the theft of credentials stored on a police officer's personal device.

Latest Apple Watch Can Grab Snippets of Conversation Without Both Speakers' Consent

By: BeauHD
10 September 2026 at 19:00
Apple's new Audio Intelligence features for the Apple Watch Series 12 are drawing privacy concerns because they can process nearby conversations without explicit consent from everyone involved. "Live Rewind lets you instantly see the last 15 seconds of a conversation as text," Apple explains in its technical summary (PDF). "Siri Recap summarizes conversations throughout your day and produces high-level Apple Intelligence-generated notes so you can stay present in the moment and catch up later." The Register reports: The latest Apple Watch comes with Audio Intelligence, a set of AI audio processing capabilities tuned for the company's S11 chip. Its features include: Sound Recognition, Music Recognition with Shazam, Live Rewind, and Siri Recap. [...] With the double-press of the Digital Crown -- as Apple grandly refers to the button on its Watch -- Live Rewind takes in an audio stream from the Watch microphone, processes it in a Secure Exclave on the S11 chip, and routes the data to the user's nearby iPhone, which runs a speech-to-text algorithm on the 15-second audio segment. The resulting text is saved and the audio is discarded. The wearer's Watch emits an audible tone, even in silent mode, to alert those in the vicinity and provides a visual cue for those able to see the face of the device. Nonetheless, bystanders alerted to the recording -- to the extent they recognize the meaning of the tone -- have not consented to being recorded, which is a legal requirement in 11 US states that have all-party consent laws. Apple characterizes its implementation of brief eavesdropping as respectful of personal privacy. It makes that claim in a section titled, "How Live Rewind respects those around you," citing the audible chime and visual on-screen animation. Siri Recap, meanwhile, "summarizes conversations throughout your day and produces high-level Apple Intelligence-generated notes so you can stay present in the moment and catch up later." This too, Apple describes as an act of respect. "By design, Siri Recap does not create a recording, does not produce a verbatim transcript, and does not identify and attribute speakers," Apple's technical documentation explains. "The output is a brief, high-level summary, comparable to notes a person might write after a conversation. There is no audible signal because no raw audio is retained, and there is no way to reconstruct the original audio from a Siri Recap or share raw audio with anyone."

Read more of this story at Slashdot.

Android Rolling Out Passkey Transfers Between Password Managers

By: BeauHD
10 September 2026 at 17:00
Android is rolling out a system-level way to securely transfer passwords and passkeys between credential managers, eliminating the need to export passwords as unencrypted text files or manually recreate passkeys. The feature initially supports Google Password Manager, 1Password, Bitwarden, and Dashlane, with other providers able to integrate through Android's Credentials Transfer API. 9to5Google reports on how to initiate the system-backed transfer method: 1. Start the move: Open your new password manager app and choose the option to import or copy your passwords and passkeys from another provider. The password manager will then hand the task over to Android. 2. Let Android securely coordinate the data transfer: Android will automatically detect existing password managers on your device and show you which you can import from. 3. Review and authorize: Once you tap "Continue," Android will bring you to your existing password manager to select, review, and authorize the transfer. Then your data will be quickly and securely transferred between the apps in just a few seconds.

Read more of this story at Slashdot.

FTC rescinds policy statement requiring health apps to notify customers after a breachย 

By: djohnson
9 September 2026 at 15:18

The Federal Trade Commission has rescinded a Biden administration-era policy statement that asserted coverage over health and fitness apps under federal data breach notification regulations.

In a half-page statement posted Wednesday, the FTC said it โ€œhas determined that the statement โ€“ contentious at the time of issuance โ€“ provided minimal benefit and has been superseded by rulemaking.โ€ The commission said the statementโ€™s withdrawal also aligns with guidance from the White House to pursue a deregulatory agenda and avoid โ€œunnecessary use of subregulatory guidance.โ€

Unlike a formal regulation, which carries the legally binding force of law created through a public rulemaking process, an agency policy statement is non-binding guidance that merely outlines how officials intend to interpret and enforce existing statutes. An FTC spokesperson told CyberScoop that the underlying policy including health apps remains codified through a regulatory update in 2024.

โ€œEach of these reasons is independently sufficient to support the Commissionโ€™s decision to rescind this policy statement,โ€ the FTC continued. โ€œParties understand that guidance generally creates neither substantive rights nor binding obligations.โ€

The initial policy statement, passed in a divided 3-2 vote during the Biden administration under then-FTC chair Lina Khan, asserted that health apps, fitness trackers and other connected devices were covered under an existing regulation requiring companies to disclose health-related data breaches to customers.

The interpretation targeted any โ€œvendor of personal health records that contain individually identifiable health information created or received by health care providers.โ€ Many health and fitness apps ask users to upload medical records and other health-related data in order to function effectively.

More recently, health and cybersecurity experts have pointed to similar regulatory gaps that exist for AI companies that make healthcare specific models that can answer questions, examine patient records and dispense medical advice to users.

The underlying Health Breach Notification Rule also triggers automatic notification when a covered entity suffers a breach of security, which can include both standard breaches and data losses as well as the disclosure of sensitive health information to third parties without usersโ€™ authorization. That would potentially put health apps on the hook for selling customer data to third-party data brokers and other entities-a standard formally codified in a binding 2024 FTC rule update.

A Sept. 2021 statement by the FTC justifies its interpretation by citing digital security and privacy provisions in the 2009 American Recovery and Reinvestment Act as well as gaps in major health privacy laws like the Health Insurance Portability and Accountability Act that allow such apps to handle and store sensitive personal health records or data without being subject to the same breach notification requirements as other health care organizations.

The FTC said it intended to enforce health apps under the law and subject violators to daily fines of $43,792 per violation.

โ€œAs many Americans turn to apps and other technologies to track diseases, diagnoses, treatment, medications, fitness, fertility, sleep, mental health, diet, and other vital areas, this Rule is more important than ever,โ€ the FTC said in 2021. โ€œFirms offering these services should take appropriate care to secure and protect consumer data.โ€

This week, the FTC voted unanimously to rescind the policy statement. But that unity is in part because President Trump fired Democratic FTC commissioners who voted in favor of the original rules, while advancing party allies as their replacements.

The two dissenting votes against the policy statement in 2021 were from Republican-appointed commissioners casting their dissents under a Democratic executive. Andrew Ferguson, a Republican commissioner nominated by former Democratic President Joe Biden, is now chair of an FTC filled entirely with Republican appointees, and has defended President Trumpโ€™s authority to fire and hire new commissioners at-will.

Update, 9/11/26, 4:15 p.m.: This story has been updated to clarify the impact of the FTCโ€™s policy statement revision.

The post FTC rescinds policy statement requiring health apps to notify customers after a breachย  appeared first on CyberScoop.

โŒ
โŒ