❌

Reading view

There are new articles available, click to refresh the page.

A bold new strategy or a dangerous precedent? Experts are divided on Trump’s memo.

A newly-signed presidential memorandum enlisting private sector companies in federal law enforcement hacking operations against criminal organizations could present a number of legal, practical and moral pitfalls, cyber experts told CyberScoop a day after the order was released.

While some have celebrated the memo as an overdue maneuver to more aggressively combat cybercriminals, others view it as risky at best and potentially destructive at worst. Supporters, critics and everyone in between also said that how it plays out could be decided in the 60-day timeframe the memo sets to establish the program.

But ultimately, “it’s a massive shift in the cyber policy community,” said Michael Garcia, a former top official at the Cybersecurity and Infrastructure Agency. “This is a philosophical shift.”

The Concerns

On the most critical end of the spectrum is security consultant Davi Ottenheimer, who has been a proponent of concepts like “hack back” or “active defense” that envision a bigger role for the private sector. But he was unsparing in his criticism of the Trump memo. 

“It’s an embarrassment to America,” he told CyberScoop. “It’s like seeing somebody strapped onto a horse backwards, looking at the wrong end of a rifle.”

The Trump memo’s approach has been likened to the “letters of marque” concept used in early U.S. history, when it authorized sea privateers to attack and capture enemy ships and goods on behalf of the country. But Ottenheimer, founder of Ottenheimer GmbH, noted that the practice fell out of favor for good reason in the 1800s because of the violence it unleashed and how it contributed to mercenarism.

Additionally, the memo raises a number of targeting-related issues, he said. Ottenheimer is concerned about Trump’s intentions. The memo specifically pertains to the use of participating companies against transnational criminal organizations.

“Left-wing opposition, liberals, anti-fascists —they’re all criminals to him,” Ottenheimer said. “So to authorize attacking criminals under this means private organizations can go hack people that he designates as criminals.”

Under the memo, the program must establish legal and constitutional procedures for the prior approval of the targeting of U.S. citizens, as well as develop procedures to halt any unintentional targeting of U.S. people or systems. 

However, the limitation on targeting criminals only creates a perverse incentive for attackers and a peculiar defense for anyone who’s attacked, Ottenheimer said.

He envisioned a scenario for a company participating in the program where “you’re hacking [a target], and they go, ‘Hey, we’re the state.’ And then [private companies] are like, ‘Oh, I can’t hack you anymore.’ Boom. They decided when you can and can’t hack.”

Furthermore, “you incentivize people to know as little as possible so [operations] can be authorized,” he said.

The memo raises ethical concerns for him as well: “You can’t attack somebody and then say it’s your fault that you didn’t notify them you didn’t want to be attacked.”

“There’s no notice for you being designated. There’s no prevention of you being designated. There’s no way for you to know you’re being designated,” Ottenheimer said. “That’s like a person sitting down next to you and smoking a cigarette and blowing smoke in your face and saying, ‘Hey, you got to say you don’t like cancer if you don’t want me to do this to you right now.’”

Garcia, now vice president of the cybersecurity practice at Monument Advocacy, said he supports some of the ideas of the memo, but worries about how it will be executed.

“It comes down to attribution, and if you make a risky bet on who we’re attributing [attacks] to, that’s where things can get dicey,” Garcia told CyberScoop.

There could be pressure to attribute faster, which could perhaps lead to lower certainty about who’s being targeted, and that in turn could lead to a private sector company accidentally attacking a foreign government, he said.

That raises legal questions: “It’s in the Constitution —the federal government has the ability to wage war. And there are laws by which private citizens can’t take up arms,” Garcia said.

He wanted the memo to include court oversight of the program, similar to what’s been required for private sector takedown operations. .

Garcia also isn’t sure whether there will be a big enough pool of companies willing to jump into offensive cyber operations.

“From the lawyer perspective, it’s, ‘Are you okay with engaging in this kind of legal risk? And who knows what protections the government will provide?’” he said. “I’d be very curious to see what the foreign governments’ reactions are — ‘We’re going to cut ties with any participating company that engages in this.’”

Errata Security CEO Robert Graham wrote that under the program, companies “are not willy-nilly hacking back,” given the federal supervision elements. “Though, I wonder if it doesn’t eventually morph into law enforcement saying ‘Stop bothering us, just do what you think is best.’’” 

The Case For

The Trump administration and the memo’s supporters  have touted it as a means to put the United States on stronger ground in cyberspace. 

Amanda Naylor, the director of cyber policy at the National Security Council who worked on the memo, said on LinkedIn that it was designed “to bring the capabilities, speed, and innovation of the American private sector into the fight against transnational cybercrime and fraud.”

Former Trump White House cybersecurity official Joshua Steinman said he views the memo as a step toward “parity,” given how U.S. adversaries operate in cyberspace.

“The Chinese and the Russians do this at scale, and I guarantee you they have very few limiting tools when they do it,” said Steinman, now founder of the security firm Gavalnick. “It opens up an entire workforce that allows us to go out and achieve strategic objectives.”

The restrictions in the memo are important, he told CyberScoop.

“The most sensitive things are going to continue to be done by the uniformed and authorized civilian workforces, but there’s a lot of low-hanging fruit,” i.e., criminal organizations, Steinman said. He doesn’t have any fear of the program overstepping as a result.

“We operate like a Boy Scout in cyberspace,” he said. “It’s measured and reasoned.” He compared it to the Right to Try Act for medications.

He also said he expects to see a lot of interest in participating in the private sector.

Ari Redbord, global head of policy at TRM Labs, praised the memo too, calling it “a huge step toward empowering the private sector at a critical moment” that “has a real opportunity to be truly transformative.”

“Scammers are using AI to move with unprecedented speed and scale, stealing billions in life savings from average Americans and small businesses,” he said. “The private sector holds the data. The public sector holds the authorities. This [memo] puts them together.”

What’s Next

The coordination center charged with establishing the program under the memo has 60 days to complete its work. That process could determine a lot. Graham noted that the memo has a classified annex, too.

The memo as written is quiet about what becomes of any seized assets, Graham noted. Redbord raised the same topic as one of his questions about execution of the memo. 

“What government direction and control looks like in the middle of a live operation,” he said in listing his questions. “How disruption turns into actual dollars back in victims’ pockets, and whether we can build a true victim compensation fund as part of this program. What happens when an operation touches a third country with its own laws and its own interests. And how success gets measured, in money recovered and networks dismantled.”

Will Barker, cybersecurity adviser at Huntress, said what’s next could be key.

“The 60-day implementing guidance is where the real substance lives,” he said in a written quote. “Minimum standards, operational procedures, the adjudicatory framework for target selection.”

The post A bold new strategy or a dangerous precedent? Experts are divided on Trump’s memo. appeared first on CyberScoop.
Alleged Kimwolf Botmaster ‘Dort’ Arrested, Charged in U.S. and Canada

Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. KrebsOnSecurity publicly named the suspect in February 2026 after the accused launched a volley of DDoS, doxing and swatting campaigns against this author and a security researcher. He now faces criminal hacking charges in both Canada and the United States.

A criminal complaint unsealed today in an Alaska district court charges Jacob Butler, a.k.a. “Dort,” of Ottawa, Canada with operating the Kimwolf DDoS botnet. A statement from the Department of Justice says the complaint against Butler was unsealed following the defendant’s arrest in Canada by the Ontario Provincial Police pursuant to a U.S. extradition warrant. Butler is currently in Canadian custody awaiting an initial court hearing scheduled for early next week.

The government said Kimwolf targeted infected devices which were traditionally “firewalled” from the rest of the internet, such as digital photo frames and web cameras. The infected systems were then rented to other cybercriminals, or forced to participate in record-smashing DDoS attacks, as well as assaults that affected Internet address ranges for the Department of Defense. Consequently, the DoD’s Defense Criminal Investigative Service is investigating the case, with assistance from the FBI field office in Anchorage.

“KimWolf was tied to DDoS attacks which were measured at nearly 30 Terabits per second, a record in recorded DDoS attack volume,” the Justice Department statement reads. “These attacks resulted in financial losses which, for some victims, exceeded one million dollars. The KimWolf botnet is alleged to have issued over 25,000 attack commands.”

On March 19, U.S. authorities joined international law enforcement partners in seizing the technical infrastructure for Kimwolf and three other large DDoS botnets — named Aisuru, JackSkid and Mossad — that were all competing for the same pool of vulnerable devices.

On February 28, KrebsOnSecurity identified Butler as the Kimwolf botmaster after digging through his various email addresses, registrations on the cybercrime forums, and posts to public Telegram and Discord servers. However, Dort continued to threaten and harass researchers who helped track down his real-life identity and dramatically slow the spread of his botnet.

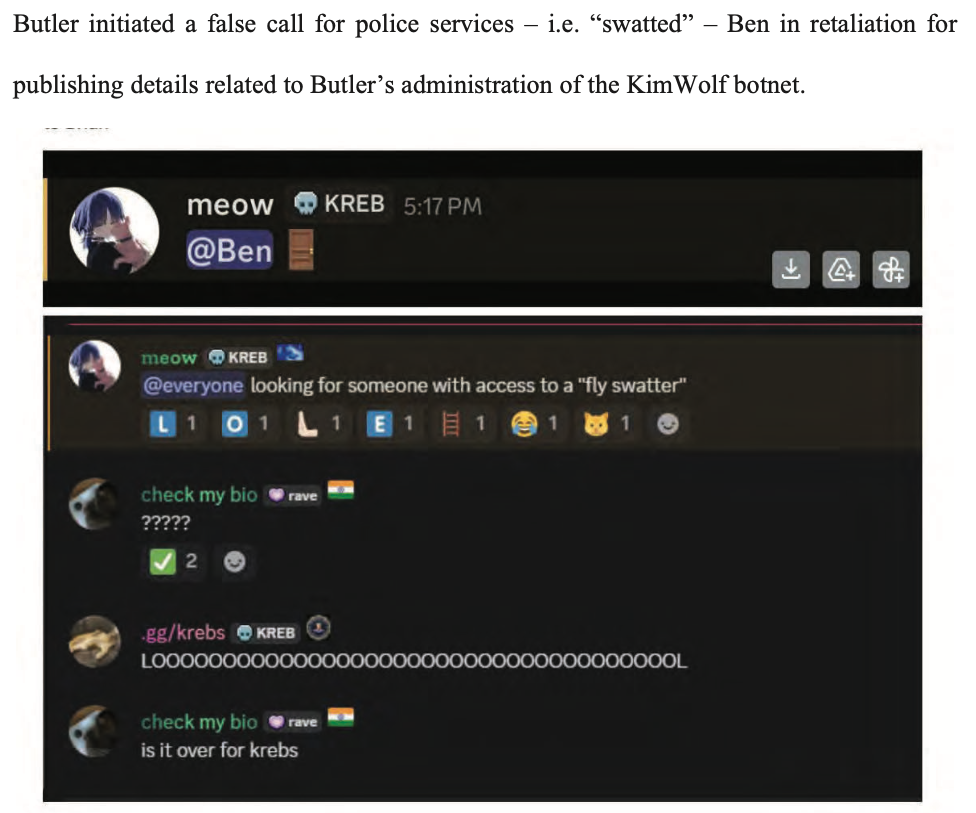
Dort claimed responsibility for at least two swatting attacks targeting the founder of Synthient, a security startup that helped to secure a widespread critical security weakness that Kimwolf was using to spread faster and more effectively than any other IoT botnet out there. Synthient was among many technology companies thanked by the Justice Department today, and Synthient’s founder Ben Brundage told KrebsOnSecurity he’s relieved Butler is in custody.

“Hopefully this will end the harassment,” Brundage said.

An excerpt from the criminal complaint against Butler, detailing how he ordered a swatting attack against Ben Brundage, the founder of the security firm Synthient.

The government says investigators connected Butler to the administration of the KimWolf botnet through IP address, online account information, transaction records, and online messaging application records obtained through the issuance of legal process. The criminal complaint against Butler (PDF) shows he did little to separate his real-life and cybercriminal identities (something we demonstrated in our February unmasking of Dort).

In April, the Justice Department joined authorities across Europe in seizing domain names tied to nearly four-dozen DDoS-for-hire services, although because of a bureaucratic mix-up the list of seized domains has remain sealed until today. The DOJ said at least one of those services collaborated with Butler’s Kimwolf botnet.

A statement from the Ontario Provincial Police said a search warrant was executed on March 19 at Butler’s address in Ottawa, where they seized multiple devices. As a result of that investigation, Butler was arrested and charged this week with unauthorized user of computer; possession of device to obtain unauthorized use of computer system or to commit mischief; and mischief in relation to computer data. He is scheduled to remain in custody until a hearing on May 26.

In the United States, Butler is facing one count of aiding and abetting computer intrusion. If extradited, tried and convicted in a U.S. court, Butler could face up to 10 years in prison, although that maximum sentence would likely be heavily tempered by considerations in the U.S. Sentencing Guidelines, which make allowances for mitigating factors such as youth, lack of criminal history and level of cooperation with investigators.

Bypassing WAFs Using Oversized Requests

Many web application firewalls (WAFs) can be bypassed by simply sending large amounts of extra data in the request body along with your payload. Most WAFs will only process requests up to a certain size limit. How the WAF is configured to handle these large requests determines exploitability, but some common WAFs will allow it by default.

The post Bypassing WAFs Using Oversized Requests appeared first on Black Hills Information Security, Inc..

Getting Started with NetExec: Streamlining Network Discovery and Access

One tool that I can't live without when performing a penetration test in an Active Directory environment is called NetExec. Being able to efficiently authenticate against multiple systems in the network is crucial, and NetExec is an incredibly powerful tool that helps automate a lot of this activity.

The post Getting Started with NetExec: Streamlining Network Discovery and Access appeared first on Black Hills Information Security, Inc..

Impacket Defense Basics With an Azure Lab 

Jordan Drysdale // Overview The following description of some of Impacket’s tools and techniques is a tribute to the authors, SecureAuthCorp, and the open-source effort to maintain and extend the code. […]

The post Impacket Defense Basics With an Azure Lab  appeared first on Black Hills Information Security, Inc..

BHIS Webcast: Tracking Attackers. Why Attribution Matters and How To Do It.

In this BHIS webcast, we cover some new techniques and tactics on how to track attackers via various honey tokens.  We cover how to track with Word Web Bugs in ADHD and […]

The post BHIS Webcast: Tracking Attackers. Why Attribution Matters and How To Do It. appeared first on Black Hills Information Security, Inc..

WEBCAST: Stop Sucking at Wireless

Jordan Drysdale & Kent Ickler// Jordan and Kent are back with more blue team madness! The shameless duo continue their efforts to wrangle decades old attacks against wireless networks. The […]

The post WEBCAST: Stop Sucking at Wireless appeared first on Black Hills Information Security, Inc..

WEBCAST: Proper Active Defense and the New ACDC Active Defense Law

John Strand// In this webcast John talks about the new ACDC law and what it means exactly. There has been quite a bit of anger and great GIFs about hacking […]

The post WEBCAST: Proper Active Defense and the New ACDC Active Defense Law appeared first on Black Hills Information Security, Inc..

Debating the Active Defense Law.. Because Arguing is Fun

John Strand // I wanted to take a few moments and address the “Hacking Back” law that is working people up. There is a tremendously well-founded fear that this law […]

The post Debating the Active Defense Law.. Because Arguing is Fun appeared first on Black Hills Information Security, Inc..

WEBCAST: CredDefense Toolkit

Beau Bullock, Brian Fehrman, & Derek Banks // Pentesting organizations as your day-to-day job quickly reveals commonalities among environments. Although each test is a bit unique, there’s a typical path […]

The post WEBCAST: CredDefense Toolkit appeared first on Black Hills Information Security, Inc..

End-Point Log Consolidation with Windows Event Forwarder

Derek Banks // I want to expand on our previous blog post on consolidated endpoint event logging and use Windows Event Forwarding and live off the Microsoft land for shipping […]

The post End-Point Log Consolidation with Windows Event Forwarder appeared first on Black Hills Information Security, Inc..

The CredDefense Toolkit

Derek Banks, Beau Bullock, & Brian Fehrman // Our clients often ask how they could have detected and prevented the post-exploitation activities we used in their environment to gain elevated […]

The post The CredDefense Toolkit appeared first on Black Hills Information Security, Inc..

How to Build Super Secure Active Directory Infrastructure*

CJ Cox // We frequently get requests from customers asking us if we provide consultation defending their systems. The other day I got a question from a customer asking us […]

The post How to Build Super Secure Active Directory Infrastructure* appeared first on Black Hills Information Security, Inc..

How to Configure Distributed Fail2Ban: Actionable Threat Feed Intelligence

Kent Ickler // How to Configure Distributed Fail2Ban: Actionable Threat Feed Intelligence Fail2Ban is a system that monitors logs and triggers actions based on those logs. While actions can be […]

The post How to Configure Distributed Fail2Ban: Actionable Threat Feed Intelligence appeared first on Black Hills Information Security, Inc..

❌