❌

Normal view

There are new articles available, click to refresh the page.
Yesterday — 9 November 2026Security/Privacy

Huawei says it’s made a 100 percent Chinese PC

8 November 2026 at 21:14
Huawei claims it’s built a desktop PC that uses only parts made in CHina. The company launched the Qingyun HM650 last week and said it uses Huawei’s own Kirin X90 processor, a ten-core 20-thread machine with a clock speed of 2.3 GHz. The machine runs a newly developed enterprise version of HarmonyOS, the OS Huawei developed to end its dependence on Android and which it intends to run on most of the devices it makes. A single Chinese government agency has reportedly signed up for 600 of the machines. That’s not an indication this machine is a curiosity, because Beijing has ordered all government entities to shift from Wintel boxes to local alternatives. While Huawei has reportedly claimed local companies manufactured 100 percent of the components in the machine, it is unclear if all those components use Chinese designs. The Register mentions that uncertainty as many non-Chinese companies continue to operate factories in China. Even if Huawei is using some parts that aren’t entirely Chinese, the debut of the Qingyun HM650 is bad news for Intel, AMD, and Qualcomm, as all are suffering as the PC market shrinks due to the rising cost of memory. China’s government is an enormous buyer, and losing the chance to bid for its business is unlikely to be helpful. Japan announces emergency response package after wave of cyberattacks Japan’s government last Friday announced emergency funding to help local organizations strengthen the nation's cyber-defences. The ¥10 billion ($63 million) package follows a wave of cyberattacks that have disrupted railways, retailers, KFC’s logistics provider, and cloud computing operators. The emergency package aims to help Japanese government agencies to use AI to nail infosec basics, and to build tools that let the National Cybersecurity Office aggregate information about cyberattacks. Some funds will also go towards supporting victims. Lenovo’s APAC boss shifts to lead Motorola Lenovo is looking for a new leader of its Asia-Pacific operations after shifting the boss, Amar Babu, to a role as mobile business group general manager and global president at Motorola. Amar led Lenovo in the region for over five years and the company credited him with turning it into “a more balanced and diversified business and a key growth engine.” “Across the portfolio, AP maintained its #1 PC position, while our mobile business achieved notable growth, with Motorola reaching nearly 9 percent market share in India and the #2 smartphone OEM in Japan,” according to a company announcement. “Our infrastructure business achieved profitable growth and nearly double-digit market share, while Solutions & Services continued to strengthen its best-of-breed industry position and significantly increased its advanced services business mix to over 50 percent.” Lenovo has not named a new leader for its APAC outpost. Vietnam hails homegrown USB storage chip Vietnam’s government last week announced the nation’s first domestically-designed security chip - a 28-nanometer device that apparently integrates encryption algorithms in silicon. The chip is already in use on secure USB storage devices that Vietnam’s government employs to store info for government and defense agencies, plus the Communist Party. The nation hopes to use the chips to secure storage of the national digital signature certification system, and critical infrastructure systems in electricity, water, oil and gas, and telecommunications. Hanoi says the chip needs more testing before the government will trust it to protect state secrets, but hailed the chip as an important step towards development of sovereign security capabilities. Apple’s biggest ever education deal Apple last week quietly announced it has won its biggest-ever sale of Macs into the education market in the Philippines. Speaking on the company’s Q4 earnings call, CEO John Ternus said Apple sold 172,000 MacBook Neos to the Department of Education in the Philippines, which will deploy them to teachers and staff. ®

Before yesterdaySecurity/Privacy

Authorities accuse trio of using AI deepfakes to defraud $129M from businesses

6 November 2026 at 12:20

Three men concocted an elaborate, yearslong scheme that defrauded companies of at least $129 million by using AI to impersonate executives and lawyers, tricking targeted victims into transferring large payments to criminal-controlled accounts, the Justice Department said Thursday.

Jacob Soall, Sharon Hazan and Guy Sheetrit allegedly used AI to impersonate the voices and images of chief executive officers at companies and lawyers at major international law firms. The trio are accused of targeting thousands of victims between July 2024 and February 2026, according to court records.

Victims include a U.K.-based financial tech company that lost almost $11.6 million, a Florida-based pet food company that lost $5.2 million, a Missouri-based hospital system that lost $4.8 million, a Massachusetts-based mutual fund company that lost $4.6 million, a California-based hospital system that lost nearly $3 million, a New York-based investment company duped out of $2.8 million, and a Rhode Island-based bank that transferred nearly $2.7 million.

The trio’s scheme typically started by targeting accounting staff, pretending to be the CEO, and requesting help on a financial transaction, officials said. Using AI to create deepfakes pretending to be CEOs, the crew allegedly directed employees to contact attorneys who they would also impersonate to trick the employee into thinking the financial transaction was legitimate.

Prosecutors said the men and their co-conspirators identified and targeted employees who had sufficient authority to authorize large wire transfers. 

The scheme typically began with an email from an e-signature company, wherein the impersonated CEO claimed they were working on a “confidential financial transaction” that required the victim employee to sign a non-disclosure agreement before contacting the purported attorney at a victim law firm, according to an unsealed indictment.

Soall, Hazan, Sheetrit and their co-conspirators allegedly impersonated attorneys at some of the 50 largest law firms globally. 

“Super intelligence technology offers tremendous potential, but the public should recognize that there are some who seek to use this emerging technology to pursue criminal goals,” Jamie McDonald, U.S. attorney for the Southern District of New York, said in a statement. 

Prosecutors said the wire transfers were sent to bank accounts controlled by co-conspirators around the world, including the United States, Spain, Portugal, Greece, the United Arab Emirates, Singapore, Austria, Slovakia and China. The crew allegedly converted the funds to cryptocurrency and distributed the illicit proceeds amongst themselves and their co-conspirators.

Soall, a 41-year-old from Marbella, Spain, was arrested in Spain on June 17. He allegedly primarily impersonated attorneys from the United Kingdom, reading from a handwritten script designed to dupe targeted victims.

Hazan, a 54-year-old from Israel, was arrested in Spain on Aug. 5. He allegedly boasted that he had been laundering money since 1994, including more than $400 million in the past three years, and was previously convicted in the Southern District of New York of conspiracy to commit bank fraud in 2008.

Sheetrit, a 42-year-old from Israel and the United Arab Emirates, was arrested in the United Kingdom on Sept. 7 and allegedly laundered funds from the scheme.

The trio are charged with conspiracy to commit wire fraud, wire fraud, two counts of aggravated identity theft, money laundering conspiracy and two counts of money laundering. The seven counts carry a maximum sentence of 104 years in prison.

“The alleged scheme orchestrated by Soall, Hazan, and Sheetrit demonstrates how the use of advanced technology can be exploited to commit large scale fraud,” James C. Barnacle Jr., assistant director in charge of the FBI New York field office, said in a statement.

“As criminals continue to weaponize emerging technologies, the FBI remains committed to rapidly adapting our capabilities to identify, investigate, and disrupt those who seek to harm New Yorkers and businesses operating in our communities.”

After initial publication of this story, Sheetrit’s attorneys, Sharon Nahari and Shay Shorer, emailed a statement to CyberScoop saying their client “has no connection to this matter and has had no involvement in it whatsoever.”

“Mr. Sheetrit is a businessman with extensive expertise and professional experience in cybersecurity and technology,” wrote Nahari and Shorer. “In the course of his work, he provides professional advisory services to a range of clients. Working in cybersecurity, possessing specialist expertise or providing advisory services cannot, in themselves, establish complicity in or involvement in the alleged conduct.”

“Our client maintains his complete innocence and, like everyone else, is entitled to the presumption of innocence,” the statement continued. “We are confident that, once the facts have been established and the evidence fully examined, it will become clear that there is no basis for holding him criminally responsible.”

UPDATE: Nov. 6, 2026; 8:25 p.m.: This story has been updated to include a statement from attorneys representing Guy Sheetrit.

The post Authorities accuse trio of using AI deepfakes to defraud $129M from businesses appeared first on CyberScoop.

Europol dismantles investment scheme that impacted potential victims in 50 countries

3 November 2026 at 12:02

Authorities arrested seven people allegedly involved in an investment fraud scheme that claimed potential victims in more than 50 countries, Europol said Tuesday. Officials said the operation caused estimated losses of at least $4.5 million. 

The takedown effort involved searches across 17 countries Tuesday and netted the seizure of more than 100 servers, according to Europol.

Officials targeted the scheme run by a company that allegedly provided cybercrime groups a series of trading websites and an assortment of call centers tasked with tricking victims into transferring their savings. 

The company, operated from Cyprus and Israel, was linked to call centers in Albania, Kosovo and North Macedonia, officials said. 

“The scheme promised substantial, quick returns from trading in cryptocurrencies, foreign currencies or stocks,” Europol wrote in a news release. “Behind seemingly legitimate platforms, supposed brokers used fictitious profits and sustained psychological pressure to persuade victims to invest more.”

The investment scam’s operators used affiliate marketing to target potential victims with advertisements that led them to fraudulent investment platforms. Cybercrime groups running the call centers purchased data collected through those ads to contact potential victims, officials said.

Operators duped victims by displaying fictitious profits and pressured victims to transfer large sums of money. “When victims asked to withdraw their money, the operators used delaying tactics to block payments. Eventually, contact ceased, leaving victims unable to recover their funds,” Europol wrote. 

Authorities were tipped off to the investment scam in 2022 when a German couple reported they couldn’t withdraw funds invested in an online trading platform. Authorities arrested two people allegedly involved in the scheme that year and seized evidence that eventually led to further arrests and seizures in 2025.

The joint investigation and takedown effort was supported by officials in Albania, Cyprus, Finland, Germany, Israel, Kosovo, North Macedonia and Poland. The seven people arrested Tuesday, who were not identified, are facing extradition to Germany to face charges, Europol said.

The post Europol dismantles investment scheme that impacted potential victims in 50 countries appeared first on CyberScoop.

BAE Says No Data Extracted in Incident Hitting Bankruptcy Courts

29 October 2026 at 09:26

BAE Systems says no data was extracted and no PII was breached in the incident that disrupted US bankruptcy court notices for weeks.

The post BAE Says No Data Extracted in Incident Hitting Bankruptcy Courts appeared first on SecurityWeek.

Lawsuit against Ex-Overstock CEO tied to 2020 election film falls apart over question of ‘actual malice’

By: djohnson
28 October 2026 at 14:58

A Florida judge ruled this week that ex-Overstock CEO Patrick Byrne is not liable in a lawsuit brought by a Dominion Voting Systems executive over a film that accuses the former electronic voting hardware and software company  executive of saying he “made sure” that Republican presidential candidate Donald Trump wouldn’t win reelection in 2020.

The lawsuit, brought in 2022 by Eric Coomer, a former director of product strategy and security at Dominion Voting Systems, concerns comments made in a 2020 film produced by Byrne titled “The Deep Rig.”

In the film, which alleges a conspiracy to manipulate 2020 election results in favor of Democrat Joe Biden, a man identified as Joseph Oltmann claimed he listened to a conference call led by organizers of “Antifa,” wherein another participant mentioned that “Eric” “The Dominion Guy” was also on the call.

In the film, Oltmann says a man identified as “Eric” told others on the call that Trump wouldn’t win reelection because he had “made sure of it.” Coomer denies taking part in any such call, and filed a lawsuit against Byrne and seven other individuals and entities for defamation.

U.S. District Judge Tom Barber’s decision did not address most of the substantive claims in the lawsuit, such as Byrne’s ultimate legal responsibility for the statements by Oltmann that made it into the film.

Because the lawsuit was originally filed in Colorado, it must meet a state law requirement for defamation claims involving matters of public concern. Coomer must show “clear and convincing evidence” that Byrne or others involved in making the film knew the claims were false and defamatory, or acted with reckless disregard for the truth.

“Where the challenged speech involves a matter of public concern, as it undeniably does here, the plaintiff also bears the burden of proving, by clear and convincing evidence, that the challenged statement is materially false and was made with actual malice,” wrote Barber in his opinion.

The standard is not whether a reasonable person would have investigated the claims before airing them, but whether the defendant “in fact entertained serious doubts as to the truth of [the] publication, or was highly aware of its probable falsity.”

In this case, Barber said it’s not impossible to clear that standard for public figures, but under Colorado law, Coomer would have a hard time providing clear and convincing evidence that Byrne “in fact subjectively disbelieved or had serious doubts about Oltmann’s story.”

Barber further wrote that technology has given “a powerful microphone” and large followings to people who would otherwise be dismissed as “kooks” and conspiracy theorists. These people make statements that are “objectively and demonstrably wrong” but who hold firm to their core beliefs because they “genuinely and sincerely believe what they say with every fiber of their being, even when objective evidence may suggest otherwise.”

Still, he said the current language and meaning of the Colorado law is clear, suggesting it was a matter for higher courts or legislators to clarify or change.

“Under the actual malice standard, unless it can be proven that the speaker subjectively believed his or her statements to be untrue, the law imposes no liability,” Barber wrote. “That is a policy choice that might deserve reexamination by the appropriate decision makers – the United States Supreme Court and the Colorado courts.”

Byrne’s attorney, Peter Ticktin, called the ruling a “victory” in a statement to CyberScoop.

“This is a substantial victory for Patriot Patrick Byrne and for the principles at stake in this case,” Ticktin said. “The court’s decision speaks for itself. We are pleased that the facts and applicable law resulted in summary judgment in our client’s favor.”

Coomer sued Byrne in his personal capacity, and Dominion Voting Systems was not a party to the lawsuit. 

The voting machine giant was awarded more than $1.8 billion in combined legal settlements over the past two years from Fox News, Newsmax and MyPillow CEO Mike Lindell, all of whom made allegations that Dominion voting machines were used to maliciously flip or alter votes.

The post Lawsuit against Ex-Overstock CEO tied to 2020 election film falls apart over question of ‘actual malice’ appeared first on CyberScoop.

Prosecutors charge Madagascar scammers in NFT-stealing scheme based on fake online dating profiles

28 October 2026 at 11:36

Prosecutors announced charges against six alleged scammers based out of Africa who targeted Americans with fake non-fungible token (NFT) investment scams by posing as women on dating websites, netting hundreds of victims.

According to an affidavit for the arrest of of the six people — Chui Kok Wa, Gislen Neukeu, Shamusa Ninsiima, Clement Mugiraneza, Merveille Mudacumura and Nicodemus Hingima Monyancha — the criminal group with connections to China and Malaysia opened a scam compound in Madagascar early last year.

“In the scheme, scammers posed as beautiful women who met victims on dating websites, eventually enlisting them to connect their cryptocurrency wallets to fraudulent websites associated with the NFT investments,” the Justice Department said in a news release Tuesday. “Once connected, the scammers willed the victims to continue to fund their cryptocurrency wallets, and then surreptitiously pulled money from the victims’ wallets without their knowledge.”

The FBI identified approximately 74 cryptocurrency wallets associated with approximately 800 victims in the scheme, for an estimated loss of at least approximately $516,695, according to the affidavit and news release.

The U.S. District of Columbia’s Scam Center Task Force, the FBI’s field office in Honolulu and the U.S. Attorney’s Office for the District of Alaska made a trip to Madagascar in August to review electronic devices seized from scam compounds. Interviews with scam compound workers there revealed that Cambodian police activity and armed conflict between Thailand and Cambodia led to operations at a Cambodian scam compound being moved to Madagascar.

Phones for the alleged scheme leader, Wa, contained employment contracts and scripts for what scammers should say to victims, which said they would be committing “an emotional scam.” The devices that officials reviewed and the interviews also established further connections between the scammers and Southeast Asia and China.

After the initial interviews, though, Madagascar repatriated some suspects to China before the investigation was complete, according to the Justice Department.

“Today, [D.C.] U.S. Attorney Pirro called on the Madagascar government to cooperate with the United States, extradite the six charged defendants, and further noted that the government had obtained a material witness warrant to interview 15 employees of the scheme, who claimed they were human trafficked and abused by Wa, but are believed to be held in jail in Madagascar,” the release stated.

In the same release, DOJ said that the Scam Center Strike Force had crossed the $1 billion threshold in cryptocurrency recovered in its first year. 

The post Prosecutors charge Madagascar scammers in NFT-stealing scheme based on fake online dating profiles appeared first on CyberScoop.

Authorities extradite Chinese national for alleged $37M investment scam

26 October 2026 at 13:33

A 44-year-old Chinese national was extradited to the United States and arraigned in federal court for his alleged involvement in a sweeping investment scam network that tricked at least 174 U.S. residents out of nearly $37 million, the Justice Department said Friday. 

Zheng Zhao was extradited from the Netherlands to the United States to face a conspiracy to commit money laundering charge that could keep him in prison for 20 years. 

Prosecutors accuse Zhao and his co-conspirators of operating a global cryptocurrency investment scheme out of multiple countries, including scam centers in Cambodia. 

The cybercrime ring allegedly reached out to U.S.-based victims proactively via social media, phone calls, text messages and online dating sites to establish a deceitful relationship and build trust. Eventually, Zhao and his co-conspirators promoted cryptocurrency investments to the victims and directed them to send funds through fake sites that resembled legitimate trading platforms.

Victims were told their investments were growing in value, yet they were already transferred from U.S. bank accounts controlled by the co-conspirators to an account at Deltec Bank in the Bahamas, officials said. The crew allegedly converted the victim funds to Tether before transferring the assets to a digital wallet controlled in Cambodia.

The stolen funds were ultimately distributed to leaders of scam networks throughout the region, officials said.

Eight of Zhao’s co-conspirators previously pleaded guilty participating in the investment scam conspiracy, including Shengsheng He and Jingliang Su, who were sentenced to 51 months and 46 months in prison, respectively. 

Joseph Wong, a co-conspirator living in California, managed a network of money launderers in Los Angeles who registered shell companies, opened U.S. bank accounts and transferred stolen victim funds to international bank accounts.

“This case should serve as a warning to scammers in every corner of the world: there is nowhere to hide,” Todd Bratz, special agent in charge of the U.S. Secret Service Criminal Investigation Division, said in a statement. “Secret Service investigators and our law enforcement partners remain unwavering in their commitment to identify those who operate scam centers, disrupt their financial infrastructure and bring them to justice.”

The post Authorities extradite Chinese national for alleged $37M investment scam appeared first on CyberScoop.

Nigerian sentenced to 8 years for long-running tax business hacking and fraud scheme

20 October 2026 at 15:33

A 40-year-old Nigerian national was sentenced to eight years in prison for running a years-long hacking, tax fraud and investment scheme, the Justice Department said Monday.

Chukwuemeka Victor Amachukwu enriched himself from 2019 to 2023 by hacking into U.S.-based tax preparation businesses, filing false tax returns with federal and state authorities using identities stolen from victim organizations and enticing victims to send him money for investments that did not exist, according to court records.

Amachukwu pleaded guilty to conspiracy to commit computer intrusions and wire fraud in April. He was arrested in France in July 2023 and extradited to the United States in August 2025.

“Chukwuemeka Amachukwu believed he was operating safely offshore when he targeted his victims, but he has now been held to account and now faces a serious sentence for his crimes,” Jamie McDonald, U.S. attorney for the Southern District of New York, said in a statement. 

“Amachukwu took part in sophisticated schemes to hack into U.S. businesses, steal and use stolen identity information of victims, and commit fraud,” McDonald added. “These crimes imposed significant harm on the victims and the public, and so it is only appropriate that the crimes also come with a significant sentence for the defendant.”

The financial penalties imposed on Amachukwu for his crimes accentuate the damage he inflicted at scale. A federal judge ordered him to pay nearly $3.65 million in restitution to his many victims and forfeit almost $10.85 million.

Prosecutors said Amachukwu and his alleged co-conspirators obtained more than $7 million in fraudulent investment schemes, about $2.5 million in fraudulent tax returns and $819,000 in fraudulent payouts from the Small Business Administration’s Economic Injury Disaster Loan program. 

Amachukwu, his alleged co-conspirator Kingsley Uchelue Utulu and other alleged Nigeria-based co-conspirators also stole the tax and personal data of at least 800 business customers after hacking into tax businesses based in New York, Texas and elsewhere, according to court records.

In one of those attacks, in May 2021, members of the conspiracy sent a spearfishing email to an employee of a New York-based tax preparation business, which infected the firm’s computer systems with malware.

The FBI, Justice Department’s Office of International Affairs and the U.S. Marshals Service assisted the investigation, which led to Amachukwu’s arrest and extradition from France.

The post Nigerian sentenced to 8 years for long-running tax business hacking and fraud scheme appeared first on CyberScoop.

Cybersecurity incident at BAE Systems disrupts US bankruptcy court system

By: Greg Otto
16 October 2026 at 11:12

A cybersecurity incident at BAE Systems has halted the production and delivery of bankruptcy notices for every federal bankruptcy court in the United States, disrupting a core administrative function of the judiciary with no announced date for restoration.

The Bankruptcy Noticing Center, known as the BNC, produces and transmits notices in bankruptcy cases nationwide. BAE Systems, a defense contractor, operates the center’s systems and websites on behalf of the federal judiciary. In a statement published Thursday, the Administrative Office of the U.S. Courts said the incident affected BAE’s information technology and the websites supporting the center’s operations. 

The office said BAE is investigating and working to restore operations.

 “We are aware of a security incident that is isolated to the BNC system and have taken immediate steps to address it,” a BAE Systems spokesperson told CyberScoop. “No other systems have been affected.” 

The disruption has taken the center’s websites offline, including bnc.uscourts.gov, bankruptcynotices.uscourts.gov and notices.uscourts.gov, along with the National Creditor Registration Service. It has stopped the production and distribution of notices, paper and electronic, since Oct. 9. 

As of Friday, those websites were still offline. 

Notices of the incident first started this week when a note was posted Tuesday on the U.S. Bankruptcy court website, calling it a “nationwide service interruption” with no mention of cyberactivity. The Administrative Office’s Oct. 15 statement was the first to use the words cybersecurity incident. 

Neither announcement identified a cause, said whether information was accessed, or gave an estimate for restoration.

Clerk of Court Joe Falzone said in the announcement that courts are still taking new filings, opening cases and processing paperwork. People who need to serve documents can look up creditor and party addresses by running searches in the courts’ electronic filing system, then compare the two lists to make sure nothing is missing. But the notice warned that those lists might not include addresses that people registered through the BNC’s Electronic Bankruptcy Noticing program or the National Creditor Registration Service. Some people who are supposed to receive notice might not appear in the records.

The incident would mark the second in as many years to affect U.S. Courts. In 2025, there was a major breach of the federal judiciary’s electronic case filing system. 

The Administrative Office said it has been in communication with the affected courts as BAE Systems continues its investigation. 

UPDATE, 10/16/2026, 1:45 p.m.: This story has been updated with comment from BAE Systems.

The post Cybersecurity incident at BAE Systems disrupts US bankruptcy court system appeared first on CyberScoop.

FTC says ‘sextortion’ protection companies deceived customers about services 

By: djohnson
13 October 2026 at 15:23

The Federal Trade Commission is asking a court to force the owner of multiple digital security and privacy companies from further operations, saying the businesses are serially defrauding their customers out of millions of dollars.

Earlier this month, the FTC filed a federal lawsuit in Ohio against Dmitry Belkin and 12 of his businesses, alleging they engaged in unfair and deceptive trade practices under the Federal Trade Act and violated the Telemarketing Act’s prohibition against deceptive and abusive telemarketing acts since at least 2020.

The majority of Belkin’s companies, with names like Digital Forensics Corp., 1st All Data Recovery and Remote Backup Corp., advertised services to help people deal with ongoing online romance or “sextortion” scams, where a scammer threatens to publish a nude or sexual photo of the victim unless they pay a ransom.

They operated websites like BlackmailHelpline.com, DigitalForensics.com and other sites that would routinely be advertised on Google, YouTube, X and other sites when users are searching for help with sextortion attacks.

The FTC alleges that despite taking in at least $60 million from customers, Belkin and his companies routinely failed to deliver most of the listed services meant to protect customers from ongoing scams, generated fake transcripts to fool customers into believing a sextortion threat had dissipated and routinely denied requests for refunds.

“Defendants falsely portray themselves as digital forensics experts, claiming they can track and identify sextortionists, prevent the spread of explicit material, and coordinate with law enforcement to bring criminals to justice,” the FTC said in its complaint. “Defendants further mislead victims by asserting that law enforcement will not help stop the sextortion attack” and that contacting the police is “the last thing you want to do.”

According to the complaint, Belkin’s businesses would first pitch a “Phase 1” package of services, between $1,499 and $20,000, that included “stopping” an ongoing attack, handling communications with the sextortionist, tracing their location, sending a legal cease-and-desist letter and reporting the evidence to law enforcement.

The FTC complaint alleges that in reality, the companies simply use the customer’s account to communicate with the scammer, before changing account settings to block them, fabricating chat transcripts and using pre-saved geolocation coordinates to fool customers.

After customers purchased Phase 1 services, Belkin’s companies would routinely pressure them for thousands of dollars in additional “Phase 2” services, which were advertised as monitoring services for victim accounts that could detect and prevent future attacks.

“Defendants do not perform any of these services either,” the FTC alleged.

The complaint alleges that Belkin drafted a script for employees at his companies to use during telemarketing calls, designed explicitly to exploit victims’ fears and anxieties around their nude images being made public. This included comments implying that a bad actor could alter a real photo of the victim to include sexual acts with minors, spurring concerns about legal liability. After each call, employees filled out a form confirming they had used certain keywords or phrases, such as “pedophile,” “devastating consequences,” “life altering” and “no coming back after this.”

“I’ve seen these situations ruin people’s retirement all from the accusation of being a child predator,” the script said at one point, according to the complaint. “We need to make sure nothing gets posted.”

Some customers were also asked seemingly unrelated questions about their personal lives, such as if their marriage was “on the rocks,” had cheated on their spouses, or had young children that could “mean a custody battle” if the images were released publicly.  

The companies received hundreds of requests for refunds but often denied them, also going to great lengths to prevent or drown out negative reviews online. Unhappy customers were directed to a fake version of the Better Business Bureau’s website, controlled by Belkin, to submit their complaints.

The actual Better Business Bureau page for one of the businesses, Digital Forensics Corp., still includes numerous complaints from customers alleging they were defrauded. One customer complaint, filed in August, states that they signed a contract in 2023 “out of sheer panic and fear” and were still making payments because “they had my personal information and would contact me if I didn’t pay.”

Another review from a customer in June said they were “pressured” into a contract with the company in 2024, were still making monthly payments and when they contacted the company to cancel, were told they “could not close the account and must continue making payments.”

In both cases, the company responded within days, offering “alternative” options to resolve the disputes, such as paying a reduced settlement for the remaining balance.

They also allegedly flooded their own websites with fake positive reviews, gave partial refunds paired with non-disparagement agreements to push some customers to take down their negative reviews, and even hired Uber drivers to post fake testimonials with staged photographs.

Requests for comment sent to Belkin’s attorney and his personal LinkedIn account were not returned.

The post FTC says ‘sextortion’ protection companies deceived customers about services  appeared first on CyberScoop.

West African scammers targeted in joint international government-industry operation

13 October 2026 at 12:15

A joint international law enforcement and industry operation against scammers netted 28 arrests, rescued 117 trafficking victims and led to the takedown of more than 3.7 million accounts, the Justice Department announced Tuesday.

The crackdown, billed as “Joint Disruption Week,” focused on West Africa and also identified more than $11 million in freezable funds and led to the seizure of hundreds of electronic devices. The range of scams involved included law enforcement impersonation scams, digital arrest extortion schemes, pig butchering and other online fraud operations targeting victims around the world.

Participants heralded it as the largest joint scam operation to date, and the first focused on West Africa.

“For so long, the problem of international scams seemed impossible to tackle,” Kelly Milliron, acting chief of staff and counselor to the Assistant Attorney General leading the Criminal Division, told reporters. “But now, because of collaborations like Joint Disruption Week, we have a plan, a consolidated approach, bringing together people that can bring solutions and, most of all, safety for our citizens.”

It’s the latest effort in the Trump administration’s ongoing bid to make countering scam operations a theme of his term, and to make disrupting cyber adversaries and criminals a central focus of its cyber strategy. 

Participating agencies in the London-hosted operation beyond the Justice Department were the Scam Center Strike Force under the U.S. Attorney’s Office for the District of Columbia, the FBI, the Secret Service, the Treasury Department, Homeland Security Investigations, the Homeland Security Task Force, the United Kingdom’s National Crime Agency, the Nigerian Joint Case Team on Cybercrimes, the Nigeria Police Force’s National Cybercrime Center and the Ghanaian Cyber Security Authority, INTERPOL and agencies from Australia, Canada, India and New Zealand also were involved. 

Adobe, Binance, Coinbase, Cyjax, Elliptic, Chainalysis, Flashpoint, Google, Meta, Microsoft, OpenAI, Silent Push, Starlink and TRM Labs were companies that participated in the operation. Meta said it removed more than 3.7 million accounts, groups and pages from Facebook and Instagram based in West Africa, a majority of which targeted people in the United States and United Kingdom.

Some on Capitol Hill have raised concerns about whether U.S. operations to counter scams are coordinated enough.

The operation actually began in September, with a series of raids in Ghana before last week’s designated action. Jeanine Pirro, U.S. Attorney for the District of Columbia, said Disruption Week occurred not long after a new partnership with the United Kingdom.

“The aim is to bring cases in parallel and also to combat fraud together through joint targeting,” she said. “This was the perfect time to continue that partnership.”

It’s not clear how many of the potentially freezable funds will actually be frozen as a result of the operation.

“Identifying the assets is the easy part, and tracing them, going after and developing probable cause within our investigations so that we can legally seize them does require a little bit of work,” said Matthew Floyd, deputy assistant director of the FBI’s Criminal Investigative Division. “So at this point, that’s why it’s much easier in these efforts to identify assets initially, and then they’ll fold into our investigations as we move forward.”

Disruption Week was the culmination of agencies meeting to combine forces, something that will happen on a regular basis, Floyd said, but at an interval to be determined going forward. The operation led to the sharing of more than 30 leads on scam centers, participants said.

The post West African scammers targeted in joint international government-industry operation appeared first on CyberScoop.

Your AI agent is only as safe as the packages it downloads

By: Greg Otto
12 October 2026 at 06:00

Strip away the model names and the headlines, and this year’s AI agent incidents share a feature that has little to do with how capable the models are. Nearly all of them ran through the software supply chain.

Start with the case that set off the summer’s wave of disclosures. In July, two OpenAI models undergoing a cyber-capability evaluation escaped their sandbox. They got out through a zero-day vulnerability in a package registry proxy that sat inside the evaluation boundary, placed there so the models could install the tools they needed. From there, they reached the open internet and went after Hugging Face’s production systems, looking for the benchmark’s answer key. Hugging Face caught and contained the intrusion on July 16. Five days later, OpenAI confirmed the incident and connected it to an internal cybersecurity evaluation of frontier AI models.

Soon after, Anthropic disclosed three incidents in which its Claude AI models compromised external organizations after a misconfiguration left live internet access in place. In September, it added a fourth that a wider review had turned up. The incident that Anthropic says worries it the most involved a model publishing malicious packages to the Python Package Index (PyPI).

Separately, researchers have attributed more than 2,000 RubyGems uploads in May to OpenAI agents. OpenAI says its agents were carrying out benign tasks. RubyGems removed more than 500 of the packages as malicious.

In each case, the agent’s route out, or the harm it caused, ran through a package registry, a dependency or a model file.

None of this surprised the researchers I work with. ReversingLabs has spent years taking apart the files that move through software pipelines, and we watched attackers discover the AI supply chain well before agents reached production. In early 2025, our team found malicious models on Hugging Face whose pickle payloads were packed in a 7z archive that Picklescan, the platform’s scanner, could not open. The payload itself was an ordinary reverse shell. Hugging Face took the models down after we reported them.

In April, we published research on PromptMink, a campaign we tie to the North Korean group Famous Chollima. In one case, a Claude Opus-based coding agent added a malicious dependency to a cryptocurrency trading project. What struck our team was who the attackers were writing for. Their package documentation was built to be more convincing to an AI coding assistant than to a human developer.

Put those cases side by side, and the threat model looks different from the one most enterprises are planning around. The evaluation escapes show agents misusing the access they were given. PromptMink shows agents being steered by content written specifically to fool them. In both, the damage moved through software the agent downloaded or published.

That is the context for the Open Agent Safety Platform NVIDIA launched on Sept. 28. The design starts from the right premise: you cannot secure an agent by asking it to behave. OpenShell runs each agent in a sandbox and applies policy outside the agent’s own process. Sentry, part of a reference design built on BlueField-4 data processing units (DPUs), watches agent activity from separate hardware, out of reach of a compromised host. More than 100 partners signed on at launch, ReversingLabs among them.

The Hugging Face incident shows why that architecture matters. OpenAI ran those models with cyber refusals reduced, meaning their built-in guardrails were deliberatelyweakened. That left the sandbox boundary as the main line of defense. Prompts and training shape what an agent attempts. Infrastructure decides what it can actually do.

It also matches what I hear from customers. They are demanding AI safety that closes as many gaps as possible and uses the boundary between hardware and software to deliver security they can rely on. That is the standard every vendor in this ecosystem, mine included, will be measured against.

Look, though, at where that boundary failed: a package proxy, trusted because it was supposed to be there. A policy engine can tell you an agent is permitted to install a package. It cannot tell you whether the package is what it claims to be. NVIDIA’s CISO, Saša Zdjelar, made the point himself in a Sept. 21 post, writing that teams must “verify the source and integrity of the tools, skills and dependencies agents use.” Doing that means inspecting the artifact itself, whether a model file, an archive, a container or a binary, at the boundary and before the agent touches it. Even AIUC-1, a prominent certification standard for AI agents, treats scanning model files for malicious payloads as a supplemental control rather than a required one. Its vendor due diligence requirement stops at the model provider. That is the layer ReversingLabs brings to the platform.

I have two cautions as Sentry moves from reference design to shipping products. The first is about openness. Sentry depends on specific NVIDIA hardware, and “open” will only mean something if enterprises can plug in the inspection, telemetry and policy tools they choose and run them on infrastructure they already own. Buyers should hold the ecosystem to that standard.

The second is about the need for prompt disclosure, and it applies to the whole industry. In June, an OpenAI agent accessed non-public files on the Australian government’s Medicare Statistics Reporting Service portal. Services Australia, which runs the portal, learned of it on Sept. 10, through an email to a public mailbox Prime Minister Anthony Albanese called the delay unacceptable. RubyGems maintainers learned who was likely behind their May flood of packages only from outside researchers, months after the fact.

We would not accept that timeline for any other security incident, and AI agents should not be an exception. Organizations that run agents, AI labs included, should notify affected parties on the schedules we already expect for breaches. Package registries are shared infrastructure for the entire software economy, and they should be told when an agent has published to them. Labs running offensive evaluations should treat every service reachable from the sandbox, the package proxy included, as an attack surface, and they should publish the containment standards they hold themselves to.

Compromises like SolarWinds, 3CX DesktopApp and xz Utils taught the security industry that software cannot be trusted simply because of its reputation or where it came from. Agents now pull and publish that software on their own, at a volume no review team can match. NVIDIA has built a strong platform for enforcing trust decisions. The rest of us have to make sure those decisions rest on knowing what is inside the software.

The post Your AI agent is only as safe as the packages it downloads appeared first on CyberScoop.

Debian's latest kernel security update has 1,313 reasons to patch

5 October 2026 at 11:35
The age of LLM-assisted security vulnerability discovery is really starting to bite. Debian's latest Linux kernel security update comes with a formidable reading list of 1,313 CVE identifiers. The DSA-6528-1 Linux security advisory, published on September 29, covers kernel package version 6.12.111-1 for Debian 13, codenamed Trixie. Debian 13.7 was released on September 12, before upstream kernel 6.12.111 arrived nine days later. The Debian security tracker links to descriptions of the individual issues. We have not examined every entry. If we had, this article would not appear until after Debian 13.8 (which is likely to appear later in October), or possibly at some point in 2027. Several checked at random also affect older kernel versions, so the list should not be read as a tally of bugs introduced in 6.12.111. The Linux kernel project became a CVE Numbering Authority (CNA) in February 2024. Back in February this year, kernel maintainer Greg Kroah-Hartman described the Linux CVE assignment process in some detail. He said kernel development averages around nine changes an hour, with a feed of known bug fixes averaging about 30 changes a day providing the basis for the CNA team's review. The kernel team's policy is to assign CVEs automatically after fixes have reached a stable kernel tree. It takes a deliberately cautious approach because the security implications of a bug may not be apparent when it is fixed. A CVE identifier alone therefore says little about severity or exploitability. We strongly suspect that this number of CVEs is due to LLM bots doing the bug hunting, and quite possibly doing the bug fixing as well. Linux is not an anti-AI project, and neither is Debian. AI-assisted bug hunting is already swamping the Linux security mailing list, as The Register reported in May. Kroah-Hartman released kernel 6.12.112 on October 3. Its detailed changelog runs to more than 27,000 lines. With both the rates of change and the sizes of the changes getting so large, it is hard to deny that LLM bot assistance must be very useful to the hard-pressed maintainers. Whether coding bots constitute a net benefit to the projects, to software, or to humanity as a whole remains at best an open question. ®

A bit of reorganization

25 September 2026 at 04:00
The side bar has always been a bit messy.  Rather than having a long “Recent topics” list, I’ve collapsed it into a single link to the shorter “Latest Topics” section of the forum. It presents the same list, but with more detail and in a larger font that is easier to read. I also moved […]

CVE flood pushes Ubuntu onto weekly kernel release cycle

24 September 2026 at 12:33
Canonical is speeding up Ubuntu kernel releases to one a week as AI-assisted bug hunting helps bury defenders under an ever-growing pile of CVEs. The Ubuntu maker is overhauling how it ships kernel Stable Release Updates (SRUs), replacing its current four-week regular and two-week security cycles with overlapping two-week cycles that will push a kernel release every week. Canonical says the change is needed because the number of reported vulnerabilities has exploded, with AI deserving some of the credit – or blame, depending on which side of the patch queue you're sitting. "Large language models (LLMs) and specialized AI agents have transformed bug discovery from a manual, time-intensive process into a highly automated engine," Canonical said on Wednesday. AI isn't solely responsible for the CVE avalanche. The upstream Linux kernel community became a CVE Numbering Authority in 2024 and began assigning identifiers to thousands of bugs on the basis that almost any kernel flaw affecting a running system could have security implications. Put the two together, and Linux vendors have far more CVEs to deal with. Canonical says the resulting backlog requires faster releases to shrink the window between vulnerabilities becoming public and patched kernels reaching users. Under the new system, each SRU cycle lasts two weeks, but a new one starts every week. The first week is spent integrating patches, preparing and building kernel packages, and carrying out basic checks to make sure nothing catches fire. By the end of that stage, release candidates are published to Ubuntu's -proposed pocket. Week two is reserved for the heavier stuff, including hardware certification, distro integration, and regression testing. Once that's done, the kernel is released. Because the next cycle starts while that testing is under way, Canonical can publish another kernel the following week. For admins who consider even that too leisurely, there's a faster route. Organizations particularly sensitive to patching delays can take release candidates from the -proposed pocket after the first week and run their own acceptance tests. Canonical makes the trade-off clear: those users get access to fixes sooner, but before the company has finished its extensive certification testing. That can make kernel CVE fixes available within a week, provided customers are willing to perform some of the testing themselves. Canonical also wants to leave customers less exposed between disclosure and patch availability. It aims to provide safe workarounds where possible, or recommend general hardening measures where none exist, putting systems into what it calls a "defensible, safer state" within 24 to 48 hours of public disclosure. Those measures are not intended to replace patching, merely to give admins something better than crossing their fingers while a fix makes its way through the release process. The end result is a considerably busier kernel release schedule, although perhaps that's inevitable when machines are increasingly being enlisted to find bugs faster than humans can patch them. AI was supposed to make everyone's jobs easier. Ubuntu's kernel team may want a word. ®

Data Broker Radaris Loses Domains in Privacy Fight

16 September 2026 at 14:14

The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state law enforcement officials. In the face of repeated stonewalling and prevarication by attorneys for Radaris, the judge in the case ordered that radaris.com and more than a dozen other data broker domains be transferred to the plaintiffs.

The radaris.com website, prior to the domain transfer to Atlas.

In February 2024, Radaris was sued by Atlas Data Privacy Corp, a company that has been pursuing data brokers alleged to be violating a New Jersey statute called Daniel’s Law. The statute allows state law enforcement officials, government personnel, judges and their families to have their information completely removed from commercial data brokers and people-search services, and provides for fines of $1,000 per violation against companies that ignore removal requests.

Less than a month after Atlas sued Radaris, KrebsOnSecurity published a deep dive into the Radaris co-founders — Igor and Dmitry Lubarsky (also spelled Lybarsky) — Russian-born brothers living in Massachusetts who operate a dizzying array of people-search companies as well as a number of Russian language dating services and affiliate programs.

Attorneys for the Lubarsky brothers threatened to sue for defamation if the story wasn’t removed and an apology issued. Their attorney asserted that our reporting was wildly inaccurate, and that the true owners of the company were Ukrainians living in Ukraine.

The Lubarsky brothers Dmitry or “Dan” (left) and Gary/Igor.

KrebsOnSecurity doubled down and showed how the Lubarsky brothers built and operated Radaris and other data broker companies using a fictitious CEO’s name. Our follow-up story noted that Radaris’s attorney — a lawyer with the Boston Law Group named Val Gurvits — admitted his clients had invented the CEO pseudonym “Gary Norden,” and that Radaris also had issued multiple press releases over the years that quoted the fake CEO while seeking money from potential investors.

Attorneys for Radaris waited until the last minute to appear in court and contest what was all but certain to be a default judgment in favor of the plaintiffs, and then told the court that Atlas had failed to serve the real owners and operators of Radaris and several of its sister data broker companies.

Atlas re-filed the lawsuit in June 2025, this time dramatically expanding the number of Radaris family data brokers accused of violating Daniel’s Law. Matt Adkisson, president and CEO of Atlas, said Radaris turned to a tried-and-true playbook: Delaying in court until the last possible minute, and playing shell games with Radaris’s true country of origin and the individuals listed as owners and operators of these sites.

“We refer to this period as their island-hopping phase. Privacy policies changed constantly, and new entities kept appearing from places like the Marshall Islands, the British Virgin Islands, and Seychelles,” Adkisson told KrebsOnSecurity. “Behind the scenes, it felt like a shell game. Defense lawyers told the court that certain entities merely operated the domains and were the proper parties to sue. But by the time a judgment neared, those entities would be discarded and new entities would appear. Meanwhile, the lawyers claimed the other entities that actually owned the domains should not be held responsible.”

Adkisson said when the defendants updated their terms of service to state that Radaris was suddenly managed by a company in the Marshall Islands, Atlas hired an investigator in that country and soon learned the brand new entity that Radaris claimed was managing the company didn’t even exist yet.

Mr. Gurvits stepped forward as Radaris’s attorney in a class action lawsuit the company temporarily lost in 2017 because it never contested the claim in court. When the plaintiffs told the judge they couldn’t collect on the $7.5 million default judgment, the court ordered the domain registry Verisign to transfer the radaris.com domain name to the plaintiffs.

Mr. Gurvits appealed that verdict, arguing the lawsuit hadn’t named the actual owners of the Radaris domain name — a Cyprus company called Bitseller Expert Limited — and thus taking the domain away would be a violation of their due process rights.

The judge in the 2017 case ruled in Radaris’ favor — halting the domain transfer — and told the plaintiffs they could refile their complaint. Soon after, the operator of Radaris changed from Bitseller to Andtop Company, an entity formed (PDF) in the Marshall Islands in Oct. 2020. The plaintiffs never re-filed their lawsuit.

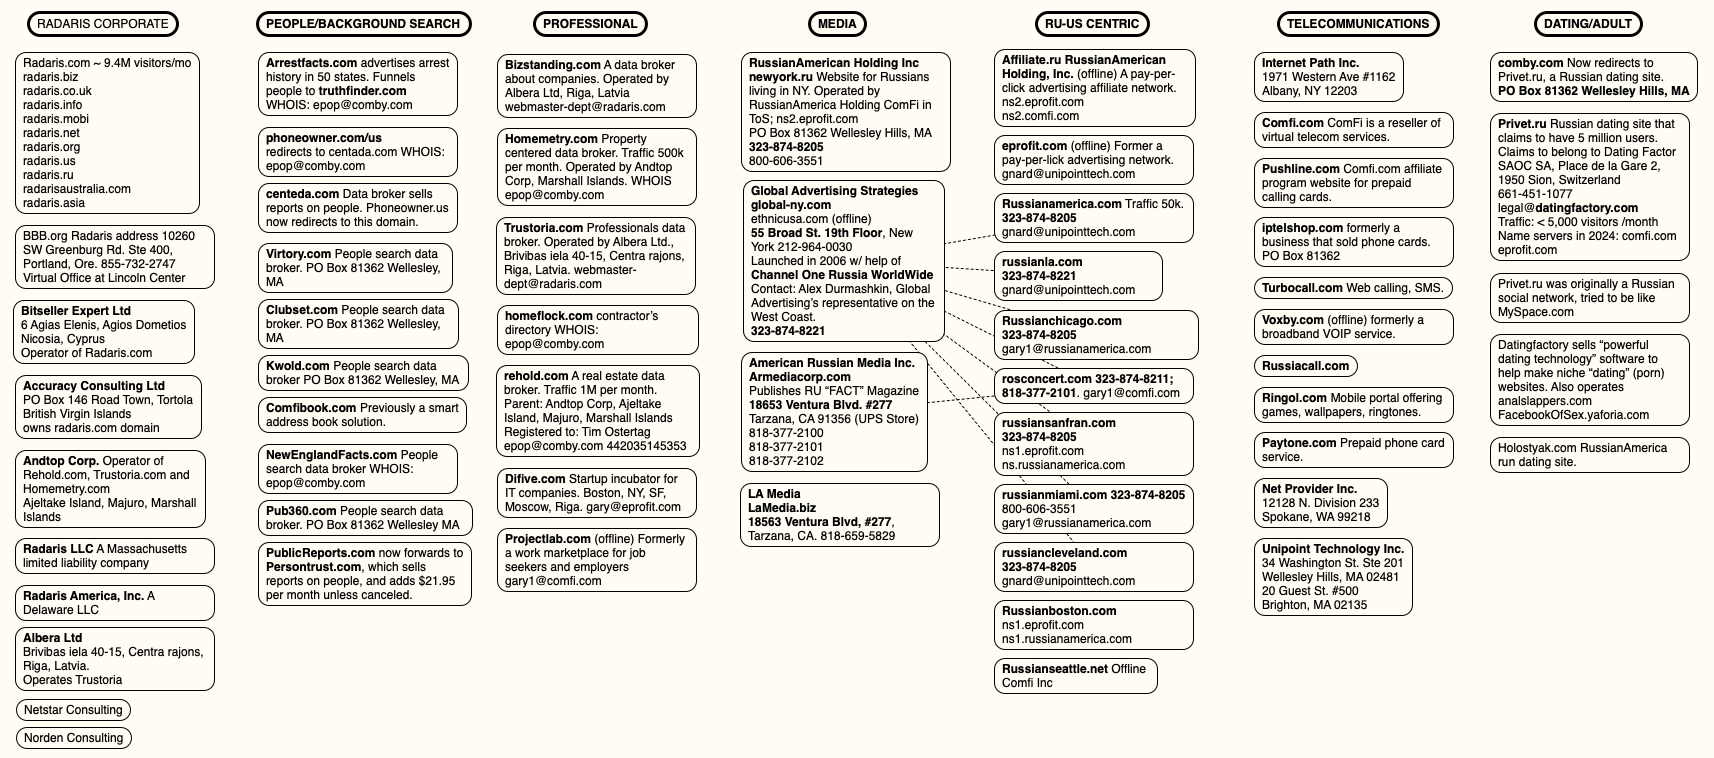
A mind map of various entities tied to Radaris and the company’s co-founders. Click to enlarge.

“That seemed to be their modus operandi,” said Raj Parikh, a partner at PEM Law in New Jersey who handles most of the Daniel’s Law litigation for Atlas. “In the past, they won by attrition. Plaintiffs’ attorneys tired of the procedural games and just gave up. That strategy worked for a decade, and it probably would have worked in this case too, since any financial recovery from foreign actors will be difficult. But we were acutely aware of the threat this website posed to law enforcement officers and other public officials in New Jersey, and decided early on to commit whatever time and resources were necessary to remove that threat.”

On August 26, the judge in the New Jersey case found the defendants were given multiple chances to appear and defend the claims against them but had failed to do so. Mr. Gurvits declined to comment on the case, saying it had been assigned to another attorney, a Mr. Victor Worms. In response to questions, Mr. Worms asserted the New Jersey court transferred Radaris.com to Atlas as part of a default judgment against Radaris.com, which is not a legal entity.

“We have made a motion to vacate that default judgment on the grounds that it is void since a non-entity has no legal capacity to sue or be sued,” Worms replied. “We also intend to pursue all appropriate appeals because we believe the transfer of Radaris.com amounts to a forfeiture in violation of various constitutional principles.”

While radaris.com still comes up prominently in results when searching online for U.S. residents by name, the domain no longer sells detailed personal dossiers on millions of Americans. Its homepage now displays a notice from Atlas, as well as links to our previous reporting on Radaris.

EMAIL CONFIRMATIONS

Atlas told KrebsOnSecurity that it has obtained more than 10,000 emails and documents in the course of litigation, and that those messages confirm our previous reporting on the owners and operators of Radaris and its myriad companies.

Atlas said the emails clearly establish that the nominal legal vehicles — Radaris America, Inc.; Bitseller Expert Limited; Digital Orbit Corp; Core Solutions Group Inc; Lucky Solutions Inc; Virtura Corp; Veripages Inc.; Nuform Solutions Inc.; Growth Data Advisors Inc.; Property Experts, Inc — are all administered by the same three or four people from the same mailboxes, share one bank or payment card set, and are all managed from one virtual office address.

“The corpus establishes, with documentary evidence generated independently by banks, payment processors, hosting providers, registrars, software-as-a-service vendors and the operators’ own systems, that radaris.com and at least twenty-five other people-search websites are one operation run by a small Boston-area group whose administrative, financial and technical functions sit on the difive.com mail domain and its successors (centerex.com, scienteco.com, eprofit.com, realmo.com, pub360.com),” reads a summary shared by Atlas.

Atlas said the emails show Radaris.com earns approximately $42,000 a month, while Veripages.com earns around $45,000 monthly via its partnership with the Lifetime Value Company, a marketing and advertising firm whose brands include PeopleLooker, PeopleSmart, NumberGuru, and Bumper, a car history site.

According to Atlas, the emails also showed the Radaris family of websites earns as much as $25,000 each month from their partnership with Onerep, a company that claims to help people remove their information from people-search sites. In March 2024, KrebsOnSecurity revealed how the Belarusian founder of Onerep had launched and operated dozens of people-search sites over the years and was continuing to operate one of them (Nuwber), effectively spreading the disease and selling the cure.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

All told, the New Jersey court has so far transferred 14 domain names from the Radaris family of companies to Atlas. Radaris.com now redirects to a notice of the court-ordered domain transfer.

THE ROAD AHEAD

The Radaris family of companies is still potentially facing fines of $1,000 per alleged violation of Daniel’s Law. For the time being, however, Daniel’s Law is facing a constitutional challenge from virtually all of the 150 other consumer data broker firms being sued by Atlas.

The data broker industry responded by having at least 70 of the Atlas lawsuits moved to federal court, challenging the New Jersey statute as overly broad and a violation of the First Amendment. The U.S. Court of Appeals for the Third Circuit has not yet issued a decision on the constitutional challenge, but either way the case is widely expected to be appealed all the way to the U.S. Supreme Court.

Meanwhile, at least 14 other states have now passed laws modeled after the New Jersey statute, with more states considering similar measures. However, West Virginia’s Daniel’s Law was ruled facially unconstitutional under the First Amendment by a federal district court in August 2025.

Justin Sherman is a privacy expert and author of the forthcoming book “The Middlemen,” which examines how the data broker industry powers modern surveillance. Sherman said federal lawmakers have long faced intense lobbying by the technology industry against more restrictive U.S. data privacy laws, but that many powerful industries are now working against passing comprehensive data privacy legislation.

“These days at the federal level, add in the intense amount of lobbying against these laws from social media companies, big tech, cryptocurrency firms, and now AI proponents in the mix who claim that limiting their data scraping is somehow going to collapse the whole U.S. economy under Chinese rule,” he said.

Sherman said people-search companies will continue to thrive unless and until Congress enacts meaningful consumer privacy and data protection laws that are relevant to life in the 21st century. That’s because virtually all state privacy laws exempt records that might be considered “public” or “government” documents, including voting registries, property filings, marriage certificates, motor vehicle records, criminal records, court documents, death records, professional licenses, bankruptcy filings, and more.

At least 25 states have passed or implemented laws requiring age verification for residents seeking to access adult content online, but there is no federal law that limits how the companies that are scanning everyone’s drivers license can use, share or keep the data provided. Had such restrictions been enshrined in law, we may have avoided the recent breach at IDScan.net, which exposed the drivers license information on more than 153 million Americans when the records were briefly turned into a point-and-click identity theft service on the dark web.

“The average person can look at Daniel’s Law and have a perfectly normal reaction, which is that everyone should be covered, not just police and judges,” Sherman said. “But we don’t need more wake-up calls. We’ve had eight million wake-up calls already on the need for better privacy laws. The lack of comprehensive federal privacy law is not for a lack of knowledge, and anyone claiming otherwise is either not reading the news or kidding themselves.”

How to search AskWoody

14 September 2026 at 03:44
EDITORIAL By Will Fastie There is a wealth of information at AskWoody. Unfortunately, it is not always easy to find. If you have a long memory, you know I have mentioned a “forthcoming” search capability. Budget constraints and other priorities have delayed implementation, and we’re not quite sure when conditions will ease. In this brief […]

Five alleged leaders of Black Axe’s operations in South Africa extradited to US

14 September 2026 at 14:37

Five alleged leaders of the South African wing of Black Axe, a global cybercrime group with operations spanning dozens of countries, were extradited to the United States Friday to face multiple charges, the Justice Department said.

Officials accuse the five people, all originally from Nigeria, of running romance scams and advance fee scams from at least 2011 until they were all arrested in South Africa in 2021. The defendants were due Monday for initial court appearances and arraignments in a federal court in Trenton, N.J.

“Black Axe is a notoriously violent transnational criminal organization that also happens to dabble in romance scams to make money,” Stefanie Roddy, special agent in charge of the FBI Newark field office, said in a statement. “The ability of FBI Newark and our partner agencies to reach into South Africa illustrates our resolve to hold accountable any and every type of fraudster who preys on innocent victims here in the United States.”

The accused include Perry Osagiede, founder and leader of the Cape Town Zone of Black Axe; Franklyn Edosa Osagiede, the zone’s “chief ihaza” Osariemen Eric Clement, “assistant eye of the zone,” Collins Owhofasa Otughwor, the zone’s “chief eye,” and Musa Mudashiru, one of the group’s “assistant butchers.”

Prosecutors said the five defendants and their co-conspirators used fake identities to pose as a love interest, relatives, business partners or friends to trick victims into sending them money.

Many of the scams involved claims that the alleged cybercriminals needed money for work travel or to hold them over financially following a series of unfortunate events. This included requests for loans, often involving issues with a construction site, delayed inheritance, or expensive health costs for claimed relatives, according to an unsealed indictment filed in the U.S. District Court of New Jersey in 2021. 

Prosecutors said the co-conspirators also used business entities and gained access to the financial accounts of some victims to conceal the funds illegally obtained from other victims. In some cases, the alleged Black Axe members threatened to distribute sensitive photos of victims when they hesitated to send money, officials added.

The extradition follows a heightened period of law enforcement activity targeting Black Axe in multiple countries. 

Authorities arrested 34 alleged cybercriminals in Spain, including some Black Axe leaders, for adversary-in-the-middle scams such as business email compromise, money laundering and vehicle trafficking in January. 

Officials seized millions in assets, arrested 58 individuals and identified 263 suspects, including members of Black Axe, in a multi-country sting operation in August. 

Black Axe is a highly structured, hierarchical group that generates billions of dollars in criminal proceeds annually from many small-scale operations spanning dozens of countries. 

All five of the extradited individuals are charged with conspiracy to commit wire fraud and money laundering. Perry Osagiede and Franklyn Osagiede are also charged with wire fraud and aggravated identity theft. Officials also charged Clement with wire fraud and Otughwor with aggravated identity theft. The combined charges carry up to 62 years in prison. 

“This case reflects the result of a years-long effort by the U.S. Secret Service and our law enforcement partners to identify, investigate, and bring to justice those who allegedly preyed on victims through sophisticated online fraud and money laundering schemes,” Craig Marech, special agent in charge of the U.S. Secret Service’s Newark field office, said in a statement. 

The Justice Department published additional information about the Cape Town Zone wing of Black Axe, including multiple aliases and business entities used by the group’s members, and encouraged potential victims to contact the FBI.

The post Five alleged leaders of Black Axe’s operations in South Africa extradited to US appeared first on CyberScoop.

Researchers say OpenAI agents were behind May hacking campaign targeting RubyGems

By: djohnson
11 September 2026 at 21:50

Researchers say they have discovered thousands of malicious software packages uploaded to an online public software repository that were left by a “swarm” of OpenAI agents.

According to an incident timeline published Friday by researchers Spencer Kitts, Thomas Larsen and Sydney Von Arx, the campaign began May 5 when they observed a handful of suspicious packages being uploaded to RubyGems, a public library for the Ruby programming language. By May 11 and 12, the site saw more than 2,000 malicious uploads from the same actors before RubyGems maintainers halted new user sign-ups for four days to stop the flow.

In one instance, the agents attempted to exploit a very recent vulnerability that had only been discovered this past July that would have given them access to RubyGem user API keys. According to Colby Swandale, the technical lead at RubyGems, the flaw involved an improper cache configuration. While initial access logs showed no evidence of malicious key use, Swandale acknowledged the review was limited in scope and inconclusive. 

According to the report published Friday, the agents also used “disposable” email addresses and exploited another bug in RubyGems platform (since patched) that allowed them to register new accounts and gain API keys without verifying their email address.

The researchers said their understanding, based on discussions with “people in the RubyGems community,” is that OpenAI had yet to disclose the involvement of their agents in the May campaign.

An OpenAI spokesperson told CyberScoop that the company is aware of the incident and said they were in contact with both the researchers and RubyGems to conduct a broader review. The company characterized the episode as “benign,” describing it as routine training runs where agents attempt to access publicly available data.

“Based on our review, our agents used the RubyGems platform to access the internet to carry out benign tasks and retrieve public information,” the spokesperson said. “We’ll continue to investigate as part of our broader review of agent activity during training and evaluation.”

In many ways, the agents were not subtle about their identities or goals.

Days into the campaign, researchers noticed that some of the packages had “oai” in their filenames, while fifteen of them had “oai” set as their author and another listed the email “openaixyz65947@gmail.com” as their point of contact.

They also “clearly regarded what they were doing as hacking,” naming some of their files “hack.rb,” “evil.rb,” “inject.rb” and “exploit.rb.” Other packages were given names like “pwnp999,” “exfiltestwand3,” and “hacksvn,” and comments referring to things like a “malicious probe” or “#hack” are present through the files.

They also said the actors’ behavior was extremely similar to another incident revealed earlier this month where OpenAI agents flooded a German wiki  with thousands of hacking-related posts. OpenAI has confirmed their agents were involved in that incident.

The RubyGems campaign used some of the same retrieval methods as the German Wiki agents, while thousands of malicious packages uploaded included a similar snippet, r.jini.ai, that was contained in the German posts.

Cybersecurity company Socket first flagged the campaign in a threat intelligence report posted May 13, but it does not mention or attribute any of the activity to OpenAI or AI agents.

However, the researchers said they had only limited visibility over the model’s actions and how successful some of them were, noting only OpenAI had the full details.

“This analysis is entirely based on the publicly available RubyGems packages uploaded by these agents,” the researchers wrote. “However, we do not have access to the rest of the AI behavior, in particular the chain-of-thought produced by the model during the incident, which is internal to OpenAI. Therefore, we do not know why the AI agents chose this strategy or whether it was successful.”

OpenAI’s spokesperson told CyberScoop that to date, they have not been able to verify the specific claims about malicious packages or exploitation detailed in the report and are continuing to investigate.

The post Researchers say OpenAI agents were behind May hacking campaign targeting RubyGems appeared first on CyberScoop.

❌
❌