❌

Reading view

There are new articles available, click to refresh the page.

CISA director pick already drawing concern from Hill Dems over Palantir connection

The two expected incoming leaders of the Senate and House homeland security panels expressed reservations Tuesday about the Trump administration’s pick to lead the Cybersecurity and Infrastructure Security Agency because he currently works for the oft-controversial tech company Palantir.

The Trump administration on Monday announced its intent to nominate Michael LoSapio, chief information security officer for Palantir, to fill the long-vacant Senate-confirmed position of CISA director.

The Senate Homeland Security and Governmental Affairs Committee has authority over approving CISA director nominees. A spokesperson for its current chairman, Rand Paul, R-Ky., didn’t respond to a request for comment, but he won’t hold the gavel much longer with Sen. Maggie Hassan, D-N.H., in line to take over as chair in 2027.

Hassan and her counterpart on the House side, prospective Homeland Security Committee Chairman Bennie Thompson, D-Miss., both voiced concerns about Palantir’s work at the Department of Homeland Security and with its subagency, Immigration and Customs Enforcement.

“CISA plays a critical role in protecting our nation’s cybersecurity infrastructure, and the Trump-Vance administration has undermined CISA by cutting its funding, reducing agency staff, and making us vulnerable to cyberattacks from our adversaries,” Hassan said in a statement to CyberScoop. “I will carefully review Mr. LoSapio’s nomination to lead CISA, as I do with any nominee. But given his senior role at Palantir, which has provided tools that helped enable ICE’s lawless behavior under this administration, I have serious questions about whether he has the independence and judgement needed for this position.” 

Thompson expressed apprehensions for similar reasons.

“CISA is at a critical juncture, rebuilding after a year of reckless efforts to hack up the agency. I don’t know much about Mr. LoSapio, but certainly his relationship with Palantir raises very serious concerns given its role in DHS surveillance programs,” he said in a statement to CyberScoop. “I’m concerned that baggage will be an unnecessary distraction from the urgent rebuilding efforts at CISA. I urge my Senate colleagues to thoroughly vet Mr. LoSapio before proceeding with his nomination.”

The current top Democrat on the Senate panel, the retiring Gary Peters of Michigan, also cited the threats CISA is facing amid cutbacks: “Mr. LoSapio must demonstrate that he possesses the independent judgment and qualifications to decisively place national security and the national interest above political pressure.”

The current chairman of the House panel, Andrew Garbarino, R-N.Y., said he appreciated Trump putting forward a nominee given the need for a Senate-confirmed director, something CISA has lacked for his second term, even as he praised the leadership of acting director Nick Andersen.

“I look forward to reviewing the qualifications of Michael LoSapio and urge the Senate to do so with urgency,” he said in a statement.

Unlike another of the top cybersecurity officials in the Trump administration prior to his nomination, National Cyber Director Sean Cairncross, LoSapio comes with technical credentials.

A former Trump administration official said that LoSapio’s name was first floated months ago, and said his cybersecurity certifications and experience managing cyber risk for a major public company would make him a good fit for the role.

A cybersecurity executive who knows and has worked with LoSapio said he was an “exceptional choice” for the job.

“Mike LoSapio is an extremely competent and talented cybersecurity leader. He knows his stuff,” the executive said. “He defends one of the most targeted organizations on the planet” because of Palantir’s sensitive government work.

CISA is primarily a technical agency, so “that work is best done by someone who knows how to do it,” the executive said. LoSapio is also a “high-integrity” person who isn’t “dogmatic or political” or “the kind of person that would be cowed by political pressure.”

But his role at Palantir is drawing criticism, something the executive said he understood given concerns about surveillance in the United States, even as the executive noted LoSapio has proven capable of navigating those “thorny issues.”

Patrick Eddington, a senior fellow at the libertarian Cato Institute think tank, acknowledged LoSapio’s technical background but said his lack of a government background and no public record of weighing in on the subject matter CISA works on adds up to a “thin resume.” More worrisome, he said, is that CISA is a Palantir customer.

“The nominee would come from the vendor whose software is already being bought, without competition, by the office he’d run,” Eddington said. “And the agency responsible for judging the security of federal civilian systems would be led by the former security chief of a vendor whose platforms now run across DHS. That’s where ethics rules would normally help, yet this administration has weakened them.”

Before confirming LoSapio, senators should find out what kind of Palantir stock or other holdings LoSapio has and whether he’ll divest it, whether he’ll recuse himself from Palantir matters for longer than the Trump administration would require, whether he has made bargains to return to Palantir after CISA service and other answers about potential conflicts of interest.

“Bottom line: Palantir’s business is fusing government data at scale, and DHS has made it the default analytics vendor across the department,” Eddington said. “Putting the company’s security chief in charge of the agency that sets the security bar for those systems, with a one-year recusal as the main safeguard, risks making CISA one vendor’s customer, regulator and alumni network all at once. Even if LoSapio is entirely well-intentioned, that’s the wrong setup.”

A Palantir spokesperson didn’t respond to requests for comment.

Even in optimal circumstances for a nominee, it can take some time to work through the Senate confirmation process and then begin shaping an agency as its leader, said Joshua Corman, a former CISA adviser and now executive in residence for public safety and resilience at the Institute for Security and Technology.

Andersen and his team, even amid budget cutbacks, “never gave up” on the agency, Corman said, and set important priorities for “the most life-safety of our critical functions.”

With two years left in Trump’s term, “it may be hard to have much of a dent, no matter who gets the nod, and as such, I really hope they lean on the current steward” in Andersen, Corman said. 

Madison Alder contributed reporting to this story.

The post CISA director pick already drawing concern from Hill Dems over Palantir connection appeared first on CyberScoop.

The US wants its quantum lead to turn into factories and supply chains

Policymakers from Congress and the executive branch are looking for ways to further boost the U.S. quantum computing industry, including by growing industrial capacity to translate scientific breakthroughs into workable technology.

Deputy Secretary of Commerce Paul Dabbar said the American industry is “by far the greatest leader in quantum technologies,” with a tech stack that is the envy of the world. The challenge will be translating those technological gains into real, brick-and-mortar industrialization and manufacturing dominance.

Dabbar pointed to other examples of federal support, such as grant funding from the CHIPS and Science Act and letters of intent signed earlier this year with nine companies investing more than $2 billion into different quantum technologies.

But one of the primary questions that Commerce officials ask companies when making decisions on federal investments is “How do we move a bit further down the road from discovery towards actually supporting individual technologies that can commercialize?” he said.

That question is being driven by U.S. assessments that the country’s quantum technology edge is real but is being threatened by countries such as China that have more robust industrial capacity.

Dabbar said the federal government is also attempting to follow its own example, citing White House executive orders on quantum computing and more aggressive timelines for agencies to migrate to quantum encryption, measures that CyberScoop was first to report last year. Commerce is the first agency scheduled to deploy its post-quantum encryption.

The department also has the authority to place export controls on technologies, as it did for Anthropic’s Mythos and Fable AI models earlier this year. Dabbar expressed caution but suggested Commerce officials were willing to use such controls to advance the interests of American technology makers.

“We have to be very careful about American leadership on the frontier on all technologies, and quantum is certainly one of them,” Dabbar said. “We want to be very thoughtful about making certain that which is invented by people in this room are retained by people in this room and are not copied or stolen.”

Dabbar’s comments came the same day that the Commission on U.S. Quantum Primacy released a report detailing the major challenges facing the American quantum industry.

The report warned that while research, software and private investment are “major strengths” for U.S. industry in its global competition with China, China’s manufacturing and supply chain production threatens to erode that edge.

“American scientific strengths may not translate into leadership in deployment and industrial production,” the report stated.

Boosting American industrial capacity in quantum is among the report’s top recommendations, including investments in physical infrastructure such as factories, foundries and suppliers that can “turn future breakthroughs into reliable systems.”

“To date, many quantum milestones have rightfully been measured in technical and scientific terms,” the report stated. “But national leadership requires a broader ambition: quantum primacy—the ability to turn scientific advances into sustained strategic advantage across quantum technologies.”

The commission is due to issue a final report in Spring 2027.

Sens. Ben Ray Luján, D-N.M. and Todd Young, R-Ind., served as co-chairs of the commission.

Meanwhile, Luján pointed to an alleged national security incident involving Nvidia CEO Jensen Huang as evidence that U.S. private industry can’t be trusted to protect America’s tech secrets. According to media reports Huang, who is married, had an affair with Chinese tech executive Alice Huang, later identified by U.S. intelligence agencies as a foreign intelligence asset working for China.

When asked about how to maintain U.S. competitiveness in quantum computing and other technologies, Luján said tech executives “need to be smarter” about protecting America’s tech secrets.

“People need to make better decisions when you’re entrusted with that kind of power and responsibility,” he said.

Luján, who did not mention Huang by name, said tech executives “know that other countries, they send people here to do bad things and get people locked up into telling secrets and things of that nature.”

“That clearly happens, and now we’re learning about it and the stock market’s reacting…don’t be stupid,” Luján said.

Luján said that while Democrats taking control of Congress will involve efforts to “push back” against executive branch overreach, he is open to working with the Trump administration and Republicans on legislation focused on the workforce and bringing “substantial investments across the United States in this space to ensure that the United States is going to stay in the front” of quantum computing.

But he suggested those investments could be wasted if Congress does not intervene with “good policy” and if tech executives can’t self-police their behavior. He pointed to another emerging technology, AI, where an innovation-at-all-costs approach has left industry poorly positioned to deal with cybersecurity and safety concerns.

“As we’re learning now from whistleblowers and others from some AI companies that we also need policy and guardrails, and the United States is qualified in a few [of those] areas,” Luján said.

The post The US wants its quantum lead to turn into factories and supply chains appeared first on CyberScoop.

Russian Turla group used new toolset to silently pilfer emails from Kazakhstan, Romanian governments

Turla, a notorious cyberespionage group aligned with the Russian government, has been wielding a new, customizable toolset to compromise governments around the world over the past year, including Kazakhstan.

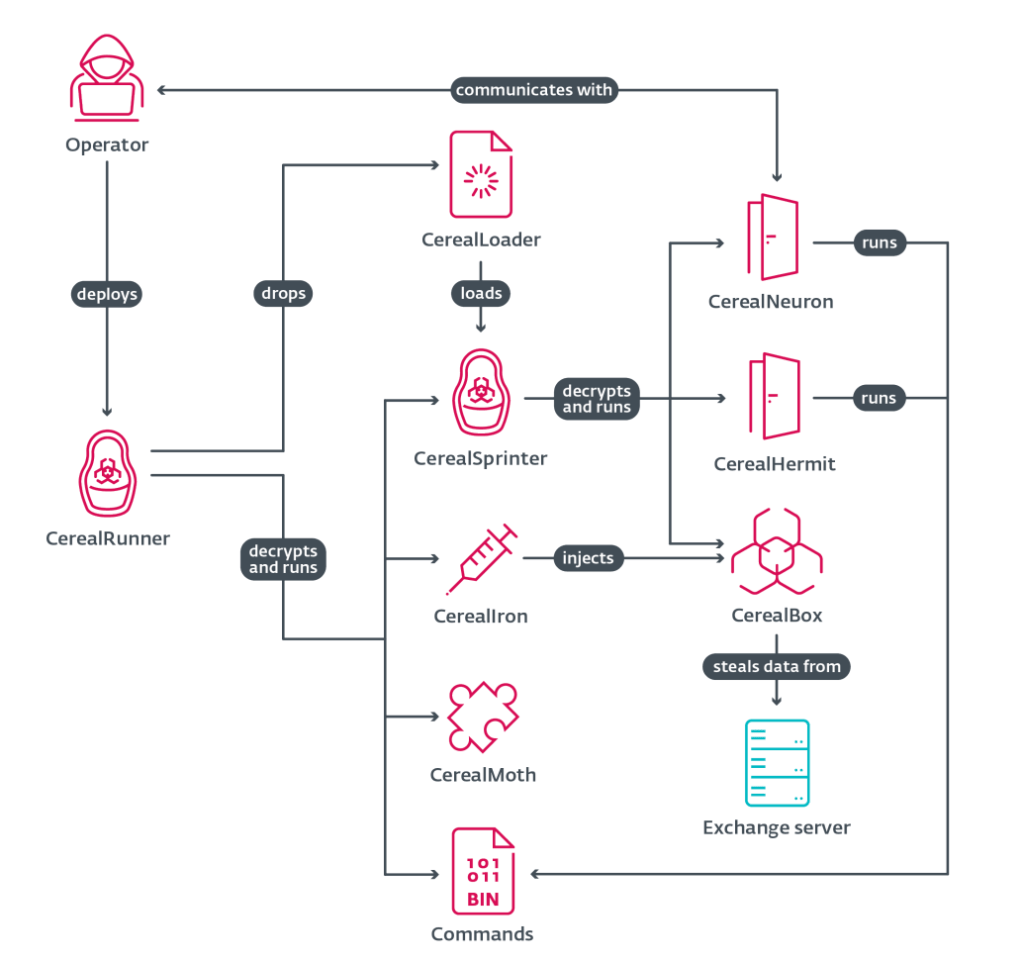
The toolset was first discovered in November 2025 by cybersecurity firm ESET, which named it “Turla’s Cereal” as a play on its highly modular, interconnected and “serialized” design. It chains and exploits different legitimate functions across Microsoft Exchange, Windows, and .NET assemblies, which Microsoft has described as “the fundamental units of deployment, version control, reuse, activation scoping, and security permissions for .NET-based applications.”

“One of the most interesting aspects of this toolset is what we did not find: external command and control infrastructure,” ESET researcher Matías Porolli wrote in the report, released Tuesday. “Instead — adding insult to injury — the victim’s compromised Exchange server is co-opted to act as the C&C infrastructure.”

Illustration of Turla’s Cereal compromise of Microsoft Exchange servers using a modular, stealthy toolset. (Source: ESET)

Multiple Western governments and threat intelligence firms have attributed Turla as a part of Russia’s Federal Security Service (FSB), which is tasked with gathering intelligence on foreign governments, businesses and organizations. According to MITRE, the group has compromised victims in more than 50 countries, spanning governments, militaries, private-sector companies and research organizations.  

Porolli said the toolset was found on a compromised Exchange server used by the government of Kazakhstan on Nov. 28, 2025, where it could receive commands, execute in memory, gather intel on the organization and collect certain email messages.

Another version found inside a Romanian government agency a month later was configured to target emails sent to or received by the Western powers — the European Union and the North Atlantic Treaty Organization — adversarial with Russia. At the time, Romanian politicians were calling for a NATO mission in the Black Sea to deter what they viewed as Russian aggression. In July, the EU announced sanctions against Russian individuals and organizations, citing a yearslong cyberespionage campaign from Turla and other Russian groups against European nations as well as the targeting of Poland’s energy grid and European businesses by Russia-aligned hacking groups.

According to ESET, the toolset lacks many features used to identify malware, such as implants, beaconing back to command-and-control infrastructure or built-in command lists. Most executables are performed in-memory using temporary storage to avoid leaving evidence, while commands written to permanent memory are delivered via encrypted payloads.

One component, dubbed CerealNeuron, operates as the main backdoor but does not beacon back to its operator the way many pieces of malware do. Instead, it runs on the compromised server and “passively listens for incoming web requests on paths that look like ordinary Exchange traffic.” The result is an attack that leaves no domain, IP address, hosting provider or timing patterns for defenders to find and block.

“The Cereal toolset demonstrates that, for Turla, Exchange servers are not just mail servers — they are durable collection points, internal execution hubs, and a suitable environment for hiding sophisticated .NET tradecraft,” Porolli wrote.

The post Russian Turla group used new toolset to silently pilfer emails from Kazakhstan, Romanian governments appeared first on CyberScoop.

New York Launches Nation's First State AI Testing Program

New York is launching a state-backed AI safety research center at Binghamton University that will independently study and test AI systems, develop safety and security techniques, and train researchers in responsible AI. "While the federal government fails to act, New York is leading the way on AI safety and holding big tech accountable," New York Gov. Kathy Hochul said. "The stakes are too high to simply take AI companies at their word." Politico reports: The center -- which is funded by a $30 million gift from Bloomberg co-founder Tom Secunda and a $25 million research investment from SUNY and New York state -- is set to launch before New York's major AI safety law, the RAISE Act, comes into effect on Jan. 1. That will require submissions of detailed safety frameworks from AI companies operating in New York State, which Hochul's office hopes will be scrutinized by researchers at the new center. "AI is opening up questions that scientists could not tackle before," said Secunda, who also serves as the board chair of Empire AI, a $500 million public-private partnership. "With Empire AI and researchers across New York, the Center can test systems independently and give public officials evidence they can use." Over 80 leading scientists and researchers on AI systems from across New York state will contribute to the effort, which will be run by the New York Center for AI Responsibility and Research at Binghamton University, according to details shared by Hochul's office. The initiative will be led by Jeannette Wing, the executive vice president for research at Columbia University, and Greg Morrisett, the vice provost of Cornell Tech. "We need new techniques that can be applied to this new kind of system with swarms of autonomous agents acting independently and without control. How can you first detect that they're going to do harm, and how can you prevent them from doing harm?" said Wing. "The beauty of what's being proposed is that this state is committing resources to really light this up."

Read more of this story at Slashdot.

Trump picks Palantir’s LoSapio to head CISA

The Cybersecurity and Infrastructure Security Agency finally got a new nominee for director, with President Donald Trump on Monday nominating Michael LoSapio, chief information security officer at Palantir.

CISA has been without a Senate-confirmed director for the entirety of Trump’s second term, after his first pick, Sean Plankey, languished in the Senate before withdrawing in April.

LoSapio could face some obstacles of his own, with Palantir far from a popular company with the Democrats set to take over Congress. Democrats have scrutinized the company over its work with the Department of Homeland Security, even as Palantir has denied aiding mass surveillance of immigrants.

As of late last month, Sen. Ron Wyden, D-Ore., was also still waiting for CISA to release a public version of a report on telecommunications cybersecurity, and he had placed one of several Senate holds on Plankey pending the receipt of that report.

Republicans will still control the Senate until January, however, and a lame-duck session began Monday.

Some CISA watchers were convinced that the agency’s acting director, Nick Andersen, was likely to continue holding the role. He was running out of days to hold the “acting” position under the law, but putting forward a nominee could pause the clock on that deadline.

The administration was thought to be looking for someone from a high-profile tech company to fill the CISA director position, a bill LoSapio fits.

The post Trump picks Palantir’s LoSapio to head CISA appeared first on CyberScoop.

Trump Backs Nvidia CEO Jensen Huang Amid Chinese Spy Affair Investigation

President Donald Trump says the FBI is investigating Nvidia CEO Jensen Huang's affair with a woman alleged by U.S. intelligence to have gathered information for Beijing. "I know the FBI is looking into it in terms of something else, and I think that he'll be in good shape," Trump said at a White House briefing. The Associated Press reports: Trump suggested the extraordinary step of directly involving himself in a counterintelligence investigation, a sign of his friendly relationship with Huang and the possible geopolitical stakes. "I did speak to him today just to see if he's feeling all right, how you're doing," Trump said. "He said he had absolutely no idea that the person in question was a spy." Trump is slated to meet next week with Chinese leader Xi Jinping in Shenzhen, China, at the Asia-Pacific Economic Cooperation summit, but he was noncommittal about bringing up the situation with Xi. "No, I don't think so," Trump said. "I mean, maybe. I'm sure President XI will ask me about it. I just know Jensen very well. I just think he's a very honorable man." Nvidia has launched its own independent investigation into whether Huang was targeted by a foreign intelligence operation. Meanwhile, China has denied the allegations. "The so-called Chinese spy allegation is unsubstantiated. It is nothing but smears against China," Chinese Foreign Ministry spokesperson Guo Jiakun said during a regular news briefing Monday. Further reading: Commerce Dept. Chip Inquiry Was Halted After Nvidia Intervention

Read more of this story at Slashdot.

Nvidia CEO Jensen Huang Summoned By Congress Over Chinese Espionage Concerns

An anonymous reader quotes a report from Ars Technica: Top Republican lawmakers have asked Jensen Huang to appear before Congress to answer questions after it was reported that US intelligence officials believe Nvidia's chief executive has been targeted by a Chinese spying operation. The chairs of the House committees on China, foreign affairs, and intelligence wrote to Huang this week asking him to appear before a joint closed-door briefing for their committees on November 18. "Recent reports raise significant national security concerns regarding the People's Republic of China's access to sensitive US technology and information," representatives John Moolenaar, Brian Mast, and Rick Crawford wrote. "The issue of PRC infiltration and access to cutting-edge US technology is core to the investigative work of our three committees this Congress. It is vital that Congress determines the extent to which US national security has been placed at risk," the lawmakers added. The New York Times last week wrote that US intelligence officials believed Huang had been the target of a Chinese spy operation. The concerns center on a Chinese woman named Alice Huang, an executive at Megaspeed, a Singapore-based cloud company that has bought billions of dollars of Nvidia's chips. Nvidia has rejected the claims and on Thursday would not say if Huang would appear before Congress. "Meetings with customers are part of a CEO's job. Jensen talks with thousands of customer executives every year," the company said. "Our regional cloud customers receive ordinary business information -- not sensitive Nvidia trade secrets -- and zero information relevant to national security," it added. The lawmakers said they wanted Huang to discuss the security protocols Nvidia had in place to protect against "foreign adversary espionage." The company said its chief executive had an "outstanding security team" that travels with him. The New York Times said Huang had not received a "defensive briefing," which the intelligence community usually, but not always, provides potential espionage targets to warn them about the activity. Nvidia said it was confident that the US government would have let the company know if it thought a person was a threat to US industry and that it often receives updates from Washington about people of concern.

Read more of this story at Slashdot.

Air Force cyber official: need to invest in digital forensics

The government needs to invest in digital forensics to keep pace with incidents and threats in cyberspace, the principal cyber adviser for the Department of the Air Force said Thursday.

“In order to detect, help us hunt and find where the incident started… the digital forensics, I believe we need to do, and focus, and invest in that world,” said Wanda Jones-Heath, speaking at the Datadog Threat Response Forum, produced by FedScoop.

The forensics role is vital even though “they’re after the fact,” she said.

“They go and look what happened weeks and months after the incident has occurred, and so I think we need to figure out: ‘How do we keep pace with incidents as they are occurring?’” Jones-Heath said. “Once we identify it, then you start looking at the forensics of what happened, who did it, where they are, where it originated from and then how you partition the areas that are still under fire while you continue to operate in that environment.” 

Jeffrey Hunt, global operations branch chief for the Department of Defense Cyber Crime Center, which provides digital forensic investigations, said at the same event that the divide between operations and security on getting visibility into networks about threats is an issue that needs to be addressed early.

But Hunt said combining the teams into one big unit is a “disaster” that doesn’t work.

“It means that you at least want to have sort of a liaison relationship where somebody from security is in the room as part of the planning team from the beginning of where your operational plan starts,” he said.

Another recommendation Jones-Heath made is changing how cyber exercises are conducted. The goal is not to be in “reactive mode” when an incident happens and knowing what to do with the “data is poisoned.” 

“They’re not designed typically of how we would operate if we have engagement,” she said. “So we have to change the lens to be more outside of the box — let the cyber team actually be engaged on the offensive and defensive side.”

“We have to get over the fact that it could never happen,” she continued. “So sharing that intel about what the adversary is doing, real world, may convince those who are not in our community to let us be a part of the exercise, show them and demonstrate what the adversary is actually doing, so that if we are in formation and you get disconnected. You know exactly what to do.

The post Air Force cyber official: need to invest in digital forensics appeared first on CyberScoop.

❌