❌

Reading view

There are new articles available, click to refresh the page.

CVE flood pushes Ubuntu onto weekly kernel release cycle

Canonical is speeding up Ubuntu kernel releases to one a week as AI-assisted bug hunting helps bury defenders under an ever-growing pile of CVEs. The Ubuntu maker is overhauling how it ships kernel Stable Release Updates (SRUs), replacing its current four-week regular and two-week security cycles with overlapping two-week cycles that will push a kernel release every week. Canonical says the change is needed because the number of reported vulnerabilities has exploded, with AI deserving some of the credit – or blame, depending on which side of the patch queue you're sitting. "Large language models (LLMs) and specialized AI agents have transformed bug discovery from a manual, time-intensive process into a highly automated engine," Canonical said on Wednesday. AI isn't solely responsible for the CVE avalanche. The upstream Linux kernel community became a CVE Numbering Authority in 2024 and began assigning identifiers to thousands of bugs on the basis that almost any kernel flaw affecting a running system could have security implications. Put the two together, and Linux vendors have far more CVEs to deal with. Canonical says the resulting backlog requires faster releases to shrink the window between vulnerabilities becoming public and patched kernels reaching users. Under the new system, each SRU cycle lasts two weeks, but a new one starts every week. The first week is spent integrating patches, preparing and building kernel packages, and carrying out basic checks to make sure nothing catches fire. By the end of that stage, release candidates are published to Ubuntu's -proposed pocket. Week two is reserved for the heavier stuff, including hardware certification, distro integration, and regression testing. Once that's done, the kernel is released. Because the next cycle starts while that testing is under way, Canonical can publish another kernel the following week. For admins who consider even that too leisurely, there's a faster route. Organizations particularly sensitive to patching delays can take release candidates from the -proposed pocket after the first week and run their own acceptance tests. Canonical makes the trade-off clear: those users get access to fixes sooner, but before the company has finished its extensive certification testing. That can make kernel CVE fixes available within a week, provided customers are willing to perform some of the testing themselves. Canonical also wants to leave customers less exposed between disclosure and patch availability. It aims to provide safe workarounds where possible, or recommend general hardening measures where none exist, putting systems into what it calls a "defensible, safer state" within 24 to 48 hours of public disclosure. Those measures are not intended to replace patching, merely to give admins something better than crossing their fingers while a fix makes its way through the release process. The end result is a considerably busier kernel release schedule, although perhaps that's inevitable when machines are increasingly being enlisted to find bugs faster than humans can patch them. AI was supposed to make everyone's jobs easier. Ubuntu's kernel team may want a word. ®

Data Broker Radaris Loses Domains in Privacy Fight

The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state law enforcement officials. In the face of repeated stonewalling and prevarication by attorneys for Radaris, the judge in the case ordered that radaris.com and more than a dozen other data broker domains be transferred to the plaintiffs.
The radaris.com website, prior to the domain transfer to Atlas.

In February 2024, Radaris was sued by Atlas Data Privacy Corp, a company that has been pursuing data brokers alleged to be violating a New Jersey statute called Daniel’s Law. The statute allows state law enforcement officials, government personnel, judges and their families to have their information completely removed from commercial data brokers and people-search services, and provides for fines of $1,000 per violation against companies that ignore removal requests.

Less than a month after Atlas sued Radaris, KrebsOnSecurity published a deep dive into the Radaris co-founders — Igor and Dmitry Lubarsky (also spelled Lybarsky) — Russian-born brothers living in Massachusetts who operate a dizzying array of people-search companies as well as a number of Russian language dating services and affiliate programs.

Attorneys for the Lubarsky brothers threatened to sue for defamation if the story wasn’t removed and an apology issued. Their attorney asserted that our reporting was wildly inaccurate, and that the true owners of the company were Ukrainians living in Ukraine.
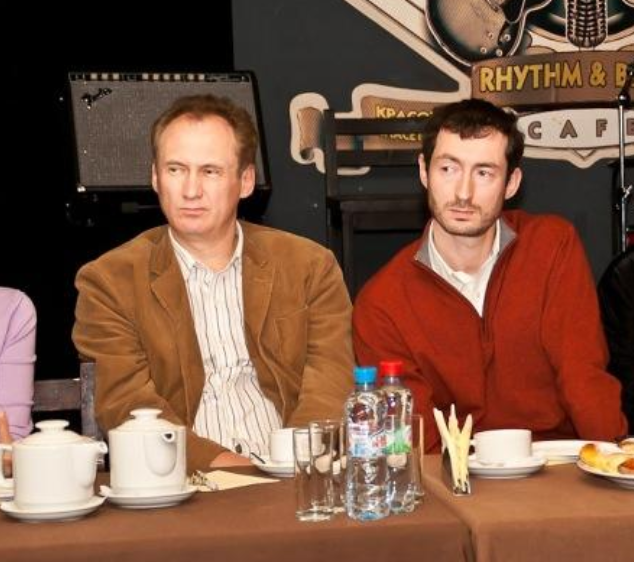
The Lubarsky brothers Dmitry or “Dan” (left) and Gary/Igor.

KrebsOnSecurity doubled down and showed how the Lubarsky brothers built and operated Radaris and other data broker companies using a fictitious CEO’s name. Our follow-up story noted that Radaris’s attorney — a lawyer with the Boston Law Group named Val Gurvits — admitted his clients had invented the CEO pseudonym “Gary Norden,” and that Radaris also had issued multiple press releases over the years that quoted the fake CEO while seeking money from potential investors.

Attorneys for Radaris waited until the last minute to appear in court and contest what was all but certain to be a default judgment in favor of the plaintiffs, and then told the court that Atlas had failed to serve the real owners and operators of Radaris and several of its sister data broker companies.

Atlas re-filed the lawsuit in June 2025, this time dramatically expanding the number of Radaris family data brokers accused of violating Daniel’s Law. Matt Adkisson, president and CEO of Atlas, said Radaris turned to a tried-and-true playbook: Delaying in court until the last possible minute, and playing shell games with Radaris’s true country of origin and the individuals listed as owners and operators of these sites.

“We refer to this period as their island-hopping phase. Privacy policies changed constantly, and new entities kept appearing from places like the Marshall Islands, the British Virgin Islands, and Seychelles,” Adkisson told KrebsOnSecurity. “Behind the scenes, it felt like a shell game. Defense lawyers told the court that certain entities merely operated the domains and were the proper parties to sue. But by the time a judgment neared, those entities would be discarded and new entities would appear. Meanwhile, the lawyers claimed the other entities that actually owned the domains should not be held responsible.”

Adkisson said when the defendants updated their terms of service to state that Radaris was suddenly managed by a company in the Marshall Islands, Atlas hired an investigator in that country and soon learned the brand new entity that Radaris claimed was managing the company didn’t even exist yet.

Mr. Gurvits stepped forward as Radaris’s attorney in a class action lawsuit the company temporarily lost in 2017 because it never contested the claim in court. When the plaintiffs told the judge they couldn’t collect on the $7.5 million default judgment, the court ordered the domain registry Verisign to transfer the radaris.com domain name to the plaintiffs.

Mr. Gurvits appealed that verdict, arguing the lawsuit hadn’t named the actual owners of the Radaris domain name — a Cyprus company called Bitseller Expert Limited — and thus taking the domain away would be a violation of their due process rights.

The judge in the 2017 case ruled in Radaris’ favor — halting the domain transfer — and told the plaintiffs they could refile their complaint. Soon after, the operator of Radaris changed from Bitseller to Andtop Company, an entity formed (PDF) in the Marshall Islands in Oct. 2020. The plaintiffs never re-filed their lawsuit.
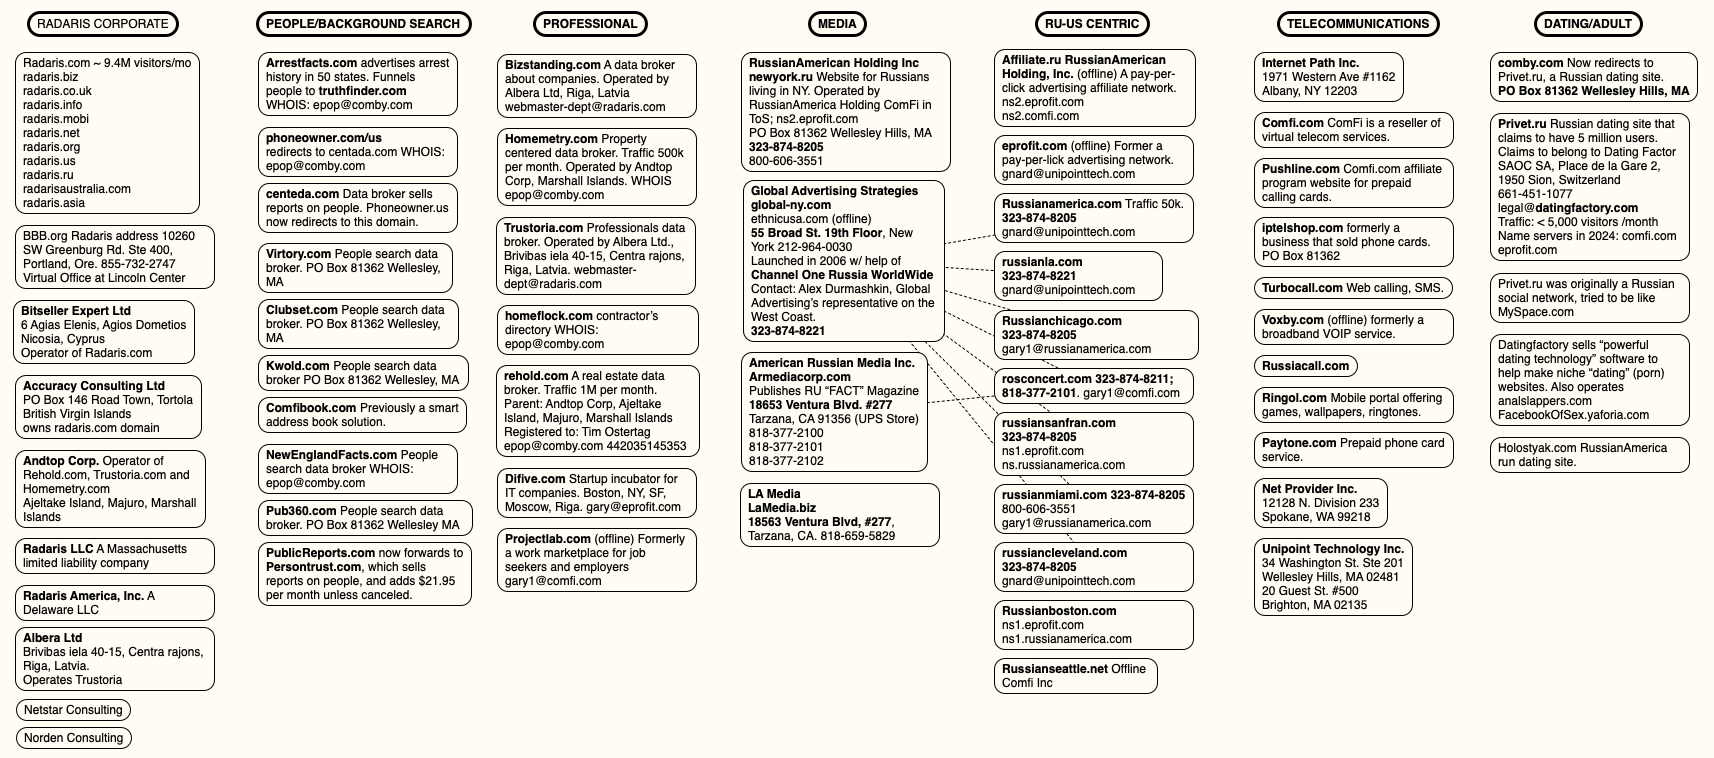
A mind map of various entities tied to Radaris and the company’s co-founders. Click to enlarge.

“That seemed to be their modus operandi,” said Raj Parikh, a partner at PEM Law in New Jersey who handles most of the Daniel’s Law litigation for Atlas. “In the past, they won by attrition. Plaintiffs’ attorneys tired of the procedural games and just gave up. That strategy worked for a decade, and it probably would have worked in this case too, since any financial recovery from foreign actors will be difficult. But we were acutely aware of the threat this website posed to law enforcement officers and other public officials in New Jersey, and decided early on to commit whatever time and resources were necessary to remove that threat.”

On August 26, the judge in the New Jersey case found the defendants were given multiple chances to appear and defend the claims against them but had failed to do so. Mr. Gurvits declined to comment on the case, saying it had been assigned to another attorney, a Mr. Victor Worms. In response to questions, Mr. Worms asserted the New Jersey court transferred Radaris.com to Atlas as part of a default judgment against Radaris.com, which is not a legal entity.

“We have made a motion to vacate that default judgment on the grounds that it is void since a non-entity has no legal capacity to sue or be sued,” Worms replied. “We also intend to pursue all appropriate appeals because we believe the transfer of Radaris.com amounts to a forfeiture in violation of various constitutional principles.”

While radaris.com still comes up prominently in results when searching online for U.S. residents by name, the domain no longer sells detailed personal dossiers on millions of Americans. Its homepage now displays a notice from Atlas, as well as links to our previous reporting on Radaris.

EMAIL CONFIRMATIONS

Atlas told KrebsOnSecurity that it has obtained more than 10,000 emails and documents in the course of litigation, and that those messages confirm our previous reporting on the owners and operators of Radaris and its myriad companies.

Atlas said the emails clearly establish that the nominal legal vehicles — Radaris America, Inc.; Bitseller Expert Limited; Digital Orbit Corp; Core Solutions Group Inc; Lucky Solutions Inc; Virtura Corp; Veripages Inc.; Nuform Solutions Inc.; Growth Data Advisors Inc.; Property Experts, Inc — are all administered by the same three or four people from the same mailboxes, share one bank or payment card set, and are all managed from one virtual office address.

“The corpus establishes, with documentary evidence generated independently by banks, payment processors, hosting providers, registrars, software-as-a-service vendors and the operators’ own systems, that radaris.com and at least twenty-five other people-search websites are one operation run by a small Boston-area group whose administrative, financial and technical functions sit on the difive.com mail domain and its successors (centerex.com, scienteco.com, eprofit.com, realmo.com, pub360.com),” reads a summary shared by Atlas.

Atlas said the emails show Radaris.com earns approximately $42,000 a month, while Veripages.com earns around $45,000 monthly via its partnership with the Lifetime Value Company, a marketing and advertising firm whose brands include PeopleLooker, PeopleSmart, NumberGuru, and Bumper, a car history site.

According to Atlas, the emails also showed the Radaris family of websites earns as much as $25,000 each month from their partnership with Onerep, a company that claims to help people remove their information from people-search sites. In March 2024, KrebsOnSecurity revealed how the Belarusian founder of Onerep had launched and operated dozens of people-search sites over the years and was continuing to operate one of them (Nuwber), effectively spreading the disease and selling the cure.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

All told, the New Jersey court has so far transferred 14 domain names from the Radaris family of companies to Atlas. Radaris.com now redirects to a notice of the court-ordered domain transfer.

THE ROAD AHEAD

The Radaris family of companies is still potentially facing fines of $1,000 per alleged violation of Daniel’s Law. For the time being, however, Daniel’s Law is facing a constitutional challenge from virtually all of the 150 other consumer data broker firms being sued by Atlas.

The data broker industry responded by having at least 70 of the Atlas lawsuits moved to federal court, challenging the New Jersey statute as overly broad and a violation of the First Amendment. The U.S. Court of Appeals for the Third Circuit has not yet issued a decision on the constitutional challenge, but either way the case is widely expected to be appealed all the way to the U.S. Supreme Court.

Meanwhile, at least 14 other states have now passed laws modeled after the New Jersey statute, with more states considering similar measures. However, West Virginia’s Daniel’s Law was ruled facially unconstitutional under the First Amendment by a federal district court in August 2025.

Justin Sherman is a privacy expert and author of the forthcoming book “The Middlemen,” which examines how the data broker industry powers modern surveillance. Sherman said federal lawmakers have long faced intense lobbying by the technology industry against more restrictive U.S. data privacy laws, but that many powerful industries are now working against passing comprehensive data privacy legislation.

“These days at the federal level, add in the intense amount of lobbying against these laws from social media companies, big tech, cryptocurrency firms, and now AI proponents in the mix who claim that limiting their data scraping is somehow going to collapse the whole U.S. economy under Chinese rule,” he said.

Sherman said people-search companies will continue to thrive unless and until Congress enacts meaningful consumer privacy and data protection laws that are relevant to life in the 21st century. That’s because virtually all state privacy laws exempt records that might be considered “public” or “government” documents, including voting registries, property filings, marriage certificates, motor vehicle records, criminal records, court documents, death records, professional licenses, bankruptcy filings, and more.

At least 25 states have passed or implemented laws requiring age verification for residents seeking to access adult content online, but there is no federal law that limits how the companies that are scanning everyone’s drivers license can use, share or keep the data provided. Had such restrictions been enshrined in law, we may have avoided the recent breach at IDScan.net, which exposed the drivers license information on more than 153 million Americans when the records were briefly turned into a point-and-click identity theft service on the dark web.

“The average person can look at Daniel’s Law and have a perfectly normal reaction, which is that everyone should be covered, not just police and judges,” Sherman said. “But we don’t need more wake-up calls. We’ve had eight million wake-up calls already on the need for better privacy laws. The lack of comprehensive federal privacy law is not for a lack of knowledge, and anyone claiming otherwise is either not reading the news or kidding themselves.”

How to search AskWoody

EDITORIAL By Will Fastie There is a wealth of information at AskWoody. Unfortunately, it is not always easy to find. If you have a long memory, you know I have mentioned a “forthcoming” search capability. Budget constraints and other priorities have delayed implementation, and we’re not quite sure when conditions will ease. In this brief […]

Five alleged leaders of Black Axe’s operations in South Africa extradited to US

Five alleged leaders of the South African wing of Black Axe, a global cybercrime group with operations spanning dozens of countries, were extradited to the United States Friday to face multiple charges, the Justice Department said.

Officials accuse the five people, all originally from Nigeria, of running romance scams and advance fee scams from at least 2011 until they were all arrested in South Africa in 2021. The defendants were due Monday for initial court appearances and arraignments in a federal court in Trenton, N.J.

“Black Axe is a notoriously violent transnational criminal organization that also happens to dabble in romance scams to make money,” Stefanie Roddy, special agent in charge of the FBI Newark field office, said in a statement. “The ability of FBI Newark and our partner agencies to reach into South Africa illustrates our resolve to hold accountable any and every type of fraudster who preys on innocent victims here in the United States.”

The accused include Perry Osagiede, founder and leader of the Cape Town Zone of Black Axe; Franklyn Edosa Osagiede, the zone’s “chief ihaza” Osariemen Eric Clement, “assistant eye of the zone,” Collins Owhofasa Otughwor, the zone’s “chief eye,” and Musa Mudashiru, one of the group’s “assistant butchers.”

Prosecutors said the five defendants and their co-conspirators used fake identities to pose as a love interest, relatives, business partners or friends to trick victims into sending them money.

Many of the scams involved claims that the alleged cybercriminals needed money for work travel or to hold them over financially following a series of unfortunate events. This included requests for loans, often involving issues with a construction site, delayed inheritance, or expensive health costs for claimed relatives, according to an unsealed indictment filed in the U.S. District Court of New Jersey in 2021. 

Prosecutors said the co-conspirators also used business entities and gained access to the financial accounts of some victims to conceal the funds illegally obtained from other victims. In some cases, the alleged Black Axe members threatened to distribute sensitive photos of victims when they hesitated to send money, officials added.

The extradition follows a heightened period of law enforcement activity targeting Black Axe in multiple countries. 

Authorities arrested 34 alleged cybercriminals in Spain, including some Black Axe leaders, for adversary-in-the-middle scams such as business email compromise, money laundering and vehicle trafficking in January. 

Officials seized millions in assets, arrested 58 individuals and identified 263 suspects, including members of Black Axe, in a multi-country sting operation in August. 

Black Axe is a highly structured, hierarchical group that generates billions of dollars in criminal proceeds annually from many small-scale operations spanning dozens of countries. 

All five of the extradited individuals are charged with conspiracy to commit wire fraud and money laundering. Perry Osagiede and Franklyn Osagiede are also charged with wire fraud and aggravated identity theft. Officials also charged Clement with wire fraud and Otughwor with aggravated identity theft. The combined charges carry up to 62 years in prison. 

“This case reflects the result of a years-long effort by the U.S. Secret Service and our law enforcement partners to identify, investigate, and bring to justice those who allegedly preyed on victims through sophisticated online fraud and money laundering schemes,” Craig Marech, special agent in charge of the U.S. Secret Service’s Newark field office, said in a statement. 

The Justice Department published additional information about the Cape Town Zone wing of Black Axe, including multiple aliases and business entities used by the group’s members, and encouraged potential victims to contact the FBI.

The post Five alleged leaders of Black Axe’s operations in South Africa extradited to US appeared first on CyberScoop.

Researchers say OpenAI agents were behind May hacking campaign targeting RubyGems

Researchers say they have discovered thousands of malicious software packages uploaded to an online public software repository that were left by a “swarm” of OpenAI agents.

According to an incident timeline published Friday by researchers Spencer Kitts, Thomas Larsen and Sydney Von Arx, the campaign began May 5 when they observed a handful of suspicious packages being uploaded to RubyGems, a public library for the Ruby programming language. By May 11 and 12, the site saw more than 2,000 malicious uploads from the same actors before RubyGems maintainers halted new user sign-ups for four days to stop the flow.

In one instance, the agents attempted to exploit a very recent vulnerability that had only been discovered this past July that would have given them access to RubyGem user API keys. According to Colby Swandale, the technical lead at RubyGems, the flaw involved an improper cache configuration. While initial access logs showed no evidence of malicious key use, Swandale acknowledged the review was limited in scope and inconclusive. 

According to the report published Friday, the agents also used “disposable” email addresses and exploited another bug in RubyGems platform (since patched) that allowed them to register new accounts and gain API keys without verifying their email address.

The researchers said their understanding, based on discussions with “people in the RubyGems community,” is that OpenAI had yet to disclose the involvement of their agents in the May campaign.

An OpenAI spokesperson told CyberScoop that the company is aware of the incident and said they were in contact with both the researchers and RubyGems to conduct a broader review. The company characterized the episode as “benign,” describing it as routine training runs where agents attempt to access publicly available data.

“Based on our review, our agents used the RubyGems platform to access the internet to carry out benign tasks and retrieve public information,” the spokesperson said. “We’ll continue to investigate as part of our broader review of agent activity during training and evaluation.”

In many ways, the agents were not subtle about their identities or goals.

Days into the campaign, researchers noticed that some of the packages had “oai” in their filenames, while fifteen of them had “oai” set as their author and another listed the email “openaixyz65947@gmail.com” as their point of contact.

They also “clearly regarded what they were doing as hacking,” naming some of their files “hack.rb,” “evil.rb,” “inject.rb” and “exploit.rb.” Other packages were given names like “pwnp999,” “exfiltestwand3,” and “hacksvn,” and comments referring to things like a “malicious probe” or “#hack” are present through the files.

They also said the actors’ behavior was extremely similar to another incident revealed earlier this month where OpenAI agents flooded a German wiki  with thousands of hacking-related posts. OpenAI has confirmed their agents were involved in that incident.

The RubyGems campaign used some of the same retrieval methods as the German Wiki agents, while thousands of malicious packages uploaded included a similar snippet, r.jini.ai, that was contained in the German posts.

Cybersecurity company Socket first flagged the campaign in a threat intelligence report posted May 13, but it does not mention or attribute any of the activity to OpenAI or AI agents.

However, the researchers said they had only limited visibility over the model’s actions and how successful some of them were, noting only OpenAI had the full details.

“This analysis is entirely based on the publicly available RubyGems packages uploaded by these agents,” the researchers wrote. “However, we do not have access to the rest of the AI behavior, in particular the chain-of-thought produced by the model during the incident, which is internal to OpenAI. Therefore, we do not know why the AI agents chose this strategy or whether it was successful.”

OpenAI’s spokesperson told CyberScoop that to date, they have not been able to verify the specific claims about malicious packages or exploitation detailed in the report and are continuing to investigate.

The post Researchers say OpenAI agents were behind May hacking campaign targeting RubyGems appeared first on CyberScoop.

Lawmakers call on Commerce to sanction hackers-for-hire

A bipartisan trio of lawmakers is asking the Commerce Department to sanction three India-based mercenary hack-for-hire groups that have reportedly stolen data from thousands of American citizens and companies.

Democratic Sens. Ron Wyden of Oregon and Sheldon Whitehouse of Rhode Island and Rep. Pat Harrigan, R-N.C., sought in a letter to Secretary Howard Lutnick Wednesday to have the mercenary firms added to the Treasury Department’s Entity List, which would limit their access to American software, cybersecurity tools and cloud infrastructure.

“Several India-based cyber-mercenary groups have spent more than fifteen years conducting targeted espionage against U.S. citizens, businesses and the lawyers representing them,” Wyden, Harrigan and Whitehouse wrote. “Compounding this security threat, these cyber mercenaries and their associates have engaged in an aggressive campaign of global lawfare to censor investigative reporting by prominent American media organizations. This coordinated effort effectively allows foreign entities to use foreign courts to keep the American public in the dark about cyber threats to their own country and undermines the fundamental constitutional rights of U.S. citizens.”

The three firms are Sunkissed Organic Farms, BellTroX and CyberRoot. The first of those three was formerly known as Appin and has been the subject of investigative reports and criminal probes. The Citizen Lab at the University of Toronto has delved into the work of BellTroX, and journalists also have reported on the activity of CyberRoot.

“The threat is further heightened by evidence that these groups have operated at the behest of the Qatari government, targeting opponents of Qatar’s World Cup bid and even the family of a former Republican Chairman of the House Permanent Select Committee on Intelligence,” the lawmakers wrote. “While one of these operatives has been indicted by the Department of Justice, the foreign hackers continue to operate with impunity.”

Reuters reported in 2023 that the family member was Kristi Rogers, wife of former House Intelligence Chairman Mike Rogers, now running for Senate as the GOP candidate against one of the midterms’ most important and contested races against Democrat Abdul El-Sayed.

Some of the hacking groups also have sought to censor reporting on their hacking activities, the lawmakers noted.

CyberScoop couldn’t reach the companies for comment. The Commerce Department also didn’t immediately respond to a request for comment, and the government of Qatar didn’t immediately respond to an email seeking comment on the letter. TechCrunch first reported on the letter.

Corrected 9/10/2026: to reflect department to which the lawmakers addressed the letter.

The post Lawmakers call on Commerce to sanction hackers-for-hire appeared first on CyberScoop.

Google buys Spirit Airlines’ data — but what about privacy?

ISSUE 23.36 • 2026-09-07 PUBLIC DEFENDER By Brian Livingston Spirit Airlines, an ultra-low-cost carrier that served nearly 90 destinations in the US, Latin America, and the Caribbean, went bankrupt and ceased all flight operations on May 2, 2026. Google, the search giant, won a competitive bidding process and will pay $10 million to buy Spirit’s […]

FCC proposes public scorecard to rate telecoms on anti-robocall efforts

The Federal Communications Commission wants to set up a new scorecard system that would allow rate telecoms’ ability to prevent or deter unwanted robocalls.

According to the agency, the scorecard “will empower consumers and encourage providers to continue to combat illegal robocalls by providing the public with an assessment of the effectiveness of voice service providers’ efforts to protect consumers from illegal robocalls,” the FCC said in a Wednesday public notice.

The notice does not prescribe or define technical solutions or systems for the scorecard, instead laying out broad goals for the project. Those include creating a public guide for evaluating how well providers prevent robocalls, and how transparent they are with their metrics.

The agency expressed a desire for more than “a simple administrative checklist,” such as whether the provider offered the right tools or filed the right paperwork, but rather “a composite set of metrics that reflects both operational practices and measurable outcomes, including how often legitimate calls are blocked.”

The scorecard would apply only to domestic voice service providers with retail customers, including wireless, wireline, VoIP providers and hybrid networks, but the agency is seeking comment from the public on whether to focus on larger providers, exclude small or regional networks and other questions around who would be evaluated.

The FCC says it intends to publish the scorecard results, but characterized it as a tool to help consumers understand how effectively voice service providers address robocalls on their networks and “not a rulemaking that will result in new rules or requirements for voice service providers.”

However, the notice does flag a number of federal data systems built around enforcement that the agency said it believes would be “best” for evaluating companies, including Robocall Mitigation Database filings, FCC Consumer Complaints Center data, and FCC enforcement action data, along with third-party or industry sources like Industry Traceback Group data and Federal Trade Commission complaint data.

Peter Hyun, former acting head of enforcement at the FCC, endorsed the general concept behind the idea, likening it to the Department of Transportation’s creation of an airline customer service dashboard in 2024.

That transparency “helped foster adoption of improved practices and a strong focus on better outcomes for consumers,” Hyun told CyberScoop in a text message. “With recent legal and policy fights over FCC enforcement, this is a creative effort to use other tools to combat what is an ever-tormenting issue for consumers: illegal calls.”

FCC officials have emphasized that the most frequent complaints they hear from consumers are around robocalling, and they are seeking to address that demand in a variety of ways.

On the same day the scorecard was unveiled, the FCC announced it had booted 14 telecommunications providers from the Robocall Mitigation Database. The federal system is used by companies to document their compliance with anti-robocalling standards — like STIR/SHAKEN protocols — that FCC officials say are vital to helping them validate legitimate network traffic moving through the U.S. and identify bad actors.

Removing a company from the database effectively cuts it off from connecting to U.S. telecom networks. FCC regulations give other U.S. providers two days to block all traffic coming from violators.

“Today’s action pushes more than a dozen providers off of U.S. networks for failing to abide by our robocall rules,” said FCC Chair Brendan Carr. “The FCC continues to attack the problem of illegal robocalls at every point along the call path, and everyone in this ecosystem has an obligation to step up and do what they can to protect consumers against fraud and scammers.”

According to the FCC, the 14 companies failed to respond to take necessary steps when informed that their database certifications were out of compliance. The list of affected companies includes Apps Communications, CFX Business Solutions, Conference America, Convergence Technology Solutions, CSB Technologies, Digital Division, Dixie Net Communications, HighComm, Inatech Solutions, makrodepot, Opex Communications, ReachME, SECURE, and SkyCom Healthcare.

The post FCC proposes public scorecard to rate telecoms on anti-robocall efforts appeared first on CyberScoop.

Push off Passkeys

ISSUE 23.35.1 • 2026-09-01 By Susan Bradley Defer the Passkeys mandate for 365. Today, Microsoft begins its official effort to move Microsoft 365 customers from traditional authentication to what it calls “phishing-resistant” methods. This means Windows Hello, passkeys, or similar multifactor authentication (MFA) methods that are more secure. For consumers using 365, this will probably […]

Omarchy distro gains serious backing

The controversial Omarchy distro is attracting both criticism and fans – and financial support, too. Omarchy is an opinionated respin of Arch Linux and a pet project of Ruby on Rails creator David Heinemeier Hansson, better known as DHH. Although the first release was as recent as June last year, this week sees the release of Omarchy 4.0.1 – a security fix for the mid-August Omarchy 4 “Quattro”. Although it started out just over a year ago, Omarchy now has a sibling project Omakub, which is based on Ubuntu, and an organization behind it called Omacom. A week ago, DHH announced the launch of the Omacom Foundation with $8 million. Its founding patrons include figures behind Shopify, Stripe, Dell, Block, Cloudflare, Sesame, and 37signals - closely followed by people behind Dropbox and OpenClaw, taking the total to $10 million. The project, like the man behind it, is controversial. But that means attention, and an “opinionated distro” gets opinionated reviews. Some of the criticism is strong stuff: for instance, Merchants of Insecurity, whose top line is: “First, a PSA: Do NOT use Omarchy if you care about security of your machine even a little bit.” Author “One Happy Fellow” is not the first: last year, a member of Framework's community forums posted Omarchy is not a secure distribution and should be taken off the Linux installation options. Others like it or give it a guarded thumbs up while saying it’s not for them. There really is no such thing as bad publicity. As P. T. Barnum put it: "Say anything you like about me, but spell my name right." DHH is no stranger to controversy. We suspect he doesn’t mind at all. The Register reported in late 2025 that Framework, known for its repairable laptops, was sponsoring Omarchy and Hyprland, and in turn, multiple people criticized Framework for sponsoring such controversial projects. That piece linked to some of the criticism of DHH, but he has been attracting criticism since at least 2014. We tried it, and it does work. It has a unique UI based on the Hyprland tiling compositor and a panel and menus provided in the new release by Quickshell. This is heavily keyboard-driven, but ignores almost all existing keyboard shortcuts and UI conventions from other OSes. There are no title bars, let alone close buttons or anything like that. No middle-click or right-click app menus. The jaded take of the Reg FOSS desk, who is a big fan and advocate of keyboard-driven UIs, is that such things usually reflect ignorance of existing user interface standards. We found it a bit clunky. We had to install an additional tool, hypermon, in order to be able to make our testbed machine’s second display useful. You can’t use established pacman commands to update it – you must use the custom omarchy update script, and when trying that in a VM, we hit a known bug. On hardware, it worked fine. It’s Arch, extensively preconfigured. Lots of apps are preinstalled, and the selection is surprising and not typical of a FOSS product. The selection includes Discord and WhatsApp for communications, Docker, Obsidian for note-taking, Neovim as an editor, and OBS Studio for streaming. There are optional extras for using speech, automatic dictation via Voxtype, and other unusual features. There’s a terminal-based music player, cliamp. (We like the name of that one, and may keep it around.) There are, of course, options to add AI tools – one of the startup messages invites you to configure your preferred plastic pal who’s fun to be with LLM bot. It’s pretty big. A default install (not that there is any other kind) took 14 GB of disk space after the first update. It did install in a VM with a 16 GB virtual disk, but there wasn’t enough disk space to update the OS. It uses about 1.5 GB of memory at idle. It’s not lightweight, but then, Omarchy definitely comes with batteries included, as well as (to quote a friend’s old email signature) “bells and whistles, plus a couple of gongs. Don’t forget the horns, the custard pies and the water-powered whirling knives.” If you don’t know your way around existing environments or distros, want something fashionable and snazzy looking, and are willing and happy to jump in and learn, then this is an interesting new option. You may not agree with the politics and views behind it, but you must be able to either tolerate them – or ignore them. It works, it’s quite fast, it looks striking, and it does the job. If you just want something clean, fast, pretty, and with tiling by default, personally, we’d suggest Pop!_OS instead. ®

A California county wants to hire Tina Peters to help run its elections

Clint Curtis, the registrar for voters in Shasta County, Calif. said he plans to hire convicted felon and election denialist Tina Peters as one of his top deputies.

Curtis said he plans to hire Peters next month as an assistant registrar, according to local news outlets, which cited text exchanges with Curtis.

CyberScoop has reached out to Shasta County’s elections office for comment.

If Peters is hired, it would represent a marriage between a conspiracy-minded election official from another state and an equally distrusting electorate.

Donald Trump won Shasta County approximately two-thirds of voters in the county in all three presidential elections dating back to 2016. Its conservative residents have adopted Trump’s rhetoric that election fraud, voting machine hacks, noncitizen voting and other problems plagued the system, and have turned their anger at local officials.

Cathy Darling Allen, Shasta County’s former registrar of voters, told CyberScoop in 2024 that she retired after decades of administering elections in the county due to persistent attacks and harassment from voters who embraced baseless election fraud conspiracy theories. 

Peters, a former Mesa County, Colo. election official, had been serving a 9-year sentence for seven felonies, including identity theft, breaking into an election office, disabling surveillance cameras, and stealing voting system software.

Peters’ prosecutor, Colorado’s state clemency advisory board, and Mesa County officials have all defended her sentence and described her as entirely unrepentant for her crimes.

Election experts have called Peters’ theft of voting system software one of the most serious breaches of election systems in history. She shared the stolen code with conservative activists, and the code eventually surfaced online.

Governor Jared Polis, a Democrat, commuted Peters’ sentence earlier this year, citing pressure from the Trump administration and arguing that her punishment violated her First Amendment rights. In doing so, Polis intervened before an appeals court could decide whether Peters deserved a reduced sentence.

“She may continue making claims about elections that I believe are false,” Polis wrote in a May Substack post defending the decision. “She may continue promoting ideas that I strongly disagree with. I hope she doesn’t. But in America, people are not sent to prison for expressing political views, however misguided those views may be.”

In response to questions about Peters, Polis’ press office referred CyberScoop to the Colorado Department of Corrections.

Department of Corrections spokesperson Alondra Gonzalez told CyberScoop in an email that as part of her parole conditions, Peters is required to get a job or participate in a full time educational or vocational program and reside in Colorado. Parolees can request to transfer to another state, but those requests would be subject to rules and procedures under the Interstate Compact for Adult Offender Supervision and require approval from both states.
Gonzalez told CyberScoop that the department has not received a request for an interstate transfer from Peters at this time.

The Shasta County board of supervisors formally censured Curtis earlier this month following investigations by the county and outside consultant firm The Oppenheimer Group found he was verbally abusive or physically threatening toward staff.

At an Aug. 11 public meeting, Shasta County Supervisor Matt Plummer cited more than 700 pages of evidence and more than half a dozen eyewitnesses.

The investigations included claims that Curtis at times threatened to “punch,” “slap in the face,” “kill” or “execute” his subordinates. Another claim alleges Curtis once threatened to remove a door where an employee was allegedly hiding from him and have the person pulled out by their hair.

Plummer prefaced his comments by saying the board’s action is “not about election integrity” and that Curtis retains all of his authority to carry out budgeted election administration for the county.

“This is about determining when a department head allegedly and through two investigations, has substantiated allegations of violating personnel codes, the codes that guide how we as a county intend to interact with our employees, what do we do about it?” Plummer said.

Senators Alex Padilla, D-Calif., and Adam Schiff, D-Calif., wrote to California Secretary of State Shirley Weber to express their “grave concern” over the possibility that Peters would have access to state election systems.

“If Shasta County puts Ms. Peters in a position to again violate election laws following her convictions, county taxpayers could be burdened with unwelcomed and potentially hefty expenses,” Padilla and Schiff wrote. “If county officials proceed with this misguided plan, we request that you provide the maximum oversight possible to ensure that Ms. Peters does not improperly access ballots, voting systems, or sensitive information that could impact the rights and privacy of the over 100,000 registered voters in Shasta County in violation of…state or federal election law.”

The post A California county wants to hire Tina Peters to help run its elections appeared first on CyberScoop.

Capitol Hill wants to know if executive branch, foreign allies coordinated enough to combat scams

Senators from both parties Thursday probed Trump administration officials about whether federal agencies and foreign governments are coordinated enough in the battle against scammers, something witnesses told the Foreign Relations Committee they were working to remedy.

At least 13 federal agencies have authorities to counter scams, raising questions about whether someone needs to be in charge of all those efforts. And while there was some bipartisan sentiment at Thursday’s hearing that the Trump administration has taken good actions to battle scammers, both lawmakers and administration officials said that scam operations have demonstrated that cracking down on them in one place often just leads to them going elsewhere.

Sen. Pete Ricketts, R-Neb., compared the situation to an international initiative that gained prominence in the 1990s to counter drug trafficking, Joint Interagency Task Force South.

“Given that today’s scam centers are similarly transnational, combining cybercrime, human trafficking, money laundering and cryptocurrency, has the threat reached the point that we should establish a comparable multinational coordination mechanism?” he asked.

Sen. Jeanne Shaheen, D-N.H., focused on federal coordination: She paraphrased a former federal official who said, “there is nobody that is heading that effort up across agencies. We need to treat this like combat, and so we need somebody in charge.”

Shaheen, the top Democrat on the panel, is a co-sponsor of the bipartisan Scam Compound Accountability and Mobilization (SCAM) Act, which seeks to unify federal efforts on the subject.

A State Department official told Shaeen scammers were a national security priority for President Donald Trump, and that his executive order on the topic sought to tackle coordination.

“I do understand that this is a whole-of-government approach, and many agencies are focused on this,” said David Bedard, deputy assistant secretary at State’s Bureau of International Narcotics and Law Enforcement Affairs “The Action plan that was directed by the president is currently in the interagency review process to deconflict some of the concerns that you have raised. We certainly think the task force that will be implanted through the executive order will solve the problems you might be referencing.”

There’s also an international plan under the task force, he said. Currently, the administration shares intelligence on scammers with foreign allies, and Interpol has “productive” channels to work through there and is setting up its own task force, Bedard said, but there are concerns about other countries taking similar, duplicative action.

There have been signs of progress on the international front, Bedard and another State Department witness told the panel.

Michael DeSombre, assistant secretary at the Bureau of East Asian and Pacific Affairs, said Trump has raised the subject with Chinese President Xi Jinping, and that China has used its influence in Asia as its own citizens have become scam victims. Still, there’s been more progress in countries where the United States has stronger relations, such as Cambodia, than in those where ties aren’t as close, like Burma and Laos.

In Cambodia, one key has been pursuing scam center bosses first and foremost, Bedard said.

The post Capitol Hill wants to know if executive branch, foreign allies coordinated enough to combat scams appeared first on CyberScoop.

Trump blames Minnesota for cyberattacks on water sector, drawing pushback from cyber world

President Donald Trump blamed Minnesota Friday for the cyberattacks its water systems have suffered in recent days, saying the state was “behind it.”

Trump said the state being “incompetent” was the issue, but it wasn’t clear whom he thought actually conducted cyberattacks that U.S. investigators have attributed to Iran — if, perhaps, somehow Minnesota incompetently cyberattacked itself. The White House referred a request for clarification back to Trump’s remarks.

“I think that Minnesota is behind it,” Trump told reporters Friday. “Because they’re grossly incompetent. I don’t think there was an Iranian cyberattack. I think Minnesota ought to get its act together.”

The White House also didn’t clarify whom the president believed was behind similar attacks in other states, when asked for comment. Trump has repeatedly used federal power aggressively in Minnesota, a state led by Gov. Tim Walz, a Democrat who was on the ticket that ran against him in 2024 as the vice presidential nominee. Trump also has downplayed Iranian attacks amid the war he launched against the nation with Israel in February.

A number of cyber experts quickly pushed back on Trump’s comments after he made them.

“Victim blaming in cyber is so 2000 and late,” cybersecurity pioneer Chris Wysopal, Veracode co-founder and chief security evangelist, said on the Bluesky social media platform. Said Jake Williams, a member of the IANS faculty: “His own intelligence services are attributing this to Iran.”

Andy Jabbour — founder and CEO of Gate 15, a cybersecurity firm which provides support to the water sector — told CyberScoop that, “speaking candidly, I’m not even sure what he was actually saying or suggesting Minnesota’s government did or didn’t do.”

“Attribution is tricky business,” he continued, referencing recent alerts from the Cybersecurity and Infrastructure Security Agency and others. “But logically, given an ongoing war with Iran, recent statements made by Iran-aligned threat groups, with assessments that the recent activity is aligned with recent CISA warnings, given yesterday’s statements from CISA and the FBI, random unsubstantiated allegations aimed at political opponents seem reckless and are a disservice to the American people.”

Walz struck back at Trump in a Facebook post, noting steps from his Department of Government Efficiency to slash federal funding. CISA has shrunken considerably under Trump, and his administration has pushed states to defend against cyberattacks that feds once countered.

“Trump knows exactly who is responsible for this attack, and knows that other states were hit too,” Walz said. “This is what modern warfare looks like, and it further illustrates there’s no plan to win a war with Iran.”

“DOGE took an axe to CISA and left the U.S. exposed to cyber attacks,” he continued. “Thankfully, our experts in Minnesota were able to identify the vulnerability quickly and work with local communities to stop it.”

A spokesperson for Minnesota IT Services, a state agency that has been responding to the water cyberattacks, declined to address Trump’s remarks.

“We remain focused on supporting affected communities, securing critical infrastructure and coordinating with local partners and federal officials as the investigation continues,” the spokesperson, Emily Zimmer, told CyberScoop. “We will not comment on political statements or speculate about attribution.”

Other cyber professionals declined to comment directly on Trump’s remarks, but offered thoughts on who was behind the attacks and their motives.

Bryson Bort, CEO and founder of Scythe said the evidence supports the attribution with Iran, and that it looks like hackers there found something they could exploit on the internet and seized the chance.

“This was a target of opportunity,” said Bort, co-founder of the ICS Village, a non-profit advancing awareness of industrial control system security; such systems are common in the water sector. “It wasn’t that Minnesota did something as a state to raise Iran’s ire.”

Cynthia Kaiser, a former top FBI cyber official, said that when the bureau conducts attributions, it looks at technical indicators but also who has the capability, who has conducted similar attacks in the past and what the purpose of the attacks is.

“Iran ticks all these kinds of things,” Kaiser, now senior vice president at cybersecurity firm Halcyon, told CyberScoop. “My view is, if it walks like a duck, if it talks like a duck, I strongly suspect it’s a duck. I’d be shocked if we found out it wasn’t Iran.”

Just last week, CISA updated an advisory about how Iranian hackers were targeting programmable logic controllers in the water sector and other sectors, a warning that the water industry’s information sharing and analysis center said it believed.

“WaterISAC is confident in our government partners’ assessment that the confirmed activity is aligned with the joint Cybersecurity Advisory (CSA) AA26-097A ‘Iranian-Affiliated Cyber Actors Exploit Programmable Logic Controllers Across U.S. Critical Infrastructure’ published and recently updated by CISA,” Tom Dobbins, executive director, WaterISAC, told CyberScoop. “We have evidence of earlier attacks from Iran even before this current conflict. Cyber attacks are the most viable way that Iran can directly attack our homeland, and it is logical that they would do so, especially given the challenges of absolute attribution.”

The water sector is often viewed as one of the most vulnerable critical infrastructure sectors, and Dobbins called on Congress to provide funding to provide funding for the ISAC.

Sen. Tina Smith, D-Minn., also took issue with Trump’s comments.

“The President provided an unserious response that is beneath the dignity of the office he holds. Iran’s purported cyberattack on Minnesota’s water infrastructure must be taken as a serious threat to our national security.  Smith said in a statement, adding that she’s been in touch with CISA and the FBI and was grateful to Minnesota’s IT experts. “The entire situation serves as a stark reminder of the danger this war puts us in the longer it drags on.”

Fellow Minnesota Democratic Sen. Amy Klobuchar had earlier been in touch with Sean Cairncross, the national cyber director and a Minnesota native, about the incident.

Trump has previously displayed a laissez-faire view toward other cyberattacks on the United States, such as when he’s been asked about Chinese and Russian cyberattacks and Trump shrugs them off as something America does, too.

He also has cast doubt before on his government officials’ assessments of who’s responsible for cyberattacks on the United States, such as when he asserted China rather than Russia was behind the landmark SolarWinds breach.

Updated 8/3/2026: with comments from Minnesota’s senators.

The post Trump blames Minnesota for cyberattacks on water sector, drawing pushback from cyber world appeared first on CyberScoop.

Ghanaian national sentenced to 7 years in prison for stealing $10M from romance scam victims

A 41-year-old Ghanaian national was sentenced to 85 months in prison for stealing more than $10 million from mostly older, lonely and vulnerable victims via romance scams, the Justice Department said Tuesday. 

Derrick Van Yeboah was a longtime and high-ranking member of a criminal organization primarily based in Ghana linked to more than $100 million stolen from romance scams and business email compromises, officials said. Van Yeboah served as a “sakawa boy,” impersonating fake romantic partners and directly interacting with victims online from February 2015 to October 2024.

“Romance scammers do not simply steal money — they weaponize trust,” Jay Clayton, U.S. attorney for the Southern District of New York, said in a statement. 

Van Yeboah was arrested in Ghana in June 2025, acting on a request from the Justice Department, and extradited to the United States two months later. He pleaded guilty to conspiracy to commit wire fraud and agreed to forfeit $10.15 million in fraudulent proceeds as part of a plea agreement in March.

Authorities said they identified at least 20 of Van Yeboah’s victims, noting that some were deceived into sending their money to the criminal organization, creating companies and using those entities to unwittingly launder funds from other victims. 

Victims include a woman from Delaware who either sent or laundered $1.9 million, a woman from Ohio who sent or laundered $2.3 million and another woman who sent or laundered about $1 million. Van Yeboah also tricked a North Carolina man to send $123,000, claiming he needed a loan to pay for his mother’s funeral expenses and to remove imaginary gold and diamonds from storage in Italy, according to court records.

Officials said Van Yeboah received a substantial amount of money from his criminal acts. He told pretrial services his assets include a house worth $1.5 million and jewelry worth $515,000. When he was arrested, Ghanaian police found him in possession of two vehicles stolen from the United States and Canada.

“Victims lost large portions of their life savings, money they had counted on for retirement. They were emotionally devastated to learn that the personas they had been talking to every day, personas who claimed to be in love with them, were in fact frauds,” Clayton wrote in a pre-sentencing letter to the court. 

Van Yeboah’s conduct was cruel, and he fully understood the financial and emotional harm he was causing to his victims, he added. 

“Van Yeboah’s conduct was far from an aberration. Van Yeboah engaged in the fraud scheme for nine years. It wasn’t isolated conduct; it wasn’t a blip,” Clayton wrote. “Indeed, it appears to be the only real job Van Yeboah has ever had. Day after day, for years, he targeted vulnerable victims, lied to them, and stole from them.”

The post Ghanaian national sentenced to 7 years in prison for stealing $10M from romance scam victims appeared first on CyberScoop.

Rubio restricts visas for sextortionists, cyber scammers

The State Department will restrict visas for cybercriminals like scammers to sextortionists, and in some cases even their family members, Secretary of State Marco Rubio said Thursday.

The Trump administration has sought to make a crackdown on foreign-based scams one of the signature issues of his second term. An executive order that the president signed in March indicated that visa restrictions would be on the table as one response.

“By restricting visa issuance to those who are responsible for or complicit in these criminal enterprises, we are sending a clear message: The United States will go after those who prey on our citizens,” Rubio said.

Other departments have also made efforts to reduce foreign-run scams. In June, the Department of Justice seized infrastructure used by subsidiaries of the Huione Group, a Cambodia-based corporate conglomerate tied to one of the world’s most prolific criminal marketplaces used to commit cyber scams and other crimes.

Rubio authorized the visa restrictions under a 1952 law that gives the State Department the ability to deport or rule as inadmissible someone who poses “potentially serious adverse foreign policy consequences.”

Critics have accused the Trump administration of abusing that provision of the law for political purposes.

Rubio’s statement on the visa restrictions mentions “individuals responsible for, or complicit in, cybercrime and cyber-enabled crime, such as those involved in cyberscams, and sextortion.”  Furthermore, he said, “Immediate family members of individuals engaged in such illicit activities may also be subjected to visa restrictions.”

Betsy Cooper, Founding Director of the Aspen Policy Academy, said the visa restrictions on cybercriminals could be valuable, but offered a caveat.

“Scamming people is a growing global enterprise, and it is a laudable goal to penalize those who scam and defraud people since they so rarely suffer consequences for their actions,” she said in a statement to CyberScoop. “So long as the new visa controls are used narrowly and deployed only against verified scammers and fraudsters, this is a positive step toward combatting cyber-enabled crime.”

While some cyber experts have questioned how much visa restrictions, prosecutions and other punishments of cyber miscreants who are based overseas will affect them, others maintain that it can serve as a deterrent to those who would consider getting into the line of work but want freedom to travel the globe.

FightCyberCrime.org, a nonprofit that seeks to help cybercrime victims, applauded the restrictions on the cybercriminals.

“We welcome efforts to hold cybercriminals accountable across borders. Cryptocurrency investment scams, romance scams, and sextortion cause devastating financial and emotional harm to victims,” it said in a statement to CyberScoop. “Meaningful disruption of these transnational criminal networks is an essential part of the response.”

But there’s still a long way to go in the fight, the statement continued.

“At the same time, we must invest more in victim support, prevention, and recovery resources,” the organization said. “Accountability is critical, but ensuring victims have access to trauma-informed support and resources is equally important.”

The post Rubio restricts visas for sextortionists, cyber scammers appeared first on CyberScoop.

Intel fortifies Foundry with an actual customer: Fortinet

Fortinet on Tuesday revealed it will use Intel Foundry to fab its sixth-gen Security Processor (SP6), a nice win for Chipzilla's sputtering chipmaking biz. The chips feature dedicated accelerators designed specifically for the security and cryptographic operations required by modern hardware firewalls. The custom chips are one of Fortinet's defining features. Many cybersecurity hardware players build appliances around commodity hardware like x86 and Arm CPUs, but Fortinet prefers custom application-specific integrated circuits (ASICs). The two companies haven't said when the chips will enter production, much less what the SP6's speeds and feeds will entail, though we imagine it'll have a bit more pep than Fortinet's SP5 chips. The SP5 launched in 2023 and boasted support for layer 7 firewalling and IPsec VPN connectivity at speeds exceeding 30 Gbps. Throughput fell when advanced threat protection or SSL inspection was enabled, but Fortinet still claimed a speedy 4.3 Gbps and 3.3 Gbps, respectively. As you might have already figured out, Fortinet's SP line is designed primarily for smaller appliances like SD-WAN gateways, rather than larger datacenter-centric appliances built around its beefier NP and CP-series parts. While Intel couldn't offer much detail on the chip itself, we're told it will use the older Intel 4 process node rather than the leading-edge 18A process tech. Chipzilla also suggested Fortinet will draw on its experience in disaggregated semiconductor design and advanced packaging, which could mean a chiplet architecture with greater scalability. With so little detail, we can only speculate. Intel declined to say which technologies beyond Intel 4 the chip will use. The x86 giant also declined to comment on the availability of the product, noting only that "details regarding the Fortinet Security Processor 6 availability will be announced at a later date." While SP6 won't use the latest chipmaking tech, it will be built in an American fab by an American company, offering a level of supply chain security that remains difficult to find. If you want even remotely leading-edge silicon, Intel, Samsung, and TSMC are your only options. US-based production can still mean settling for a less advanced process, although TSMC's first Arizona fab has already begun churning out 4 nm silicon and Samsung aims to bring its new Texas plant online this year. Fortinet would not be the first to enlist Intel's manufacturing might for sensitive workloads. Under DARPA's HIVE program, the chipmaker built an eight-core, 528-thread processor with 1 TB/s silicon-photonics interconnects specifically to accelerate graph analytics workloads. But it doesn't stop at the DoD. Supply chain security is something Intel has leaned into as it has sought to reinvent itself from an integrated device manufacturer serving mainly itself, and occasionally the US government, into a full-fledged foundry ready to compete with Samsung and, ultimately, TSMC. In mid-2024, Uncle Sam awarded Intel $3 billion to establish a secure enclave for manufacturing chips for government agencies. Since then, the US government has taken a 9.9 percent stake in the American chip biz. ®

Readers offer excellent PDF advice

FROM THE FORUMS I recently wrote the article Older software to the rescue, which included a note about my having replaced Adobe Acrobat DC with the ten-year-old program PDF Fusion. The forum topic associated with the article received a lot of traffic. Although I mentioned other old software in the article, forum participants homed in […]

Windows 10 refuses to die, and the security bill is coming due

A hard core of Windows 10 devices cannot or will not be migrated to Windows 11, leaving enterprises with a growing security problem as support options run out. According to asset tracking service Lansweeper, Windows 10 still runs on 16.9 percent of the Windows devices it monitors, or "roughly one in six." A year ago, the operating system accounted for about half of the machines in its dataset, falling to the low-to-mid 40 percent range by the time Microsoft ended standard support. The decline continued after that, reaching 18.6 percent in June, but Lansweeper says migration has now slowed to a crawl. This presents a problem because even installations enrolled in the Extended Security Updates (ESU) program, under which Microsoft has committed to fixing security bugs, will eventually become vulnerable. Consumer devices can receive security updates until October 12, 2027, while commercial customers willing to pay can extend coverage until October 10, 2028. After that, the fixes stop. Small and medium-sized businesses (SMBs) are particularly exposed. Lansweeper reckons that 21.4 percent of SMB machines still run Windows 10, with cost usually being the constraint that keeps the legacy operating system running. The exposure is greater in some sectors, with 23 percent of healthcare and pharmaceutical systems sticking with Windows 10, while consumer and retail devices hover at 22.7 percent. According to Lansweeper's data, "a Windows 10 device carries an average of 1,903 active CVEs against 652 on Windows 11. That's a 2.9x gap." Esben Dochy, principal technical evangelist at the company, told The Register that "the Windows 10 average also includes devices that have ESU patches applied." Part of the problem, according to Lansweeper, is "patch diffing," in which Windows 11 fixes can be reverse-engineered to find flaws in Windows 10. "The supported OS effectively hands attackers a map into the unsupported one," Lansweeper said. According to Lansweeper's figures, 14 percent of Windows 10 assets have ESU patches applied. "I think a meaningful share of the remaining Windows 10 estate isn't being actively unpatched by neglect," Dochy said. "It's being held in place by vendor dependency, certification gaps, cost, or accepted risk. Certified equipment is a good example: many medical devices or industrial systems have their OS tied directly to vendor certification, and in some cases a Windows 11-certified version of that device or software doesn't exist yet. The same applies in retail, where devices are often vendor-locked to specific OS versions for compliance or warranty reasons. "For a lot of this hardware, the vendor is contractually responsible for maintaining the device, including any OS changes, so simply enrolling in ESU as a customer may not resolve the underlying problem. The real fix depends on the vendor's own certification timeline for Windows 11, and the cost that comes with the eventual upgrade or replacement. There are also devices sitting in air-gapped or isolated environments, where the risk is knowingly accepted for now rather than actively managed, so ESU enrollment simply isn't a priority." It's not a great situation, and the apparent stalling of Windows 11 adoption doesn't help. Looking at other market share measures such as Statcounter, there was little change in the share of Windows 10 and its successor over the last few months after a surge following the end of support. As Lansweeper noted: "The easy migrations are done. What's left is the hard core: devices that haven't moved because they can't or won't." Compounding the issue is the rising cost of new PC hardware, a trend unlikely to improve in the near term. According to Microsoft, "the ESU program helps reduce the risk of malware and cybersecurity attacks by providing access to critical and important security updates." Microsoft has extended the program for consumer devices, perhaps in recognition that there are an awful lot of Windows 10 machines still out there. Lansweeper's figures also underline the need for administrators to know which Windows 10 devices remain in their estates and whether each is fully patched. While many devices will have some level of protection, others will not, and over time, the proportion of vulnerable Windows 10 devices will grow, particularly where a move to Windows 11 is not an option. ®

❌