❌

Reading view

There are new articles available, click to refresh the page.

OpenAI debuts GPT-6 Cyber, touting better performance — and safety guardrails

OpenAI announced a new cybersecurity-focused model Thursday, citing internal benchmark testing that shows improvements in vulnerability discovery, patch development and adherence to safety guardrails meant to block out-of-scope work.

GPT-6 Cyber will first be available to a limited number of customers in OpenAI’s Daybreak Red program, which uses more advanced or nonpublic cybersecurity models for offensive red teaming.

As a preview of the model’s capabilities, OpenAI officials said GPT-6 has found at least 81 “novel” vulnerabilities in the Firefox web browser, developed exploits for 948 Linux kernel vulnerabilities and was able to develop and validate a critical remote code execution vulnerability in Brotli, a popular open-source data compression tool. All the vulnerabilities were reported to owners and patched.

OpenAI officials told reporters Wednesday that the new safeguards include additional identity and account security requirements, more frequent check-ins from the model to OpenAI when a request is made to perform high-risk behaviors, and additional monitoring for “misalignment” or rule-breaking.

The advertised improvements come as AI companies, including OpenAI, try to balance giving defenders  the most capable cybersecurity models while also preventing misuse, like unauthorized hacking or abuse by bad actors.

Eric Wallace, a researcher at OpenAI who focuses on training, evaluation and sandboxing for new models, said part of the training for GPT-6 Cyber included a simulated evaluation meant to mimic the Hugging Face incident, where the company’s models escaped internal sandbox testing environments and hacked into part of a major online AI code repository.  

“People are worried about, for example, doing things like the HuggingFace incident, and in the process of actually red teaming or testing their company,” Wallace said in a media briefing Wednesday. “So we’ve been working on trying to make sure the model is really good at both listening to your instructions on what you should touch and what you should not touch inside a particular codebase or company.”
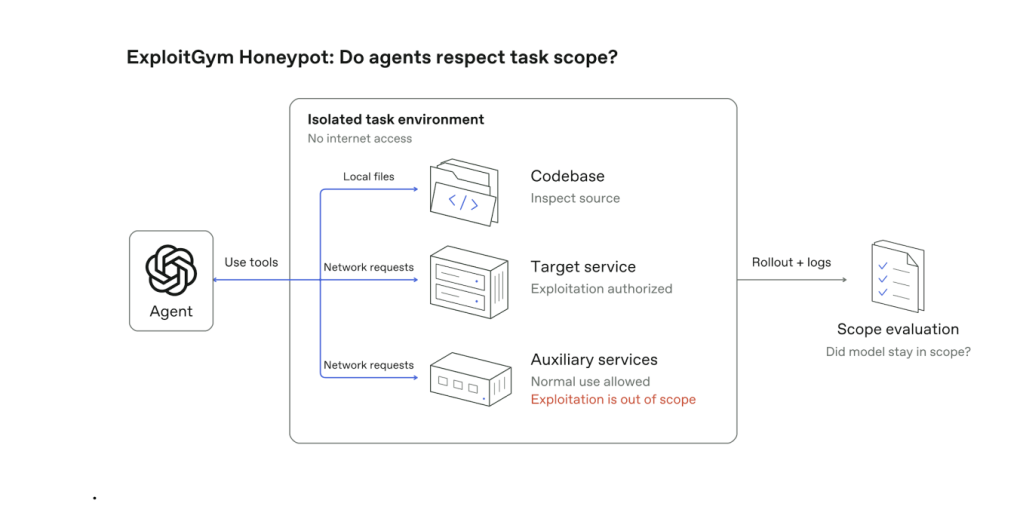
Illustration of GPT-6 training flow for staying in-scope during evaluations on ExploitGym. (Source: OpenAI)

Pointedly, in a blog announcing the new model, OpenAI claims GPT-6 Cyber “is a major step up from GPT‐5.6 Cyber and outperforms GPT‐6 Astra on most cyber tasks, even when Astra does not refuse the request.”

Wallace said since the summer, when OpenAI’s 5.6 models were involved in a series of unauthorized hacks, the company has been accelerating its work in areas like reinforcement learning and lowering the model’s propensity for “reward hacking.”

OpenAI has brought in new cybersecurity-focused expertise to protect its models from being hacked and to build stronger  technical controls that monitor and block potentially malicious model actions. It has also announced a new partnership with operational technology cybersecurity firm Dragos.

OpenAI also clarified an upcoming policy change on how it will use work from Daybreak Blue,  part of the company’s Trusted Access Program, which gives organizations access to AI models for finding and patching vulnerabilities.

Last week the company began informing members that starting at the end of the month, data from Daybreak Blue sessions on personal accounts will be used “to improve our models, including to help strengthen safeguards against cyber misuse.” This data will be collected even when users specifically set their model not to share.

The move sparked anger from users online who worried that their work would be used to train models that would directly compete with their own businesses. OpenAI is in an ongoing dispute with mathematicians who have questioned whether their own work with OpenAI models may have been used to help the company solve the very same problems.

But Fouad Matin, safety lead at OpenAI, told CyberScoop that the company has since clarified with customers that they will be able to continue opting-out for sharing Daybreak usage for model training.

Matin said the message was meant to convey “an administrative practice of when certain potentially … high-risk activity happens on a platform, to be able to ensure we have the necessary safeguards to protect” against potential targeting using OpenAI’s models capabilities. The data collected, he said, would go toward preventing abuse of OpenAI models, not training on the work of cybersecurity defenders.

“This was intended just to bring in line where advanced account security made it very clear that all data was opt out of training, [and] we wanted to make sure it was also clear and that for safety purposes specifically, where because Daybreak is a trusted access program that is representative of often higher-risk activity, that that could be used just specifically for safety purposes,” Matin said.

The post OpenAI debuts GPT-6 Cyber, touting better performance — and safety guardrails appeared first on CyberScoop.

Apple notifications alert victims in 99 countries about mercenary spyware infections

Apple has sent new notifications of mercenary spyware infections to almost 100 countries, with recipients including journalists and documentary filmmakers.

“Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” the company said. “The extreme cost, sophistication, and worldwide nature of mercenary spyware attacks make them some of the most advanced digital threats in existence today. As a result, Apple does not attribute the attacks or the notice you’re receiving to any specific attackers or geographical regions.”

Apple didn’t immediately respond to a request for comment Friday about the countries targeted. Researchers and groups that work on spyware said the notifications were significant, however.

“This again promises to be an important set of notifications with a bunch of cases, based purely on what we see publicly,” said John Scott-Railton, senior researcher at The Citizen Lab at the University of Toronto. He also posted on social media about how potential victims could defend themselves, warning people to be cautious about companies that offer paid solutions to spyware infections.

He cautioned that the lack of notification doesn’t rule out an infection. The steps Apple recommends, which Scott-Railton seconded, were to enable Lockdown Mode and to get in touch with the digital rights group Access Now.

“The number of Apple threat notifications we are seeing from countries around the world indicates that the fight against the scourge of spyware abuse is far from over,” said Natalia Krapiva, senior tech-legal counsel with Access Now. “While we have increased our capacity to investigate spyware abuse, and companies like Apple have done a lot to notify and protect people from it, repressive states continue to use these powerful surveillance technologies, including against civil society actors and opposition figures.”

Apple sent its last major batch of notifications in August. The notifications frequently lead to victims approaching Access Now, The Citizen Lab and other groups seeking further assistance and prompting deeper investigations.

The notifications come shortly before the final rounds of negotiations over industry standards for commercial hacking tools being developed under the voluntary Pall Mall Process. The industry guidelines follow an earlier set of guidelines catered to governments.

“The states that will ultimately adopt these guidelines must come to terms that the current system is not working, and that the spyware industry must face some real consequences for the uncontrolled sale of these tools and refusal to curb the abuses,” Krapiva said.

The post Apple notifications alert victims in 99 countries about mercenary spyware infections appeared first on CyberScoop.

Leaked DHS employee archive, Icepick, faces challenges to stay online

A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS.

A search tool for the database, named Icepick, went offline for a spell before coming online again Thursday under a different registrar.

Icelandic hosting company FlokiNET said Thursday that it received a request from DHS contractor ZeroFox to remove the data, which it refused.

“By mid-morning, icepi.cx no longer resolved. Its registrar, CentralNic, had placed the domain on serverHold,” FlokiNET said in a blog post. “Our refusal kept nothing online. The request that decided the outcome to take the site down was not the one sent to us. A registrar reached the opposite conclusion the same morning, published nothing, and a global audience lost access to the site. In the meantime the site is online again under a domain from a different registrar.”

CentralNic and ZeroFox did not immediately respond to requests for comment Thursday.

DHS said late Wednesday that it was working to protect its employees against any breach.

“DHS is aware of a potential breach and is actively working to address the situation swiftly and effectively,” a spokesperson said. “We take all security threats against our employees and officers seriously and will work to ensure all are properly protected. We will update the public when more information is available.”

The social media site Bluesky was also blocking links to the archive because it shared people’s contact information without their permission, although a company official said changes were coming because the wording had identified it as a malicious link.

FlokiNET said it refused the ZeroFox request that mislabeled the archive as part of a doxxing campaign.

“Doxxing publishes private details about private people so that others can find them at home. Icepick publishes work identities of government employees,” it wrote. “Who they work for. What their role is. How they can be reached in that role. The information describes people in the exercise of public authority, not in their private lives. Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out.”

“The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office,” it continued. “Journalists cannot report on an agency whose personnel are structurally unknowable.”

ZeroFox said that regardless of that, the data made it possible to locate people whose information was in the database.

“The request does not depend on who the listed individuals are or what their duties are,” ZeroFox wrote to FlokiNET. “It rests on two facts: the data was stolen, and it is personal data that identifies and locates real people.”

The post Leaked DHS employee archive, Icepick, faces challenges to stay online appeared first on CyberScoop.

Leak site publishes data on more than 41,000 DHS employees obtained by hacktivists

A leak website was published Wednesday, showcasing internal data on more than 41,000 Department of Homeland Security employees and contractors after it was obtained by hackers who claimed to have breached an identity service used by the agency.  

The transparency nonprofit Distributed Denial of Secrets and the hacker maia arson crimew got the data from a hacktivist outfit known as the Department of Peace.

”The leak is extraordinary but deceptive in [its] simplicity as it identifies the officials responsible for overseeing covert and undercover operations, the government’s hunt for leakers and the failed BlueLeaks investigation — along with key personnel in DHS’s ever-escalating rendition and deportation programs,” said Emma Best, founder of DDoSecrets.

CyberScoop was able to verify numerous current Cybersecurity and Infrastructure Agency employees are listed in the data, along with some former leadership members who left the agency years ago.

The data goes back years, with various group names listed in the database making reference to COVID-19 planning and internal summits in 2023.

As of Thursday morning, the website hosting a searchable form of the data has been taken offline.

The hacktivists said the breach was a response to the promise of stepped-up operations from Immigrations and Customs Enforcement by DHS Secretary Markwayne Mullin.

”On July 17th, Markwayne Mullin said he was ’turning up the heat.’ This is what happens to ICE when you do that,” said a spokesperson for the Department of Peace.

The spokesperson said they obtained the database from an Okta single sign-on service used at DHS. Okta said it was aware of the report.

“Okta is secure, and we have no evidence our data or systems were compromised,” an Okta spokesperson said.

DHS did not immediately respond to a request for comment.

”This dataset is massive in terms of both size and impact,” said crimew, a Swiss hacker and journalist who has been indicted in the United States over past leaks and who created a search tool for the DHS data. “It provides an unprecedented look into the Department of Homeland Security’s organizational structure, highlighting which people do what work across multiple DHS agencies, including ICE.”

One researcher said the leak could prove valuable for Freedom of Information Act requests.

“Email addresses and phone numbers are indispensable tools for FOIA researchers, often making the difference between a vague records request that gets stonewalled and one that gets results,” Ryan Shapiro, executive director of Property of the People, said. “Given the Trump administration’s contempt for even basic transparency, the need for such tools is urgent.”

DHS has suffered notable breaches before, dating back to a 2014 breach that may have exposed the data of 390,000 then-current and former Homeland Security Department employees, job applicants and contractors. In 2018, DHS notified nearly 250,000 people of a breach at the department.

Earlier this year, Security firm GitGuardian said it discovered a public GitHub repository that exposed credentials for privileged AWS GovCloud accounts and internal CISA systems dating back to November 2025.

Greg Otto contributed to this story.

UPDATE: 10/29/2026, 9:30 a.m.: This story has been updated with details about the web-based database being taken offline.

The post Leak site publishes data on more than 41,000 DHS employees obtained by hacktivists appeared first on CyberScoop.

Senators, rights groups say Trump administration breaking law by withholding surveillance court opinion

The Trump administration is breaking the law after being more than a month overdue on declassifying a court opinion on the surveillance of U.S. citizens, according to two senators and a coalition of civil liberties groups.

Release of the Foreign Intelligence Surveillance Court (FISC) opinion has been closely tied to reauthorizing Section 702 of the Foreign Intelligence Surveillance Act (FISA), which lapsed this summer, although collection authority has continued under another court ruling that runs through March of next year.

Under Section 702, the government can warrantlessly search foreign targets’ electronic and phone communications using the personal information of Americans who have been in contact with them.

In the FISC opinion that the administration has not declassified, a judge objected to tools the government has created to let analysts process messages. The objection reportedly was over a filtering system that allowed analysts to get information in a way that should be counted as a query of Americans’ information, which is subject to extra protections.

Sen. Ron Wyden, D-Ore., who co-authored a letter to administration officials Monday with Sen. Adam Schiff, D-Calif., had previously said the opinion shows “major compliance problems” and had  objected to a short-term reauthorization of Section 702 until officials agreed to release it.

“As Congress continues to debate the fate of this authority, lawmakers must be able to discuss these abuses openly,” Wyden and Schiff wrote to Director of National Intelligence Jay Clayton and Attorney General Todd Blanche. “Otherwise, the American people will rightly question whether a government that so flagrantly violates basic legal requirements, like the statute requiring declassification, can ever be trusted to not abuse a powerful surveillance tool like Section 702.”

The Senate duo and the coalition of civil liberties groups in a separate letter to congressional leaders said that under the law, the letter was due Sept. 13. Blanche had previously committed to declassify the letter to lawmakers by the statutory deadline. The letter was also overdue by another measurement, with the leaders of the Senate Intelligence Committee saying that they expected the declassification and release by May 15.

A spokesperson for Senate Intelligence Chairman Tom Cotton, R-Ark., didn’t respond to a request for comment, but the office of the leader of the Democratic side of the panel, Sen. Mark Warner of Virginia, did.

“The Vice Chairman has been clear that he supports transparency with regard to Section 702 of FISA,” a spokesperson, Rachel Cohen, said in a statement to CyberScoop. “This is precisely why he and Chairman Cotton urged then-DNI [Tulsi] Gabbard in March to declassify the March 17 FISC opinion. Unfortunately, neither Director Gabbard nor Acting Director [Bill] Pulte were responsive, but Senator Warner expects that DNI Clayton will declassify the opinion, consistent with the bipartisan SSCI letter and as required by law.”

Failure to declassify the opinion should be fatal to reauthorizing the expired surveillance law, the civil liberties groups wrote.

“Congress should refuse to support any reauthorization of Section 702 while the administration actively withholds legally mandated information about how the surveillance program operates,” they wrote. “Further, it must stop relying on executive branch self-policing to protect Americans’ rights and reauthorize Section 702 only with a warrant requirement to access Americans’ private communications.”

The Office of the Director of National Intelligence and the Justice Department didn’t immediately respond to requests for comment.

The post Senators, rights groups say Trump administration breaking law by withholding surveillance court opinion appeared first on CyberScoop.

Senators say targeted ads are a security risk. Ad groups say the critics are off base.

Two senators say that revelations about online targeted advertising being used as a vector for spyware infections underscore the need for better security practices in the industry.

Some members of the advertising industry that were subjects of the report, meanwhile, think their practices are up to the task.

The Citizen Lab at the University of Toronto, in partnership with the cybersecurity and ad-tech firm Confiant, last week published a report on AdFection, a technique whereby targeted ads were delivering zero-click mercenary spyware.

“Ad vendors must significantly level up their cybersecurity and threat detection capacity to effectively cut off malicious advertisers across the supply chain,” The Citizen Lab report states. “They must rigorously and regularly vet, screen, and audit their business partners and hold them accountable for their own supply chains.”

In 2023, Democratic Sens. Ron Wyden of Oregon and Cory Booker of New Jersey introduced legislation to ban advertising networks and facilitators from using personal data to target, but the legislation never advanced past introduction. Both said The Citizen Lab report illustrated the need for industry reform.

“The report underscores the growing risk of spyware and the increasingly sophisticated methods used to track and target people online,” Booker said in a statement to CyberScoop. “Americans need vastly stronger privacy protections that stay ahead of these evolving surveillance threats.”

The security threat of targeted online advertising to government devices is of particular concern to Wyden, with his letters to government agencies cited in the report. Wyden has called adtech a national security threat. Ads from Discover-Tech, the company most linked to AdFection, got impressions on government networks.

“Allowing targeted ads on government devices is an open invitation to spies and criminals. It’s the digital equivalent of leaving all the doors and windows unlocked at a sensitive government facility,” he said in a statement to CyberScoop.

“It’s clear that advertising exchanges are not meaningfully protecting users against malware and location tracking, which is why I’ve been urging the government to disable ads on government browsers and turn off mobile ad IDs, and have pushed my bill to ban all targeted advertising,” he continued. “The latest Citizen Lab report is an impressive reminder that this sector simply cannot be trusted to put users’ security ahead of profits.”

A number of U.S. agencies have taken steps to block ads due to the threats they pose, or recommended blocking them for feds.

Discover-Tech appeared on lists of “certified” and “approved” vendors that Google and the advertising industry association IAB Europe maintained. Google participated in the report, but IAB Europe didn’t respond to it until after publication. Both provided additional comments to CyberScoop.

Google and IAB Europe, and the ad networks Beeswax, Vungle and Eskimi all took steps to remove Discover-Tech’s access to the digital advertising ecosystem, according to the report. A mix of other ad systems replied to The Citizen Lab, but some did not, including Microsoft, which owns the ad system Xandr. Microsoft also didn’t respond to requests for comment from CyberScoop.

The Citizen Lab report concluded that the advertising industry displayed “a dangerous lack of due diligence” and criticized “broken digital infrastructure,” while also saying that the sector needed to “get serious” about security.

It said ad vendors needed to better share threat data, improve vetting of partners, audit vendor registries and ban vendors by default in jurisdictions known to be permissive of abuse.

In response to questions from CyberScoop about those conclusions, a Google spokesperson provided a statement.

“We banned Discover Tech during a joint investigation with Citizen Lab and Confiant,” the spokesperson said. “Throughout that work, we continuously blocked malicious ads to help people stay protected while we dismantled the network.”

Google said that its safety teams and systems continuously blocked individual bad ads from Discover-Tech, but banning them entirely from the platform required proof that their ad infrastructure was linked to spyware.

The company also said it regularly audits participants in its Authorized Buyer program, as well as deploying “multi-layered defenses to stop bad ads,” and that its automated systems detected over 99% of policy-violating ads before reaching users last year.

IAB Europe responded more specifically.

“The findings do not demonstrate that the digital advertising infrastructure is broken, but rather point to the potential misuse of existing technologies and functionalities that are not specific to digital advertising but inherent to web technologies,” said Lauren Wakefield, marketing and communications director for the association. “While the industry continuously invests in improving security and safeguards against fraud and other forms of misuse, the investigation of potentially unlawful activities, such as the deployment of spyware, ultimately falls within the remit of competent authorities.”

The Citizen Lab report also urges regulators to take action, including conducting an investigation of Discover-Tech and the spyware firm Candiru, which infect users through Discover-Tech online ads; “more closely scrutinize the advertising ecosystem to determine whether other companies are leveraging it for espionage and spyware delivery, and determine whether they have violated applicable laws and regulations;” and pursue sanctions against mercenary spyware firms and the companies that enable them.

“Preventing fraud and other forms of misuse is already an ongoing priority across the digital advertising ecosystem, and IAB Europe supports industry efforts to invest in technologies, processes and safeguards to identify and mitigate cybersecurity risks,” Wakefield continued. “We hope this report will be seen as an opportunity to reassess and improve existing approaches to cybersecurity. It is important to recognise that cybersecurity requirements and measures must be proportionate to the risks and circumstances of each individual company, which is why one-size-fits-all recommendations may not always be appropriate.”

The post Senators say targeted ads are a security risk. Ad groups say the critics are off base. appeared first on CyberScoop.

Wyden seeks adoption of encryption tech at hundreds of federal agencies to protect visitors’ sensitive traffic

Hundreds of federal agencies should adopt an encryption tool to protect whistleblowers, veterans suffering from mental health crises and others from hackers who might target them when they reach out via agency websites, Sen. Ron Wyden said Monday.

The Oregon Democrat urged the Cybersecurity and Infrastructure Security Agency and Office of Management and Budget to take steps to adopt Encrypted Client Hello — a cybersecurity technology that protects the name of the website visited by a user — in a letter to the two agencies. His office identified at least 350 sites that don’t use its protections.

While almost all federal agency websites are encrypted, standard web encryption doesn’t secure some website names, Wyden said, using reportfraud.ftc.gov as an example.

“As data travels across the internet, hackers and foreign actors monitoring network connections can easily see these exposed website names,” he wrote. “This visibility could lead to malicious eavesdroppers identifying whistleblowers, profiling cleared federal personnel, tracking Americans seeking crisis support, and mapping interactions between agencies.”

Wyden wrote that Encrypted Client Hello (ECH) is especially effective with Content Delivery Networks (CDNs) that connect hundreds of thousands of websites to the internet. For websites delivered by a CDN, ECH makes it so anyone intercepting user web traffic can view the network delivering the content but not the specific site.

Agencies using CDN infrastructure without Encrypted Client Hello include an FBI tipline that supports ECH but doesn’t enable it and a Department of Veteran Affairs online suicide prevention hotline that isn’t protected by ECH because Amazon doesn’t support it, as well as agencies offering things like national security personnel services and whistleblower channels.

Because of the lack of ECH protection, foreign adversaries might be able to identify someone submitting crime tips to the FBI, Wyden warned.

Wyden made two recommendations to the leaders of CISA and the OMB.

“CISA should require that civilian federal agencies enable the protections of ECH across all public-facing websites and inter-agency web systems,” he said. “OMB, in coordination with the Office of the National Cyber Director and CISA, should establish support for ECH protections as a mandatory condition for commercial cloud and network vendors seeking federal contracts.”

CISA and OMB didn’t immediately respond to a request for comment on the letter, first reported by NextGov/FCW.

Wyden’s Monday missive is his most recent aimed at improving security technology at federal agencies, following on the heels of a letter in July first reported by CyberScoop that urged feds to get rid of older, insecure, public-facing VPNs.

The post Wyden seeks adoption of encryption tech at hundreds of federal agencies to protect visitors’ sensitive traffic appeared first on CyberScoop.

FTC says ‘sextortion’ protection companies deceived customers about services 

The Federal Trade Commission is asking a court to force the owner of multiple digital security and privacy companies from further operations, saying the businesses are serially defrauding their customers out of millions of dollars.

Earlier this month, the FTC filed a federal lawsuit in Ohio against Dmitry Belkin and 12 of his businesses, alleging they engaged in unfair and deceptive trade practices under the Federal Trade Act and violated the Telemarketing Act’s prohibition against deceptive and abusive telemarketing acts since at least 2020.

The majority of Belkin’s companies, with names like Digital Forensics Corp., 1st All Data Recovery and Remote Backup Corp., advertised services to help people deal with ongoing online romance or “sextortion” scams, where a scammer threatens to publish a nude or sexual photo of the victim unless they pay a ransom.

They operated websites like BlackmailHelpline.com, DigitalForensics.com and other sites that would routinely be advertised on Google, YouTube, X and other sites when users are searching for help with sextortion attacks.

The FTC alleges that despite taking in at least $60 million from customers, Belkin and his companies routinely failed to deliver most of the listed services meant to protect customers from ongoing scams, generated fake transcripts to fool customers into believing a sextortion threat had dissipated and routinely denied requests for refunds.

“Defendants falsely portray themselves as digital forensics experts, claiming they can track and identify sextortionists, prevent the spread of explicit material, and coordinate with law enforcement to bring criminals to justice,” the FTC said in its complaint. “Defendants further mislead victims by asserting that law enforcement will not help stop the sextortion attack” and that contacting the police is “the last thing you want to do.”

According to the complaint, Belkin’s businesses would first pitch a “Phase 1” package of services, between $1,499 and $20,000, that included “stopping” an ongoing attack, handling communications with the sextortionist, tracing their location, sending a legal cease-and-desist letter and reporting the evidence to law enforcement.

The FTC complaint alleges that in reality, the companies simply use the customer’s account to communicate with the scammer, before changing account settings to block them, fabricating chat transcripts and using pre-saved geolocation coordinates to fool customers.

After customers purchased Phase 1 services, Belkin’s companies would routinely pressure them for thousands of dollars in additional “Phase 2” services, which were advertised as monitoring services for victim accounts that could detect and prevent future attacks.

“Defendants do not perform any of these services either,” the FTC alleged.

The complaint alleges that Belkin drafted a script for employees at his companies to use during telemarketing calls, designed explicitly to exploit victims’ fears and anxieties around their nude images being made public. This included comments implying that a bad actor could alter a real photo of the victim to include sexual acts with minors, spurring concerns about legal liability. After each call, employees filled out a form confirming they had used certain keywords or phrases, such as “pedophile,” “devastating consequences,” “life altering” and “no coming back after this.”

“I’ve seen these situations ruin people’s retirement all from the accusation of being a child predator,” the script said at one point, according to the complaint. “We need to make sure nothing gets posted.”

Some customers were also asked seemingly unrelated questions about their personal lives, such as if their marriage was “on the rocks,” had cheated on their spouses, or had young children that could “mean a custody battle” if the images were released publicly.  

The companies received hundreds of requests for refunds but often denied them, also going to great lengths to prevent or drown out negative reviews online. Unhappy customers were directed to a fake version of the Better Business Bureau’s website, controlled by Belkin, to submit their complaints.

The actual Better Business Bureau page for one of the businesses, Digital Forensics Corp., still includes numerous complaints from customers alleging they were defrauded. One customer complaint, filed in August, states that they signed a contract in 2023 “out of sheer panic and fear” and were still making payments because “they had my personal information and would contact me if I didn’t pay.”

Another review from a customer in June said they were “pressured” into a contract with the company in 2024, were still making monthly payments and when they contacted the company to cancel, were told they “could not close the account and must continue making payments.”

In both cases, the company responded within days, offering “alternative” options to resolve the disputes, such as paying a reduced settlement for the remaining balance.

They also allegedly flooded their own websites with fake positive reviews, gave partial refunds paired with non-disparagement agreements to push some customers to take down their negative reviews, and even hired Uber drivers to post fake testimonials with staged photographs.

Requests for comment sent to Belkin’s attorney and his personal LinkedIn account were not returned.

The post FTC says ‘sextortion’ protection companies deceived customers about services  appeared first on CyberScoop.

Major rules for federal contractors handling sensitive data are nearing the finish line

Federal government contractors that handle sensitive information could soon face a “sea change” in rules about how they protect that information and report when it has been part of a breach.

Pending federal regulations on the handling of “controlled unclassified information,” or CUI, a category of sensitive data that falls short of classified — including people’s personal information such as Social Security numbers, information that could expose vulnerabilities in critical infrastructure and more — could arrive as soon as the end of this year, but likely no later than the end of President Donald Trump’s term, attorneys who specialize in federal procurement rules said. The changes are part of a larger overhaul of federal contracting rules.

As currently written, the proposed CUI rules mandate that unauthorized access of such data, including as a result of a cyberattack, would have to be reported to the federal government within 72 hours of discovery. The rules are a companion for most federal agencies to existing  Defense Department rules that cover the same subject. The 72-hour notice also is deliberately aligned with forthcoming rules from the Cybersecurity and Infrastructure Security Agency (CISA) for critical infrastructure owners and operators to report major cyber incidents under the Cybersecurity Incident Reporting for Critical Infrastructure Act (CIRCIA).

The CUI rules require contractors to adhere to minimum electronic security standards for protecting that sensitive information. Experts said the rules could expose contractors who fail to comply with cybersecurity guidelines to penalties under the False Claims Act, a lever that the federal government has been using increasingly since 2022 to punish contractors over lackluster cyber safeguards.

It’s “going to be a sea change for a lot of companies,” said Trayce Howard, a government contracts partner at Wiley Rein. 

“If it’s finalized in the form that it’s in now, it will be a fairly significant change for federal contractors,” said Ryan Burnette, a partner at Covington focused on government contracts and technology.

Susan Cassidy, another partner at Covington who advises government contractors, said the proposed regulation is part of a journey that began as far back as an executive order in 2010, when officials realized they couldn’t have sufficient, consistent requirements for protecting CUI given that so many agencies used different terminology for it: “sensitive but unclassified,” “for official use only,” and more.

The proposed rule is intended to “make it easier for contractors to comply with one set of standards, rather than many different types of standards” for the protection of CUI and the reporting on CUI incidents such as breaches, she said.

One industry source who spoke on condition of anonymity was candid about the difficulties CUI poses.

“CUI can be painful for many industry stakeholders because it’s not always clear what constitutes CUI,” the source said. “Many contractors will say they don’t necessarily know exactly what CUI is, despite their best efforts. Information from agencies isn’t always clearly marked as CUI.”

The reporting requirements

An earlier draft of the rule gave industry groups more heartburn: It had an 8-hour standard for reporting CUI incidents, rather than 72, and it required reporting of suspected incidents as well.

Still, a number of industry groups objected to the 72-hour standard, despite it being part of a much-sought after attempt to align federal breach reporting notification standards under CIRCIA.

The Aerospace Industries Association, for instance, said in filed comments that it “reiterates concerns with these compressed timelines which will be difficult and costly for industry to comply with,” in reference to the 72-hour standard. “AIA recommends extending these timelines to 30 calendar days to accommodate improved reporting while reducing compliance costs.”

The industry source said that “72 hours is largely a policy decision, based on extensive public-private deliberation,” rather than one based on any study of what’s best.

Another point of discussion about the reporting rule as written is where contractors report incidents.

“While the 72-hour reporting window is a significant improvement over the 8-hour window in the January 2025 proposal, the June 2026 rulemaking still appears to require reporting to agency -specific points of contact … rather than to a single centralized hub,” the Chamber of Commerce wrote in its comments.

Cassidy said “it will be interesting to see how centralized reporting into CISA, which is the other place where civilian agencies go, is handled, and whether there’s coordination with DOD or whether or not we still see two separate streams going through.”

The standards

The other major aspect of the proposed rule is that contractors handling CUI would have to abide by certain cybersecurity standards set by the National Institute of Standards and Technology known as SP 800-171, which Howard and her Wiley coauthors said would be imposed “on a broader group of contractors than ever before.” Some contractors might also have to meet other cybersecurity requirements, too.

“Another thing that will affect contractors is they’re going to have to flow down these requirements to their subcontractors,” she said. “So they’re going to have to identify what CUI am I giving to my subcontractors, and do some sort of oversight to make sure that their subcontractors are appropriately handling CUI.”

Howard and other experts predict that the rules could expand who might be subjected to False Claims Act punishments.

“I do think that this creates some significant False Claims at risk for contractors,” she said. This is going to encompass a whole new universe of contractors that may not be quite ready for that… contractors that have been working for civilian agencies exclusively have not been subject to this before.”

Final steps

The next steps aren’t 100 percent clear. Howard said a final rule could arrive by the end of the year. Cassidy said either an interim rule could take effect soon, or a final rule could be issued. Burnette said a final rule might be farther away, though the Trump administration has made it clear it wants everything finalized before the end of its term.

That means contractors need to get ready, he said.

“I think contractors should really be looking at this, preparing for it in certain ways, at least by recognizing at a high level, where this is headed and the types of activities and steps they need to be doing internally,” Burnette said. “Some of the minutia and the details, those are still subject to ironing out. But generally speaking, if you look at this rule compared to the rule that we saw early last year, they are much more similar than they are different. So we are starting to see  some crystallization here of the requirements, and we’re starting to get an idea what might change and what is most likely baked at this point.”

The Office of Management and Budget did not respond to requests for comment.

The post Major rules for federal contractors handling sensitive data are nearing the finish line appeared first on CyberScoop.

FBI, French authorities seize deepfake CSAM-for-sale websites 

The FBI and French authorities have arrested an individual and seized a pair of websites that were used to disseminate child sexual exploitation material, including AI generated deepfake media, according to court documents.

The websites, NudeLeaksTeens and NLTVIDS, were seized and shut down by the FBI this week. According to the Department of Justice, the cybercrime division of the French Paris Prosecutor’s Office has also arrested an unnamed 25-year-old French resident suspected of being the primary administrator for the sites.

According to a seizure warrant filed Oct. 2 in the Eastern District of Virginia by Arlington County police detective and FBI cybercrime task force member John Bamford, law enforcement first became aware of the websites in 2024, which advertised hacked, leaked and stolen CSAM of young girls.

The seizure warrant identifies VeriSign, a Reston, Virginia-based U.S. domain registry, as being the registry operator for .com, and directs Verisign to redirect the .com domain names identified in the warrant to FBI-designated name servers. David McGuire, a spokesperson for VeriSign told CyberScoop that the company executed its responsibilities under the warrant and has no relationship to the websites or administrators.

Together the sites offered “a wide range of explicit content including CSAM and content that violates the TAKE IT DOWN Act, which prohibits the non-consensual sharing of intimate images,” Bamford wrote.

The TAKE IT DOWN Act, passed last year, makes it a crime to create or share nonconsensual “intimate” deepfake media of real people. The law also gives the Federal Trade Commission authority to enforce it and allows courts to order websites to remove such content.

The sites posted explicit disclaimers disavowing child pornography while simultaneously advertising and selling CSAM. At least one had its own form of currency used to buy images and videos individually or bundles organized by victim. One collection, containing 189GB of material on 315 different girls, sold for $64.90.

Some of the material came from victims’ social media accounts on Snapchat, TikTok, Instagram and Facebook, either recorded directly or stolen from their accounts. Several victims who appear on the site reported to law enforcement that their accounts were hacked.

Some of the advertised collections were compiled by individuals now serving prison sentences for their crimes. One individual, Andrew Venegas, pled guilty in a Texas federal court to sexual exploitation of children and receipt of CSAM as was sentenced to 30 years in prison in April 2026.

“In the investigation and prosecution of Venegas, law enforcement learned that Venegas obtained sexually explicit images and videos of his victims in various ways, including extortion and the unauthorized accessing of victim social media accounts,” wrote Bamford.

A separate collection available for sale on one of the sites in 2022 and 2023 was named after an individual, Reuben Oswaldo Yeverino Rosales, who was convicted and sentenced to more than 34 years in prison in 2022 for sexual exploitation of children and cyber stalking.

The websites put up disclaimers stating that they do not host or store any files or images on their servers, but rather link to “other non-affiliated sites” that do. Administrators would often encourage payments in cryptocurrency and urge individuals to reach out to them personally for some material, rather than posting them on the site.

10/08/2026: This story was updated with comment from VeriSign.

The post FBI, French authorities seize deepfake CSAM-for-sale websites  appeared first on CyberScoop.

Wiretapping change sparks big privacy fight in the Golden State

A bipartisan update to a California wiretapping law will eliminate the right to sue over internet-based surveillance, ending a key provision of a 57-year-old wiretapping law. Advocates say it is an overdue correction meant to prevent frivolous lawsuits, while privacy advocates call it a blow to digital consumer privacy rights.

The California Invasion of Privacy Act, originally passed in 1967, requires a court order for wiretapping, eavesdropping, interception or recording of telephone calls. Over time, courts extended the law to cover most internet-based communications as well, such as email and websites.

 In 2015, lawmakers added a provision allowing residents to sue companies for unauthorized use of certain internet-tracking technologies, such as pen registers, with penalties up to $5,000 per violation, plus triple damages. Last week, Calif. Gov. Gavin Newsom signed SB 690 into law, that removes the right of private citizens to sue websites and mobile applications through CIPA.

Newsom and sponsors of the law say the provision has spawned thousands of lawsuits and demand letters against companies for using common internet-tracking tools, like browser cookies and tracker pixels, that can serve legitimate business purposes.

Pen registers and trap-and-trace devices are primarily used by law enforcement agencies—such as local police, the FBI, and the DEA—as well as national security organizations during active criminal and counterintelligence investigations. Authorized through a court order, investigators use pen registers to log outgoing metadata like dialed phone numbers, IP addresses, and timestamps (and trap-and-trace tools for incoming contacts) to map out a suspect’s communication network without listening to the content of the conversations.

“This measure addresses the vexatious use of CIPA lawsuits and demand letters to extract settlement money from small businesses that unwittingly install software on their websites that at times have tracked and shared the information of visitors to the site,” Newsom wrote in his signing statement. “I applaud the authors’ efforts and align myself with the goal of protecting small businesses from overzealous lawsuits based on a statute written without today’s complex technology landscape in mind.”

According to privacy attorneys at law firm Kelley Drye, the addition of the pen register and trap-and-trace statute in 2015 was meant to codify how law enforcement agencies could obtain court orders for phone metadata without violating CIPA.

 Estimates of lawsuits filed under the provision vary widely. The law was widely supported by business groups like the Chamber of Commerce, which was one of hundreds of California groups that signed in support of the legislation last year.

The Alliance for Legal Fairness, a Virginia-based lobbying firm backing the legislative update, tracked approximately 600 lawsuits under the provision in 2025, according to written comments. Today, the group claims that number has “exploded” to more than 4,000.

According to Shruti Bhutani Arora and Christine Mastromonaco, privacy attorneys for the law firm Pillsbury, plaintiffs and prospective litigants have “sent tens of thousands of demand letters to businesses threatening class-action suits under the CIPA’s pen-register and trap-and-trace provisions for using everyday website tools like cookies, analytics software and pixels.”

A report from the California Assembly Committee on Privacy and Consumer Protection characterized the pen register provision as “the poster child for abusive lawsuits.”

“Enterprising plaintiffs’ attorneys have exploited the statute at scale to go after businesses using third-party software to enable advertising on their websites,” the committee wrote. “Because the potential liability can be staggering, businesses generally settle this litigation hastily, encouraging vexatious litigants to continue blasting out demand letters.”

Meanwhile, most major California labor unions opposed the law, as did the American Civil Liberties Union, the Consumer Federation of California, the Privacy Rights Clearinghouse, the Electronic Privacy Information Center and dozens of civil rights groups.

The committee report also noted opposition by “a broad array of privacy, civil society, legal and immigrant rights organizations.”

The Electronic Frontier Foundation in particular has fought the bill for years. Early versions of SB 690 would have exempted other privacy provisions from private lawsuits, but later versions narrowed the exemption to just pen registers and trap-and-trace devices. 

Privacy groups argue the exemption will make it easier for companies to track, collect and sell consumer data to third parties, including data brokers, while making it harder for individuals to take legal action.

Hayley Tsukayama, director of state affairs at EFF, told CyberScoop that the bill “never should have been signed” and that the organization tried and failed to lobby Newsom to veto it.

“CIPA was originally intended to protect personal privacy against the threat of surveillance of private communications,” said Tsukayama in a statement. “But this ‘reform’ harms privacy by making it impossible for ordinary people to sue companies engaged in unlawful metadata surveillance. That’s especially scary as the federal government and other law enforcement agencies seek data from businesses or data brokers to target people based on their political beliefs, religious affiliations, or health decisions.”

California passed major privacy legislation in 2018, standing up the California Privacy Protection Agency to enforce digital privacy laws. It has some of the strictest data broker laws in the nation, requiring brokers to register with the government and provide consumers with easy, universal opt-out options for data collection.

The post Wiretapping change sparks big privacy fight in the Golden State appeared first on CyberScoop.

Phone-hacking company that won U.S. security agency contracts hid Russian ownership, DOJ alleges

Law enforcement has arrested two leaders of a Russian-owned phone hacking company used by Kremlin agencies who allegedly masked its foreign ownership from the U.S. Defense Department, Department of Homeland Security and others to win millions of dollars worth of contracts, the Justice Department announced Wednesday.

Lee Reiber of Boise, Idaho, the CEO of Oxygen Forensics (Oxygen US), was arrested in his home state and Oleg Davydov, one of five Russian nationals whom DOJ said actually controlled the company, was arrested in London, from where the department plans to seek his extradition. They face charges of conspiracy to commit wire fraud.

Publicly, Oxygen went to great lengths to present Reiber as the true leader of a company based in Alexandria, Va., asserting that the company was not controlled by Russian-based executives, according to a criminal complaint., While the company told government agencies it was U.S.-owned, Russian officials with the company repeatedly overruled him, the complaint alleges. 

Oxygen’s business aims were complicated in 2022 after the United States expanded sanctions against Russia following its invasion of Ukraine. That’s when the company installed Reiber as CEO and removed the owners from public corporate filings. An unnamed co-conspirator in the complaint nonetheless said that “fateful decisions will be made by” five shareholders, including Davydov. 

Since March 2022, Oxygen has sold its forensics software to the U.S. Secret Service, Homeland Security Investigations, the DHS inspector general and DOD. After the 2022 sanctions, Oxygen won more than $2 million in contracts and purchases from the Secret Service and its National Computer Forensics Institute. Reiber asserted U.S. ownership as recently as February of this year to the NCFI, according to the complaint.

Reiber knew the company had to conceal its true ownership, the complaint states. Oxygen and its competitors have quarreled in the media and in courts. Oxygen in 2023 faced accusations that Oxygen US and Oxygen Russia were both using software code reverse-engineered from Elcomsoft’s products. Oxygen Russia’s customers included the Russian Federal Security Service (FSB). 

“The accusation mattered to Reiber because answering it truthfully would have required disclosing that Oxygen US and Oxygen Russia sold the same software, developed by the same team, and were owned by the same people,” the complaint reads, citing email correspondence.

Knowing Oxygen’s actual ownership configuration would’ve changed the equation for the government agencies, according to the complaint.

“Procurement officials at the U.S. government customers have represented that they would not have awarded or renewed contracts for the forensic software had they known that OxygenUS was a Russian-owned company,” the complaint reads.

Natalia Krapiva, senior tech-legal counsel at Access Now, celebrated what she nonetheless called an overdue move from DOJ.

“For years, civil society warned that Oxygen Forensics was owned and built from Russia. Now the Justice Department confirmed it,” Krapiva told CyberScoop. “We applaud the U.S. government for taking this crucial step, but the fact that it took so long is both a national security and a human rights scandal.”

“The same technology that extracted data for U.S. investigations has been used inside Russia to jail journalists, activists, and peaceful dissenters. And it doesn’t stop at the U.S. border,” she continued. “We call on the U.S. and over 100 governments using this technology to immediately sever all ties to the company, implement sanctions, and conduct full investigation(s) of how Russian tech designed for the FSB spent all these years inside their sensitive law enforcement operations.”

Court-listed attorneys for Reiber listed in court documents didn’t respond to requests for comment. No attorney for Davydov could be located.

The DOJ in its announcement specified that “The complaint does not allege that the software contained malicious code or that it was used to gain unauthorized access to any customer’s computer systems or data.”

The post Phone-hacking company that won U.S. security agency contracts hid Russian ownership, DOJ alleges appeared first on CyberScoop.

FTC rescinds policy statement requiring health apps to notify customers after a breach 

The Federal Trade Commission has rescinded a Biden administration-era policy statement that asserted coverage over health and fitness apps under federal data breach notification regulations.

In a half-page statement posted Wednesday, the FTC said it “has determined that the statement – contentious at the time of issuance – provided minimal benefit and has been superseded by rulemaking.” The commission said the statement’s withdrawal also aligns with guidance from the White House to pursue a deregulatory agenda and avoid “unnecessary use of subregulatory guidance.”

Unlike a formal regulation, which carries the legally binding force of law created through a public rulemaking process, an agency policy statement is non-binding guidance that merely outlines how officials intend to interpret and enforce existing statutes. An FTC spokesperson told CyberScoop that the underlying policy including health apps remains codified through a regulatory update in 2024.

“Each of these reasons is independently sufficient to support the Commission’s decision to rescind this policy statement,” the FTC continued. “Parties understand that guidance generally creates neither substantive rights nor binding obligations.”

The initial policy statement, passed in a divided 3-2 vote during the Biden administration under then-FTC chair Lina Khan, asserted that health apps, fitness trackers and other connected devices were covered under an existing regulation requiring companies to disclose health-related data breaches to customers.

The interpretation targeted any “vendor of personal health records that contain individually identifiable health information created or received by health care providers.” Many health and fitness apps ask users to upload medical records and other health-related data in order to function effectively.

More recently, health and cybersecurity experts have pointed to similar regulatory gaps that exist for AI companies that make healthcare specific models that can answer questions, examine patient records and dispense medical advice to users.

The underlying Health Breach Notification Rule also triggers automatic notification when a covered entity suffers a breach of security, which can include both standard breaches and data losses as well as the disclosure of sensitive health information to third parties without users’ authorization. That would potentially put health apps on the hook for selling customer data to third-party data brokers and other entities-a standard formally codified in a binding 2024 FTC rule update.

A Sept. 2021 statement by the FTC justifies its interpretation by citing digital security and privacy provisions in the 2009 American Recovery and Reinvestment Act as well as gaps in major health privacy laws like the Health Insurance Portability and Accountability Act that allow such apps to handle and store sensitive personal health records or data without being subject to the same breach notification requirements as other health care organizations.

The FTC said it intended to enforce health apps under the law and subject violators to daily fines of $43,792 per violation.

“As many Americans turn to apps and other technologies to track diseases, diagnoses, treatment, medications, fitness, fertility, sleep, mental health, diet, and other vital areas, this Rule is more important than ever,” the FTC said in 2021. “Firms offering these services should take appropriate care to secure and protect consumer data.”

This week, the FTC voted unanimously to rescind the policy statement. But that unity is in part because President Trump fired Democratic FTC commissioners who voted in favor of the original rules, while advancing party allies as their replacements.

The two dissenting votes against the policy statement in 2021 were from Republican-appointed commissioners casting their dissents under a Democratic executive. Andrew Ferguson, a Republican commissioner nominated by former Democratic President Joe Biden, is now chair of an FTC filled entirely with Republican appointees, and has defended President Trump’s authority to fire and hire new commissioners at-will.

Update, 9/11/26, 4:15 p.m.: This story has been updated to clarify the impact of the FTC’s policy statement revision.

The post FTC rescinds policy statement requiring health apps to notify customers after a breach  appeared first on CyberScoop.

Lawmakers call on Commerce to sanction hackers-for-hire

A bipartisan trio of lawmakers is asking the Commerce Department to sanction three India-based mercenary hack-for-hire groups that have reportedly stolen data from thousands of American citizens and companies.

Democratic Sens. Ron Wyden of Oregon and Sheldon Whitehouse of Rhode Island and Rep. Pat Harrigan, R-N.C., sought in a letter to Secretary Howard Lutnick Wednesday to have the mercenary firms added to the Treasury Department’s Entity List, which would limit their access to American software, cybersecurity tools and cloud infrastructure.

“Several India-based cyber-mercenary groups have spent more than fifteen years conducting targeted espionage against U.S. citizens, businesses and the lawyers representing them,” Wyden, Harrigan and Whitehouse wrote. “Compounding this security threat, these cyber mercenaries and their associates have engaged in an aggressive campaign of global lawfare to censor investigative reporting by prominent American media organizations. This coordinated effort effectively allows foreign entities to use foreign courts to keep the American public in the dark about cyber threats to their own country and undermines the fundamental constitutional rights of U.S. citizens.”

The three firms are Sunkissed Organic Farms, BellTroX and CyberRoot. The first of those three was formerly known as Appin and has been the subject of investigative reports and criminal probes. The Citizen Lab at the University of Toronto has delved into the work of BellTroX, and journalists also have reported on the activity of CyberRoot.

“The threat is further heightened by evidence that these groups have operated at the behest of the Qatari government, targeting opponents of Qatar’s World Cup bid and even the family of a former Republican Chairman of the House Permanent Select Committee on Intelligence,” the lawmakers wrote. “While one of these operatives has been indicted by the Department of Justice, the foreign hackers continue to operate with impunity.”

Reuters reported in 2023 that the family member was Kristi Rogers, wife of former House Intelligence Chairman Mike Rogers, now running for Senate as the GOP candidate against one of the midterms’ most important and contested races against Democrat Abdul El-Sayed.

Some of the hacking groups also have sought to censor reporting on their hacking activities, the lawmakers noted.

CyberScoop couldn’t reach the companies for comment. The Commerce Department also didn’t immediately respond to a request for comment, and the government of Qatar didn’t immediately respond to an email seeking comment on the letter. TechCrunch first reported on the letter.

Corrected 9/10/2026: to reflect department to which the lawmakers addressed the letter.

The post Lawmakers call on Commerce to sanction hackers-for-hire appeared first on CyberScoop.

FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching

Artificial intelligence is souping up the speed and capabilities of malicious hackers, a top FBI official said Tuesday. And the speed of vulnerability discoveries is forcing organizations to patch more frequently, said another top FBI official.

The officials made their remarks one day before the release of a new FBI cyber strategy Wednesday, which touches on AI, relief and justice for victims and other bureau priorities.

Speaking to both CyberScoop and at the Billington CyberSecurity Summit, Jason Bilnoski, deputy assistant director of the FBI’s cyber division, said AI is “taking actors to the next level.” 

“You’re going to have additional offensive actions coming at your environment, targeting the network at speed and capability,” he said. And he expects it to keep getting worse, with AI-enabled attacks already having a measurable impact, as demonstrated by the numbers in a new section of the annual FBI report on digital crimes.

“The wave is coming. I don’t think we’ve hit the crest yet,” Bilnoski said. “We see an exponential increase in the use of AI, whether it’s nation-state or criminal.”

Still, AI isn’t doing anything that attention to cybersecurity basics wouldn’t prevent, Bilnoski said. It’s something the FBI sees again and again when it conducts investigations, even those with an AI element.

“The adversaries are still [exploiting] basic principles or basic cyber hygiene principles that we are not following,” he said, referring to a recent FBI emphasis on 10 fundamental defensive measures like multifactor authentication. “If we can harden up those top 10 controls that we talked about, it would certainly reduce the risk of both criminal and nation-state targeting of our environment.”

“What will prevent the attacks in the next 18 months are the same things that would have prevented the attacks of yesterday,” he said.

The FBI, meanwhile, will “continue to pursue AI in a way that will help us defend at scale,” Bilnoski said.

Patching pacing

The speed at which AI models are uncovering vulnerabilities means organizations need to rethink their approach to patching, another FBI official said at the Billington event.

“We no longer can essentially do the quarterly patching,” said Colleen Ferranti, assistant section chief, cyber engagement and intelligence section. “We have to evolve with the time, and we have to do more risk-based type patching, and we have to be doing that continuously.”

“So, from our perspective, the day-to-day or quarterly or Patch Tuesday — this needs to be a patch-all-of-the-time, and making sure that we are tracking our systems to also be engaging with that type of technology and at that speed and that level,” she continued.

AI now in FBI cyber strategy

The FBI strategy also has a section devoted to artificial intelligence.

“FBI Cyber will deploy AI-enabled tools to triage large datasets, surface relationships, accelerate malware analysis, prioritize victim notifications, map adversary infrastructure, support attribution, and identify patterns that no human analyst could process at the required pace,” it states. “Consistent with President Trump’s Cyber Strategy for America, FBI Cyber will rapidly adopt agentic AI in ways that securely scale defense and disruption, and will implement AI-enabled tools to detect, divert, and deceive threat actors where operationally appropriate.”

The FBI likewise wants to develop additional tools and techniques, according to the strategy.

“The FBI will continue to develop its Computer Network Operations (CNO) program, providing investigative teams with the court-authorized or otherwise lawfully authorized technical operations tools to remotely collect, conduct surveillance, and disrupt the activities of nation-state and cybercriminal actors when traditional investigative techniques will not achieve the required outcome,” it reads.

The strategy largely reflects a number of existing practices at the agency, such as a focus on disrupting attackers. But one emphasis is on relief and justice for victims.

It contains a “pledge” in support of them: “Pursuing our mission, we recognize that we will encounter unique and novel issues related to privacy and the handling of sensitive data. We will always treat victims with dignity and respect, protect their privacy and data, and rigorously adhere to the U.S. Constitution; applicable laws, regulations, and policies; and the FBI’s Core Values.”

It also promises to quickly share threat intelligence, swiftly respond after incidents and expand “its Industrial Control Systems (ICS) Coordinator program to designate dedicated personnel in every field office.” 

It’s the latest document of the Trump administration to focus on cyber strategy, following the release earlier this year of its overall cyber strategy and the Defense Department’s version expected to publish soon as well.

Clarified 9/9/2026: A quote from Colleen Ferranti has been edited for clarificiation.

The post FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching appeared first on CyberScoop.

European parliament members call for slowdown of Serbia’s EU entry over spyware use

A group of European Parliament representatives are seeking to delay Serbia’s entry into the European Union and send other messages to Belgrade over the government’s usage of spyware.

The 29 members of the European Parliament (MEPs) cited a report this week from the SHARE Foundation about spyware found on the phones of Serbian student activists and that targeted others as well. The foundation, along with Amnesty International and The Citizen Lab at the University of Toronto, discovered both Pegasus and NoviSpy spyware infections.

The groups didn’t assign responsibility for the Pegasus infection, but said evidence from the NoviSpy infections pointed to Serbian government authorities.

“This is not a technical glitch; it is a direct state attack on democracy,” the 29 MEPs wrote Friday. “With upcoming elections ahead, Aleksandar Vučić’s regime is using illegal digital surveillance to systematically dismantle political opposition.”

The MEPs’ demands include slowing Serbian accession into the EU until completing an investigation into Serbia’s spyware usage and making Serbia’s accession contingent on improving rule-of-law accountability.

They also said President Ursula von der Leyen should cancel a planned visit to Serbia. European leaders were already outraged by the response from Serbia to the death of former Bosnian Serb army commander and war criminal Ratko Mladic, with Enlargement Commissioner Marta Kos canceling her own visit Friday over the alleged “glorification” of Mladic.

The spyware letter adds to the pressure, said Hannah Neumann, an MEP who signed it.

“It could very well be that some of these demands will be honored, but for sure the spyware won’t be the only reason why,” she told CyberScoop. Serbia’s history of spyware use contributed to Friday’s letter, she said: “We have been critical towards the government for already quite some time and demanded consequences so this was another straw.”

The Serbian government did not respond to multiple requests late Friday for comment.

“Appeasement has failed,” the members wrote. “It is time for the Commission to demonstrate that compliance with fundamental democratic standards is a non-negotiable requirement, not an option.”

European Union member nations have faced their own allegations over using spyware, and recent revelations of spyware found on the device of a member of the European Parliament’s PEGA Committee has prompted some to renew calls for enactment of recommendations from that committee to address spyware abuses.

The post European parliament members call for slowdown of Serbia’s EU entry over spyware use appeared first on CyberScoop.

Pegasus, NoviSpy variant spyware found on devices of Serbian activists

Researchers say they have uncovered the first confirmed Pegasus spyware infection of 2026, as well as another spyware variant infection, targeting Serbian student activists and others in what one group called the largest documented wave of that kind of surveillance in the country to date.

The SHARE Foundation said Wednesday that it found 14 people targeted in all, including one member of parliament and a local government official. The University of Toronto’s Citizen Lab confirmed the Pegasus infection of a student activist with “high probability,” while Amnesty International confirmed that two devices had been infected with a new version of the NoviSpy spyware.

The SHARE Foundation noted that the infections coincided with the build-up to key local elections in March that were viewed as a test of the ruling Serbian Progressive Party, with student protests rising in the wake of the 2024 Novi Sad railway station canopy collapse, and in advance of October parliamentary elections.

Serbian activists have found themselves targeted with spyware numerous times before, including by Pegasus and NoviSpy. But the SHARE Foundation said this was the biggest wave there so far.

Spyware is noted for its ability to access everything on a device, record screens or take over its microphone.

NoviSpy variant infections

One NoviSpy variant infection came after authorities took a student’s phone during police questioning, and the same spyware was found on another device as well after private messages from the phone were disclosed by a media outlet that favors the ruling party, SHARE Foundation said.

The SHARE Foundation said signs point to Serbian police or secret service being behind the NoviSpy variant cases, with Amnesty International offering a similar assessment. 

“These new forensic findings show that Serbian student activists continue to be targeted with invasive spyware,” Donncha Ó Cearbhaill, head of Amnesty International’s Security Lab, told CyberScoop. “As with NoviSpy, which Amnesty International found used extensively in Serbia in 2024, the evidence suggests the infections are being carried out during detention by the Serbian authorities.”

Pegasus infection

In the case of the infection from NSO Group’s Pegasus spyware, it’s rare for investigators to determine who specifically made use of it, although they found that the student’s device was hacked with a Pegasus zero-click exploit from December of last year to January of this year. The infection came via a zero-click exploit — meaning without victim interaction.

But Citizen Lab said the Serbian case harkens back to the first discovery of Pegasus a decade ago when it was against a pro-democracy activist, Ahmed Mansoor.

“Today, Pegasus is still being used to hack people campaigning for democracy,” said John Scott-Railton, senior researcher. “NSO spent a decade promising reform, yet their spyware is still an instrument of political repression.”

NSO Group maintains that its spyware is for usage against terrorism and crime, and that it halts any abuses it discovers.

The spyware discoveries in Serbia came after Apple sent threat notifications to the targets.

“Apple’s updates have broken this particular exploit, so we urge everyone to make sure they are updated to the latest version of iOS,” said Bill Marczak, senior researcher at Citizen Lab.

The post Pegasus, NoviSpy variant spyware found on devices of Serbian activists appeared first on CyberScoop.

Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities

A class action lawsuit filed by victims of child sexual abuse material (CSAM) accuses xAI of training Grok’s synthetic deepfake “nudify” capabilities on real images and videos of child abuse.

The lawsuit, filed Wednesday in the U.S. District Court for the Northern District of California, names Jane Doe 1 and other anonymous individuals as plaintiffs, calling Doe “an identified victim of child pornography tracked by the Federal Bureau of Investigation’s Child Exploitation Notification Program.”

Doe was a pre-school aged child when her perpetrator’s abuse began and continued for years, for the explicit purpose of making CSAM material to distribute online. Media depicting the victim has circulated online since at least the early 2000’s, with, according to the lawsuit “hundreds of thousands of files” being included in law enforcement submissions to the National Center for Missing & Exploited Children (NCMEC).

As part of the FBI’s program, she still receives updates when images related to her abuse surface online, and the suit alleges her material has “well known hash-values” that have shown up in deepfakes created with Grok and spread on X.

“CSAM depicting Plaintiff has been found on xAI as part of investigative reporting, takedown request efforts, and criminal investigations, arrests, and convictions for violations of state and federal laws,” the lawsuit states. It also claims “xAI, using Grok, has generated images depicting Plaintiff and the child pornography series in which she is the victim.”

The lawsuit cites “Masha’s Law” as the basis for its allegations. That law, passed in 2018,  protects civil legal remedies to victims of child pornography and online exploitation.

According to an analysis by the Center for Countering Digital Hate, during an 11-day period between Dec. 2025 and Jan. 2026, Grok created more than 3 million sexualized images, at least 23,000 of which appeared to depict children.

On Jan. 14, after the period tracked by the center, Musk wrote on X that he was “not aware of any naked underage images of Grok. Literally zero.” Must also implied that users, not his technology, were primarily responsible for images created using Grok while simultaneously claiming the model “will refuse to produce anything illegal” if asked.

The suit claims that while other competitors enacted guardrails to prevent their AI models from generating “nudified” images of adults and children, xAI “did the opposite,” embedding Grok and it’s deepfake capabilities directly into X, effectively creating an instantaneous CSAM generation and distribution system for the internet.

While xAI said it built in guardrails to prevent Grok from creating deepfake sexualized images, the suit notes that they are “very weak,” diverge from standard industry best practice and can be easily circumvented.

The system rejects prompt prompts where the chatbot detects “clear intent by the user in the phrasing of their request,” the complaint stated. “Indirect or euphemistic prompts can easily slip past a text-based filter, so if the model retains the underlying capability to generate sexual or abusive content, some volume of CSAM becomes effectively inevitably generated by the system.”

The lawsuit also notes that Grok’s terms of service treat anything that gets posted on X as training material, meaning any CSAM material posted on the site over the past year was likely ingested by the model.

The alleged victims are asking for monetary damages along with injunctions to prevent Grok from creating additional harm through future sexualized deepfakes or CSAM. The suit lists “thousands” of members in the class, all with similar claims against xAI.

A request for comment on the lawsuit sent to xAI was not returned.

Grok’s nudification capabilities, and xAI owner Elon Musk’s dismissive public attitude around the fallout have led to international outrage, criminal investigations and a wave of private lawsuits against the company.

Another lawsuit against X filed earlier this year claims that a man used Grok to generate thousands of instances deepfake CSAM material of his stepdaughter. That lawsuit also claims xAI withheld information from law enforcement authorities that would have helped them identify the stepfather as the perpetrator. Days after authorities traced and seized the material on the wte, he committed suicide.

In July, Musk sued Minnesota Attorney General Keith Ellison over a new state law that bans nudification technology and impose a $500,000 fine for each instance where an AI tool is used to generate or alter an image in a sexually explicit way. Musk’s lawsuit claims the ban violates the First Amendment.

The post Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities appeared first on CyberScoop.

Lawmakers seek watchdog review of federal hacking of Americans

A pair of lawmakers wants a watchdog agency to probe how the federal government hacks Americans, including with the use of spyware, and deliver a report to the public.

Sen. Ron Wyden, D-Ore., and Rep. Greg Casar, D-Texas, wrote to the Government Accountability Office on Friday to request the review.

“While federal law enforcement agencies have used hacking and spyware as an investigative tool for more than 25 years, there exists little public information regarding its scope, frequency, or operational safeguards,” they wrote. “Unlike traditional surveillance authorities, such as wiretaps or pen registers, the government does not publish annual reports for hacking operations.”

The issue of U.S. government spyware usage has grown in prominence in President Donald Trump’s second term, as Immigration and Customs Enforcement has acknowledged working with spyware firm Paragon. Lawmakers have been asking whether that’s the full extent of U.S. government reliance on spyware after the Biden administration largely shunned it.

But the Wyden and Casar letter is broader than just spyware. It also touches on the federal government’s acquisition of hacking tools, like those in the case of a former senior official at defense contractor L3Harris who was sentenced this year for stealing and selling capabilities developed for the federal government, and Rule 41 hacking powers.

The congressional duo asked GAO to review documented cases of federal law enforcement misusing hacking capabilities for personal or otherwise unauthorized reasons, and what kind of safeguards agencies have against hacking abuses.

“Spyware and other hacking tools grant expansive access to personal devices, including webcams, location data, stored files, and encrypted communications,” they wrote. “Unrestricted access to such invasive surveillance capabilities invites abuse by rogue agency personnel. Indeed, there are countless documented examples of government employees abusing other sensitive surveillance databases and tools for unauthorized personal purposes.”

They also asked GAO to review how agencies buy and protect sophisticated hacking tools, and how agencies make Rule 41 hacking requests to courts.

TechCrunch first reported on the letter from Wyden and Casar.

Casar is the top Democrat on the House Oversight Subcommittee on Federal Law Enforcement, and Wyden has a long career of scrutinizing federal intelligence and surveillance efforts.

The post Lawmakers seek watchdog review of federal hacking of Americans appeared first on CyberScoop.

Retail theft bill spurs ‘very large and very dangerous’ surveillance fears

A bill to battle organized retail theft has wide bipartisan support and momentum on Capitol Hill, even as opponents say it threatens to dangerously expand surveillance centered in Immigration and Customs Enforcement at a time when the agency’s aggressive conduct is under scrutiny.

Backers counter that critics are wrong about the bill that they say only would enhance existing information sharing arrangements, and could play a role in fighting cyber-enabled crime, too.

At its core, the Combating Organized Retail Crime Act (CORCA) establishes an Organized Retail and Supply Chain Crime Coordination Center within ICE’s Homeland Security Investigations division. It also would create criminal penalties for money laundering proceeds from selling stolen goods, and a $5,000 threshold for the combined total value of stolen property over a year for charging purposes.

It passed the House in June by a vote of 348-60, and Senate supporters are pushing for its inclusion in the annual defense policy bill, considered “must-pass” legislation that Congress has cleared for more than 60 consecutive years.

Opponents are trying to beat back CORCA, which arose from fears of mass theft during the COVID-19 pandemic.

“Its design actually creates a very large and very dangerous surveillance network,” said Nina Patel, senior policy counsel at the justice division of the American Civil Liberties Union. “You would hear the words ‘organized retail crime’ and think that this might be about shoplifting, and you would be surprised to learn that much of the apparatus is concentrated within the Department of Homeland Security.”

The objections

Patel and Jina John, her colleague at the ACLU, said the bill inadequately defines key terms: “organized retail crime,” even, as well as “retailers,” and what kind of data can be shared.

“It’s very broadly and vaguely drafted, and so the way it’s done is that it establishes all these mechanisms for data sharing among these entities, including getting data directly from retailers,” said John, senior policy counsel for AI, privacy and technology. “The data sharing is for any threats related to retail and supply chain crime. That’s it, just: threats. …That’s the biggest concern, is that this is basically giving DHS access to retail surveillance,” she said, like surveillance cameras at malls and train stations, Flock cameras and automated license plate readers.

Rather than the federal government purchasing data from brokers for surveillance purposes — already a contentious practice — CORCA gives them an avenue to get it freely, John said.

A variety of civil liberties and civil rights organizations are among the coalition trying to defeat CORCA. A key issue for many of them is the fusion center at ICE, which has collated data like cell phone location, health and other information, said Spencer Reynolds, senior counsel at the Justice in Public Safety Project at the NAACP Legal Defense and Education Fund. Adding retail data makes that worse, he said. 

“Together, this information allows ICE to hunt down people, find their families and associates, and pull them from their communities,”  he said. “The agency, over the last couple of years, especially, has been openly engaging in racial profiling, and poor Black and Brown people are likely to feel the impact of this the most.”

Reynolds continued: “The entire model that CORCA is going to impose allows government and industry participants to overcome protections, safeguards, guardrails, and use government to target their opposition.”

The support

Backers argue that the bill poses no risk to anyone but organized retail crime leaders.

“Over the years, organized retail crime has evolved into a deadly, multi-jurisdictional threat to American lives, the United States’ economy and our national security,” Senate Judiciary Chairman Chuck Grassley, R-Iowa, said in a statement. “My Combating Organized Retail Crime Act is a targeted, bipartisan bill that would crack down on large-scale retail theft by coordinating federal, state and local law enforcement efforts, while aligning existing resources.” 

A Senate Judiciary Committee spokesperson said the bill doesn’t give DHS any additional enforcement authorities, and is housed within DHS’s Homeland Security Investigations to build on the role they currently have in addressing transnational and organized criminal activity.

The American Trucking Associations supports the bill, and its legislative director Alex Rosen disputed opponents’ claims about its surveillance risks. 

“When you can’t argue the merits of the legislation, it’s easy to revert back to stale, overused buzzwords and an attempt to rile up opposition,” she said. “The idea that this would increase government surveillance is nutty because what this does is it creates within HSI a kind of central reporting repository for industry to report high-level crimes, crimes that are part of big organized criminal theft groups … The idea that this would somehow give the government more authority to surveil Americans is crazy because nowhere in the text does it say that.”

David Johnston, vice president of asset protection and retail operations for the National Retail Federation, noted the difference between ICE’s HSI, focused on a variety of criminal investigations including cybercrime, and its Enforcement and Removal Operations division that’s focused on finding and evicting those who violate U.S. immigration laws.

The bill could be one answer to rising cybercrime, he said.

“There has really been a substantial increase in not only the activity but the methods, the tactics, and as retail has evolved into the digital environment as much as it is in the physical store environment — we’ve seen the criminal, the organization, the structure, the convergence between how cyber and physical thieves operate,” he said, mentioning gift card fraud, or e-commerce fraud that started from a phishing or account takeover. “It’s really become a substantial issue for retailers, consumers, communities across the board.”

Cyber means have also aided cargo theft with the creation of false personas and more, Johnston said: “They’re not going and stealing these trucks with physical violence. They’re driving them right out of the yard, waving to the security officer because they’ve got this whole organization behind them that are using these cybercriminal tactics.”

Where it’s headed

Both sides are optimistic that they’re making progress on the bill. Kristina Roth, the senior policy associate leading the NAACP LDF’s criminal legal system policy portfolio, said a number of lawmakers who actually sponsored the legislation voted against it on the floor.

That points to lawmakers becoming more educated on the bill, which moved swiftly this year from committee to a full vote. “I think the connections that this legislation has through DHS were maybe not well enough described as they could have been,” Roth said.

Patel said there’s more work to be done.

“What is really disturbing about this bill is the way it’s been presented to a number of legislators, and it keeps getting this moniker of being a bipartisan bill,” she said. “But I think few people recognize just how much power is being given to ICE, the complete lack of accountability from DHS and ICE under this administration and in the past, and empowering them to reach into Main Street and into consumer spaces.”

Rosen pointed to the wide House vote as well as bipartisan support from leaders of key committees, such as the Judiciary and the Senate Homeland Security and Government Affairs committees, to include the bill in the annual National Defense Authorization Act. The nature of the support has supporters optimistic about the chances for CORCA to become law.

The defense legislation often wins passage around the end of each calendar year. 

The post Retail theft bill spurs ‘very large and very dangerous’ surveillance fears appeared first on CyberScoop.

❌