❌

Reading view

There are new articles available, click to refresh the page.

Trump picks Palantir’s LoSapio to head CISA

The Cybersecurity and Infrastructure Security Agency finally got a new nominee for director, with President Donald Trump on Monday nominating Michael LoSapio, chief information security officer at Palantir.

CISA has been without a Senate-confirmed director for the entirety of Trump’s second term, after his first pick, Sean Plankey, languished in the Senate before withdrawing in April.

LoSapio could face some obstacles of his own, with Palantir far from a popular company with the Democrats set to take over Congress. Democrats have scrutinized the company over its work with the Department of Homeland Security, even as Palantir has denied aiding mass surveillance of immigrants.

As of late last month, Sen. Ron Wyden, D-Ore., was also still waiting for CISA to release a public version of a report on telecommunications cybersecurity, and he had placed one of several Senate holds on Plankey pending the receipt of that report.

Republicans will still control the Senate until January, however, and a lame-duck session began Monday.

Some CISA watchers were convinced that the agency’s acting director, Nick Andersen, was likely to continue holding the role. He was running out of days to hold the “acting” position under the law, but putting forward a nominee could pause the clock on that deadline.

The administration was thought to be looking for someone from a high-profile tech company to fill the CISA director position, a bill LoSapio fits.

The post Trump picks Palantir’s LoSapio to head CISA appeared first on CyberScoop.

Could Nick Andersen’s leadership outlast the clock on his acting role?

The clock is running out on Nick Andersen’s time to serve as acting director of the Cybersecurity and Infrastructure Security Agency, but there appear to be efforts afoot to keep him in the role for longer, with no permanent nominee in sight.

There’s broad support for the idea of Andersen retaining the position one way or another, which he’s held since February of this year. Since then, Sean Plankey withdrew his nomination for the Senate-confirmed position in April, and in June, Department of Homeland Security Secretary Markwayne Mullin said a likely replacement nominee had met with the president and was coming soon. Four months later, no nominee has materialized.

“We proudly support the work Acting CISA Director Nick Andersen has done in his role,” a DHS spokesperson said in response to questions about keeping Andersen on board and what became of that potential nominee. DHS referred CyberScoop to the White House for any further comment, but the White House didn’t respond to inquiries.

The easiest way to keep Andersen in the acting role would be to select a nominee, thus pausing his 210-day limit on serving as acting director, said Mark Montgomery, senior director of the Foundation for Defense of Democracies think tank’s Center on Cyber and Technology Innovation.

But “my gut reaction is that there’s just no appetite at the White House to say the four-letter ‘CISA’ to the president,” given his past animosity toward the agency, Montgomery said. “The way to keep Andersen in play is to nominate somebody. I think that stops the clock. But I don’t even think they can get the president to nominate Bugs Bunny. To me, that’s troubling.”  

Other top agency positions have received Senate confirmation under Mullin, Montgomery observed.

Multiple sources told CyberScoop they’ve been told that the administration has been working to keep Andersen in the job, possibly by shifting his title to “senior official performing the duties of” CISA director.

Some would like to see Andersen receive the job full-time, but sources say that when the search to replace Plankey began, the administration was looking for someone with a high pre-existing profile, such as a role at a big-name tech company.

On Capitol Hill, the leaders of the House Homeland Security Committee offered at least some  degree of support for Andersen.

“Acting Director Andersen is doing an excellent job preparing CISA to meet today’s threats, and we have a great working relationship. He has shown exceptional leadership at the agency, which is especially important in an increasingly complex threat environment as adversaries and criminals use AI to expand their capabilities and make attacks on our networks and critical infrastructure harder to defend against,” said Chairman Andrew Garbarino, R-N.Y. “I appreciate our partnership and would gladly support his nomination.”

“Acting Director Andersen has provided some much-needed stability to CISA following a year of chaos and incompetent leadership,” said the panel’s top Democrat, Bennie Thompson of Mississippi. “While we may have our differences, I appreciate his dedication to the mission: securing government networks and the critical infrastructure ordinary Americans rely on every day. I am also concerned that any unnecessary changes to CISA’s leadership could once again destabilize CISA, which would make America less safe. It is in the best interest of CISA’s mission to have an empowered leader who has earned the trust of the agency’s workforce and its stakeholders.”

One industry source also said Andersen was a popular leader.

“Frankly, from everything [I’ve heard], people broadly support Nick, and he’s doing well at CISA,” the source said. “I don’t get the sense that anyone in the White House wants to make the effort to nominate a CISA director, which is a missed opportunity. With limited time remaining in this Congress, the administration would be wise to push his nomination through the Senate and put Nick on firmer footing.”

Andersen has made a tangible difference at an agency that has seen dramatic budget and personnel cuts, said John Zangardi, a former chief information officer at DHS.

“The organization is actually getting much better under Nick,” said Zangardi, chair of the Northern Virginia Technology Council Cyber Summit and Cyber50 Awards. “Like if you were there a year ago, it was pretty stark. … So morale has kind of gone back up, and I think Nick has been very instrumental in that. And I think he’s important in keeping that continuity going.”

One of the notions of having a Senate-confirmed nominee is for the prospective leader to be well-vetted by an outside body. On the other hand, it can also lead to nominees being stalled as senators press other agendas, something that Plankey ran into on multiple occasions.

But having a Senate-confirmed nominee at the agency also helps CISA compete for its priorities within the interagency process and at the White House, Montgomery said. Absent that, keeping Andersen in the position in some capacity is the next-best option, he said.

Montgomery also said Andersen has been making longer-term plans at the agency. Most recently, it released a strategy meant to carry CISA through 2030.

Andersen “strikes me as someone who knows he’s got more than a month left in his job,” Montgomery said. “He’s thinking hard about it, and he’s starting to think three to six months out, which is a lot for this administration.”

The post Could Nick Andersen’s leadership outlast the clock on his acting role? appeared first on CyberScoop.

CISA publishes strategy with eye on the next four years

The Cybersecurity and Infrastructure Security Agency published a strategy Monday that focuses on taking a leading role in cyber defense, prioritizing protection of critical infrastructure and building the ability to withstand attacks.

The 10-page strategy — “CISA 2030: Defend, Harden, Prevail” —  largely reaffirms existing roles for the agency, but CISA will begin reviewing its core services and capabilities within 60 days to make sure they meet key objectives, followed by implementation over the next 180 days and an update on its progress after one year.

Acting CISA Director Nick Andersen said in a foreword that the agency needs to act with “renewed purpose” in the face of threats.

“The threat landscape we face today is not static,” he said. “Nation-state actors and other malicious adversaries continue to grow more sophisticated in their efforts to compromise our networks, and there is no guarantee that a strong defense will eliminate intrusions. As President Trump has reminded us, resilience must be the foundation of our approach. We must ensure that when adversaries gain a foothold, we are prepared to detect them quickly, evict them decisively, and keep critical operations running without interruption.”

The strategy is also meant to align with the administration’s broader cyber strategy, published in March, and last year’s executive order on state and local preparedness.

“I call on every company and organization in the critical infrastructure community — from owners and operators to vendors and technology manufacturers — to act now,” Andersen said in a comment released with the strategy. “CISA 2030 provides a focused roadmap to strengthen defenses, eliminate adversarial footholds, and deny them any advantage that could endanger the nation’s security, economy, or public health.”

Within each section of the strategy, there are other goals listed.

Under “defend: lead national cyber defense,” the key objectives are to integrate state, local and industry cyber defense; protect operational technology; developing guidance and best practices on software security; and assess and develop emerging technologies.

Under “harden: prioritize national infrastructure security,” the key objectives are to coordinate intelligence for critical infrastructure; analyze infrastructure data; work with international partners; and emphasize strengthening the nation’s most important infrastructure.

Under “prevail: mobilize national resilience,” the key objectives are to invest in critical infrastructure resilience; strengthen national communications interoperability; modernize planning and exercises; and build next-generation interoperable infrastructure.

Critics say much of CISA has been badly diminished by budget cuts at the agency by the Trump administration, including many of them specifically a focus of the new strategy, that have left it understaffed.

The last strategic plan at the agency, published in 2023, also had three pillars: address immediate threats, harden the terrain and drive security at scale.

The post CISA publishes strategy with eye on the next four years appeared first on CyberScoop.

Governments ‘buying time’ in race between innovation, security, national cyber director says

The United States and allied governments are “buying time for our systems to become more secure” as artificial intelligence advances and spreads, National Cyber Director Sean Cairncross said Thursday.

“That is a big deal to be ahead of this, to be ahead of this race, and because it’s an exponential  equation,” he said at the Billington CyberSecurity Summit. “Once you fall behind, it is much more difficult to make it up, and so that is the context in which all this is taking place. We are trying to balance the innovation side of running at speed with securing our systems and handling this technology responsibly, which is to say, not letting it fall into the hands of people who would do us harm, our adversaries.”

Earlier this week, U.S. security agencies accused Chinese AI companies of trying to illegally distill U.S. frontier AI models. Also this week, Anthropic disclosed a fourth AI hacking incident where one of its models broke into third-party systems.

“We all face the same threat picture, and it’s vital that we’re working closely together to secure those systems before that technological cycle catches up on the back end,” Cairncross said.

AI has further exposed long-standing cybersecurity problems that have gone unaddressed, he said.

“In AI development, particularly on the vulnerability discovery side and the coding side, it hasn’t created a new set of problems,” Cairncross said. “What it’s done is it’s dragged to the surface problems that have been latent in this space for decades. There’s been under-resourcing and deprioritization of basic cyber hygiene and cybersecurity.”

Cairncross’s messages echoed those of other Trump administration cyber officials speaking this week at the summit.

A top FBI official, Jason Bilnoski, said the solutions to the difficulties AI poses aren’t new; basic cyber hygiene is key.

And the director of the Cybersecurity and Infrastructure Security Agency, Nick Andersen, said historical neglect of cybersecurity fundamentals poses a serious threat that requires a speedy answer.

“We know the worst that can happen, and if we don’t make some very serious, very significant changes in quick succession … you all are going to have to go home and look your family, look your friends in the eye and explain to them how you knew the worst that could happen and why we didn’t do enough,” he said.

The post Governments ‘buying time’ in race between innovation, security, national cyber director says appeared first on CyberScoop.

Industry’s message on CIRCIA: Please ask us fewer questions about cyberattacks

Industry groups who spoke at town halls hosted by the Cybersecurity and Infrastructure Security Agency about a pending cyber incident notification regulation had a few consistent messages:

We want this to apply to fewer of us. We don’t want to report to you on as many incidents. We want to give you less information when we do. 

CISA last week published transcripts from the town halls, where the agency sought feedback on the delayed rule for the 2022 Cyber Incident Reporting for Critical Infrastructure Act — perhaps the most significant cyber legislation Congress has ever passed. That law required critical infrastructure owners to report major cyberattacks to the federal government within 72 hours, and ransomware payments within 24 hours.

The law was designed to let the feds share information about significant incidents more widely to prepare other would-be victims. CISA published a proposed rule on the law in 2024 to define terms like “covered cyber incident” and more, and industry groups have persistently registered their objections since then.

CISA missed the October 2025 deadline for finalizing the rule, then missed a May reset target date, and now the administration says the rule will be completed in September.

Some industry sources told CyberScoop they consider that unlikely. Most also haven’t received any indications from CISA about how much of the town hall feedback it intends to embrace, they said.

Companies, incidents, information 

Those town hall comments over the course of four June dates were often very direct.

“The rule includes too many companies,” said Grant MacIntyre, director of regulatory affairs and senior attorney at the Auto Care Association. CISA estimated that more than 300,000 entities will be subject to its requirements.

Some industries advocated for their removal entirely, such as two different groups representing elements of the insurance sector. Some sought to reduce the number affected within their sector, such as the Nuclear Energy Institute wanting the list cut down to those already subject to Nuclear Regulatory Commission cybersecurity reporting requirements.

While CISA wrote the regulation with the intention to avoid overburdening small businesses, some feared it wouldn’t work that way in practice.

“The current approach where an entity qualifies either by size or by sector effectively negates the intended limitation on small businesses,” said Douglas Leigh, vice president of legislative affairs for the Alliance for Chemical Distribution. “In chemical distribution, even small entities could be swept in under multiple cyber categories.”

Where the rule specifies what kind of data organizations should report in a major incident, CISA should “seek to collect the least amount of information possible in the easiest to report fashion to facilitate information accuracy and reporting speed,” said Samantha Burch, vice president of technology public policy at government affairs at AHIP, a health insurance industry trade association.

Many, for instance, argued the report should not include information on the affected entities’ security measures.

Others worried about what kind of incidents would trigger reporting requirements.

“My big concern is that you’re going to be asking us to report incidents on every time some foreign entity tickles our firewall, whether they do anything or not, if they just do a ping or a search,” said Tim Pospisil, chief security officer for Nebraska Public Power District. “And that could be extremely burdensome.”

Industry Expectations

One industry representative told CyberScoop that CISA’s willingness to hold town halls, combined with the Trump administration strategy emphasizing “common sense regulation,” was a good sign about where the rule might be heading.

‘They are not picking up on the Biden administration’s approach and tweaking it. They’re thinking, ‘What are the specific pieces of information we need during a cyber incident to help critical infrastructure companies respond?’” said Henry Young, senior director of policy for the Business Software Alliance. “In general, industry is optimistic that what we’ll end up with are a few of the most important pieces of information, so that in the emergency, companies can act quickly and actually respond to an incident rather than completing lots of paperwork.”

But multiple industry sources said they haven’t gotten many indications about CISA’s intentions. Nor are they optimistic CISA can meet the September target date in the Unified Agenda of Regulatory and Deregulatory Actions.

“It could slip,” one said. “But I think they’re going to try.”

That industry source said they’d like to see a proposal from CISA before it cements anything forever.

Another industry source said it’s hard to trust the September date given past CISA delays, some of which aren’t CISA’s fault, such as dealing with multiple government shutdowns. Some of the delays trace to the Trump administration, given the massive cuts to CISA’s personnel.

Congress is also getting impatient.

The House Appropriations Committee “is concerned about delays in publishing the final CIRCIA rule and urges CISA to finalize it promptly following stakeholder review and feedback,” the panel wrote in the committee report for its fiscal 2027 Department of Homeland Security spending bill.

It’s a much different world than when CISA began writing the rule, something the agency also has to take into account now.

“AI has fundamentally changed the playing field,” the source said. “When this was set up, we didn’t even have the first generation of ChatGPT. We’re now in a mythos class environment.” That’s changed “how quickly we can identify threats, mitigate them, the level of human intervention, potential machine engagement.”

While CISA might have good intentions, past interactions give cause for skepticism about how capable it is of working collaboratively with industry, the source said.

Another industry source said conversations with CISA suggest the agency will look to simplify the regulation to keep it smaller and narrower, then potentially build upon it later.

From CISA’s mouth

Nick Andersen, the acting director of CISA, talked about his overarching intentions with CIRCIA at the town halls.

“CISA does not view CIRCIA as simply a check-the-box compliance exercise,” Andersen said at one. “CIRCIA will enhance visibility into the cyberthreat landscape to enable a robust national early warning capability for critical infrastructure. By quickly reporting covered cyber incidents and ransom payments to CISA, we will be able to provide timely and actionable defensive and eviction measures to your network defenders.”

Asked by CyberScoop about next steps for CIRCIA, and how it might incorporate the industry feedback, a spokesperson provided a statement.

“CISA recognizes the importance of CIRCIA, however, multiple funding lapses impacted CISA’s ability to conduct rulemaking activity for CIRCIA. CISA continues to work on the final rule,” the spokesperson said, adding that 1,200 critical infrastructure stakeholders attended the town halls.  “CISA will continue to communicate updates on the CIRCIA rulemaking process and timeline through CISA.gov/CIRCIA and the Office of Information and Regulatory Affairs’ Unified Agenda of Regulatory and Deregulatory Actions.”

The post Industry’s message on CIRCIA: Please ask us fewer questions about cyberattacks appeared first on CyberScoop.

Trump budget boss Russell Vought open to re-staffing CISA

Trump administration budget chief Russell Vought told lawmakers Tuesday that he’s willing to work with Department of Homeland Security Secretary Markwayne Mullin on re-staffing up the Cybersecurity and Infrastructure Security Agency, following deep personnel cuts and further proposed reductions in the fiscal 2027 budget blueprint.

Mullin said last week at a House Appropriations Subcommittee on Homeland Security hearing that he would like to hire 600 more people at CISA, similar to remarks he made earlier this month at another House hearing. President Donald Trump has cut or lost more than 1,000 from an agency that stood around 3,400-strong at the end of the Biden administration — cuts criticized by lawmakers in both parties.

At a House Appropriations Subcommittee on Financial Services and General Government   hearing Tuesday, Rep. Mark Amodei, R-Nev., asked Vought about Mullin’s CISA remarks.

“You don’t just flip a light switch on, and you got 600 folks over in CISA now. What’s the plan for getting CISA fully operational?” Amodei, who chairs the panel’s Subcommittee on Homeland Security, asked. “How do we make sure we have a robust, effective, cost-effective CISA force? Because I don’t think anybody thinks we have it now.”

Vought, director of the Office of Management and Budget, said he hasn’t received a formal request from Mullin to increase CISA’s number of full-time employees, but knows that hiring isn’t instantaneous.

“He was not here when we developed this budget, so if he feels the need to have additional resources, we will work through that internally, and at the appropriate time, come up and brief you,” he answered Amodei. “I do think he’s in the process still of getting his arms wrapped around the department,” he said. Mullen became DHS secretary in late March.

“This is probably one of those things, particularly in the cyber world, you now have a year and a half of a new administration,” Vought continued, and referred to conservative complaints about how CISA handled election security and disinformation under Biden. “We saw this agency had major concerns with it in our four years outside of government and with new management, I think it’s now an agency, or could be an agency, that plays a very valuable part for DHS’s portfolio.”

Bringing hundreds of new CISA personnel on board could prove challenging for reasons beyond the usual bureaucratic hurdles and security clearance processes that slow any federal hires in the national security space. Past CISA employees and agency observers have said the way the Trump administration has purged personnel and treated those who have stayed could prove a further disincentive to future hires.

Acting CISA director Nick Andersen recently said that the agency has begun the process of hiring new CISA staffers, and expected to have nearly 200 job offers out by the end of this month.

The post Trump budget boss Russell Vought open to re-staffing CISA appeared first on CyberScoop.

Lawmakers Demand Answers as CISA Tries to Contain Data Leak

Lawmakers in both houses of Congress are demanding answers from the U.S. Cybersecurity & Infrastructure Security Agency (CISA) after KrebsOnSecurity reported this week that a CISA contractor intentionally published AWS GovCloud keys and a vast trove of other agency secrets on a public GitHub account. The inquiry comes as CISA is still struggling to contain the breach and invalidate the leaked credentials.

On May 18, KrebsOnSecurity reported that a CISA contractor with administrative access to the agency’s code development platform had created a public GitHub profile called “Private-CISA” that included plaintext credentials to dozens of internal CISA systems. Experts who reviewed the exposed secrets said the commit logs for the code repository showed the CISA contractor disabled GitHub’s built-in protection against publishing sensitive credentials in public repos.

CISA acknowledged the leak but has not responded to questions about the duration of the data exposure. However, experts who reviewed the now-defunct Private-CISA archive said it was originally created in November 2025, and that it exhibits a pattern consistent with an individual operator using the repository as a working scratchpad or synchronization mechanism rather than a curated project repository.

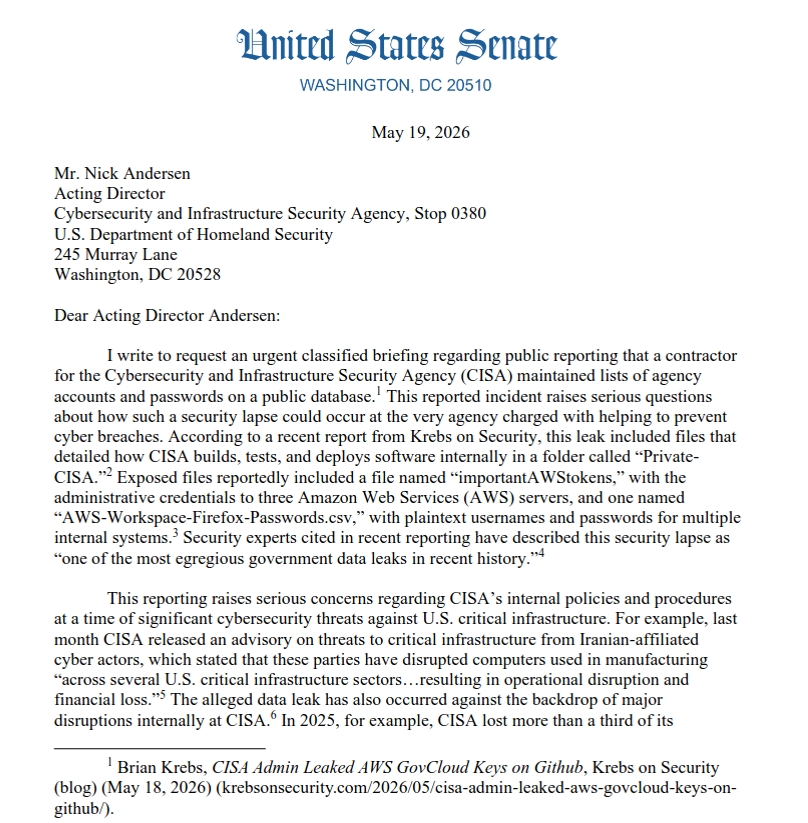
In a written statement, CISA said “there is no indication that any sensitive data was compromised as a result of the incident.” But in a May 19 a letter (PDF) to CISA’s Acting Director Nick Andersen, Sen. Maggie Hassan (D-NH) said the credential leak raises serious questions about how such a security lapse could occur at the very agency charged with helping to prevent cyber breaches.

“This reporting raises serious concerns regarding CISA’s internal policies and procedures at a time of significant cybersecurity threats against U.S. critical infrastructure,” Sen. Hassan wrote.

A May 19 letter from Sen. Margaret Hassan (D-NH) to the acting director of CISA demanded answers to a dozen questions about the breach.

Sen. Hassan noted that the incident occurred against the backdrop of major disruptions internally at CISA, which lost more than a third of it workforce and almost all of its senior leaders after the Trump administration forced a series of early retirements, buyouts, and resignations across the agency’s various divisions.

Rep. Bennie Thompson (D-MS), the ranking member on the House Homeland Security Committee, echoed the senator’s concerns.

“We are concerned that this incident reflects a diminished security culture and/or an inability for CISA to adequately manage its contract support,” Thompson wrote in a May 19 letter to the acting CISA chief that was co-signed by Rep. Delia Ramirez (D-Ill), the ranking member of the panel’s Subcommittee on Cybersecurity and Infrastructure Protection. “It’s no secret that our adversaries — like China, Russia, and Iran — seek to gain access to and persistence on federal networks. The files contained in the ‘Private-CISA’ repository provided the information, access, and roadmap to do just that.”

KrebsOnSecurity has learned that more a week after CISA was first notified of the data leak by the security firm GitGuardian, the agency is still working to invalidate and replace many of the exposed keys and secrets.

On May 20, KrebsOnSecurity heard from Dylan Ayrey, the creator of TruffleHog, an open-source tool for discovering private keys and other secrets buried in code hosted at GitHub and other public platforms. Ayrey said CISA still hadn’t invalidated an RSA private key exposed in the Private-CISA repo that granted access to a GitHub app which is owned by the CISA enterprise account and installed on the CISA-IT GitHub organization with full access to all code repositories.

“An attacker with this key can read source code from every repository in the CISA-IT organization, including private repos, register rogue self-hosted runners to hijack CI/CD pipelines and access repository secrets, and modify repository admin settings including branch protection rules, webhooks, and deploy keys,” Ayrey told KrebsOnSecurity. CI/CD stands for Continuous Integration and Continuous Delivery, and it refers to a set of practices used to automate the building, testing and deployment of software.

KrebsOnSecurity notified CISA about Ayrey’s findings on May 20. Ayrey said CISA appears to have invalidated the exposed RSA private key sometime after that notification. But he noted that CISA still hasn’t rotated leaked credentials tied to other critical security technologies that are deployed across the agency’s technology portfolio (KrebsOnSecurity is not naming those technologies publicly for the time being).

CISA responded with a brief written statement in response to questions about Ayrey’s findings, saying “CISA is actively responding and coordinating with the appropriate parties and vendors to ensure any identified leaked credentials are rotated and rendered invalid and will continue to take appropriate steps to protect the security of our systems.”

Ayrey said his company Truffle Security monitors GitHub and a number of other code platforms for exposed keys, and attempts to alert affected accounts to the sensitive data exposure(s). They can do this easily on GitHub because the platform publishes a live feed which includes a record of all commits and changes to public code repositories. But he said cybercriminal actors also monitor these public feeds, and are often quick to pounce on API or SSH keys that get inadvertently published in code commits.

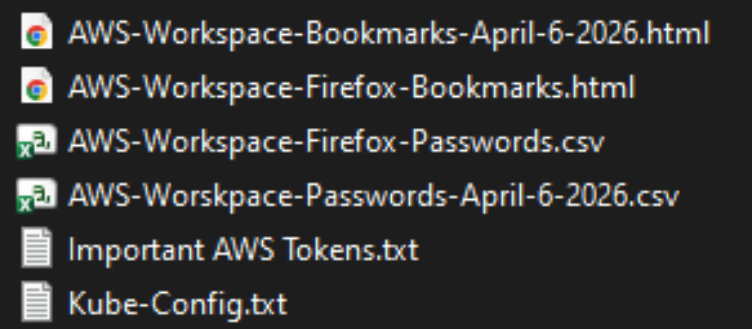
The Private CISA GitHub repo exposed dozens of plaintext credentials to important CISA GovCloud resources. The filenames include AWS-Workspace-Bookmarks-April-6-2026.html, AWS-Workspace-Firefox-Passwords.csv, Important AWS Tokens.txt, kube-config.txt, etc.

The Private-CISA GitHub repo exposed dozens of plaintext credentials to important CISA GovCloud resources.

In practical terms, it is likely that cybercrime groups or foreign adversaries also noticed the publication of these CISA secrets, the most egregious of which appears to have happened in late April 2026, Ayrey said.

“We monitor that firehose of data for keys, and we have tools to try to figure out whose they are,” he said. “We have evidence attackers monitor that firehose as well. Anyone monitoring GitHub events could be sitting on this information.”

James Wilson, the enterprise technology editor for the Risky Business security podcast, said organizations using GitHub to manage code projects can set top-down policies that prevent employees from disabling GitHub’s protections against publishing secret keys and credentials. But Wilson’s co-host Adam Boileau said it’s not clear that any technology could stop employees from opening their own personal GitHub account and using it to store sensitive and proprietary information.

“Ultimately, this is a thing you can’t solve with a technical control,” Boileau said on this week’s podcast. “This is a human problem where you’ve hired a contractor to do this work and they have decided of their own volition to use GitHub to synchronize content from a work machine to a home machine. I don’t know what technical controls you could put in place given that this is being done presumably outside of anything CISA managed or even had visibility on.”

Update, 3:05 p.m. ET: Added statement from CISA. Corrected a date in the story (Truffle Security said it found the repo gained some of its most sensitive secrets in late April 2026, not 2025).

❌